diff --git a/.codegraph/.gitignore b/.codegraph/.gitignore
index 2c9c938..d20c0fe 100644
--- a/.codegraph/.gitignore
+++ b/.codegraph/.gitignore
@@ -1,17 +1,5 @@
-# CodeGraph data files
-# These are local to each machine and should not be committed
-
-# Database
-*.db
-*.db-wal
-*.db-shm
-
-# Cache
-cache/
-
-# Logs
-*.log
-
-# Hook markers
-.dirty
-*.pid
+# CodeGraph data files — local to each machine, not for committing.
+# Ignore everything in .codegraph/ except this file itself, so transient
+# files (the database, daemon.pid, sockets, logs) never show up in git.
+*
+!.gitignore
diff --git a/.dev.vars.example b/.dev.vars.example
deleted file mode 100644
index df2fedb..0000000
--- a/.dev.vars.example
+++ /dev/null
@@ -1,5 +0,0 @@
-# JWT Secret for signing tokens (required)
-# IMPORTANT: change this value before any real deployment.
-# Generate one with: openssl rand -hex 32
-# (Example only, 64 hex chars = 32 bytes)
-JWT_SECRET=Enter-your-JWT-key-here-at-least-32-characters
diff --git a/.github/FUNDING.yml b/.github/FUNDING.yml
new file mode 100644
index 0000000..e357104
--- /dev/null
+++ b/.github/FUNDING.yml
@@ -0,0 +1,2 @@
+custom:
+ - https://nodewarden.app/sponsor
diff --git a/.github/ISSUE_TEMPLATE/config.yml b/.github/ISSUE_TEMPLATE/config.yml
index c71e250..91a17c8 100644
--- a/.github/ISSUE_TEMPLATE/config.yml
+++ b/.github/ISSUE_TEMPLATE/config.yml
@@ -1,7 +1,7 @@
blank_issues_enabled: false
contact_links:
- name: Project Wiki/ 项目文档
- url: https://github.com/shuaiplus/nodewarden/wiki
+ url: https://nodewarden.app
about: |
Please check the documentation for common questions and troubleshooting steps.
请先查看文档,常见问题和排查步骤可能已经覆盖了你的问题。
diff --git a/.github/dependabot.yml b/.github/dependabot.yml
new file mode 100644
index 0000000..3f3db6f
--- /dev/null
+++ b/.github/dependabot.yml
@@ -0,0 +1,33 @@
+version: 2
+
+updates:
+ - package-ecosystem: "npm"
+ directory: "/"
+ schedule:
+ interval: "weekly"
+ day: "monday"
+ time: "05:00"
+ timezone: "Asia/Shanghai"
+ open-pull-requests-limit: 5
+ groups:
+ npm-minor-and-patch:
+ update-types:
+ - "minor"
+ - "patch"
+ ignore:
+ - dependency-name: "tailwindcss"
+ update-types:
+ - "version-update:semver-major"
+
+ - package-ecosystem: "github-actions"
+ directory: "/"
+ schedule:
+ interval: "weekly"
+ day: "monday"
+ time: "05:10"
+ timezone: "Asia/Shanghai"
+ open-pull-requests-limit: 0
+ groups:
+ github-actions:
+ patterns:
+ - "*"
diff --git a/.github/scripts/security.cjs b/.github/scripts/security.cjs
deleted file mode 100644
index bead320..0000000
--- a/.github/scripts/security.cjs
+++ /dev/null
@@ -1,467 +0,0 @@
-const fs = require('fs');
-const path = require('path');
-
-/**
- * Security Report Generator (Node.js)
- * Better, faster, and more maintainable than Bash.
- */
-
-class SecurityReport {
- constructor() {
- this.results = {
- codeql: { status: 'PASS', findings: [], alertCount: 0, rulesCount: 0 },
- snyk: { status: 'PASS', findings: [], vulnCount: 0 },
- gitleaks: { status: 'PASS', findings: [], leaksCount: 0 },
- trivy: { status: 'PASS', findings: [], misconfigCount: 0 },
- coverage: { actions: 0, js: 0, ts: 0 },
- artifactUris: []
- };
- this.auditTime = new Date().toISOString().replace('T', ' ').substring(0, 19) + ' UTC';
- this.runId = process.env.GITHUB_RUN_ID || '0';
- this.repository = process.env.GITHUB_REPOSITORY || 'unknown/repo';
- this.runUrl = `https://github.com/${this.repository}/actions/runs/${this.runId}`;
-
- this.locales = {
- zh: {
- filename: 'security-report-cn.md',
- switcher: '[English](security-report.md) | 中文',
- title: '🛡️ 安全审计与透明度报告',
- grade: '安全评级',
- important: '> [!IMPORTANT]\n> 本报告由 **GitHub Actions** 自动生成。为确保数据主权的绝对透明度,所有核心模块的安全扫描结果均实时公开。',
- auditTime: '📅 审计时间',
- runId: '📝 运行 ID',
- env: '🛠️ 环境',
- dashboard: '📉 实时安全仪表盘',
- tool: '工具',
- status: '状态',
- findings: '发现项',
- leaks: '泄露',
- vulns: '漏洞',
- alerts: '告警',
- coverageTitle: '🔍 扫描覆盖范围',
- module: '模块',
- auditedFiles: '已审计文件',
- coverage: '覆盖率',
- detailedFindings: '🔍 详细发现项',
- gitleaksTitle: '🔑 凭据泄露检查 (Gitleaks)',
- gitleaksDesc: '`检测代码历史记录中硬编码的 API 密钥、密码或其他敏感令牌。`',
- gitleaksSafe: '✅ **安全**:未发现硬编码的敏感凭据。',
- gitleaksScope: '`扫描范围:所有代码更改和 Git 历史记录 (Gitleaks 全量扫描)`',
- snykTitle: '📦 第三方依赖',
- snykSafe: '✅ **安全**:在依赖项中未发现已知漏洞。',
- package: '软件包',
- severity: '严重程度',
- description: '描述',
- fixPlan: '修复方案',
- codeqlTitle: '💻 代码质量与安全 (CodeQL)',
- codeqlSummary: '#### 摘要',
- rulesChecked: '已检查规则',
- totalAlerts: '告警总数',
- codeqlSafe: '✅ **安全**:CodeQL 扫描清洁,未检测到问题。',
- ruleId: '规则 ID',
- level: '级别',
- location: '位置',
- auditedList: '📂 已审计文件列表',
- guideTitle: '⚠️ 操作指南',
- guideDesc: '如果您看到 **FAIL** 状态或严重的代码问题:',
- guideStep1: '1. **开发人员**:使用上方表格中的 **位置** 列找到确切的文件和行号。',
- guideStep2: '2. **纠正**:遵循为每个规则提供的文档链接以提交修复。',
- guideStep3: '3. **可追溯性**:完整的原始 `.sarif` 数据已附加到此分支。下载并将其导入您的 IDE(例如 VS Code SARIF 查看器)进行本地分析。',
- footer: '💡 *由 NodeWarden 安全工作流生成。透明度是我们的承诺。*',
- auditedIcon: '✅ **已审计**',
- noFiles: '未检索到文件。',
- trivyTitle: '🛡️ 容器配置安全 (Trivy)',
- trivyDesc: '`检测 Dockerfile 和容器配置中的安全风险与最佳实践。`',
- trivySafe: '✅ **安全**:未发现容器配置缺陷。'
- },
- en: {
- filename: 'security-report.md',
- switcher: 'English | [中文](security-report-cn.md)',
- title: '🛡️ Security Audit & Transparency Report',
- grade: 'Security Grade',
- important: '> [!IMPORTANT]\n> This report is automatically generated by **GitHub Actions**. To ensure absolute transparency of data sovereignty, all core module security scan results are made public in real-time.',
- auditTime: '📅 Audit Time',
- runId: '📝 Run ID',
- env: '🛠️ Environment',
- dashboard: '📉 Real-time Security Dashboard',
- tool: 'Tool',
- status: 'Status',
- findings: 'Findings',
- leaks: 'Leaks',
- vulns: 'Vulns',
- alerts: 'Alerts',
- coverageTitle: '🔍 Scan Coverage',
- module: 'Module',
- auditedFiles: 'Audited Files',
- coverage: 'Coverage',
- detailedFindings: '🔍 Detailed Findings',
- gitleaksTitle: '🔑 Credential Leak Check (Gitleaks)',
- gitleaksDesc: '`This section detects hardcoded API Keys, passwords, or other sensitive tokens in the code history.`',
- gitleaksSafe: '✅ **SAFE**: No hardcoded sensitive credentials found.',
- gitleaksScope: '`Scan Scope: All code changes and Git history (Gitleaks Full Scan)`',
- snykTitle: '📦 Third-party Dependencies',
- snykSafe: '✅ **SAFE**: No known vulnerabilities found in dependencies.',
- package: 'Package',
- severity: 'Severity',
- description: 'Description',
- fixPlan: 'Fix Plan',
- codeqlTitle: '💻 Code Quality & Safety (CodeQL)',
- codeqlSummary: '#### Summary',
- rulesChecked: 'Rules Checked',
- totalAlerts: 'Total Alerts',
- codeqlSafe: '✅ **SAFE**: CodeQL clean. No issues detected.',
- ruleId: 'Rule ID',
- level: 'Level',
- location: 'Location',
- auditedList: '📂 Audited File List',
- guideTitle: '⚠️ Action Guide',
- guideDesc: 'If you see a **FAIL** status or serious code issues:',
- guideStep1: '1. **Developers**: Use the **Location** column in the tables above to find the exact file and line number.',
- guideStep2: '2. **Remediate**: Follow the documentation links provided for each rule to submit a fix.',
- guideStep3: '3. **Traceability**: Full raw `.sarif` data is attached to this branch. Download and import it into your IDE (e.g., VS Code SARIF Viewer) for local analysis.',
- footer: '💡 *Generated by the NodeWarden security workflow. Transparency is our commitment.*',
- auditedIcon: '✅ **Audited**',
- noFiles: 'No files found.',
- trivyTitle: '🛡️ Container Config Security (Trivy)',
- trivyDesc: '`This section detects security risks and best practices in Dockerfile and container configurations.`',
- trivySafe: '✅ **SAFE**: No container configuration defects found.'
- }
- };
- }
-
- // --- Data Parsers ---
-
- async parseCodeQL() {
- const sarifPath = 'sarif-results';
- if (!fs.existsSync(sarifPath)) return;
-
- const files = this.globFiles(sarifPath, '.sarif');
- let totalAlerts = 0;
- let rulesSet = new Set();
- let findings = [];
- let artifactUris = new Set();
-
- for (const file of files) {
- const data = JSON.parse(fs.readFileSync(file, 'utf8'));
- for (const run of data.runs || []) {
- // Collect Rules
- (run.tool.driver.rules || []).forEach(r => rulesSet.add(r.id));
- (run.tool.extensions || []).forEach(ext => {
- (ext.rules || []).forEach(r => rulesSet.add(r.id));
- });
-
- // Collect Results
- for (const res of run.results || []) {
- totalAlerts++;
- const loc = (res.locations && res.locations[0]?.physicalLocation) || {};
- findings.push({
- id: res.ruleId,
- level: res.level || 'warning',
- path: loc.artifactLocation?.uri || 'Global',
- line: loc.region?.startLine || '-',
- message: res.message?.text || 'No description'
- });
- }
-
- // Track Coverage (Deduplicated)
- (run.artifacts || []).forEach(art => {
- const uri = art.location?.uri || '';
- if (uri) artifactUris.add(uri);
- });
- }
- }
-
- this.results.artifactUris = Array.from(artifactUris).sort();
- this.results.coverage.actions = this.results.artifactUris.filter(u => u.startsWith('.github/workflows/')).length;
- this.results.coverage.js = this.results.artifactUris.filter(u => u.endsWith('.js')).length;
- this.results.coverage.ts = this.results.artifactUris.filter(u => u.endsWith('.ts')).length;
-
- this.results.codeql.alertCount = totalAlerts;
- this.results.codeql.rulesCount = rulesSet.size;
- this.results.codeql.findings = findings;
- if (totalAlerts > 0) this.results.codeql.status = 'INFO';
- }
-
- async parseSnyk() {
- const jsonPath = 'snyk_result.json';
- if (!fs.existsSync(jsonPath)) return;
-
- try {
- const data = JSON.parse(fs.readFileSync(jsonPath, 'utf8'));
- const projects = Array.isArray(data) ? data : [data];
- let vulnTotal = 0;
- let findings = [];
-
- for (const proj of projects) {
- const vulns = proj.vulnerabilities || [];
- vulnTotal += vulns.length;
- vulns.forEach(v => {
- findings.push({
- pkg: `${v.packageName}@${v.version}`,
- severity: v.severity,
- title: v.title,
- url: v.url,
- fixedIn: Array.isArray(v.fixedIn) ? v.fixedIn.join(', ') : (v.fixedIn || 'N/A')
- });
- });
- }
-
- this.results.snyk.vulnCount = vulnTotal;
- this.results.snyk.findings = findings;
- if (vulnTotal > 0) this.results.snyk.status = 'WARN';
- } catch (e) {
- console.error('Error parsing Snyk JSON:', e.message);
- }
- }
-
- async parseGitleaks() {
- const files = this.globFiles('.', 'results.sarif');
- if (files.length === 0) return;
-
- try {
- const data = JSON.parse(fs.readFileSync(files[0], 'utf8'));
- let leaks = 0;
- let findings = [];
- for (const run of data.runs || []) {
- for (const res of run.results || []) {
- leaks++;
- findings.push({
- id: res.ruleId,
- message: res.message.text,
- path: res.locations[0]?.physicalLocation?.artifactLocation?.uri || 'Unknown'
- });
- }
- }
-
- this.results.gitleaks.leaksCount = leaks;
- this.results.gitleaks.findings = findings;
- if (leaks > 0) this.results.gitleaks.status = 'FAIL';
- } catch (e) {
- console.error('Error parsing Gitleaks SARIF:', e.message);
- }
- }
-
- async parseTrivy() {
- const jsonPath = 'trivy_result.json';
- if (!fs.existsSync(jsonPath)) return;
-
- try {
- const data = JSON.parse(fs.readFileSync(jsonPath, 'utf8'));
- let misconfigs = 0;
- let findings = [];
-
- (data.Results || []).forEach(res => {
- (res.Misconfigurations || []).forEach(m => {
- misconfigs++;
- findings.push({
- id: m.ID,
- severity: m.Severity,
- title: m.Title,
- message: m.Message,
- status: m.Status,
- target: res.Target
- });
- });
- });
-
- this.results.trivy.misconfigCount = misconfigs;
- this.results.trivy.findings = findings;
- if (misconfigs > 0) this.results.trivy.status = 'WARN';
- } catch (e) {
- console.error('Error parsing Trivy JSON:', e.message);
- }
- }
-
- generateTable(type, t) {
- let files = [];
- if (type === 'actions') files = this.results.artifactUris.filter(u => u.startsWith('.github/workflows/'));
- else if (type === 'js') files = this.results.artifactUris.filter(u => u.endsWith('.js'));
- else if (type === 'ts') files = this.results.artifactUris.filter(u => u.endsWith('.ts'));
-
- if (files.length === 0) return `> ${t.noFiles}\n`;
-
- let table = `| ${t.module} | ${t.location} | ${t.status} |\n| :--- | :--- | :--- |\n`;
- files.forEach(f => {
- const filename = path.basename(f);
- table += `| \`${filename}\` | \`${f}\` | ${t.auditedIcon} |\n`;
- });
- return table;
- }
-
- // --- Renderers ---
-
- generateMarkdown(localeKey) {
- const { codeql, snyk, gitleaks, coverage } = this.results;
- const t = this.locales[localeKey];
-
- // Calculate Grade
- let grade = 'A+';
- let gradeColor = 'success';
- if (gitleaks.status === 'FAIL') { grade = 'D'; gradeColor = 'red'; }
- else if (snyk.vulnCount > 10 || this.results.trivy.misconfigCount > 5) { grade = 'C'; gradeColor = 'orange'; }
- else if (snyk.vulnCount > 0 || codeql.alertCount > 0 || this.results.trivy.misconfigCount > 0) { grade = 'B'; gradeColor = 'blue'; }
-
- const badge = (label, value, color) => `}-${value}-${color}?style=for-the-badge)`;
-
- let md = `# ${t.title}\n\n`;
- md += `${t.switcher}\n\n`;
- md += `${badge(t.grade.replace(/ /g, '_'), grade, gradeColor)}\n\n`;
- md += `${t.important}\n\n`;
-
- md += `| ${t.auditTime} | ${t.runId} | ${t.env} |\n`;
- md += `| :--- | :--- | :--- |\n`;
- md += `| \`${this.auditTime}\` | [#${this.runId}](${this.runUrl}) | \`GitHub CI/CD\` |\n\n`;
-
- md += `---\n\n## ${t.dashboard}\n\n`;
- md += `| ${t.tool} | ${t.status} | ${t.findings} |\n`;
- md += `| :--- | :--- | :--- |\n`;
- md += `| **Credential Leak (Gitleaks)** | ${this.getBadge(gitleaks.status)} | \`${gitleaks.leaksCount}\` ${t.leaks} |\n`;
- md += `| **Dependency Scan (Snyk)** | ${this.getBadge(snyk.status)} | \`${snyk.vulnCount}\` ${t.vulns} |\n`;
- md += `| **Static Analysis (CodeQL)** | ${this.getBadge(codeql.status)} | \`${codeql.alertCount}\` ${t.alerts} |\n`;
- md += `| **Container Scan (Trivy)** | ${this.getBadge(this.results.trivy.status)} | \`${this.results.trivy.misconfigCount}\` ${t.findings} |\n\n`;
-
- md += `---\n\n## ${t.coverageTitle}\n\n`;
- md += `| ${t.module} | ${t.auditedFiles} | ${t.coverage} |\n`;
- md += `| :--- | :---: | :---: |\n`;
- md += `| **GitHub Actions** | \`${coverage.actions}\` | ✨ **100%** |\n`;
- md += `| **JavaScript (Frontend)** | \`${coverage.js}\` | ✨ **100%** |\n`;
- md += `| **TypeScript (Backend)** | \`${coverage.ts}\` | ✨ **100%** |\n\n`;
-
- md += `---\n\n## ${t.detailedFindings}\n\n`;
-
- // Gitleaks Section
- md += `### ${t.gitleaksTitle}\n`;
- md += `${t.gitleaksDesc} ${t.gitleaksScope}\n\n`;
- if (gitleaks.findings.length > 0) {
- md += `| ${t.ruleId} | ${t.location} | ${t.description} |\n`;
- md += `| :--- | :--- | :--- |\n`;
- gitleaks.findings.forEach(f => {
- md += `| \`${f.id}\` | \`${f.path}\` | ${f.message} |\n`;
- });
- } else {
- md += `${t.gitleaksSafe}\n`;
- }
-
- // Trivy Section
- md += `\n### ${t.trivyTitle}\n`;
- md += `${t.trivyDesc}\n\n`;
- if (this.results.trivy.findings.length > 0) {
- md += `| ${t.ruleId} | ${t.severity} | ${t.location} | ${t.description} |\n`;
- md += `| :--- | :---: | :--- | :--- |\n`;
- this.results.trivy.findings.forEach(f => {
- const icon = f.severity === 'CRITICAL' ? '🔴' : (f.severity === 'HIGH' ? '🟠' : '🟡');
- md += `| \`${f.id}\` | ${icon} ${f.severity} | \`${f.target}\` | ${f.title}: ${f.message} |\n`;
- });
- } else {
- md += `${t.trivySafe}\n`;
- }
-
- // Snyk Section
- md += `\n### ${t.snykTitle}\n`;
- if (snyk.findings.length > 0) {
- md += `| ${t.package} | ${t.severity} | ${t.description} | ${t.fixPlan} |\n`;
- md += `| :--- | :---: | :--- | :--- |\n`;
- snyk.findings.forEach(f => {
- const icon = f.severity === 'critical' ? '🔴' : (f.severity === 'high' ? '🟠' : '🟡');
- md += `| \`${f.pkg}\` | ${icon} ${f.severity} | [${f.title}](${f.url}) | ${f.fixedIn === 'N/A' ? 'No fix' : `Upgrade to \`${f.fixedIn}\``} |\n`;
- });
- } else {
- md += `${t.snykSafe}\n`;
- }
-
- // CodeQL Section
- md += `\n### ${t.codeqlTitle}\n`;
- if (codeql.findings.length > 0) {
- md += `${t.codeqlSummary}\n- **${t.rulesChecked}**: \`${codeql.rulesCount}\`\n- **${t.totalAlerts}**: \`${codeql.alertCount}\`\n\n`;
- md += `| ${t.ruleId} | ${t.level} | ${t.location} | ${t.description} |\n`;
- md += `| :--- | :---: | :--- | :--- |\n`;
- codeql.findings.forEach(f => {
- const icon = f.level === 'error' ? '🔴' : (f.level === 'warning' ? '🟠' : '🔵');
- const prefix = f.id.split('/')[0];
- const langMap = {
- 'js': 'javascript',
- 'actions': 'github-actions',
- 'cpp': 'cpp',
- 'cs': 'csharp',
- 'go': 'go',
- 'java': 'java',
- 'py': 'python',
- 'rb': 'ruby',
- 'swift': 'swift'
- };
- const langPath = langMap[prefix] || 'javascript';
- md += `| [${f.id}](https://codeql.github.com/codeql-query-help/${langPath}/${f.id.replace(/\//g, '-')}/) | ${icon} ${f.level} | \`${f.path}:${f.line}\` | ${f.message} |\n`;
- });
- } else {
- md += `${t.codeqlSafe}\n`;
- }
-
- // Audited Files List
- md += `\n### ${t.auditedList}\n`;
- md += `\nGitHub Actions (${this.results.coverage.actions})
\n\n`;
- md += this.generateTable('actions', t);
- md += `\n \n\n`;
-
- md += `\nJavaScript (${this.results.coverage.js})
\n\n`;
- md += this.generateTable('js', t);
- md += `\n \n\n`;
-
- md += `\nTypeScript (${this.results.coverage.ts})
\n\n`;
- md += this.generateTable('ts', t);
- md += `\n \n\n`;
-
- // Action Guide
- md += `--- \n\n## ${t.guideTitle}\n\n`;
- md += `${t.guideDesc}\n`;
- md += `${t.guideStep1}\n`;
- md += `${t.guideStep2}\n`;
- md += `${t.guideStep3}\n\n`;
-
- md += `--- \n\n${t.footer}`;
-
- return md;
- }
-
- // --- Helpers ---
-
- getBadge(status) {
- if (status === 'PASS') return '';
- if (status === 'WARN' || status === 'INFO') return '';
- return '';
- }
-
- globFiles(dir, ext) {
- let results = [];
- const list = fs.readdirSync(dir);
- for (const file of list) {
- const fullPath = path.join(dir, file);
- const stat = fs.statSync(fullPath);
- if (stat && stat.isDirectory()) {
- results = results.concat(this.globFiles(fullPath, ext));
- } else if (file.endsWith(ext)) {
- results.push(fullPath);
- }
- }
- return results;
- }
-
- async run() {
- console.log('--- Security Report Generation Started ---');
- await this.parseCodeQL();
- await this.parseSnyk();
- await this.parseGitleaks();
- await this.parseTrivy();
-
- for (const localeKey of Object.keys(this.locales)) {
- const locale = this.locales[localeKey];
- const markdown = this.generateMarkdown(localeKey);
- fs.writeFileSync(locale.filename, markdown);
- console.log(`Report generated successfully at ${locale.filename}`);
- }
- }
-}
-
-new SecurityReport().run().catch(err => {
- console.error('Report generation failed:', err);
- process.exit(1);
-});
diff --git a/.github/workflows/codeql.yml b/.github/workflows/codeql.yml
new file mode 100644
index 0000000..88cf643
--- /dev/null
+++ b/.github/workflows/codeql.yml
@@ -0,0 +1,44 @@
+name: "CodeQL Advanced"
+
+on:
+ push:
+ branches:
+ - "**"
+
+permissions:
+ contents: read
+ actions: read
+ security-events: write
+ packages: read
+
+jobs:
+ analyze:
+ name: CodeQL Analyze (${{ matrix.language }})
+ runs-on: ubuntu-latest
+
+ strategy:
+ fail-fast: false
+ matrix:
+ include:
+ - language: actions
+ build-mode: none
+ - language: javascript-typescript
+ build-mode: none
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Initialize CodeQL
+ uses: github/codeql-action/init@411bbbe57033eedfc1a82d68c01345aa96c737d7
+ with:
+ languages: ${{ matrix.language }}
+ build-mode: ${{ matrix.build-mode }}
+ queries: security-extended,security-and-quality
+
+ - name: Perform CodeQL Analysis
+ uses: github/codeql-action/analyze@411bbbe57033eedfc1a82d68c01345aa96c737d7
+ with:
+ category: "/language:${{ matrix.language }}"
diff --git a/.github/workflows/security-extra.yml b/.github/workflows/security-extra.yml
new file mode 100644
index 0000000..c565257
--- /dev/null
+++ b/.github/workflows/security-extra.yml
@@ -0,0 +1,200 @@
+name: "Extra Security Scan"
+
+on:
+ push:
+ branches:
+ - "**"
+
+permissions:
+ contents: read
+
+jobs:
+ gitleaks:
+ name: Gitleaks Secret Scan
+ runs-on: ubuntu-latest
+
+ permissions:
+ contents: read
+
+ steps:
+ - name: Checkout full history
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ fetch-depth: 0
+ persist-credentials: false
+
+ - name: Run Gitleaks
+ uses: gitleaks/gitleaks-action@e0c47f4f8be36e29cdc102c57e68cb5cbf0e8d1e
+ env:
+ GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
+ GITLEAKS_ENABLE_SUMMARY: "true"
+ GITLEAKS_ENABLE_UPLOAD_ARTIFACT: "true"
+ # 如果仓库属于 GitHub Organization,需要在 Settings -> Secrets 里加 GITLEAKS_LICENSE
+ # GITLEAKS_LICENSE: ${{ secrets.GITLEAKS_LICENSE }}
+
+ osv:
+ name: OSV Dependency Scan
+ uses: google/osv-scanner-action/.github/workflows/osv-scanner-reusable.yml@9a498708959aeaef5ef730655706c5a1df1edbc2
+
+ permissions:
+ contents: read
+ actions: read
+ security-events: write
+
+ with:
+ scan-args: |-
+ --recursive
+ ./
+ upload-sarif: true
+ fail-on-vuln: true
+
+ pnpm-audit:
+ name: pnpm audit
+ runs-on: ubuntu-latest
+
+ permissions:
+ contents: read
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Setup Node.js
+ uses: actions/setup-node@48b55a011bda9f5d6aeb4c2d9c7362e8dae4041e
+ with:
+ node-version: 22
+
+ - name: Run pnpm audit
+ shell: bash
+ run: |
+ if [ ! -f pnpm-lock.yaml ]; then
+ echo "pnpm-lock.yaml not found, skip pnpm audit."
+ exit 0
+ fi
+
+ corepack enable
+ corepack prepare pnpm@10 --activate
+ pnpm audit --audit-level=high
+
+ semgrep:
+ name: Semgrep CE Scan
+ runs-on: ubuntu-latest
+
+ permissions:
+ contents: read
+ security-events: write
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Run Semgrep CE
+ shell: bash
+ run: |
+ docker run --rm \
+ -v "${PWD}:/src" \
+ -w /src \
+ semgrep/semgrep:latest \
+ semgrep scan --config p/default --sarif --output semgrep.sarif . || true
+
+ if [ ! -f semgrep.sarif ]; then
+ cat > semgrep.sarif <<'EOF'
+ {
+ "version": "2.1.0",
+ "$schema": "https://json.schemastore.org/sarif-2.1.0.json",
+ "runs": [
+ {
+ "tool": {
+ "driver": {
+ "name": "Semgrep",
+ "informationUri": "https://semgrep.dev",
+ "rules": []
+ }
+ },
+ "results": []
+ }
+ ]
+ }
+ EOF
+ fi
+
+ - name: Upload Semgrep SARIF
+ uses: github/codeql-action/upload-sarif@411bbbe57033eedfc1a82d68c01345aa96c737d7
+ with:
+ sarif_file: semgrep.sarif
+ category: semgrep
+
+ actionlint:
+ name: GitHub Actions Syntax Scan
+ runs-on: ubuntu-latest
+
+ permissions:
+ contents: read
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Run actionlint
+ shell: bash
+ run: |
+ docker run --rm \
+ -v "${PWD}:/repo" \
+ -w /repo \
+ rhysd/actionlint:latest
+
+ zizmor:
+ name: GitHub Actions Security Scan
+ runs-on: ubuntu-latest
+
+ permissions:
+ contents: read
+ actions: read
+ security-events: write
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Run zizmor
+ uses: zizmorcore/zizmor-action@192e21d79ab29983730a13d1382995c2307fbcaa
+ with:
+ persona: auditor
+ min-severity: medium
+ min-confidence: medium
+
+ scorecard:
+ name: OpenSSF Scorecard
+ runs-on: ubuntu-latest
+ if: github.ref == 'refs/heads/main'
+
+ permissions:
+ contents: read
+ security-events: write
+
+ steps:
+ - name: Checkout repository
+ uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
+ with:
+ persist-credentials: false
+
+ - name: Run OpenSSF Scorecard
+ uses: ossf/scorecard-action@99c09fe975337306107572b4fdf4db224cf8e2f2
+ with:
+ results_file: scorecard.sarif
+ results_format: sarif
+ publish_results: false
+
+ - name: Upload Scorecard SARIF
+ uses: github/codeql-action/upload-sarif@411bbbe57033eedfc1a82d68c01345aa96c737d7
+ with:
+ sarif_file: scorecard.sarif
+ category: openssf-scorecard
diff --git a/.github/workflows/security.yml b/.github/workflows/security.yml
deleted file mode 100644
index 644582b..0000000
--- a/.github/workflows/security.yml
+++ /dev/null
@@ -1,142 +0,0 @@
-name: Security Scan
-
-on:
- push:
- branches:
- - main
- pull_request:
- branches:
- - main
- workflow_dispatch:
-
-jobs:
- scan:
- runs-on: ubuntu-latest
- permissions:
- contents: read
- security-events: write
- actions: read
- env:
- SECURITY_SNYK_TOKEN: ${{ secrets.SECURITY_SNYK_TOKEN }}
- steps:
- - uses: actions/checkout@v5
- with:
- fetch-depth: 0
-
- - name: Initialize CodeQL
- if: env.ACT != 'true'
- continue-on-error: true
- uses: github/codeql-action/init@v4
- with:
- languages: javascript-typescript, actions
- build-mode: none
- queries: security-extended,security-and-quality
-
- - name: Perform CodeQL Analysis
- if: env.ACT != 'true'
- continue-on-error: true
- uses: github/codeql-action/analyze@v4
- with:
- upload: true
- output: sarif-results
-
- - name: Install Gitleaks
- if: env.ACT != 'true'
- continue-on-error: true
- run: |
- GITLEAKS_VERSION="8.28.0"
- curl -sSL -o gitleaks.tar.gz "https://github.com/gitleaks/gitleaks/releases/download/v${GITLEAKS_VERSION}/gitleaks_${GITLEAKS_VERSION}_linux_x64.tar.gz"
- tar -xzf gitleaks.tar.gz gitleaks
- chmod +x gitleaks
- sudo mv gitleaks /usr/local/bin/gitleaks
-
- - name: Secret Detection
- if: env.ACT != 'true'
- continue-on-error: true
- run: |
- gitleaks git . --report-format sarif --report-path results.sarif --no-banner || true
-
- - name: Install Project Dependencies
- if: env.SECURITY_SNYK_TOKEN != ''
- env:
- SECURITY_PACKAGE: ${{ vars.SECURITY_PACKAGE || '' }}
- run: |
- echo "Preparing dependency lock files for security scanning..."
- if [ -z "$SECURITY_PACKAGE" ]; then
- echo "SECURITY_PACKAGE is empty, installing in root..."
- npm install --package-lock-only
- else
- echo "SECURITY_PACKAGE is set to: $SECURITY_PACKAGE"
- # Split by comma and install
- IFS=',' read -ra PACKAGES <<< "$SECURITY_PACKAGE"
- for pkg in "${PACKAGES[@]}"; do
- if [ -d "$pkg" ]; then
- echo "Installing in "$pkg"..."
- npm install --prefix "$pkg" --package-lock-only
- else
- echo "Warning: Directory $pkg not found, skipping."
- fi
- done
- fi
-
- - name: Dependency Scan
- id: snyk
- if: env.SECURITY_SNYK_TOKEN != ''
- continue-on-error: true
- run: |
- npm install -g snyk
- snyk auth ${{ secrets.SECURITY_SNYK_TOKEN }}
- snyk test --all-projects --json-file-output=snyk_result.json > snyk_result.txt || true
- env:
- SECURITY_SNYK_TOKEN: ${{ secrets.SECURITY_SNYK_TOKEN }}
-
- - name: Check for Dockerfile
- id: check_docker
- run: |
- if [ -f "Dockerfile" ]; then
- echo "exists=true" >> $GITHUB_OUTPUT
- else
- echo "exists=false" >> $GITHUB_OUTPUT
- fi
-
- - name: Container Security Scan (Trivy)
- if: steps.check_docker.outputs.exists == 'true'
- continue-on-error: true
- run: |
- VERSION="0.56.1"
- echo "Installing Trivy $VERSION..."
- curl -sfL https://raw.githubusercontent.com/aquasecurity/trivy/main/contrib/install.sh | sh -s -- -b /usr/local/bin "v$VERSION"
- trivy config . --format json --output trivy_result.json --severity CRITICAL,HIGH || true
-
- - name: Generate Security Report
- run: |
- # Gitleaks typically produces results.sarif if configured or by default in some versions
- # We'll ensure it exists for our reporter
- node .github/scripts/security.cjs
-
- # Also append to step summary for immediate visibility in GHA UI
- cat security-report.md >> $GITHUB_STEP_SUMMARY
- echo -e "\n---\n" >> $GITHUB_STEP_SUMMARY
- cat security-report-cn.md >> $GITHUB_STEP_SUMMARY
-
- - name: Upload Gitleaks Results to GitHub Security
- uses: github/codeql-action/upload-sarif@v4
- if: always()
- with:
- sarif_file: results.sarif
- category: gitleaks
-
- - name: Upload Security Report Artifacts
- if: always()
- uses: actions/upload-artifact@v6
- with:
- name: security-report
- if-no-files-found: ignore
- path: |
- security-report.md
- security-report-cn.md
- snyk_result.txt
- snyk_result.json
- trivy_result.json
- results.sarif
- sarif-results/*.sarif
diff --git a/.github/workflows/sync-global-domains.yml b/.github/workflows/sync-global-domains.yml
index 15dd781..12cbb40 100644
--- a/.github/workflows/sync-global-domains.yml
+++ b/.github/workflows/sync-global-domains.yml
@@ -19,20 +19,29 @@ jobs:
sync-global-domains:
runs-on: ubuntu-latest
steps:
- - uses: actions/checkout@v4
+ - uses: actions/checkout@9c091bb21b7c1c1d1991bb908d89e4e9dddfe3e0
- - uses: actions/setup-node@v4
+ - uses: actions/setup-node@48b55a011bda9f5d6aeb4c2d9c7362e8dae4041e
with:
node-version: 22
- name: Sync generated Bitwarden domains
- run: npm run domains:sync -- --ref "${{ inputs.bitwarden_ref || 'main' }}"
+ env:
+ BITWARDEN_REF: ${{ inputs.bitwarden_ref || 'main' }}
+ run: |
+ case "$BITWARDEN_REF" in
+ "" | *[!A-Za-z0-9._/-]* )
+ echo "Invalid bitwarden_ref"
+ exit 1
+ ;;
+ esac
+ npm run domains:sync -- --ref "$BITWARDEN_REF"
- name: Verify custom domains were not touched
run: git diff --exit-code -- src/static/global_domains.custom.json
- name: Create pull request
- uses: peter-evans/create-pull-request@v6
+ uses: peter-evans/create-pull-request@5f6978faf089d4d20b00c7766989d076bb2fc7f1
with:
branch: chore/sync-bitwarden-global-domains
delete-branch: true
diff --git a/.github/workflows/sync-upstream.yml b/.github/workflows/sync-upstream.yml
deleted file mode 100644
index 2925833..0000000
--- a/.github/workflows/sync-upstream.yml
+++ /dev/null
@@ -1,143 +0,0 @@
-name: Sync upstream
-
-on:
- schedule:
- - cron: "0 3 * * *"
- workflow_dispatch:
- inputs:
- target_commit:
- description: 'Commit hash (leave blank to use latest commit)'
- required: false
- type: string
-
-permissions:
- contents: write
-
-jobs:
- sync:
- runs-on: ubuntu-latest
- steps:
- - uses: actions/checkout@v4
- with:
- fetch-depth: 0
-
- - name: Configure git
- run: |
- git config user.name "github-actions[bot]"
- git config user.email "41898282+github-actions[bot]@users.noreply.github.com"
-
- - name: Add upstream
- run: |
- git remote add upstream https://github.com/shuaiplus/NodeWarden.git || true
- git fetch upstream --tags
-
- - name: Resolve target commit
- id: resolve
- run: |
- TRIGGER="${{ github.event_name }}"
- MANUAL_INPUT="${{ github.event.inputs.target_commit }}"
-
- if [ "$TRIGGER" = "schedule" ]; then
- # Auto mode: resolve latest upstream release tag
- LATEST_TAG=$(curl -s https://api.github.com/repos/shuaiplus/NodeWarden/releases/latest | jq -r .tag_name)
- if [ "$LATEST_TAG" = "null" ] || [ -z "$LATEST_TAG" ]; then
- echo "No release found in upstream."
- exit 1
- fi
- TARGET_SHA=$(git rev-list -n 1 "$LATEST_TAG" 2>/dev/null)
- if [ -z "$TARGET_SHA" ]; then
- echo "Tag '$LATEST_TAG' not found after fetch."
- exit 1
- fi
- echo "mode=auto" >> $GITHUB_OUTPUT
- echo "latest_tag=$LATEST_TAG" >> $GITHUB_OUTPUT
- echo "target_sha=$TARGET_SHA" >> $GITHUB_OUTPUT
- echo "Auto mode — latest release: $LATEST_TAG ($TARGET_SHA)"
-
- elif [ -n "$MANUAL_INPUT" ]; then
- # Manual mode: use provided commit hash or tag
- TARGET_SHA=$(git rev-parse "$MANUAL_INPUT" 2>/dev/null)
- if [ -z "$TARGET_SHA" ]; then
- echo "Cannot resolve '$MANUAL_INPUT' to a commit."
- exit 1
- fi
- echo "mode=manual" >> $GITHUB_OUTPUT
- echo "target_sha=$TARGET_SHA" >> $GITHUB_OUTPUT
- echo "Manual mode — target: $MANUAL_INPUT ($TARGET_SHA)"
-
- else
- # Manual mode, blank input: use latest commit on upstream/main
- TARGET_SHA=$(git rev-parse upstream/main)
- echo "mode=manual" >> $GITHUB_OUTPUT
- echo "target_sha=$TARGET_SHA" >> $GITHUB_OUTPUT
- echo "Manual mode — latest commit: $TARGET_SHA"
- fi
-
- - name: Check if update is needed
- id: check
- run: |
- TARGET_SHA="${{ steps.resolve.outputs.target_sha }}"
- MODE="${{ steps.resolve.outputs.mode }}"
-
- if [ "$MODE" = "manual" ]; then
- # Manual: skip only if HEAD is exactly this commit
- CURRENT_SHA=$(git rev-parse HEAD)
- if [ "$CURRENT_SHA" = "$TARGET_SHA" ]; then
- echo "Already at $TARGET_SHA — skipping."
- echo "needs_update=false" >> $GITHUB_OUTPUT
- else
- echo "Switching to $TARGET_SHA"
- echo "needs_update=true" >> $GITHUB_OUTPUT
- fi
- else
- # Auto: skip if target is already in ancestry
- if git merge-base --is-ancestor "$TARGET_SHA" HEAD 2>/dev/null; then
- echo "Already up to date with $TARGET_SHA — skipping."
- echo "needs_update=false" >> $GITHUB_OUTPUT
- else
- echo "Update needed — target: $TARGET_SHA"
- echo "needs_update=true" >> $GITHUB_OUTPUT
- fi
- fi
-
- - name: Apply update
- if: steps.check.outputs.needs_update == 'true'
- run: |
- TARGET_SHA="${{ steps.resolve.outputs.target_sha }}"
- MODE="${{ steps.resolve.outputs.mode }}"
- git checkout main
- if [ "$MODE" = "manual" ]; then
- # Hard reset allows both upgrade and rollback
- git reset --hard "$TARGET_SHA"
- else
- git merge "$TARGET_SHA" --no-edit
- fi
-
- - name: Restore workflow file
- if: steps.check.outputs.needs_update == 'true'
- run: |
- # Always keep our own workflow file, never let upstream overwrite it
- git checkout HEAD@{1} -- .github/workflows/sync-upstream.yml 2>/dev/null || true
- if ! git diff --cached --quiet; then
- git commit -m "chore: restore sync-upstream workflow after sync"
- fi
-
- - name: Push
- if: steps.check.outputs.needs_update == 'true'
- run: |
- if [ "${{ steps.resolve.outputs.mode }}" = "manual" ]; then
- git push origin main --force
- else
- git push origin main
- fi
-
- - name: Summary
- run: |
- if [ "${{ steps.check.outputs.needs_update }}" = "true" ]; then
- echo "### Synced successfully" >> $GITHUB_STEP_SUMMARY
- echo "- **Mode:** ${{ steps.resolve.outputs.mode }}" >> $GITHUB_STEP_SUMMARY
- echo "- **Tag:** ${{ steps.resolve.outputs.latest_tag || 'N/A (manual)' }}" >> $GITHUB_STEP_SUMMARY
- echo "- **Commit:** \`${{ steps.resolve.outputs.target_sha }}\`" >> $GITHUB_STEP_SUMMARY
- else
- echo "### Nothing to update" >> $GITHUB_STEP_SUMMARY
- fi
diff --git a/.gitignore b/.gitignore
index b83ab26..547d6e6 100644
--- a/.gitignore
+++ b/.gitignore
@@ -18,6 +18,7 @@ build/
.idea/
*.swp
*.swo
+docs/
# OS
.DS_Store
@@ -42,7 +43,7 @@ tmp/
.tmp/
.tmp-bitwarden-clients/
-nodewarden.wiki/
+nodewarden-wiki/
wiki/
AGENTS.md
settings.json
@@ -55,9 +56,11 @@ NodeWarden-compat/
.codex-upstream/bitwarden-browser/
.reasonix/
+.upstream/
# Compatibility analysis documents
BITWARDEN_COMPATIBILITY_ANALYSIS.md
+security-audits/
.mcp.json
opencode.jsonc
.cursor/
diff --git a/README.md b/README.md
index 79715bd..c025586 100644
--- a/README.md
+++ b/README.md
@@ -3,95 +3,102 @@
- 运行在 Cloudflare Workers 上的 Bitwarden 兼容服务端
+ Bitwarden-compatible server running on Cloudflare Workers
 -
 +
- Telegram 频道 |
- Telegram 群组
+ Telegram Channel |
+ Telegram Group
- English |
- 贡献指南
+ 中文 |
+ Contributing |
+ Official wiki
-> **免责声明**
-> 本项目仅供学习与交流使用,请定期备份你的密码库。
-> 本项目与 Bitwarden 官方无关,请不要向 Bitwarden 官方反馈 NodeWarden 的问题。
+> **Disclaimer**
+> This project is for learning and discussion purposes only. Please back up your vault regularly.
+> This project is not affiliated with Bitwarden. Please do not report NodeWarden issues to the official Bitwarden team.
---
-## 与 Bitwarden 官方服务端能力对比
+## Feature comparison with the official Bitwarden server
-| 能力 | Bitwarden | NodeWarden | 说明 |
+| Feature | Bitwarden Free | NodeWarden | Notes |
|---|---|---|---|
-| 网页密码库 | ✅ | ✅ | **原创Web Vault界面** |
-| **PWA 支持** | ⚠️ 基础 | ✅ | **可安装、离线使用、App快捷方式** |
-| **Web Vault 离线查看** | ❌ | ✅ | **网页端支持离线查看保险库** |
-| **Passkey 登录** | ✅ | ✅ | **支持WebAuthn/FIDO2无密码登录** |
-| 全量同步 `/api/sync` | ✅ | ✅ | 已针对官方客户端做兼容优化 |
-| 附件上传 / 下载 | ✅ | ✅ | Cloudflare R2 或 KV |
-| Send | ✅ | ✅ | 支持文本与文件 Send |
-| 导入 / 导出 | ✅ | ✅ | 支持 Bitwarden JSON / CSV / **ZIP 导入(包括附件)** |
-| **云端备份中心** | ❌ | ✅ | **支持 WebDAV / S3 定时备份(OneDrive/Google Drive等)** |
-| 密码提示(网页端) | ⚠️ 有限 | ✅ | **无需发送邮件** |
-| TOTP / Steam TOTP | ✅ | ✅ | 含 `steam://` 支持 |
-| 多用户 | ✅ | ✅ | 支持邀请码注册 |
-| 组织 / 集合 / 成员权限 | ✅ | ❌ | 未实现 |
-| 登录 2FA | ✅ | ⚠️ 部分支持 | 支持TOTP和Passkey(作为第二因素) |
-| SSO / SCIM / 企业目录 | ✅ | ❌ | 未实现 |
+| Web vault | ✅ | ✅ | **Original Web Vault UI** |
+| TOTP | ❌ | ✅ | Includes `steam://` support |
+| **PWA / offline** | ❌ | ✅ | **Installable, offline** |
+| **Passkey login** | ✅ | ✅ | **passwordless auth** |
+| API keys | ✅ | ✅ | CLI keys; create and rotate |
+| Login 2FA | ✅ | ✅ | TOTP, YubiKey, Passkey |
+| 2FA recovery codes | ✅ | ✅ | One-time 2FA disable codes |
+| Real-time push sync | ✅ | ✅ | All device sync |
+| Attachments / Send | ✅ | ✅ | Cloudflare R2 or KV |
+| Import / export | ✅ | ✅ | Bitwarden JSON / CSV / **ZIP** |
+| **Cloud backup center** | ❌ | ✅ | **Scheduled WebDAV / S3 incrementals** |
+| Device management | ✅ | ✅ | **Remove devices; trust controls** |
+| Login requests | ✅ | ✅ | **Cross-device login approval/unlock** |
+| **Multi-user** | ✅ | ✅ | Invite-code registration |
+| Domain rules | ✅ | ✅ | Equivalent domains, global exclusions |
+| Fill-assist | ✅ | ✅ | `POST /fill-assist`|
+| Organizations / collections / roles | ✅ | ❌ | Not implemented |
+| SSO / SCIM / directory | ✅ | ❌ | Not implemented |
---
-## 已测试客户端
+## Tested clients
-- ✅ Windows 桌面端
-- ✅ 手机 App
-- ✅ 浏览器扩展
-- ✅ Linux 桌面端
-- ⚠️ macOS 桌面端尚未完整验证
+- ✅ Windows desktop
+- ✅ Mobile app
+- ✅ Browser extension
+- ✅ Linux desktop
+- ⚠️ macOS desktop not fully verified yet
---
-## 可视化快速部署
+## Visual quick deploy
-1. Fork NodeWarden 仓库到自己的 GitHub 账号
-2. 进入 [Cloudflare Workers & Pages](https://dash.cloudflare.com/?to=/:account/workers-and-pages/create)
-3. 选择 Continue with GitHub 并选择你的仓库
-4. 构建命令填 `npm run build`,部署命令填 `npm run deploy`
-- 如果你打算用 KV 模式,把部署命令改成 `npm run deploy:kv`
-5. 等部署完成后,打开生成的 Workers 域名
+1. Fork the NodeWarden repository to your GitHub account
+2. Open [Cloudflare Workers & Pages](https://dash.cloudflare.com/?to=/:account/workers-and-pages/create)
+3. Choose **Continue with GitHub** and select your fork
+4. Set **build command** to `npm run build` and **deploy command** to `npm run deploy`
+ - For KV mode, change the deploy command to `npm run deploy:kv`
+5. After deployment finishes, open the generated Workers URL
-- Workers 默认域名在部分网络环境不可直连。如需自定义域名,到 [Workers 设置](https://dash.cloudflare.com/?to=/:account/workers/services/view/nodewarden/production/settings)里添加。
+- The default Workers hostname may be unreachable on some networks. To use a custom domain, add it in [Workers settings](https://dash.cloudflare.com/?to=/:account/workers/services/view/nodewarden/production/settings).
-- 页面提示缺少 `JWT_SECRET` 时,到 Workers 设置里添加 Secret。正式环境至少使用 32 个字符以上的随机字符串,不要使用临时值或示例值。
+- If the site reports a missing `JWT_SECRET`, add it as a **Secret** in Workers settings. In production use a random string of at least 32 characters; do not use temporary or example values.
-- 这套流程里,用户实际做的是把代码交给 Cloudflare 构建并部署。代码里的 `wrangler.toml` 或 `wrangler.kv.toml` 决定绑定名,Worker 第一次处理请求时会自动初始化 D1 schema,不需要用户上传 SQL。
+- To hide the Web Vault, add a text variable named `HIDE_WEB_VAULT` with the value `1` under **Workers settings → Variables and Secrets**. While enabled, server-hosted frontend pages and static assets return `404 Not Found`, while the login, sync, attachment, icon, notification, and other server endpoints used by Bitwarden clients remain available; an already installed or cached PWA can continue using its local frontend. Delete the variable (or change it to anything other than `1`) to restore the server-hosted Web Vault.
+
+- In this flow you hand code to Cloudflare to build and deploy. `wrangler.toml` or `wrangler.kv.toml` in the repo defines binding names; the Worker initializes the D1 schema on first request—no manual SQL upload.
> [!TIP]
-> 默认R2与可选KV的区别:
-> | 储存 | 是否需绑卡 | 单个附件/Send文件上限 | 免费额度 |
+> Default R2 vs optional KV:
+> | Storage | Card required | Max single attachment / Send file | Free tier |
> |---|---|---|---|
-> | R2 | 需要 | 100 MB(软限制可更改) | 10 GB |
-> | KV | 不需要 | 25 MiB(Cloudflare限制) | 1 GB |
+> | R2 | Yes | 100 MB (soft limit, adjustable) | 10 GB |
+> | KV | No | 25 MiB (Cloudflare limit) | 1 GB |
-## 更新方法:
-- 手动:打开你 Fork 的 GitHub 仓库,看到顶部同步提示后,点击 `Sync fork` ➜ `Update branch`
-- 自动:进入你的 Fork 仓库 ➜ `Actions` ➜ `Sync upstream` ➜ `Enable workflow`,会在每天凌晨 3 点自动同步上游。
+## How to update
+
+- Manual: open your fork on GitHub; when the sync banner appears, click **Sync fork** → **Update branch**
-## CLI 部署
+
+## CLI deploy
```powershell
git clone https://github.com/shuaiplus/NodeWarden.git
@@ -100,85 +107,46 @@ cd NodeWarden
npm install
npx wrangler login
-# 默认:R2 模式
+# Default: R2 mode
npm run deploy
-# 可选:KV 模式
+# Optional: KV mode
npm run deploy:kv
-# 本地开发
+# Local development
npm run dev
npm run dev:kv
```
---
-## 主要特性
-### PWA 渐进式 Web 应用
-
-- ✅ **可安装到桌面** - 像原生应用一样运行
-- ✅ **离线使用** - Service Worker 缓存,离线也能查看密码
-- ✅ **App 快捷方式** - 快速启动保险库、TOTP代码
-- ✅ **后台解密** - Web Worker 处理解密,不阻塞UI
-
-### Passkey 无密码登录
-
-- ✅ **WebAuthn/FIDO2 支持** - 使用指纹、Face ID等登录
-- ✅ **PRF 密钥解锁** - Passkey 可直接解锁保险库
-- ✅ **官方客户端兼容** - Chromium系浏览器扩展可用Passkey登录
-- ✅ **多设备同步** - 支持iCloud、Google Password Manager等
-
-### 云端备份说明
-
-- 远程备份支持 **WebDAV** 与 **S3**
-- 支持 **OneDrive**(通过Koofr)、**Google Drive**(通过Koofr)、**Cloudflare R2**、**Backblaze B2** 等
-- 勾选”包含附件”后:
- - ZIP 内仍只包含 `db.json` 与 `manifest.json`
- - 真实附件单独存放在 `attachments/`
- - 后续备份会按稳定 blob 名复用已有附件,不会每次全量重传
-- 远程还原时:
- - 会从 `attachments/` 目录按需读取附件
- - 缺失的附件会被安全跳过
- - 被跳过的附件不会在恢复后的数据库中留下脏记录
-
----
-
-## 导入 / 导出
-
-当前支持的导入来源包括:
-
-- Bitwarden JSON
-- Bitwarden CSV
-- Bitwarden 密码库 + 附件 ZIP
-- NodeWarden JSON
-- 网页导入器里可见的多种浏览器 / 密码管理器格式
-
-当前支持的导出方式包括:
-
-- Bitwarden JSON
-- Bitwarden 加密 JSON
-- 带附件的 ZIP 导出
-- NodeWarden JSON 系列
-- 备份中心中的实例级完整手动导出
-
----
-
-
-## 开源协议
+## License
LGPL-3.0 License
---
-## 致谢
+## Credits
-- [Bitwarden](https://bitwarden.com/) - 原始设计与客户端
-- [Vaultwarden](https://github.com/dani-garcia/vaultwarden) - 服务端实现参考
-- [Cloudflare Workers](https://workers.cloudflare.com/) - 无服务器平台
+- [Bitwarden](https://bitwarden.com/) - Original design and clients
+- [Vaultwarden](https://github.com/dani-garcia/vaultwarden) - Server implementation reference
+- [Cloudflare Workers](https://workers.cloudflare.com/) - Serverless platform
---
+## Contributors
+
+
+  +
+
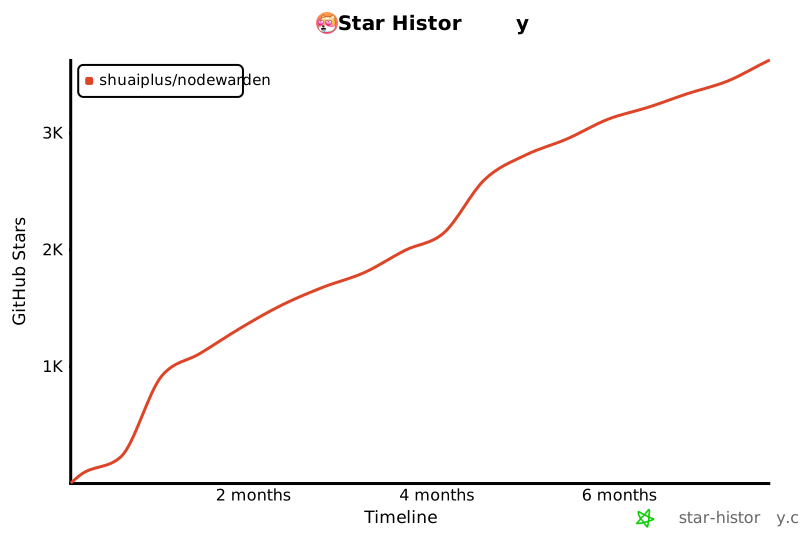
## Star History
-[](https://www.star-history.com/#shuaiplus/NodeWarden&type=timeline&legend=top-left)
+
+
+
+
+
 +
+
diff --git a/README_EN.md b/README_EN.md
deleted file mode 100644
index c60eb82..0000000
--- a/README_EN.md
+++ /dev/null
@@ -1,172 +0,0 @@
-
-  -
-
-
- Bitwarden-compatible server running on Cloudflare Workers
-
-
-
-
-
-
-
-
-
-
-
- Telegram Channel |
- Telegram Group
-
-
-
- 中文说明 |
- Contributing
-
-
-> **Disclaimer**
->
-> This project is for learning and discussion purposes only. Please back up your vault regularly.
->
-> This project is not affiliated with Bitwarden. Please do not report NodeWarden issues to the official Bitwarden team.
-
----
-
-## Feature Comparison with the Official Bitwarden Server
-
-| Capability | Bitwarden | NodeWarden | Notes |
-|---|---|---|---|
-| Web Vault | ✅ | ✅ | **Original Web Vault interface** |
-| **PWA Support** | ⚠️ Basic | ✅ | **Installable, offline-capable, app shortcuts** |
-| **Web Vault Offline Access** | ❌ | ✅ | **Web client supports offline vault viewing** |
-| **Passkey Login** | ✅ | ✅ | **WebAuthn/FIDO2 passwordless login** |
-| Full sync `/api/sync` | ✅ | ✅ | Compatibility optimized for official clients |
-| Attachment upload / download | ✅ | ✅ | Cloudflare R2 or KV |
-| Send | ✅ | ✅ | Supports both text and file Sends |
-| Import / Export | ✅ | ✅ | Supports Bitwarden JSON / CSV / **ZIP import with attachments** |
-| **Cloud Backup Center** | ❌ | ✅ | **WebDAV / S3 scheduled backup (OneDrive/Google Drive etc.)** |
-| Password hint (web) | ⚠️ Limited | ✅ | **No email required** |
-| TOTP / Steam TOTP | ✅ | ✅ | Includes `steam://` support |
-| Multi-user | ✅ | ✅ | Invite-based registration |
-| Organizations / Collections / Member roles | ✅ | ❌ | Not implemented |
-| Login 2FA | ✅ | ⚠️ Partial | TOTP and Passkey (as second factor) |
-| SSO / SCIM / Enterprise directory | ✅ | ❌ | Not implemented |
-
----
-
-## Tested Clients
-
-- ✅ Windows desktop client
-- ✅ Mobile app
-- ✅ Browser extension
-- ✅ Linux desktop client
-- ⚠️ macOS desktop client has not been fully verified yet
-
----
-
-## Web Deploy
-
-1. Fork this repository. If this project helps you, consider giving it a Star.
-2. Open [Workers](https://dash.cloudflare.com/?to=/:account/workers-and-pages/create) -> `Continue with GitHub` -> select your forked repository (`NodeWarden`) -> continue.
-3. R2 is used by default. If R2 is not enabled on your account, you can use KV instead by changing the **deploy command** to `npm run deploy:kv`.
-4. Deploy and open the generated URL.
-
-| Storage | Card required | Single attachment / Send file limit | Free tier |
-|---|---|---|---|
-| R2 | Yes | 100 MB (soft limit, adjustable) | 10 GB |
-| KV | No | 25 MiB (Cloudflare limit) | 1 GB |
-
-> [!TIP]
-> How to keep your fork updated:
-> - Manual: open your fork on GitHub, click `Sync fork`, then `Update branch`
-> - Automatic: go to your fork -> `Actions` -> `Sync upstream` -> `Enable workflow`; it will sync upstream automatically every day at 3 AM
-
-## CLI Deploy
-
-```powershell
-git clone https://github.com/shuaiplus/NodeWarden.git
-cd NodeWarden
-npm install
-npx wrangler login
-
-# Default: R2 mode
-npm run deploy
-
-# Optional: KV mode
-npm run deploy:kv
-
-# Local development
-npm run dev
-npm run dev:kv
-```
-
----
-
-## Key Features
-
-### PWA Progressive Web App
-
-- ✅ **Install to desktop** - Runs like a native app
-- ✅ **Offline usage** - Service Worker caching, view passwords offline
-- ✅ **App shortcuts** - Quick launch vault, TOTP codes
-- ✅ **Background decryption** - Web Worker handles decryption without blocking UI
-
-### Passkey Passwordless Login
-
-- ✅ **WebAuthn/FIDO2 support** - Login with fingerprint, Face ID, etc.
-- ✅ **PRF key unlock** - Passkey can unlock vault directly
-- ✅ **Official client compatibility** - Chromium browser extension supports Passkey login
-- ✅ **Multi-device sync** - Supports iCloud, Google Password Manager, etc.
-
-### Cloud Backup Notes
-
-- Remote backup supports **WebDAV** and **S3**
-- Supports **OneDrive** (via Koofr), **Google Drive** (via Koofr), **Cloudflare R2**, **Backblaze B2**, etc.
-- When `Include attachments` is enabled:
- - the ZIP still contains only `db.json` and `manifest.json`
- - actual attachment files are stored separately under `attachments/`
- - later backups reuse existing attachments by stable blob name instead of re-uploading everything every time
-- During remote restore:
- - required attachment files are loaded from `attachments/` on demand
- - missing attachments are skipped safely
- - skipped attachments do not leave broken rows in the restored database
-
----
-
-## Import / Export
-
-Current supported import sources include:
-
-- Bitwarden JSON
-- Bitwarden CSV
-- Bitwarden vault + attachments ZIP
-- NodeWarden JSON
-- Multiple browser / password-manager formats available in the web import selector
-
-Current supported export formats include:
-
-- Bitwarden JSON
-- Bitwarden encrypted JSON
-- ZIP export with attachments
-- NodeWarden JSON variants
-- Full manual instance export from the backup center
-
----
-
-## License
-
-LGPL-3.0 License
-
----
-
-## Credits
-
-- [Bitwarden](https://bitwarden.com/) - Original design and clients
-- [Vaultwarden](https://github.com/dani-garcia/vaultwarden) - Server implementation reference
-- [Cloudflare Workers](https://workers.cloudflare.com/) - Serverless platform
-
----
-
-## Star History
-
-[](https://www.star-history.com/#shuaiplus/NodeWarden&type=timeline&legend=top-left)
diff --git a/README_ZH.md b/README_ZH.md
new file mode 100644
index 0000000..56fb130
--- /dev/null
+++ b/README_ZH.md
@@ -0,0 +1,151 @@
+
+
+
+
+
+ 运行在 Cloudflare Workers 上的 Bitwarden 兼容服务端
+
+
+
+
+
+
+
+
+
+
+ Telegram 频道 |
+ Telegram 群组
+
+
+
+ English |
+ 贡献指南 |
+ 官方wiki
+
+
+> **免责声明**
+> 本项目仅供学习与交流使用,请定期备份你的密码库。
+> 本项目与 Bitwarden 官方无关,请不要向 Bitwarden 官方反馈 NodeWarden 的问题。
+
+---
+
+## 与 Bitwarden 官方服务端能力对比
+
+| 能力 | Bitwarden免费版 | NodeWarden | 说明 |
+|---|---|---|---|
+| 网页密码库 | ✅ | ✅ | **原创Web Vault界面** |
+| TOTP | ❌ | ✅ | 包括 `steam://` 支持 |
+| **PWA / 离线使用** | ❌ | ✅ | **可安装、离线使用、App快捷方式** |
+| **Passkey 登录** | ✅ | ✅ | **支持WebAuthn/FIDO2无密码登录** |
+| API 密钥 | ✅ | ✅ | 供bitwarden cli使用,支持获取和轮换 |
+| 登录 2FA | ✅ | ✅ | 支持 TOTP、YubiKey、Passkey |
+| 2FA 恢复码 | ✅ | ✅ | 一次性恢复码用于禁用 2FA |
+| 实时推送同步 | ✅ | ✅ | 网页端、浏览器扩展、电脑端和手机端实时同步 |
+| 附件 / Send| ✅ | ✅ | Cloudflare R2 或 KV |
+| 导入 / 导出 | ✅ | ✅ | 支持 Bitwarden JSON / CSV / **ZIP 导入(包括附件)** |
+| **云端备份中心** | ❌ | ✅ | **支持 WebDAV / S3 定时增量备份** |
+| 设备管理 | ✅ | ✅ | **删除设备、撤销信任、永久信任** |
+| 登录请求 | ✅ | ✅ | **多端免密登录审批、跨设备解锁请求** |
+| **多用户使用** | ✅ | ✅ | 支持邀请码注册 |
+| 域名规则 | ✅ | ✅ | 自定义等效域名、全局域名排除 |
+| Fill-assist | ✅ | ✅ | `POST /fill-assist` 辅助客户端自动填充;不能绕过保险库解锁 |
+| 组织 / 集合 / 成员权限 | ✅ | ❌ | 未实现 |
+| SSO / SCIM / 企业目录 | ✅ | ❌ | 未实现 |
+
+---
+
+## 已测试客户端
+
+- ✅ Windows 桌面端
+- ✅ 手机 App
+- ✅ 浏览器扩展
+- ✅ Linux 桌面端
+- ⚠️ macOS 桌面端尚未完整验证
+
+---
+
+## 可视化快速部署
+
+1. Fork NodeWarden 仓库到自己的 GitHub 账号
+2. 进入 [Cloudflare Workers & Pages](https://dash.cloudflare.com/?to=/:account/workers-and-pages/create)
+3. 选择 Continue with GitHub 并选择你的仓库
+4. 构建命令填 `npm run build`,部署命令填 `npm run deploy`
+- 如果你打算用 KV 模式,把部署命令改成 `npm run deploy:kv`
+5. 等部署完成后,打开生成的 Workers 域名
+
+- Workers 默认域名在部分网络环境不可直连。如需自定义域名,到 [Workers 设置](https://dash.cloudflare.com/?to=/:account/workers/services/view/nodewarden/production/settings)里添加。
+
+- 页面提示缺少 `JWT_SECRET` 时,到 Workers 设置里添加 Secret。正式环境至少使用 32 个字符以上的随机字符串,不要使用临时值或示例值。
+
+- 如需隐藏 Web Vault,在 Workers 的“设置 → 变量和机密”中添加文本变量 `HIDE_WEB_VAULT`,值设为 `1`。启用后,服务器上的前端页面和静态资源统一返回 `404 Not Found`,Bitwarden 客户端所需的登录、同步、附件、图标、通知等服务端接口仍可使用;已经安装或缓存的 PWA 可以继续使用本地前端。删除该变量(或将值改为非 `1`)即可恢复服务器上的 Web Vault。
+
+- 这套流程里,用户实际做的是把代码交给 Cloudflare 构建并部署。代码里的 `wrangler.toml` 或 `wrangler.kv.toml` 决定绑定名,Worker 第一次处理请求时会自动初始化 D1 schema,不需要用户上传 SQL。
+
+
+> [!TIP]
+> 默认R2与可选KV的区别:
+> | 储存 | 是否需绑卡 | 单个附件/Send文件上限 | 免费额度 |
+> |---|---|---|---|
+> | R2 | 需要 | 100 MB(软限制可更改) | 10 GB |
+> | KV | 不需要 | 25 MiB(Cloudflare限制) | 1 GB |
+
+
+## 更新方法:
+- 手动:打开你 Fork 的 GitHub 仓库,看到顶部同步提示后,点击 `Sync fork` ➜ `Update branch`
+
+
+
+
+## CLI 部署
+
+```powershell
+git clone https://github.com/shuaiplus/NodeWarden.git
+cd NodeWarden
+
+npm install
+npx wrangler login
+
+# 默认:R2 模式
+npm run deploy
+
+# 可选:KV 模式
+npm run deploy:kv
+
+# 本地开发
+npm run dev
+npm run dev:kv
+```
+
+---
+
+
+## 开源协议
+
+LGPL-3.0 License
+
+---
+
+## 致谢
+
+- [Bitwarden](https://bitwarden.com/) - 原始设计与客户端
+- [Vaultwarden](https://github.com/dani-garcia/vaultwarden) - 服务端实现参考
+- [Cloudflare Workers](https://workers.cloudflare.com/) - 无服务器平台
+
+---
+
+## 贡献者
+
+
+
+
+
+## Star History
+
+
+
+
+
+
+
+
diff --git a/RELEASE_NOTES.md b/RELEASE_NOTES.md
new file mode 100644
index 0000000..da91669
--- /dev/null
+++ b/RELEASE_NOTES.md
@@ -0,0 +1,389 @@
+
+
+# v1.8.0 - Deployment Control, Session Reliability, and Compatibility Fixes
+
+### Added
+
+1. **Web Vault visibility control.** Cloudflare Workers deployments can now set `HIDE_WEB_VAULT=1` to return `404 Not Found` for server-hosted Web Vault pages and static assets while keeping Bitwarden login, sync, attachment, icon, notification, and compatibility endpoints available. Removing the variable restores the Web Vault, and already installed or cached PWAs can continue using their local frontend. Commit: [d990b2c](https://github.com/shuaiplus/nodewarden/commit/d990b2c71ff43a43f4598cad715b09c673e87b53).
+
+### Improved
+
+1. **Simpler desktop and mobile navigation.** The Web Vault now uses a consistent grouped sidebar with persistent expanded sections, clearer separation between tools, settings, and system management, and matching mobile settings navigation. This removes the previous layout-mode picker and makes frequently used destinations easier to find. Commit: [e25ec15](https://github.com/shuaiplus/nodewarden/commit/e25ec159bb2cd07ec6b3a794032a8a2978340d3d).
+
+1. **Safer YubiKey validation credential management.** Yubico validation credentials now use centralized, concurrency-safe initialization; only active administrators can view or replace configured credentials, and credential initialization and reconfiguration are recorded in the security audit log. Regular users can still enroll YubiKeys without gaining access to server-wide credentials. Commit: [573451c](https://github.com/shuaiplus/nodewarden/commit/573451c52f02978dee5ab8379ff86e59da805437).
+
+1. **Bitwarden-compatible personal API keys and safer backups.** Personal API keys can now be viewed after master-password verification and rotated without revoking unrelated sessions. Legacy hashed keys continue to authenticate until the user explicitly rotates them, while new backups exclude personal API keys and runtime authentication or device-trust state; older archives remain importable, but that runtime state is intentionally ignored during restore. Commit: [299eda5](https://github.com/shuaiplus/nodewarden/commit/299eda597ff8a07bf0b7ddfb6e3a5e7f800096db).
+
+### Fixed
+
+1. **Unexpected logout during temporary refresh failures.** Refresh sessions now use client-aware sliding lifetimes with an absolute upper bound, and transient network or service failures no longer turn a locked Web Vault into a forced full login. The Web Vault preserves the locked session, shows a retry path, and keeps official desktop, mobile, browser-extension, and web-cookie flows compatible. Commit: [b731a01](https://github.com/shuaiplus/nodewarden/commit/b731a014f1d86552615110cdf543f809a5c6a7e6).
+
+1. **Complete key data required for master-password changes.** Password changes now reject incomplete or inconsistent authentication and unlock data, require the newly wrapped user key, and prevent KDF settings from being changed through the password-only endpoint. This avoids accepting a password update that could leave the account unable to decrypt its vault. Commit: [19de8d6](https://github.com/shuaiplus/nodewarden/commit/19de8d6e5769be463f973c8f2ec4de2e1530005c).
+
+1. **Extended vault item imports preserve their data.** Web imports now correctly map bank accounts, driver's licenses, and passports instead of reducing item types 6-8 to incomplete generic drafts. Import summaries also report these item types by name. Commit: [e943357](https://github.com/shuaiplus/nodewarden/commit/e943357067236deeaa76ac0003020fa986abf2ab).
+
+1. **Reliable bulk folder deletion.** Bulk folder deletion now calculates Cloudflare D1 bind limits correctly and batches the related cipher cleanup and folder removal statements safely, preventing large selections from failing or leaving partially updated folder references. Commit: [63b642b](https://github.com/shuaiplus/nodewarden/commit/63b642b2511207f435546802e197b6842f5c7aca).
+
+1. **Fresh remote backup directory listings.** Opening a remote backup destination now automatically refreshes directory data when the saved cache is older than five minutes, so newly created backup files appear without requiring a manual refresh. Commit: [72d8ec9](https://github.com/shuaiplus/nodewarden/commit/72d8ec9cbadcb1b74d032deb5e5eea96e785d9c4).
+
+---
+
+### 新增
+
+1. **Web Vault 显示开关。** Cloudflare Workers 部署现在可以设置 `HIDE_WEB_VAULT=1`,让服务器托管的 Web Vault 页面和静态资源统一返回 `404 Not Found`,同时继续提供 Bitwarden 客户端所需的登录、同步、附件、图标、通知和兼容接口。删除变量即可恢复 Web Vault,已经安装或缓存的 PWA 仍可继续使用本地前端。提交:[d990b2c](https://github.com/shuaiplus/nodewarden/commit/d990b2c71ff43a43f4598cad715b09c673e87b53)。
+
+### 改进
+
+1. **更简洁的桌面端和移动端导航。** Web Vault 现在统一使用分组侧边栏,并会保存各分组的展开状态;工具、设置和系统管理的层级更加清楚,移动端设置入口也同步调整。原有布局模式选择器已移除,常用功能更容易查找。提交:[e25ec15](https://github.com/shuaiplus/nodewarden/commit/e25ec159bb2cd07ec6b3a794032a8a2978340d3d)。
+
+1. **更安全的 YubiKey 验证凭据管理。** Yubico 验证凭据现在通过统一且可防并发冲突的流程初始化;只有状态正常的管理员能够查看或替换服务器凭据,初始化和重新配置操作也会写入安全审计日志。普通用户仍可绑定 YubiKey,但无法接触服务器级凭据。提交:[573451c](https://github.com/shuaiplus/nodewarden/commit/573451c52f02978dee5ab8379ff86e59da805437)。
+
+1. **兼容 Bitwarden 的个人 API Key 与更安全的备份。** 用户现在可以在验证主密码后查看个人 API Key,并在不撤销无关会话的情况下轮换密钥。旧版哈希密钥在用户主动轮换前仍可继续认证;新备份不再包含个人 API Key、运行中的认证状态或设备信任状态,旧备份仍能导入,但其中这类运行时状态会被主动忽略。提交:[299eda5](https://github.com/shuaiplus/nodewarden/commit/299eda597ff8a07bf0b7ddfb6e3a5e7f800096db)。
+
+### 修复
+
+1. **临时刷新失败导致意外退出登录。** 刷新会话现在根据客户端采用滑动有效期,并保留绝对最长时限;临时网络或服务故障不会再把已锁定的 Web Vault 直接变成完整登录页。Web Vault 会保留锁定会话并提供重试入口,同时兼容官方桌面端、移动端、浏览器扩展和 Web Cookie 会话。提交:[b731a01](https://github.com/shuaiplus/nodewarden/commit/b731a014f1d86552615110cdf543f809a5c6a7e6)。
+
+1. **修改主密码时必须提交完整密钥数据。** 密码修改接口现在会拒绝不完整或不一致的认证与解锁数据,强制要求新的用户密钥包装结果,并禁止通过仅修改密码的接口顺带更改 KDF 设置,避免出现密码已更新但保险库无法解密的账户状态。提交:[19de8d6](https://github.com/shuaiplus/nodewarden/commit/19de8d6e5769be463f973c8f2ec4de2e1530005c)。
+
+1. **扩展保险库条目导入时完整保留数据。** Web 导入现在会正确映射银行账户、驾驶证和护照,不再把类型 6-8 转换为字段缺失的通用草稿;导入结果摘要也会按名称显示这些条目类型。提交:[e943357](https://github.com/shuaiplus/nodewarden/commit/e943357067236deeaa76ac0003020fa986abf2ab)。
+
+1. **可靠的批量文件夹删除。** 批量删除文件夹时现在会正确计算 Cloudflare D1 的绑定参数上限,并安全批处理密码条目引用清理和文件夹删除语句,避免大量选择时失败或留下只更新了一部分的文件夹引用。提交:[63b642b](https://github.com/shuaiplus/nodewarden/commit/63b642b2511207f435546802e197b6842f5c7aca)。
+
+1. **远端备份目录自动显示最新文件。** 打开远端备份目标时,如果已保存的目录缓存超过五分钟,页面会自动获取最新数据,新生成的备份文件无需手动点击刷新即可出现。提交:[72d8ec9](https://github.com/shuaiplus/nodewarden/commit/72d8ec9cbadcb1b74d032deb5e5eea96e785d9c4)。
+
+# v1.7.4 - Password Tools, Localization, and Security Hardening
+
+### Added
+
+1. **Built-in password generator.** The web vault now provides a dedicated generator for creating strong, configurable passwords, including memorable passphrases backed by the EFF word list. Generated values can be used while creating or editing vault items without leaving the app. Commits: [dfc9800](https://github.com/shuaiplus/nodewarden/commit/dfc98008cb58e9ed01b21ba158bb2584291462a3), [fb37679](https://github.com/shuaiplus/nodewarden/commit/fb376797d266003f8e23b64870f3638fde35d428).
+
+1. **Password security dashboard.** A new password-security view scans the vault and reports weak, reused, exposed, and missing two-factor-authentication passwords, helping users prioritize account cleanup. Commit: [99b5027](https://github.com/shuaiplus/nodewarden/commit/99b50275a6a845e6ebbbae4d647350df939457f9).
+
+1. **Duplicate-item selection tools.** Duplicate results are grouped by color and sorted alphabetically, and the vault now lets users select the unique items from a duplicate group for quicker review and cleanup. Commits: [0992170](https://github.com/shuaiplus/nodewarden/commit/099217062a4cb3a3caacce7513354bb388e8d76c), [39d9df7](https://github.com/shuaiplus/nodewarden/commit/39d9df78ea324fb2d1509221606408b1bb610118).
+
+1. **Five additional interface languages.** Finnish, German, French, Italian, and Swedish are now available in the web vault, expanding the supported interface languages to ten. Commits: [dd90d7b](https://github.com/shuaiplus/nodewarden/commit/dd90d7b8b88a8a49ff1423bb36abb4eeb8f2f329), [9caa064](https://github.com/shuaiplus/nodewarden/commit/9caa0644888c25db835f8c5c93b8341ed80a42fe).
+
+### Improved
+
+1. **Passkey unlock and Bitwarden-client compatibility.** Account passkeys can now unlock the web vault directly, and supported FIDO2 origins, worker-routed fill-assist, Android asset-links checks, and web bootstrap paths are recognized more consistently. Commits: [8c65cb2](https://github.com/shuaiplus/nodewarden/commit/8c65cb2e80c6e5454fb53dbd7ea45cb83bf88ef7), [db31792](https://github.com/shuaiplus/nodewarden/commit/db31792cefc0f21fd543faf21407107a53b8dac2).
+
+1. **Clearer offline and Send experiences.** The app now clearly indicates when it is operating offline, Send pages use improved date formatting, and closing dialogs retain their title through the animation to avoid a visual flash. Commits: [aae614a](https://github.com/shuaiplus/nodewarden/commit/aae614a079b5fa151e2bb98506f1b4fceac29072), [04cb475](https://github.com/shuaiplus/nodewarden/commit/04cb4759358b85029e3e32a5cab6ca39cbbef744), [525b773](https://github.com/shuaiplus/nodewarden/commit/525b773cf4799913ac24e34857348e3aa176608b).
+
+1. **Simplified new-device sign-in.** New-device verification is no longer enforced, removing an extra login step for devices that are otherwise able to authenticate successfully. Commit: [14dff8e](https://github.com/shuaiplus/nodewarden/commit/14dff8ee6a59b741d86a42b25451116b120ac404).
+
+### Fixed
+
+1. **Backup destination SSRF protection.** Backup destination validation now rejects IPv6 loopback addresses, closing a path that could otherwise bypass loopback-host safeguards. Commit: [3c581d1](https://github.com/shuaiplus/nodewarden/commit/3c581d1fb1d92da9e00d3ff139c46f080462e6e8).
+
+1. **Sensitive admin actions require the master password.** Administrative operations and device-wipe actions now require master-password confirmation, reducing the impact of an unattended or compromised web session. Commit: [fa611dc](https://github.com/shuaiplus/nodewarden/commit/fa611dc8430fc80744662feaaf3912341d5b63f2).
+
+---
+
+### 新增
+
+1. **内置密码生成器。** Web 保险库现在提供专用的密码生成器,可创建高强度且可配置的密码,也支持基于 EFF 词表的易记口令短语。生成的值可直接用于新建或编辑保险库条目,无需离开应用。提交:[dfc9800](https://github.com/shuaiplus/nodewarden/commit/dfc98008cb58e9ed01b21ba158bb2584291462a3)、[fb37679](https://github.com/shuaiplus/nodewarden/commit/fb376797d266003f8e23b64870f3638fde35d428)。
+
+1. **密码安全仪表板。** 新增的密码安全视图会扫描保险库,并报告弱密码、重复密码、已泄露密码和缺少双因素认证的密码,帮助用户优先处理需要清理的账户。提交:[99b5027](https://github.com/shuaiplus/nodewarden/commit/99b50275a6a845e6ebbbae4d647350df939457f9)。
+
+1. **重复条目选择工具。** 重复项结果会按颜色分组并按字母顺序排序;保险库现在还可以从重复组中选择唯一条目,以便更快地审查和清理。提交:[0992170](https://github.com/shuaiplus/nodewarden/commit/099217062a4cb3a3caacce7513354bb388e8d76c)、[39d9df7](https://github.com/shuaiplus/nodewarden/commit/39d9df78ea324fb2d1509221606408b1bb610118)。
+
+1. **新增五种界面语言。** Web 保险库现在提供芬兰语、德语、法语、意大利语和瑞典语,支持的界面语言扩展至十种。提交:[dd90d7b](https://github.com/shuaiplus/nodewarden/commit/dd90d7b8b88a8a49ff1423bb36abb4eeb8f2f329)、[9caa064](https://github.com/shuaiplus/nodewarden/commit/9caa0644888c25db835f8c5c93b8341ed80a42fe)。
+
+### 改进
+
+1. **通行密钥解锁和 Bitwarden 客户端兼容性。** 账户通行密钥现在可以直接解锁 Web 保险库;同时,对受支持 FIDO2 来源、Worker 路由的 fill-assist、Android asset-links 检查和 Web 启动路径的识别更加一致。提交:[8c65cb2](https://github.com/shuaiplus/nodewarden/commit/8c65cb2e80c6e5454fb53dbd7ea45cb83bf88ef7)、[db31792](https://github.com/shuaiplus/nodewarden/commit/db31792cefc0f21fd543faf21407107a53b8dac2)。
+
+1. **更清晰的离线和 Send 使用体验。** 应用现在会明确提示离线运行状态,Send 页面采用了更好的日期格式,关闭对话框时会在动画期间保留标题,避免视觉闪烁。提交:[aae614a](https://github.com/shuaiplus/nodewarden/commit/aae614a079b5fa151e2bb98506f1b4fceac29072)、[04cb475](https://github.com/shuaiplus/nodewarden/commit/04cb4759358b85029e3e32a5cab6ca39cbbef744)、[525b773](https://github.com/shuaiplus/nodewarden/commit/525b773cf4799913ac24e34857348e3aa176608b)。
+
+1. **简化新设备登录。** 不再强制执行新设备验证,能够正常完成身份验证的设备无需额外登录步骤。提交:[14dff8e](https://github.com/shuaiplus/nodewarden/commit/14dff8ee6a59b741d86a42b25451116b120ac404)。
+
+### 修复
+
+1. **备份目标的 SSRF 防护。** 备份目标校验现在会拒绝 IPv6 回环地址,堵住了可能绕过回环主机保护的路径。提交:[3c581d1](https://github.com/shuaiplus/nodewarden/commit/3c581d1fb1d92da9e00d3ff139c46f080462e6e8)。
+
+1. **敏感管理员操作需要主密码。** 管理员操作和设备擦除操作现在需要确认主密码,降低无人值守或会话遭入侵时的影响。提交:[fa611dc](https://github.com/shuaiplus/nodewarden/commit/fa611dc8430fc80744662feaaf3912341d5b63f2)。
+
+# v1.7.3 - Stronger Two-Step Login and Client Compatibility
+
+### Added
+
+1. **YubiKey OTP and passkey two-step login.** NodeWarden now supports YubiKey OTP as a managed two-factor provider and adds passkey-based two-factor authentication, including setup screens, WebAuthn fallback connector handling, multi-provider login prompts, and safer WebAuthn response normalization. Commits: [f63b745](https://github.com/shuaiplus/nodewarden/commit/f63b745), [c019c93](https://github.com/shuaiplus/nodewarden/commit/c019c93), [e73ae3d](https://github.com/shuaiplus/nodewarden/commit/e73ae3d), [d8cc88d](https://github.com/shuaiplus/nodewarden/commit/d8cc88d).
+
+1. **Bitwarden extended vault item types.** Vault items now cover bank accounts, driver's licenses, and passports in addition to the existing login, card, identity, secure note, and SSH key flows. The web vault can create, display, decrypt, import, and export these item types with clearer sidebar icons. Commits: [109593d](https://github.com/shuaiplus/nodewarden/commit/109593d), [9de0d3b](https://github.com/shuaiplus/nodewarden/commit/9de0d3b).
+
+1. **More Bitwarden client compatibility endpoints.** Added device verification settings, device registration routes, admin auth-request compatibility, fill-assist alignment, and push relay installation handling so more official Bitwarden client flows receive expected responses. Unsupported email verification and KDF routes now return explicit unsupported responses instead of ambiguous failures. Commits: [e376a84](https://github.com/shuaiplus/nodewarden/commit/e376a84), [8b2f98b](https://github.com/shuaiplus/nodewarden/commit/8b2f98b), [f0e5233](https://github.com/shuaiplus/nodewarden/commit/f0e5233), [56b301f](https://github.com/shuaiplus/nodewarden/commit/56b301f), [fd46dff](https://github.com/shuaiplus/nodewarden/commit/fd46dff), [cde4555](https://github.com/shuaiplus/nodewarden/commit/cde4555).
+
+### Improved
+
+1. **TOTP QR scanning and Bitwarden-compatible TOTP behavior.** Uploading TOTP QR codes now falls back to `jsQR` when browser `BarcodeDetector` support is incomplete, handles transparent PNGs correctly, validates uploaded QR images, and throttles camera fallback decoding to reduce CPU usage. TOTP storage and decryption behavior is also aligned more closely with Bitwarden clients. Commits: [b0a679b](https://github.com/shuaiplus/nodewarden/commit/b0a679b), [d024798](https://github.com/shuaiplus/nodewarden/commit/d024798), [73bbe8b](https://github.com/shuaiplus/nodewarden/commit/73bbe8b), [6e72220](https://github.com/shuaiplus/nodewarden/commit/6e72220), [8a5b210](https://github.com/shuaiplus/nodewarden/commit/8a5b210).
+
+1. **Settings, device management, and localization polish.** Device management now lives inside Settings with updated navigation, the two-step provider UI is more responsive, and new settings, audit-log, and validation messages are localized across supported languages. This makes the security settings area easier to scan on desktop and mobile. Commits: [c7eb6c6](https://github.com/shuaiplus/nodewarden/commit/c7eb6c6), [062c966](https://github.com/shuaiplus/nodewarden/commit/062c966), [12af18e](https://github.com/shuaiplus/nodewarden/commit/12af18e), [c53d71f](https://github.com/shuaiplus/nodewarden/commit/c53d71f), [01ff627](https://github.com/shuaiplus/nodewarden/commit/01ff627).
+
+1. **Encrypted Send password visibility and editing.** Password-protected Sends now show a lock indicator in the list, display masked password dots when editing an existing protected Send, and provide a compact trash-icon control for removing the stored password. This makes password state visible without exposing the password itself. Commits: [a870142](https://github.com/shuaiplus/nodewarden/commit/a870142), [ebc8e8e](https://github.com/shuaiplus/nodewarden/commit/ebc8e8e).
+
+1. **Website icon behavior and workflow maintenance.** Website icons are now always available without the old `WEBSITE_ICONS_ENABLED` environment toggle, while icon requests keep privacy protections. The global-domains sync workflow also validates its ref before running. Commits: [57c5ef9](https://github.com/shuaiplus/nodewarden/commit/57c5ef9), [c643874](https://github.com/shuaiplus/nodewarden/commit/c643874), [680e287](https://github.com/shuaiplus/nodewarden/commit/680e287).
+
+### Fixed
+
+1. **Authentication, token, and rate-limit hardening.** API keys are stored as hashes, password rotation and JWT handling were tightened, user cache invalidates on token handling, remembered 2FA tokens survive a bad password attempt, the current access-token session is revoked correctly, and known rate-limit reset bypasses were closed. Commits: [1545881](https://github.com/shuaiplus/nodewarden/commit/1545881), [439683d](https://github.com/shuaiplus/nodewarden/commit/439683d), [60dd298](https://github.com/shuaiplus/nodewarden/commit/60dd298), [d9a36fe](https://github.com/shuaiplus/nodewarden/commit/d9a36fe), [1bad32f](https://github.com/shuaiplus/nodewarden/commit/1bad32f), [2df43cc](https://github.com/shuaiplus/nodewarden/commit/2df43cc), [ae168be](https://github.com/shuaiplus/nodewarden/commit/ae168be).
+
+1. **User data isolation and request validation.** Storage reads are scoped by user, Send file routes gate access more strictly, anonymous notification hub requests are validated, and multipart backup/upload requests now have caps. This reduces the chance of cross-user data reads or oversized requests reaching deeper handlers. Commits: [baf5699](https://github.com/shuaiplus/nodewarden/commit/baf5699), [8c481a1](https://github.com/shuaiplus/nodewarden/commit/8c481a1), [23c53bd](https://github.com/shuaiplus/nodewarden/commit/23c53bd), [5142846](https://github.com/shuaiplus/nodewarden/commit/5142846).
+
+1. **Backup, restore, and download safety.** Remote backup deletes are verified, archives and backup blobs are validated before use, destination secrets are redacted from settings responses, backup/download token flows are harder to misuse, and WebAuthn credential purpose survives backup export/import. A backup uploader redirect guard was also reverted to restore compatible remote behavior. Commits: [0cef6a0](https://github.com/shuaiplus/nodewarden/commit/0cef6a0), [00e0ec0](https://github.com/shuaiplus/nodewarden/commit/00e0ec0), [5c8f01b](https://github.com/shuaiplus/nodewarden/commit/5c8f01b), [cc4a830](https://github.com/shuaiplus/nodewarden/commit/cc4a830), [f532d3a](https://github.com/shuaiplus/nodewarden/commit/f532d3a), [a366acb](https://github.com/shuaiplus/nodewarden/commit/a366acb).
+
+1. **Import compatibility and encrypted-field validation.** Imports now validate payload structure and ZIP entries before processing, and plaintext FIDO2 credential, SSH key, and password-history fields are rejected instead of being silently accepted and later dropped. This makes failed imports clearer and protects encrypted vault fields from incompatible plaintext data. Commits: [cf14704](https://github.com/shuaiplus/nodewarden/commit/cf14704), [1ec6ed4](https://github.com/shuaiplus/nodewarden/commit/1ec6ed4).
+
+1. **Admin, audit, WebAuthn, and backup endpoint edge cases.** Admin audit-clears are recorded, passkey 2FA status is reported correctly, WebAuthn extension origins are constrained, and auth-request plus backup endpoint checks were tightened around sensitive flows. Commits: [d028b19](https://github.com/shuaiplus/nodewarden/commit/d028b19), [ace00e8](https://github.com/shuaiplus/nodewarden/commit/ace00e8), [7ac6ae5](https://github.com/shuaiplus/nodewarden/commit/7ac6ae5).
+
+---
+
+### 新增
+
+1. **YubiKey OTP 和通行密钥两步登录。** NodeWarden 现在支持将 YubiKey OTP 作为可管理的双因素提供商,并新增基于通行密钥的双因素认证,包含设置界面、WebAuthn 备用连接器处理、多提供商登录提示,以及更安全的 WebAuthn 响应规范化。提交:[f63b745](https://github.com/shuaiplus/nodewarden/commit/f63b745)、[c019c93](https://github.com/shuaiplus/nodewarden/commit/c019c93)、[e73ae3d](https://github.com/shuaiplus/nodewarden/commit/e73ae3d)、[d8cc88d](https://github.com/shuaiplus/nodewarden/commit/d8cc88d)。
+
+1. **Bitwarden 扩展保险库条目类型。** 除现有登录、银行卡、身份、安全笔记和 SSH 密钥流程外,保险库条目现在还覆盖银行账户、驾驶证和护照。Web 保险库可以创建、展示、解密、导入和导出这些条目类型,并提供更清晰的侧边栏图标。提交:[109593d](https://github.com/shuaiplus/nodewarden/commit/109593d)、[9de0d3b](https://github.com/shuaiplus/nodewarden/commit/9de0d3b)。
+
+1. **更多 Bitwarden 客户端兼容端点。** 新增设备验证设置、设备注册路由、管理员认证请求兼容、fill-assist 对齐和推送中继安装处理,让更多官方 Bitwarden 客户端流程能获得预期响应。不支持的邮箱验证和 KDF 路由现在会返回明确的不支持响应,而不是含糊失败。提交:[e376a84](https://github.com/shuaiplus/nodewarden/commit/e376a84)、[8b2f98b](https://github.com/shuaiplus/nodewarden/commit/8b2f98b)、[f0e5233](https://github.com/shuaiplus/nodewarden/commit/f0e5233)、[56b301f](https://github.com/shuaiplus/nodewarden/commit/56b301f)、[fd46dff](https://github.com/shuaiplus/nodewarden/commit/fd46dff)、[cde4555](https://github.com/shuaiplus/nodewarden/commit/cde4555)。
+
+### 改进
+
+1. **TOTP 二维码扫描和 Bitwarden 兼容 TOTP 行为。** 上传 TOTP 二维码时,如果浏览器 `BarcodeDetector` 支持不完整,现在会回退到 `jsQR`,并正确处理透明 PNG、校验上传的二维码图片、限制摄像头回退解码频率以降低 CPU 占用。TOTP 的存储和解密行为也更贴近 Bitwarden 客户端。提交:[b0a679b](https://github.com/shuaiplus/nodewarden/commit/b0a679b)、[d024798](https://github.com/shuaiplus/nodewarden/commit/d024798)、[73bbe8b](https://github.com/shuaiplus/nodewarden/commit/73bbe8b)、[6e72220](https://github.com/shuaiplus/nodewarden/commit/6e72220)、[8a5b210](https://github.com/shuaiplus/nodewarden/commit/8a5b210)。
+
+1. **设置、设备管理和本地化打磨。** 设备管理现在整合进设置页并更新了导航,两步验证提供商界面在响应式布局下更顺手,新的设置、审计日志和校验消息也补齐了受支持语言的本地化。安全设置区域在桌面和移动端都更容易浏览。提交:[c7eb6c6](https://github.com/shuaiplus/nodewarden/commit/c7eb6c6)、[062c966](https://github.com/shuaiplus/nodewarden/commit/062c966)、[12af18e](https://github.com/shuaiplus/nodewarden/commit/12af18e)、[c53d71f](https://github.com/shuaiplus/nodewarden/commit/c53d71f)、[01ff627](https://github.com/shuaiplus/nodewarden/commit/01ff627)。
+
+1. **加密 Send 的密码状态展示与编辑。** 受密码保护的 Send 现在会在列表中显示锁定标记,编辑已有受保护 Send 时会显示密码掩码圆点,并提供紧凑的垃圾桶图标用于移除已保存密码。这样可以看清密码状态,同时不暴露密码本身。提交:[a870142](https://github.com/shuaiplus/nodewarden/commit/a870142)、[ebc8e8e](https://github.com/shuaiplus/nodewarden/commit/ebc8e8e)。
+
+1. **网站图标行为和工作流维护。** 网站图标现在无需旧的 `WEBSITE_ICONS_ENABLED` 环境开关即可始终可用,同时图标请求仍保留隐私保护。global-domains 同步工作流也会在运行前校验引用。提交:[57c5ef9](https://github.com/shuaiplus/nodewarden/commit/57c5ef9)、[c643874](https://github.com/shuaiplus/nodewarden/commit/c643874)、[680e287](https://github.com/shuaiplus/nodewarden/commit/680e287)。
+
+### 修复
+
+1. **认证、令牌和速率限制加固。** API key 现在以哈希形式存储,密码轮换和 JWT 处理更严格,令牌处理时会使用户缓存失效,错误密码不会丢失已记住的 2FA token,当前访问令牌会被正确撤销,并关闭了已知的速率限制重置绕过路径。提交:[1545881](https://github.com/shuaiplus/nodewarden/commit/1545881)、[439683d](https://github.com/shuaiplus/nodewarden/commit/439683d)、[60dd298](https://github.com/shuaiplus/nodewarden/commit/60dd298)、[d9a36fe](https://github.com/shuaiplus/nodewarden/commit/d9a36fe)、[1bad32f](https://github.com/shuaiplus/nodewarden/commit/1bad32f)、[2df43cc](https://github.com/shuaiplus/nodewarden/commit/2df43cc)、[ae168be](https://github.com/shuaiplus/nodewarden/commit/ae168be)。
+
+1. **用户数据隔离和请求校验。** 存储读取现在按用户限定范围,Send 文件路由更严格地拦截访问,匿名通知 hub 请求会被校验,并且多段备份/上传请求增加了上限。这降低了跨用户数据读取或超大请求进入深层处理器的风险。提交:[baf5699](https://github.com/shuaiplus/nodewarden/commit/baf5699)、[8c481a1](https://github.com/shuaiplus/nodewarden/commit/8c481a1)、[23c53bd](https://github.com/shuaiplus/nodewarden/commit/23c53bd)、[5142846](https://github.com/shuaiplus/nodewarden/commit/5142846)。
+
+1. **备份、恢复和下载安全性。** 远端备份删除现在会被验证,归档和备份 blob 使用前会校验,目标配置里的密钥会在设置响应中脱敏,备份/下载令牌流程更难被误用,WebAuthn 凭据用途也会在备份导出/导入中保留。备份上传器的重定向防护也已回退,以恢复兼容的远端行为。提交:[0cef6a0](https://github.com/shuaiplus/nodewarden/commit/0cef6a0)、[00e0ec0](https://github.com/shuaiplus/nodewarden/commit/00e0ec0)、[5c8f01b](https://github.com/shuaiplus/nodewarden/commit/5c8f01b)、[cc4a830](https://github.com/shuaiplus/nodewarden/commit/cc4a830)、[f532d3a](https://github.com/shuaiplus/nodewarden/commit/f532d3a)、[a366acb](https://github.com/shuaiplus/nodewarden/commit/a366acb)。
+
+1. **导入兼容性和加密字段校验。** 导入流程现在会在处理前校验 payload 结构和 ZIP 条目,明文 FIDO2 凭据、SSH 密钥和密码历史字段会被拒绝,而不是先被静默接受再在响应时丢弃。这让失败导入更清楚,也保护加密保险库字段不接收不兼容的明文数据。提交:[cf14704](https://github.com/shuaiplus/nodewarden/commit/cf14704)、[1ec6ed4](https://github.com/shuaiplus/nodewarden/commit/1ec6ed4)。
+
+1. **管理员、审计、WebAuthn 和备份端点边界情况。** 管理员清空审计日志会被记录,通行密钥 2FA 状态会正确上报,WebAuthn 扩展来源会受到限制,并且认证请求与备份端点围绕敏感流程的校验也更严格。提交:[d028b19](https://github.com/shuaiplus/nodewarden/commit/d028b19)、[ace00e8](https://github.com/shuaiplus/nodewarden/commit/ace00e8)、[7ac6ae5](https://github.com/shuaiplus/nodewarden/commit/7ac6ae5)。
+
+---
+
+# v1.7.2 - New Backup Providers, WebAuthn PRF, and UI Polish
+
+### Added
+
+1. **Three new S3-compatible backup providers: Backblaze B2, Cloudflare R2, and Tigris.** Each new destination comes with detailed provider-specific recommendations, storage-class guidance, and localization strings across all five supported languages. You can now back up to more services without custom scripting. Commits: [1acc31e](https://github.com/shuaiplus/nodewarden/commit/1acc31e), [c3dc53b](https://github.com/shuaiplus/nodewarden/commit/c3dc53b), [ff85698](https://github.com/shuaiplus/nodewarden/commit/ff85698).
+
+2. **WebAuthn PRF (pseudorandom function) extension support.** Credential creation and assertion now pass browser-compatible PRF extension requests, support excluding PRF extensions where the client doesn't need them, and handle the underlying passkey operations more robustly. This improves WebAuthn compatibility with modern browsers and password managers that rely on PRF for per-credential keys. Commits: [8942e5b](https://github.com/shuaiplus/nodewarden/commit/8942e5b), [31cfd19](https://github.com/shuaiplus/nodewarden/commit/31cfd19), [6a1a835](https://github.com/shuaiplus/nodewarden/commit/6a1a835), [bf6ac7b](https://github.com/shuaiplus/nodewarden/commit/bf6ac7b).
+
+3. **Backup import locking and checksum verification.** Restoring a full backup now acquires an exclusive lock so concurrent imports cannot collide, and the importer verifies file checksums before applying the data. This makes disaster recovery safer when multiple admins might trigger restores. Commit: [e9272ec](https://github.com/shuaiplus/nodewarden/commit/e9272ec).
+
+4. **Fullscreen layout toggle.** The web vault can now switch to fullscreen mode with a dedicated toggle button, with corresponding localization updates. Useful for kiosk-mode or presentation setups. Commit: [d722815](https://github.com/shuaiplus/nodewarden/commit/d722815).
+
+5. **Fill-assist API handlers.** NodeWarden now implements Bitwarden-compatible credential fill-assist endpoints, letting clients fetch credentials inline via the new `POST /fill-assist` route. Device response types are also updated to include the fields needed by the fill-assist flow. Commit: [e4215b4](https://github.com/shuaiplus/nodewarden/commit/e4215b4).
+
+6. **Device selection and removal in SecurityDevicesPage.** The security devices panel now supports selecting individual trusted devices and removing them directly from the web UI, so you no longer need to use the API to revoke a specific device. Commit: [a5ad16a](https://github.com/shuaiplus/nodewarden/commit/a5ad16a).
+
+7. **Delete invalid organization invitations.** Admins can now detect and remove dangling or invalid invitations from the admin panel, helping keep the invitation list clean. The API also renamed `revokeInvite` to `deleteInvite` for clearer semantics. Commits: [0d1bb19](https://github.com/shuaiplus/nodewarden/commit/0d1bb19), [f82dcc3](https://github.com/shuaiplus/nodewarden/commit/f82dcc3).
+
+8. **validFolderIds support in cipher responses.** Sync and cipher responses now include a `validFolderIds` field so clients can distinguish real folders from orphaned references. The folder repository also validates folder existence more strictly. Commit: [82f968e](https://github.com/shuaiplus/nodewarden/commit/82f968e).
+
+9. **Pending auth request loading state.** The pending login-request panel shows a refreshing indicator while fetching or updating the request list, providing clearer feedback during auth request workflows. Commit: [4378e1b](https://github.com/shuaiplus/nodewarden/commit/4378e1b).
+
+### Improved
+
+1. **Enhanced Bitwarden CSV import with custom field and multiline support.** The CSV parser now recognizes custom fields and restores their metadata correctly during import. It also preserves multiline values such as SSH private keys—previously, any line without a `: ` delimiter was silently dropped, truncating private keys to the first line. Text fields containing newlines now survive a full export-import round-trip. Commits: [5eeaf4e](https://github.com/shuaiplus/nodewarden/commit/5eeaf4e), [68c42a0](https://github.com/shuaiplus/nodewarden/commit/68c42a0).
+
+2. **Consolidated security devices UI.** Device management and authorized devices sections are merged into a single coherent card on SecurityDevicesPage, and the pending-auth-requests panel has been removed from the general SettingsPage to reduce clutter. The device list also includes improved selection controls. Commit: [c694f1b](https://github.com/shuaiplus/nodewarden/commit/c694f1b).
+
+3. **Refined app-shell styles and dark mode consistency.** Removed redundant global styles, cleaned up shell component spacing, and improved dark-mode visual consistency across the header, sidebar, and main content areas. Commit: [1bfb9a6](https://github.com/shuaiplus/nodewarden/commit/1bfb9a6).
+
+4. **Backup and restore error messages across all locales.** New error strings for backup/restore edge cases—lock failures, checksum mismatches, missing files—are now localized in all five supported languages (en, es, ru, zh-CN, zh-TW), with improved UI prompts for backup browser refresh scenarios. Commit: [4cd9ad0](https://github.com/shuaiplus/nodewarden/commit/4cd9ad0).
+
+5. **Updated project wiki link and removed obsolete security scripts.** The issue-template wiki link now points to the correct URL, and the old local security scanning scripts and workflows have been removed in favor of GitHub-native security automation (CodeQL, security-extra workflows). Commit: [e31f82c](https://github.com/shuaiplus/nodewarden/commit/e31f82c).
+
+6. **Security automation and dependency hardening.** Added GitHub-native CodeQL and security-extra workflows, overrode a `ws` vulnerability, and upgraded CI actions to pinned major versions (checkout v7, setup-node v6, create-pull-request v8). Dependencies refreshed include TypeScript 6.0, `@types/node` 26, `lucide-preact` 1.x, and many others across npm and GitHub Actions. Commits: [64f26e7](https://github.com/shuaiplus/nodewarden/commit/64f26e7), [32b3d2a](https://github.com/shuaiplus/nodewarden/commit/32b3d2a), [5dd9dff](https://github.com/shuaiplus/nodewarden/commit/5dd9dff), [8d292ca](https://github.com/shuaiplus/nodewarden/commit/8d292ca), [5bd7dab](https://github.com/shuaiplus/nodewarden/commit/5bd7dab), [99f2d7f](https://github.com/shuaiplus/nodewarden/commit/99f2d7f), [fb9a2ae](https://github.com/shuaiplus/nodewarden/commit/fb9a2ae), [c87e6ac](https://github.com/shuaiplus/nodewarden/commit/c87e6ac).
+
+### Fixed
+
+1. **CSV import truncating multiline field values.** `parseBitwardenCsvFieldLines` previously discarded any line that did not contain a `: ` delimiter, silently dropping SSH private keys and other multiline content to only the first line. The parser now accumulates continuation lines correctly, restoring full private key content through a CSV round-trip. Commit: [68c42a0](https://github.com/shuaiplus/nodewarden/commit/68c42a0).
+
+---
+
+### 新增
+
+1. **三个新的 S3 兼容备份提供商:Backblaze B2、Cloudflare R2 和 Tigris。** 每个新目标都带有详细的提供商建议、存储层级指导和五种语言的本地化字符串,无需额外脚本即可将备份扩展到更多存储服务。提交:[1acc31e](https://github.com/shuaiplus/nodewarden/commit/1acc31e)、[c3dc53b](https://github.com/shuaiplus/nodewarden/commit/c3dc53b)、[ff85698](https://github.com/shuaiplus/nodewarden/commit/ff85698)。
+
+2. **WebAuthn PRF(伪随机函数)扩展支持。** 创建和断言凭证时会传递浏览器兼容的 PRF 扩展请求,支持在不需要时排除 PRF 扩展,并且底层密钥操作更健壮。这改善了与依赖 PRF 做每凭据密钥派生功能的现代浏览器和密码管理器的兼容性。提交:[8942e5b](https://github.com/shuaiplus/nodewarden/commit/8942e5b)、[31cfd19](https://github.com/shuaiplus/nodewarden/commit/31cfd19)、[6a1a835](https://github.com/shuaiplus/nodewarden/commit/6a1a835)、[bf6ac7b](https://github.com/shuaiplus/nodewarden/commit/bf6ac7b)。
+
+3. **备份导入加锁和校验和验证。** 完整恢复备份时现在会获取独占锁,防止并发导入冲突;导入前还会验证文件校验和再应用数据。多管理员可能同时触发恢复时,该机制让灾难恢复更加安全。提交:[e9272ec](https://github.com/shuaiplus/nodewarden/commit/e9272ec)。
+
+4. **全屏布局切换。** Web 保险库现在可以通过专用按钮切换全屏模式,附带对应本地化更新。适合信息亭模式或展示等场景。提交:[d722815](https://github.com/shuaiplus/nodewarden/commit/d722815)。
+
+5. **Fill-assist API 处理器。** NodeWarden 现在实现了与 Bitwarden 兼容的凭据填充辅助端点,客户端可以通过新的 `POST /fill-assist` 路由内联获取凭据。设备响应类型也补上了 fill-assist 流程需要的字段。提交:[e4215b4](https://github.com/shuaiplus/nodewarden/commit/e4215b4)。
+
+6. **安全设备页的设备选择与删除。** 设备面板现在支持在 Web UI 中直接选择单个可信设备并移除,无需通过 API 手动撤销指定设备。提交:[a5ad16a](https://github.com/shuaiplus/nodewarden/commit/a5ad16a)。
+
+7. **删除无效邀请码。** 管理员现在可以在管理面板中检测并删除悬空或无效的邀请,保持邀请列表整洁。API 也将 `revokeInvite` 改名为 `deleteInvite`,语义更清晰。提交:[0d1bb19](https://github.com/shuaiplus/nodewarden/commit/0d1bb19)、[f82dcc3](https://github.com/shuaiplus/nodewarden/commit/f82dcc3)。
+
+8. **密码条目响应增加 validFolderIds。** 同步和密码条目响应现在包含 `validFolderIds` 字段,方便客户端区分真实文件夹和孤立引用;文件夹存储也加强了对文件夹存在性的校验。提交:[82f968e](https://github.com/shuaiplus/nodewarden/commit/82f968e)。
+
+9. **待处理认证请求的加载状态。** 待处理的登录请求面板现在会在获取或更新请求列表时显示刷新指示器,为认证请求操作提供更清晰的反馈。提交:[4378e1b](https://github.com/shuaiplus/nodewarden/commit/4378e1b)。
+
+### 改进
+
+1. **增强的 Bitwarden CSV 导入——自定义字段和多行支持。** CSV 解析器现在可以识别自定义字段并在导入时正确恢复其元数据。同时保留了 SSH 私钥等多行值——之前任何不带 `: ` 分隔符的行都会被丢弃,导致私钥只保留第一行。包含换行符的文本字段现在可以完整通过导出-导入周期。提交:[5eeaf4e](https://github.com/shuaiplus/nodewarden/commit/5eeaf4e)、[68c42a0](https://github.com/shuaiplus/nodewarden/commit/68c42a0)。
+
+2. **整合安全设备界面。** 设备管理和已授权设备两个部分合并为 SecurityDevicesPage 上的一个统一卡片;待处理认证请求面板从 SettingsPage 中移除以减少杂乱。设备列表也改进了选择操作。提交:[c694f1b](https://github.com/shuaiplus/nodewarden/commit/c694f1b)。
+
+3. **精简应用外壳样式与暗色模式一致性。** 移除了冗余全局样式,清理了外壳组件间距,改善了头部、侧边栏和主内容区在暗色模式下的视觉一致性。提交:[1bfb9a6](https://github.com/shuaiplus/nodewarden/commit/1bfb9a6)。
+
+4. **备份/恢复错误消息全语言本地化。** 备份/恢复边界场景(加锁失败、校验和不匹配、文件缺失)的新错误字符串已在五种支持语言(en、es、ru、zh-CN、zh-TW)中完成本地化,同时改进了备份浏览器刷新场景下的界面提示。提交:[4cd9ad0](https://github.com/shuaiplus/nodewarden/commit/4cd9ad0)。
+
+5. **更新项目 Wiki 链接并移除过时安全脚本。** 议题模板中的 Wiki 链接已指向正确 URL;老旧的本地安全扫描脚本和工作流已移除,改用 GitHub 原生安全自动化(CodeQL、security-extra 工作流)。提交:[e31f82c](https://github.com/shuaiplus/nodewarden/commit/e31f82c)。
+
+6. **安全自动化和依赖加固。** 新增 GitHub 原生 CodeQL 和 security-extra 工作流;覆盖了 `ws` 的已知漏洞;将 CI Action 升级到钉死的主要版本(checkout v7、setup-node v6、create-pull-request v8)。依赖升级包括 TypeScript 6.0、`@types/node` 26、`lucide-preact` 1.x,以及 npm 和 GitHub Actions 的多项更新。提交:[64f26e7](https://github.com/shuaiplus/nodewarden/commit/64f26e7)、[32b3d2a](https://github.com/shuaiplus/nodewarden/commit/32b3d2a)、[5dd9dff](https://github.com/shuaiplus/nodewarden/commit/5dd9dff)、[8d292ca](https://github.com/shuaiplus/nodewarden/commit/8d292ca)、[5bd7dab](https://github.com/shuaiplus/nodewarden/commit/5bd7dab)、[99f2d7f](https://github.com/shuaiplus/nodewarden/commit/99f2d7f)、[fb9a2ae](https://github.com/shuaiplus/nodewarden/commit/fb9a2ae)、[c87e6ac](https://github.com/shuaiplus/nodewarden/commit/c87e6ac)。
+
+### 修复
+
+1. **CSV 导入截断多行字段值。** `parseBitwardenCsvFieldLines` 之前会丢弃任何不包含 `: ` 分隔符的行,导致 SSH 私钥等多行内容被静默截断为仅第一行。解析器现已正确累积后续行,使私钥等完整内容能够通过 CSV 导出-导入周期完好保留。提交:[68c42a0](https://github.com/shuaiplus/nodewarden/commit/68c42a0)。
+
+# v1.7.1 - Security Hardening Update
+
+Thanks to GN998 for responsibly reporting security issues addressed in this release.
+
+### Added
+
+1. **No new user-facing features.** This patch release intentionally focuses on security fixes and defensive hardening rather than new product functionality. Commits: [7279668](https://github.com/shuaiplus/nodewarden/commit/7279668), [850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f), [a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c), [23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3).
+
+### Improved
+
+1. **Stronger security defaults.** NodeWarden now applies more conservative handling around sensitive authentication, backup, and file-delivery flows while keeping existing clients compatible. Upgrade is recommended for all deployments. Commits: [7279668](https://github.com/shuaiplus/nodewarden/commit/7279668), [850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f), [a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c), [23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3).
+
+### Fixed
+
+1. **High-priority security fixes.** This release closes multiple reported security issues across sensitive server-side flows and response hardening without exposing operational details in the public notes. Commits: [7279668](https://github.com/shuaiplus/nodewarden/commit/7279668), [850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f), [a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c), [23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3).
+
+2. **Security dependency overrides.** Package overrides were added for selected transitive dependencies so installs resolve to patched versions where applicable. Commit: [0daad46](https://github.com/shuaiplus/nodewarden/commit/0daad46).
+
+---
+
+### 新增
+
+感谢 GN998 负责任地报告了本次发布中修复的安全问题。
+
+1. **没有新增面向用户的功能。** 本次补丁发布刻意专注于安全修复和防护加固,不包含新的产品功能。提交:[7279668](https://github.com/shuaiplus/nodewarden/commit/7279668)、[850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f)、[a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c)、[23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3)。
+
+### 改进
+
+1. **更稳妥的安全默认行为。** NodeWarden 对敏感认证、备份和文件响应流程采用了更保守的处理方式,同时保持现有客户端兼容。建议所有部署尽快升级。提交:[7279668](https://github.com/shuaiplus/nodewarden/commit/7279668)、[850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f)、[a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c)、[23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3)。
+
+### 修复
+
+1. **高优先级安全修复。** 本次发布修复了多项已报告的安全问题,覆盖敏感服务端流程和响应加固;公开说明中不会展开可操作的攻击细节。提交:[7279668](https://github.com/shuaiplus/nodewarden/commit/7279668)、[850fe0f](https://github.com/shuaiplus/nodewarden/commit/850fe0f)、[a2a8f1c](https://github.com/shuaiplus/nodewarden/commit/a2a8f1c)、[23b23f3](https://github.com/shuaiplus/nodewarden/commit/23b23f3)。
+
+2. **安全依赖覆盖。** 为部分传递依赖添加了版本覆盖,让安装时尽可能解析到已修复版本。提交:[0daad46](https://github.com/shuaiplus/nodewarden/commit/0daad46)。
+
+# v1.7.0 - Faster Multi-Device Sync, Mobile Push, and a Smoother Vault
+
+
+### Added
+
+1. **Resource-level realtime sync.** NodeWarden now sends Bitwarden-style notifications for cipher, folder, and Send create, update, and delete events. The web app can refresh only the affected resource instead of reloading the full vault every time, and state-changing operations such as attachment uploads, attachment deletes, public Send access counts, and Send file downloads also emit the right updates. Commits: [fe0c66c](https://github.com/shuaiplus/nodewarden/commit/fe0c66c), [42b765b](https://github.com/shuaiplus/nodewarden/commit/42b765b), [045b23f](https://github.com/shuaiplus/nodewarden/commit/045b23f), [46ba8b9](https://github.com/shuaiplus/nodewarden/commit/46ba8b9), [f096681](https://github.com/shuaiplus/nodewarden/commit/f096681).
+
+2. **Bitwarden mobile push relay support.** Devices can now store `push_uuid` and `push_token`, register or unregister through the Bitwarden push relay, and receive mobile push notifications when vault resources change. The database schema includes the new push fields and indexes needed to detect push-capable devices. Commit: [79ed7c9](https://github.com/shuaiplus/nodewarden/commit/79ed7c9).
+
+3. **Bitwarden CSV export.** The web app can now export a Bitwarden-compatible CSV file alongside the existing JSON, encrypted JSON, and attachment ZIP formats. Multiple login URIs are serialized safely, and non-login item types such as cards, identities, and SSH keys are preserved as clearly as possible in field text. Commits: [b024226](https://github.com/shuaiplus/nodewarden/commit/b024226), [a06cb0e](https://github.com/shuaiplus/nodewarden/commit/a06cb0e).
+
+4. **More duplicate detection modes.** Duplicate search can now compare exact item content, login site plus credentials, username plus password, or password alone. Duplicate groups are color-coded, and the mobile vault UI includes the new duplicate mode selector and improved filter controls. Commits: [7b3be2c](https://github.com/shuaiplus/nodewarden/commit/7b3be2c), [b444c0f](https://github.com/shuaiplus/nodewarden/commit/b444c0f).
+
+5. **S3 addressing style selection.** Backup destinations can now choose between path-style and virtual-hosted-style S3 URLs, improving compatibility with more S3-compatible providers and self-hosted object storage. Commit: [a818316](https://github.com/shuaiplus/nodewarden/commit/a818316).
+
+### Improved
+
+1. **Web vault updates feel immediate.** Creating, editing, deleting, archiving, restoring, and moving items; creating or deleting folders; and creating, updating, or deleting Sends now update the local encrypted snapshot, decrypted lists, and revision timestamp directly. This reduces visible lag after successful actions and makes cached vault validation work better with resource-level sync. Commits: [42b765b](https://github.com/shuaiplus/nodewarden/commit/42b765b), [045b23f](https://github.com/shuaiplus/nodewarden/commit/045b23f).
+
+2. **Better Bitwarden client compatibility.** Profile and sync responses now include fields such as `organizationsNew`, `policiesNew`, and `V2UpgradeToken`; `/api/accounts/keys` supports GET; password change and password verification accept newer `authenticationData` and `unlockData` request shapes; and device routes work with both `/api/devices` and `/devices`. Cipher responses also preserve stored `edit`, `viewPassword`, and `permissions` flags instead of resetting them. Commits: [add921b](https://github.com/shuaiplus/nodewarden/commit/add921b), [f9fe532](https://github.com/shuaiplus/nodewarden/commit/f9fe532).
+
+3. **Cleaner mobile and narrow-screen UI.** Topbar controls, network status, theme switching, and lock buttons now share more consistent sizing and styling. The vault list search, sorting, filtering, create button, and bulk selection toolbar are more compact on mobile, and mobile filter menus can switch between all items, favorites, archive, trash, duplicates, types, and folders. Commits: [7e0406f](https://github.com/shuaiplus/nodewarden/commit/7e0406f), [16bde22](https://github.com/shuaiplus/nodewarden/commit/16bde22), [cd2ec82](https://github.com/shuaiplus/nodewarden/commit/cd2ec82), [c1f5795](https://github.com/shuaiplus/nodewarden/commit/c1f5795).
+
+4. **More tolerant TOTP handling.** TOTP codes are grouped more naturally for 5-digit, 6-digit, 8-digit, and other lengths, and the TOTP list no longer overflows narrow screens because of fixed column widths. `otpauth://` parsing is also more tolerant of unusual parameter encoding, with more stable Steam-code detection. Commits: [9e0908f](https://github.com/shuaiplus/nodewarden/commit/9e0908f), [d5c2ab2](https://github.com/shuaiplus/nodewarden/commit/d5c2ab2).
+
+5. **Less jumpy network status.** The web app no longer switches offline after one short failed probe. It uses a longer timeout, waits for repeated failures, and lets normal API successes or failures update the network state, reducing false offline unlock fallbacks when the service is reachable but slow. Commit: [b4dfb04](https://github.com/shuaiplus/nodewarden/commit/b4dfb04).
+
+6. **More complete backups.** Full instance backups now include trusted two-factor device tokens and restore them during import. The importer validates token ownership, device identifiers, expiration times, and duplicates, so remembered two-factor devices can survive a full migration. Commit: [f6169b7](https://github.com/shuaiplus/nodewarden/commit/f6169b7).
+
+### Fixed
+
+1. **Realtime notification correctness.** Resource notification type numbers now match Bitwarden semantics, while NodeWarden-specific device status and backup progress notifications use internal values to avoid conflicts with official Send update types. SignalR MessagePack invocations now include `streamIds`, pending auth request notifications refresh the login request list, and the web app ignores notifications sent by the current device to avoid redundant refreshes. Commits: [fe0c66c](https://github.com/shuaiplus/nodewarden/commit/fe0c66c), [9a21504](https://github.com/shuaiplus/nodewarden/commit/9a21504), [4900de0](https://github.com/shuaiplus/nodewarden/commit/4900de0).
+
+2. **Attachment and Send download details.** Public attachment and Send file downloads now include `Content-Disposition` filenames and `X-Content-Type-Options: nosniff`, making browser downloads keep better filenames and reducing content sniffing issues. Attachment delete responses now include both uppercase and lowercase field forms for broader client compatibility. Commit: [add921b](https://github.com/shuaiplus/nodewarden/commit/add921b).
+
+3. **Deleted item and bulk action edge cases.** Vault paging now detects deleted items from both database columns and older JSON payload fields, preventing old deleted items from appearing in the normal vault list. Bulk archive skips deleted items, and duplicate detection now uses decrypted password history instead of encrypted stored text. Commits: [add921b](https://github.com/shuaiplus/nodewarden/commit/add921b), [b444c0f](https://github.com/shuaiplus/nodewarden/commit/b444c0f).
+
+4. **Export, dialog, and toast polish.** CSV export now escapes login URIs correctly inside a single CSV cell; some dialog dismissal behavior is more stable; login and unlock success toasts are less noisy; and the toast close button now uses a styled SVG icon. Commits: [b024226](https://github.com/shuaiplus/nodewarden/commit/b024226), [a06cb0e](https://github.com/shuaiplus/nodewarden/commit/a06cb0e), [8f2704f](https://github.com/shuaiplus/nodewarden/commit/8f2704f), [907126d](https://github.com/shuaiplus/nodewarden/commit/907126d).
+
+5. **S3 backup URL construction.** Virtual-hosted-style backup operations now use the `bucket.endpoint` form for upload, download, delete, and existence checks, while avoiding duplicate bucket names when the endpoint already includes the bucket. Path-style mode keeps the existing `endpoint/bucket` behavior. Commit: [a818316](https://github.com/shuaiplus/nodewarden/commit/a818316).
+
+---
+
+### 新增
+
+1. **资源级实时同步。** NodeWarden 现在会按 Bitwarden 风格发送密码条目、文件夹、Send 的新增、更新和删除通知。Web 端收到通知后可以只刷新受影响的资源,而不是每次都重新同步整个保险库;附件上传、附件删除、公开 Send 访问计数、Send 文件下载等会改变状态的操作,也会触发对应更新。提交:[fe0c66c](https://github.com/shuaiplus/nodewarden/commit/fe0c66c)、[42b765b](https://github.com/shuaiplus/nodewarden/commit/42b765b)、[045b23f](https://github.com/shuaiplus/nodewarden/commit/045b23f)、[46ba8b9](https://github.com/shuaiplus/nodewarden/commit/46ba8b9)、[f096681](https://github.com/shuaiplus/nodewarden/commit/f096681)。
+
+2. **Bitwarden 移动端推送中继支持。** 设备现在可以保存 `push_uuid` 和 `push_token`,通过 Bitwarden push relay 注册或注销,并在保险库资源变化时尝试接收移动端推送。数据库结构也补上了推送字段和索引,用于识别哪些设备可以被推送。提交:[79ed7c9](https://github.com/shuaiplus/nodewarden/commit/79ed7c9)。
+
+3. **Bitwarden CSV 导出。** 除了原有 JSON、加密 JSON 和带附件 ZIP 导出,现在 Web 端可以直接导出 Bitwarden 兼容 CSV。多个登录 URI 会按 CSV 规则安全序列化,卡片、身份、SSH Key 等非登录类型也会尽量保留到字段文本中,方便迁移或人工整理。提交:[b024226](https://github.com/shuaiplus/nodewarden/commit/b024226)、[a06cb0e](https://github.com/shuaiplus/nodewarden/commit/a06cb0e)。
+
+4. **更多重复项检测模式。** 重复项现在可以按完全一致、登录站点加凭据、用户名加密码、单独密码等方式判断。重复组会用颜色辅助区分,移动端保险库也补上了重复项模式选择和更完整的筛选入口。提交:[7b3be2c](https://github.com/shuaiplus/nodewarden/commit/7b3be2c)、[b444c0f](https://github.com/shuaiplus/nodewarden/commit/b444c0f)。
+
+5. **S3 地址样式选择。** 远程备份目标现在可以选择 path-style 或 virtual-hosted-style,兼容更多 S3 服务和自建对象存储。提交:[a818316](https://github.com/shuaiplus/nodewarden/commit/a818316)。
+
+### 改进
+
+1. **Web 保险库操作反馈更及时。** 创建、编辑、删除、归档、恢复、移动条目,创建或删除文件夹,以及创建、更新、删除 Send 时,前端会直接更新本地加密快照、解密列表和修订时间。这样操作成功后列表更快跟上,也让资源级同步下的本地缓存校验更稳定。提交:[42b765b](https://github.com/shuaiplus/nodewarden/commit/42b765b)、[045b23f](https://github.com/shuaiplus/nodewarden/commit/045b23f)。
+
+2. **Bitwarden 客户端兼容性更好。** 账户资料和同步响应补齐了 `organizationsNew`、`policiesNew`、`V2UpgradeToken` 等字段;`/api/accounts/keys` 支持 GET;改密和校验密码接口兼容较新的 `authenticationData`、`unlockData` 请求结构;设备路由同时兼容 `/api/devices` 和 `/devices`。密码条目响应也会保留已存储的 `edit`、`viewPassword` 和 `permissions`,避免跨客户端编辑时权限标记被重置。提交:[add921b](https://github.com/shuaiplus/nodewarden/commit/add921b)、[f9fe532](https://github.com/shuaiplus/nodewarden/commit/f9fe532)。
+
+3. **移动端和小屏界面更顺手。** 顶部栏按钮、网络状态、主题切换、锁定按钮的尺寸和样式更统一。保险库列表里的搜索、排序、筛选、创建按钮和批量选择工具栏在移动端更紧凑;移动筛选菜单可以直接切换全部、收藏、归档、回收站、重复项、类型和文件夹。提交:[7e0406f](https://github.com/shuaiplus/nodewarden/commit/7e0406f)、[16bde22](https://github.com/shuaiplus/nodewarden/commit/16bde22)、[cd2ec82](https://github.com/shuaiplus/nodewarden/commit/cd2ec82)、[c1f5795](https://github.com/shuaiplus/nodewarden/commit/c1f5795)。
+
+4. **TOTP 展示和解析更稳。** 验证码会按 5 位、6 位、8 位等不同长度更自然地分组,列表在窄屏下不会再被固定列宽撑破。`otpauth://` 解析也更能容忍特殊参数编码,Steam 类验证码识别更稳定。提交:[9e0908f](https://github.com/shuaiplus/nodewarden/commit/9e0908f)、[d5c2ab2](https://github.com/shuaiplus/nodewarden/commit/d5c2ab2)。
+
+5. **网络状态不再过度敏感。** Web 端不会因为一次短暂探测失败就立刻判定离线,而是延长探测超时并等待连续失败;普通 API 请求成功或失败也会反向更新网络状态。在线但网络较慢时,不容易误进入离线解锁流程。提交:[b4dfb04](https://github.com/shuaiplus/nodewarden/commit/b4dfb04)。
+
+6. **备份内容更完整。** 完整实例备份现在会导出和还原可信二步验证设备令牌。导入时会校验令牌所属用户、设备标识、过期时间和重复项,让“记住此设备”的二步验证状态在完整迁移后也能保留下来。提交:[f6169b7](https://github.com/shuaiplus/nodewarden/commit/f6169b7)。
+
+### 修复
+
+1. **实时通知类型和刷新逻辑。** 资源通知的类型编号调整为与 Bitwarden 官方语义一致,NodeWarden 自定义的设备状态和备份进度通知改用内部编号,避免和官方 Send 更新类型冲突。SignalR MessagePack 调用补齐了 `streamIds`,认证请求通知会刷新待处理登录请求列表,Web 端也会忽略当前设备自己发出的通知,避免重复刷新。提交:[fe0c66c](https://github.com/shuaiplus/nodewarden/commit/fe0c66c)、[9a21504](https://github.com/shuaiplus/nodewarden/commit/9a21504)、[4900de0](https://github.com/shuaiplus/nodewarden/commit/4900de0)。
+
+2. **附件和 Send 文件下载细节。** 公开附件和 Send 文件下载现在会带上 `Content-Disposition` 文件名和 `X-Content-Type-Options: nosniff`,浏览器保存文件时更接近原文件名,也减少类型嗅探问题。删除附件的响应同时提供大小写两套字段,兼容不同客户端读取方式。提交:[add921b](https://github.com/shuaiplus/nodewarden/commit/add921b)。
+
+3. **已删除条目和批量操作边界。** 保险库分页查询现在会同时识别数据库列和历史 JSON 数据里的删除时间,避免旧数据中已删除条目出现在正常列表。批量归档会跳过已删除条目,重复项判断也会使用已解密的密码历史,避免加密文本影响结果。提交:[add921b](https://github.com/shuaiplus/nodewarden/commit/add921b)、[b444c0f](https://github.com/shuaiplus/nodewarden/commit/b444c0f)。
+
+4. **导出、弹窗和提示细节。** CSV 导出中的登录 URI 会按单行 CSV 单元格正确转义;部分弹窗关闭行为更稳定;登录或解锁成功后的 toast 更克制,避免重复提示;toast 关闭按钮换成了 SVG 图标并调整了样式。提交:[b024226](https://github.com/shuaiplus/nodewarden/commit/b024226)、[a06cb0e](https://github.com/shuaiplus/nodewarden/commit/a06cb0e)、[8f2704f](https://github.com/shuaiplus/nodewarden/commit/8f2704f)、[907126d](https://github.com/shuaiplus/nodewarden/commit/907126d)。
+
+5. **S3 备份地址拼接。** 选择 virtual-hosted-style 时,备份上传、下载、删除和存在性检查会使用 `bucket.endpoint` 形式;如果 endpoint 已经带有 bucket,也不会重复拼接 bucket。path-style 仍保持原有 `endpoint/bucket` 形式。提交:[a818316](https://github.com/shuaiplus/nodewarden/commit/a818316)。
diff --git a/SECURITY.md b/SECURITY.md
new file mode 100644
index 0000000..11b9f7d
--- /dev/null
+++ b/SECURITY.md
@@ -0,0 +1,76 @@
+# Security Policy
+
+## Reporting a Vulnerability
+
+Thank you for helping keep NodeWarden safe.
+
+Please **do not report security vulnerabilities through public GitHub issues, discussions, pull requests, or chat groups**.
+
+Use GitHub Private Vulnerability Reporting instead:
+
+1. Open the NodeWarden repository on GitHub.
+2. Go to **Security and quality**.
+3. Click **Report a vulnerability**.
+4. Submit the report privately.
+
+NodeWarden is independent from Bitwarden. Please do not report NodeWarden-specific issues to the official Bitwarden team.
+
+## What to Include
+
+Please include as much detail as possible:
+
+* A clear description of the vulnerability.
+* Steps to reproduce.
+* Affected version, commit, or deployment method.
+* Affected area, such as login, sync, vault data, attachments, Send, import/export, backup/restore, Passkey, WebAuthn, or API routes.
+* Expected behavior and actual behavior.
+* Security impact, such as authentication bypass, authorization bypass, replay, cross-user access, token misuse, data leakage, or secret exposure.
+* Proof of concept, logs, screenshots, or request examples, if safe to share privately.
+
+Please redact real passwords, tokens, private keys, recovery keys, vault data, and other secrets before submitting.
+
+## Scope
+
+Security reports are welcome for issues affecting NodeWarden itself, including:
+
+* Authentication and session handling.
+* User authorization and cross-user access.
+* Vault data, cipher sync, attachments, and Send.
+* Import, export, backup, and restore.
+* Passkey, WebAuthn, and two-factor authentication.
+* Secret handling and provider credentials.
+* Cloudflare Workers, D1, R2, KV, WebDAV, or S3 behavior caused by NodeWarden code or documentation.
+
+## Out of Scope
+
+The following are usually out of scope:
+
+* Issues only affecting third-party services or user infrastructure.
+* Misconfigured personal deployments not caused by NodeWarden defaults.
+* Social engineering or phishing.
+* Denial-of-service testing.
+* Scanner-only reports without a practical exploit path.
+* Reports that only mention outdated dependencies without showing real impact.
+
+## Response
+
+NodeWarden is maintained on a best-effort basis.
+
+We aim to acknowledge valid private reports within 72 hours, investigate the issue, and release a fix or mitigation when appropriate.
+
+Please do not publicly disclose vulnerability details before a fix or mitigation is available.
+
+## Supported Versions
+
+Security fixes are generally provided for the latest release and the latest code on the default branch.
+
+| Version | Supported |
+| -------------- | ---------------------- |
+| Latest release | Yes |
+| `main` branch | Yes |
+| Older releases | Best effort |
+| Modified forks | Not directly supported |
+
+## Rewards
+
+NodeWarden does not currently operate a paid bug bounty program.
diff --git a/migrations/0001_init.sql b/migrations/0001_init.sql
index 6755792..d30dfa6 100644
--- a/migrations/0001_init.sql
+++ b/migrations/0001_init.sql
@@ -31,7 +31,7 @@ CREATE TABLE IF NOT EXISTS users (
security_stamp TEXT NOT NULL,
role TEXT NOT NULL DEFAULT 'user',
status TEXT NOT NULL DEFAULT 'active',
- verify_devices INTEGER NOT NULL DEFAULT 1,
+ verify_devices INTEGER NOT NULL DEFAULT 0,
totp_secret TEXT,
totp_recovery_code TEXT,
api_key TEXT,
@@ -132,6 +132,11 @@ CREATE TABLE IF NOT EXISTS refresh_tokens (
expires_at INTEGER NOT NULL,
device_identifier TEXT,
device_session_stamp TEXT,
+ security_stamp TEXT,
+ created_at INTEGER,
+ last_used_at INTEGER,
+ absolute_expires_at INTEGER,
+ client_type TEXT,
FOREIGN KEY (user_id) REFERENCES users(id) ON DELETE CASCADE
);
CREATE INDEX IF NOT EXISTS idx_refresh_tokens_user ON refresh_tokens(user_id);
@@ -176,6 +181,8 @@ CREATE TABLE IF NOT EXISTS devices (
encrypted_user_key TEXT,
encrypted_public_key TEXT,
encrypted_private_key TEXT,
+ push_uuid TEXT,
+ push_token TEXT,
banned INTEGER NOT NULL DEFAULT 0,
banned_at TEXT,
device_note TEXT,
@@ -187,6 +194,7 @@ CREATE TABLE IF NOT EXISTS devices (
);
CREATE INDEX IF NOT EXISTS idx_devices_user_updated ON devices(user_id, updated_at);
CREATE INDEX IF NOT EXISTS idx_devices_user_last_seen ON devices(user_id, last_seen_at);
+CREATE INDEX IF NOT EXISTS idx_devices_user_push ON devices(user_id, push_token);
CREATE TABLE IF NOT EXISTS auth_requests (
id TEXT PRIMARY KEY,
@@ -225,9 +233,20 @@ CREATE TABLE IF NOT EXISTS trusted_two_factor_device_tokens (
CREATE INDEX IF NOT EXISTS idx_trusted_two_factor_device_tokens_user_device
ON trusted_two_factor_device_tokens(user_id, device_identifier);
+CREATE TABLE IF NOT EXISTS totp_login_replays (
+ user_id TEXT NOT NULL,
+ time_counter INTEGER NOT NULL,
+ consumed_at INTEGER NOT NULL,
+ PRIMARY KEY (user_id, time_counter),
+ FOREIGN KEY (user_id) REFERENCES users(id) ON DELETE CASCADE
+);
+CREATE INDEX IF NOT EXISTS idx_totp_login_replays_consumed_at
+ ON totp_login_replays(consumed_at);
+
CREATE TABLE IF NOT EXISTS webauthn_credentials (
id TEXT PRIMARY KEY,
user_id TEXT NOT NULL,
+ purpose TEXT NOT NULL DEFAULT 'login',
name TEXT NOT NULL,
public_key TEXT NOT NULL,
credential_id TEXT NOT NULL,
diff --git a/package-lock.json b/package-lock.json
index 4601533..8ea6c08 100644
--- a/package-lock.json
+++ b/package-lock.json
@@ -1,41 +1,42 @@
{
"name": "nodewarden",
- "version": "1.5.2",
+ "version": "1.8.0",
"lockfileVersion": 3,
"requires": true,
"packages": {
"": {
"name": "nodewarden",
- "version": "1.5.2",
+ "version": "1.8.0",
"license": "LGPL-3.0",
"dependencies": {
- "@noble/hashes": "^2.0.1",
- "@simplewebauthn/server": "^13.3.1",
- "@tanstack/react-query": "^5.90.21",
- "@zip.js/zip.js": "^2.8.22",
- "fflate": "^0.8.2",
- "lucide-preact": "^0.575.0",
- "preact": "^10.28.4",
+ "@noble/hashes": "^2.2.0",
+ "@simplewebauthn/server": "^13.3.2",
+ "@tanstack/react-query": "^5.101.2",
+ "@zip.js/zip.js": "^2.8.26",
+ "fflate": "^0.8.3",
+ "jsqr": "1.4.0",
+ "lucide-preact": "^1.22.0",
+ "preact": "^10.29.3",
"qrcode-generator": "^2.0.4",
- "wouter": "^3.9.0"
+ "wouter": "^3.10.0"
},
"devDependencies": {
- "@cloudflare/workers-types": "^4.20260131.0",
- "@preact/preset-vite": "^2.10.3",
- "@types/node": "^25.2.3",
- "autoprefixer": "^10.4.21",
- "opencc-js": "^1.0.5",
- "postcss": "^8.5.6",
- "tailwindcss": "^3.4.17",
- "tsx": "^4.21.0",
- "typescript": "^5.9.3",
- "vite": "^7.3.1",
- "wrangler": "^4.71.0"
+ "@cloudflare/workers-types": "^4.20260630.1",
+ "@preact/preset-vite": "^2.10.5",
+ "@types/node": "^26.0.1",
+ "autoprefixer": "^10.5.2",
+ "opencc-js": "^1.3.2",
+ "postcss": "^8.5.23",
+ "tailwindcss": "^3.4.19",
+ "tsx": "^4.22.4",
+ "typescript": "^6.0.3",
+ "vite": "^8.1.3",
+ "wrangler": "^4.105.0"
}
},
"node_modules/@alloc/quick-lru": {
"version": "5.2.0",
- "resolved": "https://registry.npmmirror.com/@alloc/quick-lru/-/quick-lru-5.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/@alloc/quick-lru/-/quick-lru-5.2.0.tgz",
"integrity": "sha512-UrcABB+4bUrFABwbluTIBErXwvbsU/V7TZWfmbgJfbkwiBuziS9gxdODUyuiecfdGQ85jglMW6juS3+z5TsKLw==",
"dev": true,
"license": "MIT",
@@ -48,7 +49,7 @@
},
"node_modules/@babel/code-frame": {
"version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/code-frame/-/code-frame-7.29.0.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/code-frame/-/code-frame-7.29.0.tgz",
"integrity": "sha512-9NhCeYjq9+3uxgdtp20LSiJXJvN0FeCtNGpJxuMFZ1Kv3cWUNb6DOhJwUvcVCzKGR66cw4njwM6hrJLqgOwbcw==",
"dev": true,
"license": "MIT",
@@ -62,59 +63,194 @@
}
},
"node_modules/@babel/compat-data": {
- "version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/compat-data/-/compat-data-7.29.0.tgz",
- "integrity": "sha512-T1NCJqT/j9+cn8fvkt7jtwbLBfLC/1y1c7NtCeXFRgzGTsafi68MRv8yzkYSapBnFA6L3U2VSc02ciDzoAJhJg==",
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/compat-data/-/compat-data-8.0.0.tgz",
+ "integrity": "sha512-DOjnob/cXOUgDOozCDeq/aK2p5y8dUIVdf6tNhEV1HQRd6I8aQ4f4fbtHRVEvb6lP3BGomrKHiS8ICAASSVQSw==",
"dev": true,
"license": "MIT",
"engines": {
- "node": ">=6.9.0"
+ "node": "^22.18.0 || >=24.11.0"
}
},
"node_modules/@babel/core": {
- "version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/core/-/core-7.29.0.tgz",
- "integrity": "sha512-CGOfOJqWjg2qW/Mb6zNsDm+u5vFQ8DxXfbM09z69p5Z6+mE1ikP2jUXw+j42Pf1XTYED2Rni5f95npYeuwMDQA==",
+ "version": "8.0.1",
+ "resolved": "https://registry.npmmirror.com/@babel/core/-/core-8.0.1.tgz",
+ "integrity": "sha512-5FgxM4dLQpMJHSiVATk8foW263dVHQHBVpXYiimNECVWG01f4nFyEbQixeT6Mwvg7TayREJ2gpKl3o2RoMdnqw==",
"dev": true,
"license": "MIT",
"dependencies": {
- "@babel/code-frame": "^7.29.0",
- "@babel/generator": "^7.29.0",
- "@babel/helper-compilation-targets": "^7.28.6",
- "@babel/helper-module-transforms": "^7.28.6",
- "@babel/helpers": "^7.28.6",
- "@babel/parser": "^7.29.0",
- "@babel/template": "^7.28.6",
- "@babel/traverse": "^7.29.0",
- "@babel/types": "^7.29.0",
- "@jridgewell/remapping": "^2.3.5",
+ "@babel/code-frame": "^8.0.0",
+ "@babel/generator": "^8.0.0",
+ "@babel/helper-compilation-targets": "^8.0.0",
+ "@babel/helpers": "^8.0.0",
+ "@babel/parser": "^8.0.0",
+ "@babel/template": "^8.0.0",
+ "@babel/traverse": "^8.0.0",
+ "@babel/types": "^8.0.0",
+ "@types/gensync": "^1.0.5",
"convert-source-map": "^2.0.0",
- "debug": "^4.1.0",
+ "empathic": "^2.0.1",
"gensync": "^1.0.0-beta.2",
+ "import-meta-resolve": "^4.2.0",
"json5": "^2.2.3",
- "semver": "^6.3.1"
+ "obug": "^2.1.1",
+ "semver": "^7.7.3"
},
"engines": {
- "node": ">=6.9.0"
+ "node": "^22.18.0 || >=24.11.0"
},
"funding": {
"type": "opencollective",
"url": "https://opencollective.com/babel"
}
},
- "node_modules/@babel/core/node_modules/semver": {
- "version": "6.3.1",
- "resolved": "https://registry.npmmirror.com/semver/-/semver-6.3.1.tgz",
- "integrity": "sha512-BR7VvDCVHO+q2xBEWskxS6DJE1qRnb7DxzUrogb71CWoSficBxYsiAGd+Kl0mmq/MprG9yArRkyrQxTO6XjMzA==",
+ "node_modules/@babel/core/node_modules/@babel/code-frame": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/code-frame/-/code-frame-8.0.0.tgz",
+ "integrity": "sha512-dYYg153EyN2Ekbqw2zAsbd6/JR+9N2SEoC7YV2GyyqMM7x9bLDTjBD6XBhSMLH0wtIVyJj03jWNriQhaN+eoCw==",
"dev": true,
- "license": "ISC",
- "bin": {
- "semver": "bin/semver.js"
+ "license": "MIT",
+ "dependencies": {
+ "@babel/helper-validator-identifier": "^8.0.0",
+ "js-tokens": "^10.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
}
},
+ "node_modules/@babel/core/node_modules/@babel/generator": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/generator/-/generator-8.0.0.tgz",
+ "integrity": "sha512-NT9NrVwJsbSV6Y2FSstWa71EETOnzrjkL5/wX3D2mYHtKM+qvqB1DvR4D0Setb/gDBsHzRICifwEWMO8CnTF6g==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/parser": "^8.0.0",
+ "@babel/types": "^8.0.0",
+ "@jridgewell/gen-mapping": "^0.3.12",
+ "@jridgewell/trace-mapping": "^0.3.28",
+ "@types/jsesc": "^2.5.0",
+ "jsesc": "^3.0.2"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/helper-globals": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-globals/-/helper-globals-8.0.0.tgz",
+ "integrity": "sha512-lLozHOM6sWWlxNo8CYqHy4MBZeTvHXNgVPBfPOGsjPKUzHC2Az9QwB6gxdQmpwHl6GlQtbGgS+lj5887guDiLw==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/helper-string-parser": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-string-parser/-/helper-string-parser-8.0.0.tgz",
+ "integrity": "sha512-6mJgmFFFIIO82vvoLt9XtRC7/TkzXfts1t/SpRX4IHSzMgqoPYCWesVu1udUPUWioAE/2fcG6WuI8zrkE1gwrg==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/helper-validator-identifier": {
+ "version": "8.0.2",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-validator-identifier/-/helper-validator-identifier-8.0.2.tgz",
+ "integrity": "sha512-9Fr9QeyCAyi1BR1jKZ6uYQ24EIhQUx5ReHfQU7drOE+TPOb+w11/dsqLkMOT2U29OdCT71XajrOT8xDc1C7orA==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/parser": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/parser/-/parser-8.0.0.tgz",
+ "integrity": "sha512-aLxAE+imI9bCcyaPrUDjBv3uSkWieifjLe0kuFOZF0zli0L6GCsTmsePnTr55adbIAgYz2zhN1vnFimCBUYcRQ==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/types": "^8.0.0"
+ },
+ "bin": {
+ "parser": "bin/babel-parser.js"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/template": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/template/-/template-8.0.0.tgz",
+ "integrity": "sha512-eAD0QW/AlbamBbw0FeGiwasbCVPq5ncW0HNVyLP3B9czqLyh4gvw+5JTSNt6le9+ziAU7mqDZsKTHf3jTb4chQ==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/code-frame": "^8.0.0",
+ "@babel/parser": "^8.0.0",
+ "@babel/types": "^8.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/traverse": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/traverse/-/traverse-8.0.0.tgz",
+ "integrity": "sha512-bxTj/W2VclGE6CctlfQOpxg8MPDzXArRqkOBePw8EHfebcjF7fETWSS3BriEECo+UiU/Yblq+xUtSImFu7cTbw==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/code-frame": "^8.0.0",
+ "@babel/generator": "^8.0.0",
+ "@babel/helper-globals": "^8.0.0",
+ "@babel/parser": "^8.0.0",
+ "@babel/template": "^8.0.0",
+ "@babel/types": "^8.0.0",
+ "obug": "^2.1.1"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@babel/types": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/types/-/types-8.0.0.tgz",
+ "integrity": "sha512-K8ponJDxBwDHigkeFqaqT5wLGl4bTlwMafR8k7b5CPxr6Ww+UG9ls8Yx6Tcpboxu97eeGVEEyKcHmEyOwN1vSw==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/helper-string-parser": "^8.0.0",
+ "@babel/helper-validator-identifier": "^8.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/core/node_modules/@jridgewell/trace-mapping": {
+ "version": "0.3.31",
+ "resolved": "https://registry.npmmirror.com/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
+ "integrity": "sha512-zzNR+SdQSDJzc8joaeP8QQoCQr8NuYx2dIIytl1QeBEZHJ9uW6hebsrYgbz8hJwUQao3TWCMtmfV8Nu1twOLAw==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@jridgewell/resolve-uri": "^3.1.0",
+ "@jridgewell/sourcemap-codec": "^1.4.14"
+ }
+ },
+ "node_modules/@babel/core/node_modules/js-tokens": {
+ "version": "10.0.0",
+ "resolved": "https://registry.npmmirror.com/js-tokens/-/js-tokens-10.0.0.tgz",
+ "integrity": "sha512-lM/UBzQmfJRo9ABXbPWemivdCW8V2G8FHaHdypQaIy523snUjog0W71ayWXTjiR+ixeMyVHN2XcpnTd/liPg/Q==",
+ "dev": true,
+ "license": "MIT"
+ },
"node_modules/@babel/generator": {
"version": "7.29.1",
- "resolved": "https://registry.npmmirror.com/@babel/generator/-/generator-7.29.1.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/generator/-/generator-7.29.1.tgz",
"integrity": "sha512-qsaF+9Qcm2Qv8SRIMMscAvG4O3lJ0F1GuMo5HR/Bp02LopNgnZBC/EkbevHFeGs4ls/oPz9v+Bsmzbkbe+0dUw==",
"dev": true,
"license": "MIT",
@@ -131,7 +267,7 @@
},
"node_modules/@babel/generator/node_modules/@jridgewell/trace-mapping": {
"version": "0.3.31",
- "resolved": "https://registry.npmmirror.com/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
+ "resolved": "https://registry.npmjs.org/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
"integrity": "sha512-zzNR+SdQSDJzc8joaeP8QQoCQr8NuYx2dIIytl1QeBEZHJ9uW6hebsrYgbz8hJwUQao3TWCMtmfV8Nu1twOLAw==",
"dev": true,
"license": "MIT",
@@ -142,7 +278,7 @@
},
"node_modules/@babel/helper-annotate-as-pure": {
"version": "7.27.3",
- "resolved": "https://registry.npmmirror.com/@babel/helper-annotate-as-pure/-/helper-annotate-as-pure-7.27.3.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-annotate-as-pure/-/helper-annotate-as-pure-7.27.3.tgz",
"integrity": "sha512-fXSwMQqitTGeHLBC08Eq5yXz2m37E4pJX1qAU1+2cNedz/ifv/bVXft90VeSav5nFO61EcNgwr0aJxbyPaWBPg==",
"dev": true,
"license": "MIT",
@@ -154,35 +290,25 @@
}
},
"node_modules/@babel/helper-compilation-targets": {
- "version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/helper-compilation-targets/-/helper-compilation-targets-7.28.6.tgz",
- "integrity": "sha512-JYtls3hqi15fcx5GaSNL7SCTJ2MNmjrkHXg4FSpOA/grxK8KwyZ5bubHsCq8FXCkua6xhuaaBit+3b7+VZRfcA==",
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-compilation-targets/-/helper-compilation-targets-8.0.0.tgz",
+ "integrity": "sha512-JwculLABZvyPvyLBpwU/E/IbH2uM3mnxNtIJpxnIfb24y1PrdVxK5Dqjle4DpgqpGRnwgC7G8IkzPdSXZrO1Ew==",
"dev": true,
"license": "MIT",
"dependencies": {
- "@babel/compat-data": "^7.28.6",
- "@babel/helper-validator-option": "^7.27.1",
+ "@babel/compat-data": "^8.0.0",
+ "@babel/helper-validator-option": "^8.0.0",
"browserslist": "^4.24.0",
- "lru-cache": "^5.1.1",
- "semver": "^6.3.1"
+ "lru-cache": "^11.0.0",
+ "semver": "^7.7.3"
},
"engines": {
- "node": ">=6.9.0"
- }
- },
- "node_modules/@babel/helper-compilation-targets/node_modules/semver": {
- "version": "6.3.1",
- "resolved": "https://registry.npmmirror.com/semver/-/semver-6.3.1.tgz",
- "integrity": "sha512-BR7VvDCVHO+q2xBEWskxS6DJE1qRnb7DxzUrogb71CWoSficBxYsiAGd+Kl0mmq/MprG9yArRkyrQxTO6XjMzA==",
- "dev": true,
- "license": "ISC",
- "bin": {
- "semver": "bin/semver.js"
+ "node": "^22.18.0 || >=24.11.0"
}
},
"node_modules/@babel/helper-globals": {
"version": "7.28.0",
- "resolved": "https://registry.npmmirror.com/@babel/helper-globals/-/helper-globals-7.28.0.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-globals/-/helper-globals-7.28.0.tgz",
"integrity": "sha512-+W6cISkXFa1jXsDEdYA8HeevQT/FULhxzR99pxphltZcVaugps53THCeiWA8SguxxpSp3gKPiuYfSWopkLQ4hw==",
"dev": true,
"license": "MIT",
@@ -192,7 +318,7 @@
},
"node_modules/@babel/helper-module-imports": {
"version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/helper-module-imports/-/helper-module-imports-7.28.6.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-module-imports/-/helper-module-imports-7.28.6.tgz",
"integrity": "sha512-l5XkZK7r7wa9LucGw9LwZyyCUscb4x37JWTPz7swwFE/0FMQAGpiWUZn8u9DzkSBWEcK25jmvubfpw2dnAMdbw==",
"dev": true,
"license": "MIT",
@@ -204,27 +330,9 @@
"node": ">=6.9.0"
}
},
- "node_modules/@babel/helper-module-transforms": {
- "version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/helper-module-transforms/-/helper-module-transforms-7.28.6.tgz",
- "integrity": "sha512-67oXFAYr2cDLDVGLXTEABjdBJZ6drElUSI7WKp70NrpyISso3plG9SAGEF6y7zbha/wOzUByWWTJvEDVNIUGcA==",
- "dev": true,
- "license": "MIT",
- "dependencies": {
- "@babel/helper-module-imports": "^7.28.6",
- "@babel/helper-validator-identifier": "^7.28.5",
- "@babel/traverse": "^7.28.6"
- },
- "engines": {
- "node": ">=6.9.0"
- },
- "peerDependencies": {
- "@babel/core": "^7.0.0"
- }
- },
"node_modules/@babel/helper-plugin-utils": {
"version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/helper-plugin-utils/-/helper-plugin-utils-7.28.6.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-plugin-utils/-/helper-plugin-utils-7.28.6.tgz",
"integrity": "sha512-S9gzZ/bz83GRysI7gAD4wPT/AI3uCnY+9xn+Mx/KPs2JwHJIz1W8PZkg2cqyt3RNOBM8ejcXhV6y8Og7ly/Dug==",
"dev": true,
"license": "MIT",
@@ -234,7 +342,7 @@
},
"node_modules/@babel/helper-string-parser": {
"version": "7.27.1",
- "resolved": "https://registry.npmmirror.com/@babel/helper-string-parser/-/helper-string-parser-7.27.1.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-string-parser/-/helper-string-parser-7.27.1.tgz",
"integrity": "sha512-qMlSxKbpRlAridDExk92nSobyDdpPijUq2DW6oDnUqd0iOGxmQjyqhMIihI9+zv4LPyZdRje2cavWPbCbWm3eA==",
"dev": true,
"license": "MIT",
@@ -244,7 +352,7 @@
},
"node_modules/@babel/helper-validator-identifier": {
"version": "7.28.5",
- "resolved": "https://registry.npmmirror.com/@babel/helper-validator-identifier/-/helper-validator-identifier-7.28.5.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/helper-validator-identifier/-/helper-validator-identifier-7.28.5.tgz",
"integrity": "sha512-qSs4ifwzKJSV39ucNjsvc6WVHs6b7S03sOh2OcHF9UHfVPqWWALUsNUVzhSBiItjRZoLHx7nIarVjqKVusUZ1Q==",
"dev": true,
"license": "MIT",
@@ -253,32 +361,118 @@
}
},
"node_modules/@babel/helper-validator-option": {
- "version": "7.27.1",
- "resolved": "https://registry.npmmirror.com/@babel/helper-validator-option/-/helper-validator-option-7.27.1.tgz",
- "integrity": "sha512-YvjJow9FxbhFFKDSuFnVCe2WxXk1zWc22fFePVNEaWJEu8IrZVlda6N0uHwzZrUM1il7NC9Mlp4MaJYbYd9JSg==",
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-validator-option/-/helper-validator-option-8.0.0.tgz",
+ "integrity": "sha512-U4Dybxh4WESWHt5XhBeExi4DrY0/DNK1aHpQbsrQXCUbFHuMweT0TpLEWKvaraV2Y6fS+ZXunsZ8zIuZIgvF2Q==",
"dev": true,
"license": "MIT",
"engines": {
- "node": ">=6.9.0"
+ "node": "^22.18.0 || >=24.11.0"
}
},
"node_modules/@babel/helpers": {
- "version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/helpers/-/helpers-7.28.6.tgz",
- "integrity": "sha512-xOBvwq86HHdB7WUDTfKfT/Vuxh7gElQ+Sfti2Cy6yIWNW05P8iUslOVcZ4/sKbE+/jQaukQAdz/gf3724kYdqw==",
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helpers/-/helpers-8.0.0.tgz",
+ "integrity": "sha512-wfbi91pM3py96oIiJEz7qIpyXDytgr9zQC1HEWwlGNVRAEmItuU/0a41ZUKu1sJGyhhOIpc4t5vk4PYzt8wpsg==",
"dev": true,
"license": "MIT",
"dependencies": {
- "@babel/template": "^7.28.6",
- "@babel/types": "^7.28.6"
+ "@babel/template": "^8.0.0",
+ "@babel/types": "^8.0.0"
},
"engines": {
- "node": ">=6.9.0"
+ "node": "^22.18.0 || >=24.11.0"
}
},
+ "node_modules/@babel/helpers/node_modules/@babel/code-frame": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/code-frame/-/code-frame-8.0.0.tgz",
+ "integrity": "sha512-dYYg153EyN2Ekbqw2zAsbd6/JR+9N2SEoC7YV2GyyqMM7x9bLDTjBD6XBhSMLH0wtIVyJj03jWNriQhaN+eoCw==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/helper-validator-identifier": "^8.0.0",
+ "js-tokens": "^10.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/@babel/helper-string-parser": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-string-parser/-/helper-string-parser-8.0.0.tgz",
+ "integrity": "sha512-6mJgmFFFIIO82vvoLt9XtRC7/TkzXfts1t/SpRX4IHSzMgqoPYCWesVu1udUPUWioAE/2fcG6WuI8zrkE1gwrg==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/@babel/helper-validator-identifier": {
+ "version": "8.0.2",
+ "resolved": "https://registry.npmmirror.com/@babel/helper-validator-identifier/-/helper-validator-identifier-8.0.2.tgz",
+ "integrity": "sha512-9Fr9QeyCAyi1BR1jKZ6uYQ24EIhQUx5ReHfQU7drOE+TPOb+w11/dsqLkMOT2U29OdCT71XajrOT8xDc1C7orA==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/@babel/parser": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/parser/-/parser-8.0.0.tgz",
+ "integrity": "sha512-aLxAE+imI9bCcyaPrUDjBv3uSkWieifjLe0kuFOZF0zli0L6GCsTmsePnTr55adbIAgYz2zhN1vnFimCBUYcRQ==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/types": "^8.0.0"
+ },
+ "bin": {
+ "parser": "bin/babel-parser.js"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/@babel/template": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/template/-/template-8.0.0.tgz",
+ "integrity": "sha512-eAD0QW/AlbamBbw0FeGiwasbCVPq5ncW0HNVyLP3B9czqLyh4gvw+5JTSNt6le9+ziAU7mqDZsKTHf3jTb4chQ==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/code-frame": "^8.0.0",
+ "@babel/parser": "^8.0.0",
+ "@babel/types": "^8.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/@babel/types": {
+ "version": "8.0.0",
+ "resolved": "https://registry.npmmirror.com/@babel/types/-/types-8.0.0.tgz",
+ "integrity": "sha512-K8ponJDxBwDHigkeFqaqT5wLGl4bTlwMafR8k7b5CPxr6Ww+UG9ls8Yx6Tcpboxu97eeGVEEyKcHmEyOwN1vSw==",
+ "dev": true,
+ "license": "MIT",
+ "dependencies": {
+ "@babel/helper-string-parser": "^8.0.0",
+ "@babel/helper-validator-identifier": "^8.0.0"
+ },
+ "engines": {
+ "node": "^22.18.0 || >=24.11.0"
+ }
+ },
+ "node_modules/@babel/helpers/node_modules/js-tokens": {
+ "version": "10.0.0",
+ "resolved": "https://registry.npmmirror.com/js-tokens/-/js-tokens-10.0.0.tgz",
+ "integrity": "sha512-lM/UBzQmfJRo9ABXbPWemivdCW8V2G8FHaHdypQaIy523snUjog0W71ayWXTjiR+ixeMyVHN2XcpnTd/liPg/Q==",
+ "dev": true,
+ "license": "MIT"
+ },
"node_modules/@babel/parser": {
"version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/parser/-/parser-7.29.0.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/parser/-/parser-7.29.0.tgz",
"integrity": "sha512-IyDgFV5GeDUVX4YdF/3CPULtVGSXXMLh1xVIgdCgxApktqnQV0r7/8Nqthg+8YLGaAtdyIlo2qIdZrbCv4+7ww==",
"dev": true,
"license": "MIT",
@@ -294,7 +488,7 @@
},
"node_modules/@babel/plugin-syntax-jsx": {
"version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/plugin-syntax-jsx/-/plugin-syntax-jsx-7.28.6.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/plugin-syntax-jsx/-/plugin-syntax-jsx-7.28.6.tgz",
"integrity": "sha512-wgEmr06G6sIpqr8YDwA2dSRTE3bJ+V0IfpzfSY3Lfgd7YWOaAdlykvJi13ZKBt8cZHfgH1IXN+CL656W3uUa4w==",
"dev": true,
"license": "MIT",
@@ -310,7 +504,7 @@
},
"node_modules/@babel/plugin-transform-react-jsx": {
"version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/plugin-transform-react-jsx/-/plugin-transform-react-jsx-7.28.6.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/plugin-transform-react-jsx/-/plugin-transform-react-jsx-7.28.6.tgz",
"integrity": "sha512-61bxqhiRfAACulXSLd/GxqmAedUSrRZIu/cbaT18T1CetkTmtDN15it7i80ru4DVqRK1WMxQhXs+Lf9kajm5Ow==",
"dev": true,
"license": "MIT",
@@ -330,7 +524,7 @@
},
"node_modules/@babel/plugin-transform-react-jsx-development": {
"version": "7.27.1",
- "resolved": "https://registry.npmmirror.com/@babel/plugin-transform-react-jsx-development/-/plugin-transform-react-jsx-development-7.27.1.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/plugin-transform-react-jsx-development/-/plugin-transform-react-jsx-development-7.27.1.tgz",
"integrity": "sha512-ykDdF5yI4f1WrAolLqeF3hmYU12j9ntLQl/AOG1HAS21jxyg1Q0/J/tpREuYLfatGdGmXp/3yS0ZA76kOlVq9Q==",
"dev": true,
"license": "MIT",
@@ -346,7 +540,7 @@
},
"node_modules/@babel/template": {
"version": "7.28.6",
- "resolved": "https://registry.npmmirror.com/@babel/template/-/template-7.28.6.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/template/-/template-7.28.6.tgz",
"integrity": "sha512-YA6Ma2KsCdGb+WC6UpBVFJGXL58MDA6oyONbjyF/+5sBgxY/dwkhLogbMT2GXXyU84/IhRw/2D1Os1B/giz+BQ==",
"dev": true,
"license": "MIT",
@@ -361,7 +555,7 @@
},
"node_modules/@babel/traverse": {
"version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/traverse/-/traverse-7.29.0.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/traverse/-/traverse-7.29.0.tgz",
"integrity": "sha512-4HPiQr0X7+waHfyXPZpWPfWL/J7dcN1mx9gL6WdQVMbPnF3+ZhSMs8tCxN7oHddJE9fhNE7+lxdnlyemKfJRuA==",
"dev": true,
"license": "MIT",
@@ -380,7 +574,7 @@
},
"node_modules/@babel/types": {
"version": "7.29.0",
- "resolved": "https://registry.npmmirror.com/@babel/types/-/types-7.29.0.tgz",
+ "resolved": "https://registry.npmjs.org/@babel/types/-/types-7.29.0.tgz",
"integrity": "sha512-LwdZHpScM4Qz8Xw2iKSzS+cfglZzJGvofQICy7W7v4caru4EaAmyUuO6BGrbyQ2mYV11W0U8j5mBhd14dd3B0A==",
"dev": true,
"license": "MIT",
@@ -419,9 +613,9 @@
}
},
"node_modules/@cloudflare/workerd-darwin-64": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workerd-darwin-64/-/workerd-darwin-64-1.20260603.1.tgz",
- "integrity": "sha512-cEXDWu6V3ZrpmwWkM4OJE9AeXjdAgOY5rh8EHhcBVCuP5rxnzUbPzLtrVOHx0UUUAcCrFq0Xsa6mZKL1VUZsKQ==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workerd-darwin-64/-/workerd-darwin-64-1.20260625.1.tgz",
+ "integrity": "sha512-naCfBv0WnnTQIQPTniqMoUlklOIFjrAcSn1X+IAOhY8aFLF/xGYtFjs1eEE8sFib3ZuChGGpU23FFORVczqr0A==",
"cpu": [
"x64"
],
@@ -436,9 +630,9 @@
}
},
"node_modules/@cloudflare/workerd-darwin-arm64": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workerd-darwin-arm64/-/workerd-darwin-arm64-1.20260603.1.tgz",
- "integrity": "sha512-uBPK4LaWJNbbCYwPnUAehlHbbVulhVZPZsdcAhBPfZhHb3QAuAEPAQepO/P67R3V6Cni4YGx1fLbL8A5wwoaNA==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workerd-darwin-arm64/-/workerd-darwin-arm64-1.20260625.1.tgz",
+ "integrity": "sha512-jmH6zjp6Wrux46+qtFwDwrj+vd7s5bdwEqeGvdnwE0a4IEeAhKs0L42HQOyID+g5lkrHq9m55+AbhtmRAm63Pw==",
"cpu": [
"arm64"
],
@@ -453,9 +647,9 @@
}
},
"node_modules/@cloudflare/workerd-linux-64": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workerd-linux-64/-/workerd-linux-64-1.20260603.1.tgz",
- "integrity": "sha512-ht9l6/8Tk7Rp6kA4S9oFZ4X8u0VjnnFdmU/6B3fnABYKREYTKh2RdOqXqXxcp5eNJseireKnWik/hQOPK1CutQ==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workerd-linux-64/-/workerd-linux-64-1.20260625.1.tgz",
+ "integrity": "sha512-MiQkpA/dX8d83Zp64pzHUKfd6ca4cvwxnNobSP6CnXvfESvnNI9pfa+nfwnParla36sPmnYntNkjR7NjRuDeKQ==",
"cpu": [
"x64"
],
@@ -470,9 +664,9 @@
}
},
"node_modules/@cloudflare/workerd-linux-arm64": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workerd-linux-arm64/-/workerd-linux-arm64-1.20260603.1.tgz",
- "integrity": "sha512-LJZ6x00rAjSrobV4m0ZW0TpH5ilBbKcWBzlH+y+KOUsIE/CpTuhAzKV43TbSnFLRX5+jrWKiz2v0hO91lPXy6A==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workerd-linux-arm64/-/workerd-linux-arm64-1.20260625.1.tgz",
+ "integrity": "sha512-LxxW7Qv60Xvv37+w6gUSDpYZziyqMy+cZWd9IvSA5ehVgKAxmzEaYPMiSZlxk32nbIWL9u/tfjXYCOKJ4Lo+XQ==",
"cpu": [
"arm64"
],
@@ -487,9 +681,9 @@
}
},
"node_modules/@cloudflare/workerd-windows-64": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workerd-windows-64/-/workerd-windows-64-1.20260603.1.tgz",
- "integrity": "sha512-DvwqkXMAJRPoDN4PxapAwhlz/6ouD+6R1ttbAEK3cWD/QBvFF5STx7Ds/9Irf+rBly3np3uHWkeX+wZnNFEuzA==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workerd-windows-64/-/workerd-windows-64-1.20260625.1.tgz",
+ "integrity": "sha512-LH6iIX1HHaTwVKV5VokDxxUErXJzQoNZFRwVm7Vx/3fB/ApcTcRCUaMqcxI4as94jEUqg+pmX5czOndiveohow==",
"cpu": [
"x64"
],
@@ -504,9 +698,9 @@
}
},
"node_modules/@cloudflare/workers-types": {
- "version": "4.20260609.1",
- "resolved": "https://registry.npmjs.org/@cloudflare/workers-types/-/workers-types-4.20260609.1.tgz",
- "integrity": "sha512-krGHtwSApCFBjTe1NTx/TFQ0P5i/bHGQOqCPnCLssb8rOKaAG4JkPFJZsossr0z/ZTMnpP2Tid5jWju+/i0hCA==",
+ "version": "4.20260630.1",
+ "resolved": "https://registry.npmjs.org/@cloudflare/workers-types/-/workers-types-4.20260630.1.tgz",
+ "integrity": "sha512-yl+c9vwvko9UZ0frmtsHuwOh3BRHvNjLrfelAp5Akpqe1+Ho1UWekr3nmjJ1D64CH0Yb0K0oRMV4i7npOFzsog==",
"dev": true,
"license": "MIT OR Apache-2.0"
},
@@ -523,10 +717,33 @@
"node": ">=12"
}
},
+ "node_modules/@emnapi/core": {
+ "version": "1.11.1",
+ "resolved": "https://registry.npmjs.org/@emnapi/core/-/core-1.11.1.tgz",
+ "integrity": "sha512-RSvbQmHzdKzNsLYa/wHrbc3KN4sYLKAdPZxqiM2HATqv/SBk2/ENSHpvXGaLOMcsAyz0poEGqkmmKYG3OWiJEQ==",
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "dependencies": {
+ "@emnapi/wasi-threads": "1.2.2",
+ "tslib": "^2.4.0"
+ }
+ },
"node_modules/@emnapi/runtime": {
- "version": "1.11.0",
- "resolved": "https://registry.npmjs.org/@emnapi/runtime/-/runtime-1.11.0.tgz",
- "integrity": "sha512-55coeOFKHv1ywEcUXJtWU5f+Jr/W5tZDvZig8DLKSwUN1JpROQ4rk/SNOQiFWmaR/VKF4zuFyW1B8JduOSv6Pg==",
+ "version": "1.11.1",
+ "resolved": "https://registry.npmjs.org/@emnapi/runtime/-/runtime-1.11.1.tgz",
+ "integrity": "sha512-vgj7R3y3Wgx24IQaGPA/R6YFXLHVMOZ0uVEyIQPaWs+rd1AzfEMXlAC22FYwO1XkKR6NPsq7mUandH8oIRdZFw==",
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "dependencies": {
+ "tslib": "^2.4.0"
+ }
+ },
+ "node_modules/@emnapi/wasi-threads": {
+ "version": "1.2.2",
+ "resolved": "https://registry.npmjs.org/@emnapi/wasi-threads/-/wasi-threads-1.2.2.tgz",
+ "integrity": "sha512-c95qOXkHdydNKhscBTebqEC1CVAZpyqOfVfBzQ1qgzyl3gfeldUjIggDbIZgDKsHLgnsM+igH7TJ/eAasaVuMA==",
"dev": true,
"license": "MIT",
"optional": true,
@@ -535,9 +752,9 @@
}
},
"node_modules/@esbuild/aix-ppc64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/aix-ppc64/-/aix-ppc64-0.27.3.tgz",
- "integrity": "sha512-9fJMTNFTWZMh5qwrBItuziu834eOCUcEqymSH7pY+zoMVEZg3gcPuBNxH1EvfVYe9h0x/Ptw8KBzv7qxb7l8dg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/aix-ppc64/-/aix-ppc64-0.28.1.tgz",
+ "integrity": "sha512-Svl7tq8k/08+p6CXPpRjQ1fKX+1odH/BQbb48fV6fj3CWHhsoIOoY87w1oHXm0qEpkIK3ZfVgp0hed3XBXzXMQ==",
"cpu": [
"ppc64"
],
@@ -552,9 +769,9 @@
}
},
"node_modules/@esbuild/android-arm": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/android-arm/-/android-arm-0.27.3.tgz",
- "integrity": "sha512-i5D1hPY7GIQmXlXhs2w8AWHhenb00+GxjxRncS2ZM7YNVGNfaMxgzSGuO8o8SJzRc/oZwU2bcScvVERk03QhzA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/android-arm/-/android-arm-0.28.1.tgz",
+ "integrity": "sha512-0k2F129Xdio1TdJfzJ8sy1Q47vUD2NnwdhiAf7drUN1EBTfPf4hsFCtmMgu/6m8JSzsBrlmVjudMBQqOfG8usQ==",
"cpu": [
"arm"
],
@@ -569,9 +786,9 @@
}
},
"node_modules/@esbuild/android-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/android-arm64/-/android-arm64-0.27.3.tgz",
- "integrity": "sha512-YdghPYUmj/FX2SYKJ0OZxf+iaKgMsKHVPF1MAq/P8WirnSpCStzKJFjOjzsW0QQ7oIAiccHdcqjbHmJxRb/dmg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/android-arm64/-/android-arm64-0.28.1.tgz",
+ "integrity": "sha512-34EGEbCIAgosYz6goLcopX6Mo7NyGv9tfwEM2/7Ce2VcVRk568iSvniGWcUXIy7wEDR1wzolcxcriFVrWYcwBg==",
"cpu": [
"arm64"
],
@@ -586,9 +803,9 @@
}
},
"node_modules/@esbuild/android-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/android-x64/-/android-x64-0.27.3.tgz",
- "integrity": "sha512-IN/0BNTkHtk8lkOM8JWAYFg4ORxBkZQf9zXiEOfERX/CzxW3Vg1ewAhU7QSWQpVIzTW+b8Xy+lGzdYXV6UZObQ==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/android-x64/-/android-x64-0.28.1.tgz",
+ "integrity": "sha512-dbwY7ltSMDWsRatcRpCnES4F+im88OCUgGZjy52shC7GqHRE/cYlxNbB4Z4UpJswpcc4Qxd2oE/ufM0p61IKng==",
"cpu": [
"x64"
],
@@ -603,9 +820,9 @@
}
},
"node_modules/@esbuild/darwin-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/darwin-arm64/-/darwin-arm64-0.27.3.tgz",
- "integrity": "sha512-Re491k7ByTVRy0t3EKWajdLIr0gz2kKKfzafkth4Q8A5n1xTHrkqZgLLjFEHVD+AXdUGgQMq+Godfq45mGpCKg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/darwin-arm64/-/darwin-arm64-0.28.1.tgz",
+ "integrity": "sha512-TZbWkQY7kvTAXbXUT7uVACR5cMHsDiSz9z7ZKAX/RTq/WJEk3QyRr0wZpNhBDX+/0CtdqUIJlOiodQcta6tY3Q==",
"cpu": [
"arm64"
],
@@ -620,9 +837,9 @@
}
},
"node_modules/@esbuild/darwin-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/darwin-x64/-/darwin-x64-0.27.3.tgz",
- "integrity": "sha512-vHk/hA7/1AckjGzRqi6wbo+jaShzRowYip6rt6q7VYEDX4LEy1pZfDpdxCBnGtl+A5zq8iXDcyuxwtv3hNtHFg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/darwin-x64/-/darwin-x64-0.28.1.tgz",
+ "integrity": "sha512-zfdzgK9ACBNZLI/CyHTOx81SyNbM6YXn7rxSgX97VjyiPl9W1i4Ka4fgKECEoFCKGpvBj5qArWIGgQjOwkgskQ==",
"cpu": [
"x64"
],
@@ -637,9 +854,9 @@
}
},
"node_modules/@esbuild/freebsd-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/freebsd-arm64/-/freebsd-arm64-0.27.3.tgz",
- "integrity": "sha512-ipTYM2fjt3kQAYOvo6vcxJx3nBYAzPjgTCk7QEgZG8AUO3ydUhvelmhrbOheMnGOlaSFUoHXB6un+A7q4ygY9w==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/freebsd-arm64/-/freebsd-arm64-0.28.1.tgz",
+ "integrity": "sha512-wG2EA8ENdEI0qhkSZMjfqrdY+ziCYCPMmtZjjIwOmXFjmyzEHn+UUxk5of+SYsjtfs3VpnlC7QLzSI5hY/rOAw==",
"cpu": [
"arm64"
],
@@ -654,9 +871,9 @@
}
},
"node_modules/@esbuild/freebsd-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/freebsd-x64/-/freebsd-x64-0.27.3.tgz",
- "integrity": "sha512-dDk0X87T7mI6U3K9VjWtHOXqwAMJBNN2r7bejDsc+j03SEjtD9HrOl8gVFByeM0aJksoUuUVU9TBaZa2rgj0oA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/freebsd-x64/-/freebsd-x64-0.28.1.tgz",
+ "integrity": "sha512-i7dZ9vQgnvSCzi/rYCXNgtF/U+eKZNJBzu3eTQbRgHnM7tNSizLOkRFAl3qzVc/Op/u5YkHHa4pf/3DOYHthLQ==",
"cpu": [
"x64"
],
@@ -671,9 +888,9 @@
}
},
"node_modules/@esbuild/linux-arm": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-arm/-/linux-arm-0.27.3.tgz",
- "integrity": "sha512-s6nPv2QkSupJwLYyfS+gwdirm0ukyTFNl3KTgZEAiJDd+iHZcbTPPcWCcRYH+WlNbwChgH2QkE9NSlNrMT8Gfw==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-arm/-/linux-arm-0.28.1.tgz",
+ "integrity": "sha512-qVXBOHQS+d5Y722GwJzJUtOLlX7km3CraOaGormF1pDtPd2C/l1SHRPgjLunLGe51Sh5YYWKMFDyV4SxgMQYTQ==",
"cpu": [
"arm"
],
@@ -688,9 +905,9 @@
}
},
"node_modules/@esbuild/linux-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-arm64/-/linux-arm64-0.27.3.tgz",
- "integrity": "sha512-sZOuFz/xWnZ4KH3YfFrKCf1WyPZHakVzTiqji3WDc0BCl2kBwiJLCXpzLzUBLgmp4veFZdvN5ChW4Eq/8Fc2Fg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-arm64/-/linux-arm64-0.28.1.tgz",
+ "integrity": "sha512-yHs+0uc8+nvEAfAfxrWQKK5peSNzBc4PegcMO0EJ2hT71uA7vB8Ihg2e77R2P7SG5uYjPbHlLLmve4LLLRCf0g==",
"cpu": [
"arm64"
],
@@ -705,9 +922,9 @@
}
},
"node_modules/@esbuild/linux-ia32": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-ia32/-/linux-ia32-0.27.3.tgz",
- "integrity": "sha512-yGlQYjdxtLdh0a3jHjuwOrxQjOZYD/C9PfdbgJJF3TIZWnm/tMd/RcNiLngiu4iwcBAOezdnSLAwQDPqTmtTYg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-ia32/-/linux-ia32-0.28.1.tgz",
+ "integrity": "sha512-d1z4ZuP0ajrfz/FhGT4vv278rX8KnPPJx8i5+AtK7TYbx9Le9F1hyzurZpkEyjkGa9dUGhQow4C1NmeGvqxN2w==",
"cpu": [
"ia32"
],
@@ -722,9 +939,9 @@
}
},
"node_modules/@esbuild/linux-loong64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-loong64/-/linux-loong64-0.27.3.tgz",
- "integrity": "sha512-WO60Sn8ly3gtzhyjATDgieJNet/KqsDlX5nRC5Y3oTFcS1l0KWba+SEa9Ja1GfDqSF1z6hif/SkpQJbL63cgOA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-loong64/-/linux-loong64-0.28.1.tgz",
+ "integrity": "sha512-M5sRjUVZrkm1OAPR3dlOYzNmN+loZKGVi1VUQGrwuqLcbR6qeAz+famMhjASeH3YVKvZz+zT1jlh/keC3Rj/lg==",
"cpu": [
"loong64"
],
@@ -739,9 +956,9 @@
}
},
"node_modules/@esbuild/linux-mips64el": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-mips64el/-/linux-mips64el-0.27.3.tgz",
- "integrity": "sha512-APsymYA6sGcZ4pD6k+UxbDjOFSvPWyZhjaiPyl/f79xKxwTnrn5QUnXR5prvetuaSMsb4jgeHewIDCIWljrSxw==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-mips64el/-/linux-mips64el-0.28.1.tgz",
+ "integrity": "sha512-mRObBZeHh2OxcBFPWE/FjylkRgZdYuiTR3vaTozquCGOH14iP9oN4x4Ge81CoIDYQrXmIxpFumJBu5MtZpnQJQ==",
"cpu": [
"mips64el"
],
@@ -756,9 +973,9 @@
}
},
"node_modules/@esbuild/linux-ppc64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-ppc64/-/linux-ppc64-0.27.3.tgz",
- "integrity": "sha512-eizBnTeBefojtDb9nSh4vvVQ3V9Qf9Df01PfawPcRzJH4gFSgrObw+LveUyDoKU3kxi5+9RJTCWlj4FjYXVPEA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-ppc64/-/linux-ppc64-0.28.1.tgz",
+ "integrity": "sha512-slScBsMAb3GFDcdrCgLwZtPYRoH2H/youv10QiZyRjmsP48fznoveWytSgCI/R0ZcUgpc0ZhIUEx6LHts8yrfQ==",
"cpu": [
"ppc64"
],
@@ -773,9 +990,9 @@
}
},
"node_modules/@esbuild/linux-riscv64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-riscv64/-/linux-riscv64-0.27.3.tgz",
- "integrity": "sha512-3Emwh0r5wmfm3ssTWRQSyVhbOHvqegUDRd0WhmXKX2mkHJe1SFCMJhagUleMq+Uci34wLSipf8Lagt4LlpRFWQ==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-riscv64/-/linux-riscv64-0.28.1.tgz",
+ "integrity": "sha512-kw0owk1o0GFETUJyW0jc0G4Yzs0BHZn0JDZ8JRT088vjJYX777BAs1fDGxAC+q831qOs2DTC96mNsG2opdfyyQ==",
"cpu": [
"riscv64"
],
@@ -790,9 +1007,9 @@
}
},
"node_modules/@esbuild/linux-s390x": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-s390x/-/linux-s390x-0.27.3.tgz",
- "integrity": "sha512-pBHUx9LzXWBc7MFIEEL0yD/ZVtNgLytvx60gES28GcWMqil8ElCYR4kvbV2BDqsHOvVDRrOxGySBM9Fcv744hw==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-s390x/-/linux-s390x-0.28.1.tgz",
+ "integrity": "sha512-/lAIjX8aYFRByhh6L5rYtPEDRqa9de/4V/juOXcta5frjvzXO4/sqEtyytse0g3zZFuWu5cDN0MkLz2qRDD2Ag==",
"cpu": [
"s390x"
],
@@ -807,9 +1024,9 @@
}
},
"node_modules/@esbuild/linux-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/linux-x64/-/linux-x64-0.27.3.tgz",
- "integrity": "sha512-Czi8yzXUWIQYAtL/2y6vogER8pvcsOsk5cpwL4Gk5nJqH5UZiVByIY8Eorm5R13gq+DQKYg0+JyQoytLQas4dA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/linux-x64/-/linux-x64-0.28.1.tgz",
+ "integrity": "sha512-u/anNYF2mmVOEDwLtnQ1wOr3EZ9sTNGLWrsYGYwHWzGA3Si84IOkHXlbWTD1NB+9/1lcnweYKO54uhxZydNzfA==",
"cpu": [
"x64"
],
@@ -824,9 +1041,9 @@
}
},
"node_modules/@esbuild/netbsd-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/netbsd-arm64/-/netbsd-arm64-0.27.3.tgz",
- "integrity": "sha512-sDpk0RgmTCR/5HguIZa9n9u+HVKf40fbEUt+iTzSnCaGvY9kFP0YKBWZtJaraonFnqef5SlJ8/TiPAxzyS+UoA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/netbsd-arm64/-/netbsd-arm64-0.28.1.tgz",
+ "integrity": "sha512-oks0DYbLwWMmaakTsCb+zL4E+aHRVLom9IJZOAthMQEPiQmydXHkziYEsGYRx0uNV/IjEKGAV941JzH02pflqw==",
"cpu": [
"arm64"
],
@@ -841,9 +1058,9 @@
}
},
"node_modules/@esbuild/netbsd-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/netbsd-x64/-/netbsd-x64-0.27.3.tgz",
- "integrity": "sha512-P14lFKJl/DdaE00LItAukUdZO5iqNH7+PjoBm+fLQjtxfcfFE20Xf5CrLsmZdq5LFFZzb5JMZ9grUwvtVYzjiA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/netbsd-x64/-/netbsd-x64-0.28.1.tgz",
+ "integrity": "sha512-aeL6lAnN89Hz43Mlh1G8ARasbuoYvSITDEx0tHh5b7jJnHcssqgjy9Yx430GDpmCa6OyrKoS0aNRjKundRizGg==",
"cpu": [
"x64"
],
@@ -858,9 +1075,9 @@
}
},
"node_modules/@esbuild/openbsd-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/openbsd-arm64/-/openbsd-arm64-0.27.3.tgz",
- "integrity": "sha512-AIcMP77AvirGbRl/UZFTq5hjXK+2wC7qFRGoHSDrZ5v5b8DK/GYpXW3CPRL53NkvDqb9D+alBiC/dV0Fb7eJcw==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/openbsd-arm64/-/openbsd-arm64-0.28.1.tgz",
+ "integrity": "sha512-MEFJe5C3R8pwXdZ5Y21oo6m7ePiS0d9pWucn99O/wvyJZChoIQKrQDxKrGeW8F5+T0okTHesAmDeiHDTIq0V/Q==",
"cpu": [
"arm64"
],
@@ -875,9 +1092,9 @@
}
},
"node_modules/@esbuild/openbsd-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/openbsd-x64/-/openbsd-x64-0.27.3.tgz",
- "integrity": "sha512-DnW2sRrBzA+YnE70LKqnM3P+z8vehfJWHXECbwBmH/CU51z6FiqTQTHFenPlHmo3a8UgpLyH3PT+87OViOh1AQ==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/openbsd-x64/-/openbsd-x64-0.28.1.tgz",
+ "integrity": "sha512-i/ZLIOafE0Z8cI/XANJAixoJL/uRAoS2xOA3rb0xN+KK0K177cMAsQYkzHtBrtMXAKuAc7HGgcWiZ/sRC1Nxgw==",
"cpu": [
"x64"
],
@@ -892,9 +1109,9 @@
}
},
"node_modules/@esbuild/openharmony-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/openharmony-arm64/-/openharmony-arm64-0.27.3.tgz",
- "integrity": "sha512-NinAEgr/etERPTsZJ7aEZQvvg/A6IsZG/LgZy+81wON2huV7SrK3e63dU0XhyZP4RKGyTm7aOgmQk0bGp0fy2g==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/openharmony-arm64/-/openharmony-arm64-0.28.1.tgz",
+ "integrity": "sha512-ge+Z7EXFNt2BO1oAMsVpiQ8EwndV9i1xXerAeTIK7AtPs3bKFXQM7nlRxDSIUIMeueR1CNXxqztLzdNeReKBJg==",
"cpu": [
"arm64"
],
@@ -909,9 +1126,9 @@
}
},
"node_modules/@esbuild/sunos-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/sunos-x64/-/sunos-x64-0.27.3.tgz",
- "integrity": "sha512-PanZ+nEz+eWoBJ8/f8HKxTTD172SKwdXebZ0ndd953gt1HRBbhMsaNqjTyYLGLPdoWHy4zLU7bDVJztF5f3BHA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/sunos-x64/-/sunos-x64-0.28.1.tgz",
+ "integrity": "sha512-BEjgtECkL3vY+SaSQ6nzVfiALUeFxpawyp8Jmf5PtYhf1Ug40N1h/hxlhts+f1FvSvarEigdxS3BlSMI2PJLcQ==",
"cpu": [
"x64"
],
@@ -926,9 +1143,9 @@
}
},
"node_modules/@esbuild/win32-arm64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/win32-arm64/-/win32-arm64-0.27.3.tgz",
- "integrity": "sha512-B2t59lWWYrbRDw/tjiWOuzSsFh1Y/E95ofKz7rIVYSQkUYBjfSgf6oeYPNWHToFRr2zx52JKApIcAS/D5TUBnA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/win32-arm64/-/win32-arm64-0.28.1.tgz",
+ "integrity": "sha512-lCv9eK/H6ZJWbE7bh2nw54CZ9M2nupBxJcTsdk/QQnWkdSjKGuxmmH8/GWrlT1eMmZfn4dGcCjRte397WqfQXA==",
"cpu": [
"arm64"
],
@@ -943,9 +1160,9 @@
}
},
"node_modules/@esbuild/win32-ia32": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/win32-ia32/-/win32-ia32-0.27.3.tgz",
- "integrity": "sha512-QLKSFeXNS8+tHW7tZpMtjlNb7HKau0QDpwm49u0vUp9y1WOF+PEzkU84y9GqYaAVW8aH8f3GcBck26jh54cX4Q==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/win32-ia32/-/win32-ia32-0.28.1.tgz",
+ "integrity": "sha512-zvb/mB2bSCoJOpoCBgYKKpX6YM6mJBlBUVUtVj41DlZJVEB6/0CKlRYxP5wWl1C1ILiCoAU5wZZ4q1P3qeS6Eg==",
"cpu": [
"ia32"
],
@@ -960,9 +1177,9 @@
}
},
"node_modules/@esbuild/win32-x64": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/@esbuild/win32-x64/-/win32-x64-0.27.3.tgz",
- "integrity": "sha512-4uJGhsxuptu3OcpVAzli+/gWusVGwZZHTlS63hh++ehExkVT8SgiEf7/uC/PclrPPkLhZqGgCTjd0VWLo6xMqA==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/@esbuild/win32-x64/-/win32-x64-0.28.1.tgz",
+ "integrity": "sha512-bm4Mowrv+GXMlpWX++EcXw/iLyd1o3+bJkC2DkWXYVvgZCqD/bSj9ctZeAMC3cIxgjRVR2Dufaiu4YPxr5gW1A==",
"cpu": [
"x64"
],
@@ -978,7 +1195,7 @@
},
"node_modules/@hexagon/base64": {
"version": "1.1.28",
- "resolved": "https://registry.npmmirror.com/@hexagon/base64/-/base64-1.1.28.tgz",
+ "resolved": "https://registry.npmjs.org/@hexagon/base64/-/base64-1.1.28.tgz",
"integrity": "sha512-lhqDEAvWixy3bZ+UOYbPwUbBkwBq5C1LAJ/xPC8Oi+lL54oyakv/npbA0aU2hgCsx/1NUd4IBvV03+aUBWxerw==",
"license": "MIT"
},
@@ -993,9 +1210,9 @@
}
},
"node_modules/@img/sharp-darwin-arm64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-darwin-arm64/-/sharp-darwin-arm64-0.34.5.tgz",
- "integrity": "sha512-imtQ3WMJXbMY4fxb/Ndp6HBTNVtWCUI0WdobyheGf5+ad6xX8VIDO8u2xE4qc/fr08CKG/7dDseFtn6M6g/r3w==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-darwin-arm64/-/sharp-darwin-arm64-0.35.0.tgz",
+ "integrity": "sha512-ZgaYEwaj+lx/5n4W8GmZ2IYz0PQHjN5eqRcfijWGB+2Aq7ZInZGa0qJyAn6DEtyLuWHRSrmWOqT9q3qqTBvmUQ==",
"cpu": [
"arm64"
],
@@ -1006,19 +1223,19 @@
"darwin"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-darwin-arm64": "1.2.4"
+ "@img/sharp-libvips-darwin-arm64": "1.3.0"
}
},
"node_modules/@img/sharp-darwin-x64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-darwin-x64/-/sharp-darwin-x64-0.34.5.tgz",
- "integrity": "sha512-YNEFAF/4KQ/PeW0N+r+aVVsoIY0/qxxikF2SWdp+NRkmMB7y9LBZAVqQ4yhGCm/H3H270OSykqmQMKLBhBJDEw==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-darwin-x64/-/sharp-darwin-x64-0.35.0.tgz",
+ "integrity": "sha512-c1z9LFpKB0slQW3RchwBE8iSVzGp70TNjUUO9k4BZwwW4HH7JBGHeIy4b+kk4n/kcBASb9evKCE3/7Slmslgiw==",
"cpu": [
"x64"
],
@@ -1029,19 +1246,39 @@
"darwin"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-darwin-x64": "1.2.4"
+ "@img/sharp-libvips-darwin-x64": "1.3.0"
+ }
+ },
+ "node_modules/@img/sharp-freebsd-wasm32": {
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-freebsd-wasm32/-/sharp-freebsd-wasm32-0.35.0.tgz",
+ "integrity": "sha512-Li2KTev0H90kEtnJHkI9xQojXt1AqWmFBMXiPw5kqd1jQgP7gi5HVK/qC5Rmh/59NuAwUuPzzPITmX22NomYYQ==",
+ "dev": true,
+ "license": "Apache-2.0",
+ "optional": true,
+ "os": [
+ "freebsd"
+ ],
+ "dependencies": {
+ "@img/sharp-wasm32": "0.35.0"
+ },
+ "engines": {
+ "node": ">=20.9.0"
+ },
+ "funding": {
+ "url": "https://opencollective.com/libvips"
}
},
"node_modules/@img/sharp-libvips-darwin-arm64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-darwin-arm64/-/sharp-libvips-darwin-arm64-1.2.4.tgz",
- "integrity": "sha512-zqjjo7RatFfFoP0MkQ51jfuFZBnVE2pRiaydKJ1G/rHZvnsrHAOcQALIi9sA5co5xenQdTugCvtb1cuf78Vf4g==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-darwin-arm64/-/sharp-libvips-darwin-arm64-1.3.0.tgz",
+ "integrity": "sha512-EKbmBKtyTH+GPFDRw2TgK2oV6hyxxlJVIar4hoTYSNmIwipgMFdxPQqR392GmfdsPGWga0mCFN1cCKjRb9cljw==",
"cpu": [
"arm64"
],
@@ -1056,9 +1293,9 @@
}
},
"node_modules/@img/sharp-libvips-darwin-x64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-darwin-x64/-/sharp-libvips-darwin-x64-1.2.4.tgz",
- "integrity": "sha512-1IOd5xfVhlGwX+zXv2N93k0yMONvUlANylbJw1eTah8K/Jtpi15KC+WSiaX/nBmbm2HxRM1gZ0nSdjSsrZbGKg==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-darwin-x64/-/sharp-libvips-darwin-x64-1.3.0.tgz",
+ "integrity": "sha512-Pl2OmOvrJ42adUllESxBsG54PfXLo1OYg9i3c5/5Ln/qJ0gZuTM9YMhQJPIbXqwidLRc/c2zuHt4RsrymmNv7A==",
"cpu": [
"x64"
],
@@ -1073,9 +1310,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-arm": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-arm/-/sharp-libvips-linux-arm-1.2.4.tgz",
- "integrity": "sha512-bFI7xcKFELdiNCVov8e44Ia4u2byA+l3XtsAj+Q8tfCwO6BQ8iDojYdvoPMqsKDkuoOo+X6HZA0s0q11ANMQ8A==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-arm/-/sharp-libvips-linux-arm-1.3.0.tgz",
+ "integrity": "sha512-A8UpHoUDW4DwnXoV6+q3C1s7QLRAHtPDEjWuNZjwHMyoCNZnm0GeNN8ls9f/bsEYTRQRW96C/n34XJQHJ2fT7A==",
"cpu": [
"arm"
],
@@ -1093,9 +1330,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-arm64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-arm64/-/sharp-libvips-linux-arm64-1.2.4.tgz",
- "integrity": "sha512-excjX8DfsIcJ10x1Kzr4RcWe1edC9PquDRRPx3YVCvQv+U5p7Yin2s32ftzikXojb1PIFc/9Mt28/y+iRklkrw==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-arm64/-/sharp-libvips-linux-arm64-1.3.0.tgz",
+ "integrity": "sha512-C0SqjoFKnszqa44EQ7xoaT48nnO0lOyXEULfXMWi8krrjOPGYkeK30Okzla6ATbBYsyZ0ySinK0FVkpv3DwzfQ==",
"cpu": [
"arm64"
],
@@ -1113,9 +1350,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-ppc64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-ppc64/-/sharp-libvips-linux-ppc64-1.2.4.tgz",
- "integrity": "sha512-FMuvGijLDYG6lW+b/UvyilUWu5Ayu+3r2d1S8notiGCIyYU/76eig1UfMmkZ7vwgOrzKzlQbFSuQfgm7GYUPpA==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-ppc64/-/sharp-libvips-linux-ppc64-1.3.0.tgz",
+ "integrity": "sha512-WOpkVxAjFd369iaIzEgNRreFD+gWdUMIGD5zplhNKNeqS6mm5dac3q2AFyCBmzYoAdouzZvRBgxy4z8QHZb4/A==",
"cpu": [
"ppc64"
],
@@ -1133,9 +1370,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-riscv64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-riscv64/-/sharp-libvips-linux-riscv64-1.2.4.tgz",
- "integrity": "sha512-oVDbcR4zUC0ce82teubSm+x6ETixtKZBh/qbREIOcI3cULzDyb18Sr/Wcyx7NRQeQzOiHTNbZFF1UwPS2scyGA==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-riscv64/-/sharp-libvips-linux-riscv64-1.3.0.tgz",
+ "integrity": "sha512-DRWw0mOHusrCCuw2rqP87oLg6PGlkomVDFqw2hIwsSfwWpu4k3XLcBPaKKl6ct/GtL/cwNkgwjV/tc0Mqht3VA==",
"cpu": [
"riscv64"
],
@@ -1153,9 +1390,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-s390x": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-s390x/-/sharp-libvips-linux-s390x-1.2.4.tgz",
- "integrity": "sha512-qmp9VrzgPgMoGZyPvrQHqk02uyjA0/QrTO26Tqk6l4ZV0MPWIW6LTkqOIov+J1yEu7MbFQaDpwdwJKhbJvuRxQ==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-s390x/-/sharp-libvips-linux-s390x-1.3.0.tgz",
+ "integrity": "sha512-9APy+nFWhHS+kzLgWZfLcyrUd7YqnAQVa4BPOo4xkoHpdoktOAPG4cEr9+Jpl0TtqfVmcMJimNL5qNTyyOHZNA==",
"cpu": [
"s390x"
],
@@ -1173,9 +1410,9 @@
}
},
"node_modules/@img/sharp-libvips-linux-x64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-x64/-/sharp-libvips-linux-x64-1.2.4.tgz",
- "integrity": "sha512-tJxiiLsmHc9Ax1bz3oaOYBURTXGIRDODBqhveVHonrHJ9/+k89qbLl0bcJns+e4t4rvaNBxaEZsFtSfAdquPrw==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linux-x64/-/sharp-libvips-linux-x64-1.3.0.tgz",
+ "integrity": "sha512-y9RNUYDe2A1UAdhLyfeOodGRszQdaEoe4nfOpp/sNVPl2CWIcUyFaDoCh4vPLPxu19803j2naLqZup2WxDXCLA==",
"cpu": [
"x64"
],
@@ -1193,9 +1430,9 @@
}
},
"node_modules/@img/sharp-libvips-linuxmusl-arm64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linuxmusl-arm64/-/sharp-libvips-linuxmusl-arm64-1.2.4.tgz",
- "integrity": "sha512-FVQHuwx1IIuNow9QAbYUzJ+En8KcVm9Lk5+uGUQJHaZmMECZmOlix9HnH7n1TRkXMS0pGxIJokIVB9SuqZGGXw==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linuxmusl-arm64/-/sharp-libvips-linuxmusl-arm64-1.3.0.tgz",
+ "integrity": "sha512-cC1wkC0Mlucd0KSiGrLkJnB/ZqPvZCntc/Lk7ZnYO5ZSbF2euNek4Xvxafojq+wN1q/W0eprdpUIjUr/EV2PBg==",
"cpu": [
"arm64"
],
@@ -1213,9 +1450,9 @@
}
},
"node_modules/@img/sharp-libvips-linuxmusl-x64": {
- "version": "1.2.4",
- "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linuxmusl-x64/-/sharp-libvips-linuxmusl-x64-1.2.4.tgz",
- "integrity": "sha512-+LpyBk7L44ZIXwz/VYfglaX/okxezESc6UxDSoyo2Ks6Jxc4Y7sGjpgU9s4PMgqgjj1gZCylTieNamqA1MF7Dg==",
+ "version": "1.3.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-libvips-linuxmusl-x64/-/sharp-libvips-linuxmusl-x64-1.3.0.tgz",
+ "integrity": "sha512-LiYMhUZicB1QG//+RvmYZpXJO8fYRENfp+MZUCnG9aw+AKvGAy9gPaCnuwsPcBFs8EV66M0NNxj9VHcNklE8zw==",
"cpu": [
"x64"
],
@@ -1233,9 +1470,9 @@
}
},
"node_modules/@img/sharp-linux-arm": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-arm/-/sharp-linux-arm-0.34.5.tgz",
- "integrity": "sha512-9dLqsvwtg1uuXBGZKsxem9595+ujv0sJ6Vi8wcTANSFpwV/GONat5eCkzQo/1O6zRIkh0m/8+5BjrRr7jDUSZw==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-arm/-/sharp-linux-arm-0.35.0.tgz",
+ "integrity": "sha512-VVlpEWwizEFIOom0zdoeKuO5nuTswzVE5uHcBNvHzmeHUpNFajY3HFfbQ+zIH4E2kVaZ/yVxmsShW56TtEy4uA==",
"cpu": [
"arm"
],
@@ -1249,19 +1486,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-arm": "1.2.4"
+ "@img/sharp-libvips-linux-arm": "1.3.0"
}
},
"node_modules/@img/sharp-linux-arm64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-arm64/-/sharp-linux-arm64-0.34.5.tgz",
- "integrity": "sha512-bKQzaJRY/bkPOXyKx5EVup7qkaojECG6NLYswgktOZjaXecSAeCWiZwwiFf3/Y+O1HrauiE3FVsGxFg8c24rZg==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-arm64/-/sharp-linux-arm64-0.35.0.tgz",
+ "integrity": "sha512-4+4XHLNT5wDT0roYlHTEmH9lDKt0acf9Tv+3hM3iceOirkxrR404/3WjAYZ9F9CkHrxeRcGLJXbi4vluMZ9O+A==",
"cpu": [
"arm64"
],
@@ -1275,19 +1512,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-arm64": "1.2.4"
+ "@img/sharp-libvips-linux-arm64": "1.3.0"
}
},
"node_modules/@img/sharp-linux-ppc64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-ppc64/-/sharp-linux-ppc64-0.34.5.tgz",
- "integrity": "sha512-7zznwNaqW6YtsfrGGDA6BRkISKAAE1Jo0QdpNYXNMHu2+0dTrPflTLNkpc8l7MUP5M16ZJcUvysVWWrMefZquA==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-ppc64/-/sharp-linux-ppc64-0.35.0.tgz",
+ "integrity": "sha512-N3hzbEpUTJC8pWpPVJvgzGxM+so/MAXc8O2s/53B0LL9ZGpfXpME7Wizkc5d/8fRBlBtkDjzoZGDCqqNDHqLEw==",
"cpu": [
"ppc64"
],
@@ -1301,19 +1538,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-ppc64": "1.2.4"
+ "@img/sharp-libvips-linux-ppc64": "1.3.0"
}
},
"node_modules/@img/sharp-linux-riscv64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-riscv64/-/sharp-linux-riscv64-0.34.5.tgz",
- "integrity": "sha512-51gJuLPTKa7piYPaVs8GmByo7/U7/7TZOq+cnXJIHZKavIRHAP77e3N2HEl3dgiqdD/w0yUfiJnII77PuDDFdw==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-riscv64/-/sharp-linux-riscv64-0.35.0.tgz",
+ "integrity": "sha512-l6vmKVPnbS0RhVMbyxP5meAARsbhCnBN4fy31qz0+3a6Rv4jEqfzDrT89y6ZPkCi0AJGnwp2En528yXo401Hpw==",
"cpu": [
"riscv64"
],
@@ -1327,19 +1564,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-riscv64": "1.2.4"
+ "@img/sharp-libvips-linux-riscv64": "1.3.0"
}
},
"node_modules/@img/sharp-linux-s390x": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-s390x/-/sharp-linux-s390x-0.34.5.tgz",
- "integrity": "sha512-nQtCk0PdKfho3eC5MrbQoigJ2gd1CgddUMkabUj+rBevs8tZ2cULOx46E7oyX+04WGfABgIwmMC0VqieTiR4jg==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-s390x/-/sharp-linux-s390x-0.35.0.tgz",
+ "integrity": "sha512-MYlMiPFiv/EKPAHnp3yNZ9AAWFsxga9c5Bkc6wkar6bqzHLlkGVJHRm0u1ei+VXnZxp3Mz9MG9ZIsI8vSOf3sQ==",
"cpu": [
"s390x"
],
@@ -1353,19 +1590,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-s390x": "1.2.4"
+ "@img/sharp-libvips-linux-s390x": "1.3.0"
}
},
"node_modules/@img/sharp-linux-x64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linux-x64/-/sharp-linux-x64-0.34.5.tgz",
- "integrity": "sha512-MEzd8HPKxVxVenwAa+JRPwEC7QFjoPWuS5NZnBt6B3pu7EG2Ge0id1oLHZpPJdn3OQK+BQDiw9zStiHBTJQQQQ==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linux-x64/-/sharp-linux-x64-0.35.0.tgz",
+ "integrity": "sha512-TYaItB5oj1ioXjhyn2xrR208vf+YuIIcHptQWRRaBmFhvIvL9D72DXN8w75xup0KXA8UdEAhQ9Qb2S49FD/9Cw==",
"cpu": [
"x64"
],
@@ -1379,19 +1616,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linux-x64": "1.2.4"
+ "@img/sharp-libvips-linux-x64": "1.3.0"
}
},
"node_modules/@img/sharp-linuxmusl-arm64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linuxmusl-arm64/-/sharp-linuxmusl-arm64-0.34.5.tgz",
- "integrity": "sha512-fprJR6GtRsMt6Kyfq44IsChVZeGN97gTD331weR1ex1c1rypDEABN6Tm2xa1wE6lYb5DdEnk03NZPqA7Id21yg==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linuxmusl-arm64/-/sharp-linuxmusl-arm64-0.35.0.tgz",
+ "integrity": "sha512-DSTb6ijQzqe6DdAaOBVqJ/SYf1vO8EW5bK6X6LRXufEBebf2722VCdvBUtZ3rtV0x2ApfPNDy/p7LrrjaWjiyQ==",
"cpu": [
"arm64"
],
@@ -1405,19 +1642,19 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linuxmusl-arm64": "1.2.4"
+ "@img/sharp-libvips-linuxmusl-arm64": "1.3.0"
}
},
"node_modules/@img/sharp-linuxmusl-x64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-linuxmusl-x64/-/sharp-linuxmusl-x64-0.34.5.tgz",
- "integrity": "sha512-Jg8wNT1MUzIvhBFxViqrEhWDGzqymo3sV7z7ZsaWbZNDLXRJZoRGrjulp60YYtV4wfY8VIKcWidjojlLcWrd8Q==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-linuxmusl-x64/-/sharp-linuxmusl-x64-0.35.0.tgz",
+ "integrity": "sha512-K7ykQ+26Rt6+4BTU80AuGgTPIYX86UxiAKT4rcXX/WNTo7k1ZxpKz+TguHnwVpCqQK3B5PK0vZ0ZBe6nz/ib1w==",
"cpu": [
"x64"
],
@@ -1431,39 +1668,56 @@
"linux"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-libvips-linuxmusl-x64": "1.2.4"
+ "@img/sharp-libvips-linuxmusl-x64": "1.3.0"
}
},
"node_modules/@img/sharp-wasm32": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-wasm32/-/sharp-wasm32-0.34.5.tgz",
- "integrity": "sha512-OdWTEiVkY2PHwqkbBI8frFxQQFekHaSSkUIJkwzclWZe64O1X4UlUjqqqLaPbUpMOQk6FBu/HtlGXNblIs0huw==",
- "cpu": [
- "wasm32"
- ],
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-wasm32/-/sharp-wasm32-0.35.0.tgz",
+ "integrity": "sha512-9woLIFORERCr+6cWu87dQ22J34EExkhc73U1kZW0c+RclQqWetoodByp4dWZ/hN8/KVmTRAx2HOnUwib8AwZdA==",
"dev": true,
"license": "Apache-2.0 AND LGPL-3.0-or-later AND MIT",
"optional": true,
"dependencies": {
- "@emnapi/runtime": "^1.7.0"
+ "@emnapi/runtime": "^1.11.0"
},
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
+ },
+ "funding": {
+ "url": "https://opencollective.com/libvips"
+ }
+ },
+ "node_modules/@img/sharp-webcontainers-wasm32": {
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-webcontainers-wasm32/-/sharp-webcontainers-wasm32-0.35.0.tgz",
+ "integrity": "sha512-t+kie1TOyaDM6Dho+f+y0VqIUNhYQaKCUahuZVi0E0frgdiaOaPsDxDW3wfKacUdaNBCnK/ZDBMg33ydvHj8uA==",
+ "cpu": [
+ "wasm32"
+ ],
+ "dev": true,
+ "license": "Apache-2.0",
+ "optional": true,
+ "dependencies": {
+ "@img/sharp-wasm32": "0.35.0"
+ },
+ "engines": {
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
}
},
"node_modules/@img/sharp-win32-arm64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-win32-arm64/-/sharp-win32-arm64-0.34.5.tgz",
- "integrity": "sha512-WQ3AgWCWYSb2yt+IG8mnC6Jdk9Whs7O0gxphblsLvdhSpSTtmu69ZG1Gkb6NuvxsNACwiPV6cNSZNzt0KPsw7g==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-win32-arm64/-/sharp-win32-arm64-0.35.0.tgz",
+ "integrity": "sha512-M5eKxug0dabbaWgFKvPa3odNs2OpaP+81NASfGKkt4GcYXpNhSu7CaeYxWkLNV6vHmUp4hnCxnxrUyhUJhXbKA==",
"cpu": [
"arm64"
],
@@ -1474,16 +1728,16 @@
"win32"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
}
},
"node_modules/@img/sharp-win32-ia32": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-win32-ia32/-/sharp-win32-ia32-0.34.5.tgz",
- "integrity": "sha512-FV9m/7NmeCmSHDD5j4+4pNI8Cp3aW+JvLoXcTUo0IqyjSfAZJ8dIUmijx1qaJsIiU+Hosw6xM5KijAWRJCSgNg==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-win32-ia32/-/sharp-win32-ia32-0.35.0.tgz",
+ "integrity": "sha512-z0+pZ03QCDvdVN0Ez9IX/yjWC19ikMlXrmdYMwYNLTh2BLPx3hXWPvyqWfquZ0BTO9O6GVOjIVoTcyyacMnWlQ==",
"cpu": [
"ia32"
],
@@ -1494,16 +1748,16 @@
"win32"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": "^20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
}
},
"node_modules/@img/sharp-win32-x64": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/@img/sharp-win32-x64/-/sharp-win32-x64-0.34.5.tgz",
- "integrity": "sha512-+29YMsqY2/9eFEiW93eqWnuLcWcufowXewwSNIT6UwZdUUCrM3oFjMWH/Z6/TMmb4hlFenmfAVbpWeup2jryCw==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/@img/sharp-win32-x64/-/sharp-win32-x64-0.35.0.tgz",
+ "integrity": "sha512-feNnlz5ZHKr0MY1LPHvZQyJeBkbo4ctsn0D8FvA53VTw5TC63rfEL2UrWbkSBR19htSE7Mw78xYVwdJqoMWVHw==",
"cpu": [
"x64"
],
@@ -1514,7 +1768,7 @@
"win32"
],
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
@@ -1522,7 +1776,7 @@
},
"node_modules/@jridgewell/gen-mapping": {
"version": "0.3.13",
- "resolved": "https://registry.npmmirror.com/@jridgewell/gen-mapping/-/gen-mapping-0.3.13.tgz",
+ "resolved": "https://registry.npmjs.org/@jridgewell/gen-mapping/-/gen-mapping-0.3.13.tgz",
"integrity": "sha512-2kkt/7niJ6MgEPxF0bYdQ6etZaA+fQvDcLKckhy1yIQOzaoKjBBjSj63/aLVjYE3qhRt5dvM+uUyfCg6UKCBbA==",
"dev": true,
"license": "MIT",
@@ -1533,29 +1787,7 @@
},
"node_modules/@jridgewell/gen-mapping/node_modules/@jridgewell/trace-mapping": {
"version": "0.3.31",
- "resolved": "https://registry.npmmirror.com/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
- "integrity": "sha512-zzNR+SdQSDJzc8joaeP8QQoCQr8NuYx2dIIytl1QeBEZHJ9uW6hebsrYgbz8hJwUQao3TWCMtmfV8Nu1twOLAw==",
- "dev": true,
- "license": "MIT",
- "dependencies": {
- "@jridgewell/resolve-uri": "^3.1.0",
- "@jridgewell/sourcemap-codec": "^1.4.14"
- }
- },
- "node_modules/@jridgewell/remapping": {
- "version": "2.3.5",
- "resolved": "https://registry.npmmirror.com/@jridgewell/remapping/-/remapping-2.3.5.tgz",
- "integrity": "sha512-LI9u/+laYG4Ds1TDKSJW2YPrIlcVYOwi2fUC6xB43lueCjgxV4lffOCZCtYFiH6TNOX+tQKXx97T4IKHbhyHEQ==",
- "dev": true,
- "license": "MIT",
- "dependencies": {
- "@jridgewell/gen-mapping": "^0.3.5",
- "@jridgewell/trace-mapping": "^0.3.24"
- }
- },
- "node_modules/@jridgewell/remapping/node_modules/@jridgewell/trace-mapping": {
- "version": "0.3.31",
- "resolved": "https://registry.npmmirror.com/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
+ "resolved": "https://registry.npmjs.org/@jridgewell/trace-mapping/-/trace-mapping-0.3.31.tgz",
"integrity": "sha512-zzNR+SdQSDJzc8joaeP8QQoCQr8NuYx2dIIytl1QeBEZHJ9uW6hebsrYgbz8hJwUQao3TWCMtmfV8Nu1twOLAw==",
"dev": true,
"license": "MIT",
@@ -1566,7 +1798,7 @@
},
"node_modules/@jridgewell/resolve-uri": {
"version": "3.1.2",
- "resolved": "https://registry.npmmirror.com/@jridgewell/resolve-uri/-/resolve-uri-3.1.2.tgz",
+ "resolved": "https://registry.npmjs.org/@jridgewell/resolve-uri/-/resolve-uri-3.1.2.tgz",
"integrity": "sha512-bRISgCIjP20/tbWSPWMEi54QVPRZExkuD9lJL+UIxUKtwVJA8wW1Trb1jMs1RFXo1CBTNZ/5hpC9QvmKWdopKw==",
"dev": true,
"license": "MIT",
@@ -1576,7 +1808,7 @@
},
"node_modules/@jridgewell/sourcemap-codec": {
"version": "1.5.5",
- "resolved": "https://registry.npmmirror.com/@jridgewell/sourcemap-codec/-/sourcemap-codec-1.5.5.tgz",
+ "resolved": "https://registry.npmjs.org/@jridgewell/sourcemap-codec/-/sourcemap-codec-1.5.5.tgz",
"integrity": "sha512-cYQ9310grqxueWbl+WuIUIaiUaDcj7WOq5fVhEljNVgRfOUhY9fy2zTvfoqWsnebh8Sl70VScFbICvJnLKB0Og==",
"dev": true,
"license": "MIT"
@@ -1594,14 +1826,33 @@
},
"node_modules/@levischuck/tiny-cbor": {
"version": "0.2.11",
- "resolved": "https://registry.npmmirror.com/@levischuck/tiny-cbor/-/tiny-cbor-0.2.11.tgz",
+ "resolved": "https://registry.npmjs.org/@levischuck/tiny-cbor/-/tiny-cbor-0.2.11.tgz",
"integrity": "sha512-llBRm4dT4Z89aRsm6u2oEZ8tfwL/2l6BwpZ7JcyieouniDECM5AqNgr/y08zalEIvW3RSK4upYyybDcmjXqAow==",
"license": "MIT"
},
+ "node_modules/@napi-rs/wasm-runtime": {
+ "version": "1.1.6",
+ "resolved": "https://registry.npmjs.org/@napi-rs/wasm-runtime/-/wasm-runtime-1.1.6.tgz",
+ "integrity": "sha512-ZLv/JdUfkvOy9eCnnBaGfiO+XimbjebAeO+MRQqD/B+FR1tnRN0tpKSJHRbE8sFfS6aqsXZ67TQjfwfsxULVbg==",
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "dependencies": {
+ "@tybys/wasm-util": "^0.10.3"
+ },
+ "funding": {
+ "type": "github",
+ "url": "https://github.com/sponsors/Brooooooklyn"
+ },
+ "peerDependencies": {
+ "@emnapi/core": "^1.7.1",
+ "@emnapi/runtime": "^1.7.1"
+ }
+ },
"node_modules/@noble/hashes": {
- "version": "2.0.1",
- "resolved": "https://registry.npmmirror.com/@noble/hashes/-/hashes-2.0.1.tgz",
- "integrity": "sha512-XlOlEbQcE9fmuXxrVTXCTlG2nlRXa9Rj3rr5Ue/+tX+nmkgbX720YHh0VR3hBF9xDvwnb8D2shVGOwNx+ulArw==",
+ "version": "2.2.0",
+ "resolved": "https://registry.npmjs.org/@noble/hashes/-/hashes-2.2.0.tgz",
+ "integrity": "sha512-IYqDGiTXab6FniAgnSdZwgWbomxpy9FtYvLKs7wCUs2a8RkITG+DFGO1DM9cr+E3/RgADRpFjrKVaJ1z6sjtEg==",
"license": "MIT",
"engines": {
"node": ">= 20.19.0"
@@ -1612,7 +1863,7 @@
},
"node_modules/@nodelib/fs.scandir": {
"version": "2.1.5",
- "resolved": "https://registry.npmmirror.com/@nodelib/fs.scandir/-/fs.scandir-2.1.5.tgz",
+ "resolved": "https://registry.npmjs.org/@nodelib/fs.scandir/-/fs.scandir-2.1.5.tgz",
"integrity": "sha512-vq24Bq3ym5HEQm2NKCr3yXDwjc7vTsEThRDnkp2DK9p1uqLR+DHurm/NOTo0KG7HYHU7eppKZj3MyqYuMBf62g==",
"dev": true,
"license": "MIT",
@@ -1626,7 +1877,7 @@
},
"node_modules/@nodelib/fs.stat": {
"version": "2.0.5",
- "resolved": "https://registry.npmmirror.com/@nodelib/fs.stat/-/fs.stat-2.0.5.tgz",
+ "resolved": "https://registry.npmjs.org/@nodelib/fs.stat/-/fs.stat-2.0.5.tgz",
"integrity": "sha512-RkhPPp2zrqDAQA/2jNhnztcPAlv64XdhIp7a7454A5ovI7Bukxgt7MX7udwAu3zg1DcpPU0rz3VV1SeaqvY4+A==",
"dev": true,
"license": "MIT",
@@ -1636,7 +1887,7 @@
},
"node_modules/@nodelib/fs.walk": {
"version": "1.2.8",
- "resolved": "https://registry.npmmirror.com/@nodelib/fs.walk/-/fs.walk-1.2.8.tgz",
+ "resolved": "https://registry.npmjs.org/@nodelib/fs.walk/-/fs.walk-1.2.8.tgz",
"integrity": "sha512-oGB+UxlgWcgQkgwo8GcEGwemoTFt3FIO9ababBmaGwXIoBKZ+GTy0pP185beGg7Llih/NSHSV2XAs1lnznocSg==",
"dev": true,
"license": "MIT",
@@ -1648,9 +1899,19 @@
"node": ">= 8"
}
},
+ "node_modules/@oxc-project/types": {
+ "version": "0.138.0",
+ "resolved": "https://registry.npmjs.org/@oxc-project/types/-/types-0.138.0.tgz",
+ "integrity": "sha512-1a7ZKmrRTCoN1XMZ4L0PyyqrMnrNlLyPuOkdSX2MZg7IiIGRUyurNhAm73ptDOraoBcIordsIGKNPKUzy3ZmfA==",
+ "dev": true,
+ "license": "MIT",
+ "funding": {
+ "url": "https://github.com/sponsors/Boshen"
+ }
+ },
"node_modules/@peculiar/asn1-android": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-android/-/asn1-android-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-android/-/asn1-android-2.7.0.tgz",
"integrity": "sha512-iD3VskhVQnM4nE3PN9cBdPTR7JrqZy3FYk+uD2CeG6DUqKoANqaEfx0f7izPmW+Qm5JBM35ek+viLCmjy18ByQ==",
"license": "MIT",
"dependencies": {
@@ -1661,7 +1922,7 @@
},
"node_modules/@peculiar/asn1-cms": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-cms/-/asn1-cms-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-cms/-/asn1-cms-2.7.0.tgz",
"integrity": "sha512-hew63shtzzvBcSHbhm+cyAmKe6AIfinT9hzEqSPjDC6opTTMKmTkQ0gHuN2KsWlvqiKw1S/fS94fhag/FJkioQ==",
"license": "MIT",
"dependencies": {
@@ -1674,7 +1935,7 @@
},
"node_modules/@peculiar/asn1-csr": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-csr/-/asn1-csr-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-csr/-/asn1-csr-2.7.0.tgz",
"integrity": "sha512-VVsAyGqErT9D1SY4aEqozThXMVI+ssVRiv2DDeYuvpBKLIgZ3hYs3Ay3u/VSoKq6ESFi9cf6rf3IOOzfwh7oMA==",
"license": "MIT",
"dependencies": {
@@ -1686,7 +1947,7 @@
},
"node_modules/@peculiar/asn1-ecc": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-ecc/-/asn1-ecc-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-ecc/-/asn1-ecc-2.7.0.tgz",
"integrity": "sha512-n7KEs/Q/wrB415cxy4fHOBhegp4NdJ15fkJPwcB/3/8iNBQC2L/N7SChJPKDJPZGYH0jD4Tg4/0vnHmwghnbKw==",
"license": "MIT",
"dependencies": {
@@ -1698,7 +1959,7 @@
},
"node_modules/@peculiar/asn1-pfx": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-pfx/-/asn1-pfx-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-pfx/-/asn1-pfx-2.7.0.tgz",
"integrity": "sha512-V/nrlQVmhg7lYAsM7E13UDL5erAwFv6kCIVFqNaMIHSVi7dngcT839JkRTkQBqznMG98l2XjxYk74ZztAohZzA==",
"license": "MIT",
"dependencies": {
@@ -1712,7 +1973,7 @@
},
"node_modules/@peculiar/asn1-pkcs8": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-pkcs8/-/asn1-pkcs8-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-pkcs8/-/asn1-pkcs8-2.7.0.tgz",
"integrity": "sha512-9GTl1nE8Mx1kTZ+7QyYatDyKsm34QcWRBFkY1iPvWC3X4Dona5s/tlLiQsx5WzVdZqiMBZNYT0buyw4/vbhnjw==",
"license": "MIT",
"dependencies": {
@@ -1724,7 +1985,7 @@
},
"node_modules/@peculiar/asn1-pkcs9": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-pkcs9/-/asn1-pkcs9-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-pkcs9/-/asn1-pkcs9-2.7.0.tgz",
"integrity": "sha512-Bh7m+OuIaSEllPQcSd9OSp93F4ROWH7sbITWV8MI+8dwsjE5111/87VxiWVvYFKyww3vp39geLv9ENqhwWHcew==",
"license": "MIT",
"dependencies": {
@@ -1740,7 +2001,7 @@
},
"node_modules/@peculiar/asn1-rsa": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-rsa/-/asn1-rsa-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-rsa/-/asn1-rsa-2.7.0.tgz",
"integrity": "sha512-/qvENQrXyTZURjMqSeofHul0JJt2sNSzSwk36pl2olkHbaioMQgrASDZAlHXl0xUlnVbHj0uGgOrBMTb5x2aJQ==",
"license": "MIT",
"dependencies": {
@@ -1752,7 +2013,7 @@
},
"node_modules/@peculiar/asn1-schema": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-schema/-/asn1-schema-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-schema/-/asn1-schema-2.7.0.tgz",
"integrity": "sha512-W8ZfWzLmQnrcky+eh3tni4IozMdqBDiHWU0N+vve/UGjMaUs8c0L7A2oEdkBXS8rTpWDpK/aoI3DG/L/hxmxPg==",
"license": "MIT",
"dependencies": {
@@ -1763,7 +2024,7 @@
},
"node_modules/@peculiar/asn1-x509": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-x509/-/asn1-x509-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-x509/-/asn1-x509-2.7.0.tgz",
"integrity": "sha512-mUn9RRrkGDnG4ALfunDmzyRW5dg+sWCj/pfnCCqEHYbkGxEpvUt6iVJv8Yw1cyp6SWZ26ZE5oSmI5SqEaen15g==",
"license": "MIT",
"dependencies": {
@@ -1775,7 +2036,7 @@
},
"node_modules/@peculiar/asn1-x509-attr": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/@peculiar/asn1-x509-attr/-/asn1-x509-attr-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/asn1-x509-attr/-/asn1-x509-attr-2.7.0.tgz",
"integrity": "sha512-NS8e7SOgXipkzUPLF/sce7ukpMpWjhxYsH0n6Y+bHYo4TTxOb95Zv7hqwSuL212mj5YxovjdOKQOgH1As3E94w==",
"license": "MIT",
"dependencies": {
@@ -1787,7 +2048,7 @@
},
"node_modules/@peculiar/utils": {
"version": "2.0.3",
- "resolved": "https://registry.npmmirror.com/@peculiar/utils/-/utils-2.0.3.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/utils/-/utils-2.0.3.tgz",
"integrity": "sha512-+oL3HPFRIZ1St2K50lWCXiioIgSoxzz7R1J3uF6neO2yl1sgmpgY6XXJH4BdpoDkMWznQTeYF6oWNDZLCdQ4eQ==",
"license": "MIT",
"dependencies": {
@@ -1796,7 +2057,7 @@
},
"node_modules/@peculiar/x509": {
"version": "1.14.3",
- "resolved": "https://registry.npmmirror.com/@peculiar/x509/-/x509-1.14.3.tgz",
+ "resolved": "https://registry.npmjs.org/@peculiar/x509/-/x509-1.14.3.tgz",
"integrity": "sha512-C2Xj8FZ0uHWeCXXqX5B4/gVFQmtSkiuOolzAgutjTfseNOHT3pUjljDZsTSxXFGgio54bCzVFqmEOUrIVk8RDA==",
"license": "MIT",
"dependencies": {
@@ -1846,9 +2107,9 @@
"license": "MIT"
},
"node_modules/@preact/preset-vite": {
- "version": "2.10.3",
- "resolved": "https://registry.npmmirror.com/@preact/preset-vite/-/preset-vite-2.10.3.tgz",
- "integrity": "sha512-1SiS+vFItpkNdBs7q585PSAIln0wBeBdcpJYbzPs1qipsb/FssnkUioNXuRsb8ZnU8YEQHr+3v8+/mzWSnTQmg==",
+ "version": "2.10.5",
+ "resolved": "https://registry.npmjs.org/@preact/preset-vite/-/preset-vite-2.10.5.tgz",
+ "integrity": "sha512-p0vJpxiVO7KWWazWny3LUZ+saXyZKWv6Ju0bYMWNJRp2YveufRPgSUB1C4MTqGJfz07EehMgfN+AJNwQy+w6Iw==",
"dev": true,
"license": "MIT",
"dependencies": {
@@ -1858,24 +2119,26 @@
"@rollup/pluginutils": "^5.0.0",
"babel-plugin-transform-hook-names": "^1.0.2",
"debug": "^4.4.3",
+ "magic-string": "^0.30.21",
"picocolors": "^1.1.1",
- "vite-prerender-plugin": "^0.5.8"
+ "vite-prerender-plugin": "^0.5.8",
+ "zimmerframe": "^1.1.4"
},
"peerDependencies": {
"@babel/core": "7.x",
- "vite": "2.x || 3.x || 4.x || 5.x || 6.x || 7.x"
+ "vite": "2.x || 3.x || 4.x || 5.x || 6.x || 7.x || 8.x"
}
},
"node_modules/@prefresh/babel-plugin": {
"version": "0.5.3",
- "resolved": "https://registry.npmmirror.com/@prefresh/babel-plugin/-/babel-plugin-0.5.3.tgz",
+ "resolved": "https://registry.npmjs.org/@prefresh/babel-plugin/-/babel-plugin-0.5.3.tgz",
"integrity": "sha512-57LX2SHs4BX2s1IwCjNzTE2OJeEepRCNf1VTEpbNcUyHfMO68eeOWGDIt4ob9aYlW6PEWZ1SuwNikuoIXANDtQ==",
"dev": true,
"license": "MIT"
},
"node_modules/@prefresh/core": {
"version": "1.5.9",
- "resolved": "https://registry.npmmirror.com/@prefresh/core/-/core-1.5.9.tgz",
+ "resolved": "https://registry.npmjs.org/@prefresh/core/-/core-1.5.9.tgz",
"integrity": "sha512-IKBKCPaz34OFVC+adiQ2qaTF5qdztO2/4ZPf4KsRTgjKosWqxVXmEbxCiUydYZRY8GVie+DQlKzQr9gt6HQ+EQ==",
"dev": true,
"license": "MIT",
@@ -1885,14 +2148,14 @@
},
"node_modules/@prefresh/utils": {
"version": "1.2.1",
- "resolved": "https://registry.npmmirror.com/@prefresh/utils/-/utils-1.2.1.tgz",
+ "resolved": "https://registry.npmjs.org/@prefresh/utils/-/utils-1.2.1.tgz",
"integrity": "sha512-vq/sIuN5nYfYzvyayXI4C2QkprfNaHUQ9ZX+3xLD8nL3rWyzpxOm1+K7RtMbhd+66QcaISViK7amjnheQ/4WZw==",
"dev": true,
"license": "MIT"
},
"node_modules/@prefresh/vite": {
"version": "2.4.12",
- "resolved": "https://registry.npmmirror.com/@prefresh/vite/-/vite-2.4.12.tgz",
+ "resolved": "https://registry.npmjs.org/@prefresh/vite/-/vite-2.4.12.tgz",
"integrity": "sha512-FY1fzXpUjiuosznMV0YM7XAOPZjB5FIdWS0W24+XnlxYkt9hNAwwsiKYn+cuTEoMtD/ZVazS5QVssBr9YhpCQA==",
"dev": true,
"license": "MIT",
@@ -1910,7 +2173,7 @@
},
"node_modules/@prefresh/vite/node_modules/@rollup/pluginutils": {
"version": "4.2.1",
- "resolved": "https://registry.npmmirror.com/@rollup/pluginutils/-/pluginutils-4.2.1.tgz",
+ "resolved": "https://registry.npmjs.org/@rollup/pluginutils/-/pluginutils-4.2.1.tgz",
"integrity": "sha512-iKnFXr7NkdZAIHiIWE+BX5ULi/ucVFYWD6TbAV+rZctiRTY2PL6tsIKhoIOaoskiWAkgu+VsbXgUVDNLHf+InQ==",
"dev": true,
"license": "MIT",
@@ -1935,9 +2198,291 @@
"url": "https://github.com/sponsors/jonschlinkert"
}
},
+ "node_modules/@rolldown/binding-android-arm64": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-android-arm64/-/binding-android-arm64-1.1.4.tgz",
+ "integrity": "sha512-EZLpf/8y7GXkkra90ML47kzik/GMP3EMcE9bPyHmRfxLC6z9+aW5A8poCsoxjrT5GfEcNAAvWwUHjvP1pUQkfw==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "android"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-darwin-arm64": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-darwin-arm64/-/binding-darwin-arm64-1.1.4.tgz",
+ "integrity": "sha512-aUi+HBvmYb7j8krl1+qJgkG8C17fO79gk3c+jPw4S8glRFc1DTija9S3EyaTSQUm5GJXYKDAsugBEhFHH2vYiQ==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "darwin"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-darwin-x64": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-darwin-x64/-/binding-darwin-x64-1.1.4.tgz",
+ "integrity": "sha512-F7hHC3gwY11+vByKPRWqwGbeXWVgKmL+pTGCinaEhdihzBV2aQ0fvZOch9cXYUOKuKKq429HeYXOqQLc7wFCEg==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "darwin"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-freebsd-x64": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-freebsd-x64/-/binding-freebsd-x64-1.1.4.tgz",
+ "integrity": "sha512-sI5yw+7s92SK6odiEhD5lKCBlWcpjHS5qyqpVQbZAJ0fIzEUXrmbl3DH2ybR3PZogulNJF+COLtmA8hUfvkCCQ==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "freebsd"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-arm-gnueabihf": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-arm-gnueabihf/-/binding-linux-arm-gnueabihf-1.1.4.tgz",
+ "integrity": "sha512-mCi0OKgEieFircrtVYmQAFGszRtMnZ6fpZAXrxanXAu7lqZcsK1E1RAaZNG0uKAnxox3B1f4EyQNnoyMfN1vAA==",
+ "cpu": [
+ "arm"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-arm64-gnu": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-arm64-gnu/-/binding-linux-arm64-gnu-1.1.4.tgz",
+ "integrity": "sha512-B9Ial3Kv5sh0SHnB1g/QWcUQCEvCF6QKGAl4zXypYj65mVI+B4AhFBwPtSN7pDrJeIx8Z7zdy4ntx+wQABom7w==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-arm64-musl": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-arm64-musl/-/binding-linux-arm64-musl-1.1.4.tgz",
+ "integrity": "sha512-lZVym0PuHE1KZ22gmFTC15lAkrg9iTszR617oYRB/iPY1A56ywoJzVKOJBKaot5RiikCObmur6pogpse3gRcng==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "libc": [
+ "musl"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-ppc64-gnu": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-ppc64-gnu/-/binding-linux-ppc64-gnu-1.1.4.tgz",
+ "integrity": "sha512-t2DNiLJWNTbnEHyUzTumldML6ET4/g16467LZoDDJ3tSxGvguL5/NyC2lCsNKuyRycg9XeDQF5SSv+TNOhQEXg==",
+ "cpu": [
+ "ppc64"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-s390x-gnu": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-s390x-gnu/-/binding-linux-s390x-gnu-1.1.4.tgz",
+ "integrity": "sha512-0WIRnL1Uw4BvTZRLQt+PVgo6ZKTJadlC2btP+/EOXv2f/DWbY0rEgl+y834mIVwP1FkTlWVTrGGJXf12lru7EQ==",
+ "cpu": [
+ "s390x"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-x64-gnu": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-x64-gnu/-/binding-linux-x64-gnu-1.1.4.tgz",
+ "integrity": "sha512-JWtGshGfX+oENAKonoNkqEJX+7hC8yfhi9GUyPX1VX4mdh1y5r+ZiJLR5XzAB0aoP6s/PcILsGjKq8O0mm24bw==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-linux-x64-musl": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-linux-x64-musl/-/binding-linux-x64-musl-1.1.4.tgz",
+ "integrity": "sha512-rT6yQcxUuXs4CnbofqwHRRV0iem349rLMYpTjkgQGLjrY4ado/eDzwPZPTCgTOlF6Nkp8NEv70yLMTn6qkWxsQ==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "libc": [
+ "musl"
+ ],
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-openharmony-arm64": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-openharmony-arm64/-/binding-openharmony-arm64-1.1.4.tgz",
+ "integrity": "sha512-KXMGoboq5cyaCQjDA4GLuRiOwBQ0EyFnJoVViLeZ45/3rFItRODEr+NdsBcVpll40hhNArlm/speWGRvj08LzA==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "openharmony"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-wasm32-wasi": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-wasm32-wasi/-/binding-wasm32-wasi-1.1.4.tgz",
+ "integrity": "sha512-5K83rb36oJiY7BCyE9zLZtGcPV4g5wvq+xwdO0XPIwDVZI8cyB/AUjkNXGb92/rnmezEkjMOpgY61rtwjQtFwg==",
+ "cpu": [
+ "wasm32"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "dependencies": {
+ "@emnapi/core": "1.11.1",
+ "@emnapi/runtime": "1.11.1",
+ "@napi-rs/wasm-runtime": "^1.1.6"
+ },
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-win32-arm64-msvc": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-win32-arm64-msvc/-/binding-win32-arm64-msvc-1.1.4.tgz",
+ "integrity": "sha512-PnWBtw3TV5KOg69HQQDR0mnQuyCmSGR2pAB4DC1rPF808fgKeTUMj2EOEyKATpgiuxuR5APQmiDO7PDgEjTFSA==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "win32"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/binding-win32-x64-msvc": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/@rolldown/binding-win32-x64-msvc/-/binding-win32-x64-msvc-1.1.4.tgz",
+ "integrity": "sha512-M1lpniBePobTfsa7Ks9a199e1akxsXn+GYBUKsEzv3YFzOm1HJAMNwKI3qr0Zq+mxwx9gOZoTdP1yXRYsZUocQ==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "os": [
+ "win32"
+ ],
+ "engines": {
+ "node": "^20.19.0 || >=22.12.0"
+ }
+ },
+ "node_modules/@rolldown/pluginutils": {
+ "version": "1.0.1",
+ "resolved": "https://registry.npmjs.org/@rolldown/pluginutils/-/pluginutils-1.0.1.tgz",
+ "integrity": "sha512-2j9bGt5Jh8hj+vPtgzPtl72j0yRxHAyumoo6TNfAjsLB04UtpSvPbPcDcBMxz7n+9CYB0c1GxQFxYRg2jimqGw==",
+ "dev": true,
+ "license": "MIT"
+ },
"node_modules/@rollup/pluginutils": {
"version": "5.3.0",
- "resolved": "https://registry.npmmirror.com/@rollup/pluginutils/-/pluginutils-5.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/@rollup/pluginutils/-/pluginutils-5.3.0.tgz",
"integrity": "sha512-5EdhGZtnu3V88ces7s53hhfK5KSASnJZv8Lulpc04cWO3REESroJXg73DFsOmgbU2BhwV0E20bu2IDZb3VKW4Q==",
"dev": true,
"license": "MIT",
@@ -1958,360 +2503,10 @@
}
}
},
- "node_modules/@rollup/rollup-android-arm-eabi": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-android-arm-eabi/-/rollup-android-arm-eabi-4.59.0.tgz",
- "integrity": "sha512-upnNBkA6ZH2VKGcBj9Fyl9IGNPULcjXRlg0LLeaioQWueH30p6IXtJEbKAgvyv+mJaMxSm1l6xwDXYjpEMiLMg==",
- "cpu": [
- "arm"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "android"
- ]
- },
- "node_modules/@rollup/rollup-android-arm64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-android-arm64/-/rollup-android-arm64-4.59.0.tgz",
- "integrity": "sha512-hZ+Zxj3SySm4A/DylsDKZAeVg0mvi++0PYVceVyX7hemkw7OreKdCvW2oQ3T1FMZvCaQXqOTHb8qmBShoqk69Q==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "android"
- ]
- },
- "node_modules/@rollup/rollup-darwin-arm64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-darwin-arm64/-/rollup-darwin-arm64-4.59.0.tgz",
- "integrity": "sha512-W2Psnbh1J8ZJw0xKAd8zdNgF9HRLkdWwwdWqubSVk0pUuQkoHnv7rx4GiF9rT4t5DIZGAsConRE3AxCdJ4m8rg==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "darwin"
- ]
- },
- "node_modules/@rollup/rollup-darwin-x64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-darwin-x64/-/rollup-darwin-x64-4.59.0.tgz",
- "integrity": "sha512-ZW2KkwlS4lwTv7ZVsYDiARfFCnSGhzYPdiOU4IM2fDbL+QGlyAbjgSFuqNRbSthybLbIJ915UtZBtmuLrQAT/w==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "darwin"
- ]
- },
- "node_modules/@rollup/rollup-freebsd-arm64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-freebsd-arm64/-/rollup-freebsd-arm64-4.59.0.tgz",
- "integrity": "sha512-EsKaJ5ytAu9jI3lonzn3BgG8iRBjV4LxZexygcQbpiU0wU0ATxhNVEpXKfUa0pS05gTcSDMKpn3Sx+QB9RlTTA==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "freebsd"
- ]
- },
- "node_modules/@rollup/rollup-freebsd-x64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-freebsd-x64/-/rollup-freebsd-x64-4.59.0.tgz",
- "integrity": "sha512-d3DuZi2KzTMjImrxoHIAODUZYoUUMsuUiY4SRRcJy6NJoZ6iIqWnJu9IScV9jXysyGMVuW+KNzZvBLOcpdl3Vg==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "freebsd"
- ]
- },
- "node_modules/@rollup/rollup-linux-arm-gnueabihf": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-arm-gnueabihf/-/rollup-linux-arm-gnueabihf-4.59.0.tgz",
- "integrity": "sha512-t4ONHboXi/3E0rT6OZl1pKbl2Vgxf9vJfWgmUoCEVQVxhW6Cw/c8I6hbbu7DAvgp82RKiH7TpLwxnJeKv2pbsw==",
- "cpu": [
- "arm"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-arm-musleabihf": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-arm-musleabihf/-/rollup-linux-arm-musleabihf-4.59.0.tgz",
- "integrity": "sha512-CikFT7aYPA2ufMD086cVORBYGHffBo4K8MQ4uPS/ZnY54GKj36i196u8U+aDVT2LX4eSMbyHtyOh7D7Zvk2VvA==",
- "cpu": [
- "arm"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-arm64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-arm64-gnu/-/rollup-linux-arm64-gnu-4.59.0.tgz",
- "integrity": "sha512-jYgUGk5aLd1nUb1CtQ8E+t5JhLc9x5WdBKew9ZgAXg7DBk0ZHErLHdXM24rfX+bKrFe+Xp5YuJo54I5HFjGDAA==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-arm64-musl": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-arm64-musl/-/rollup-linux-arm64-musl-4.59.0.tgz",
- "integrity": "sha512-peZRVEdnFWZ5Bh2KeumKG9ty7aCXzzEsHShOZEFiCQlDEepP1dpUl/SrUNXNg13UmZl+gzVDPsiCwnV1uI0RUA==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-loong64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-loong64-gnu/-/rollup-linux-loong64-gnu-4.59.0.tgz",
- "integrity": "sha512-gbUSW/97f7+r4gHy3Jlup8zDG190AuodsWnNiXErp9mT90iCy9NKKU0Xwx5k8VlRAIV2uU9CsMnEFg/xXaOfXg==",
- "cpu": [
- "loong64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-loong64-musl": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-loong64-musl/-/rollup-linux-loong64-musl-4.59.0.tgz",
- "integrity": "sha512-yTRONe79E+o0FWFijasoTjtzG9EBedFXJMl888NBEDCDV9I2wGbFFfJQQe63OijbFCUZqxpHz1GzpbtSFikJ4Q==",
- "cpu": [
- "loong64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-ppc64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-ppc64-gnu/-/rollup-linux-ppc64-gnu-4.59.0.tgz",
- "integrity": "sha512-sw1o3tfyk12k3OEpRddF68a1unZ5VCN7zoTNtSn2KndUE+ea3m3ROOKRCZxEpmT9nsGnogpFP9x6mnLTCaoLkA==",
- "cpu": [
- "ppc64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-ppc64-musl": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-ppc64-musl/-/rollup-linux-ppc64-musl-4.59.0.tgz",
- "integrity": "sha512-+2kLtQ4xT3AiIxkzFVFXfsmlZiG5FXYW7ZyIIvGA7Bdeuh9Z0aN4hVyXS/G1E9bTP/vqszNIN/pUKCk/BTHsKA==",
- "cpu": [
- "ppc64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-riscv64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-riscv64-gnu/-/rollup-linux-riscv64-gnu-4.59.0.tgz",
- "integrity": "sha512-NDYMpsXYJJaj+I7UdwIuHHNxXZ/b/N2hR15NyH3m2qAtb/hHPA4g4SuuvrdxetTdndfj9b1WOmy73kcPRoERUg==",
- "cpu": [
- "riscv64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-riscv64-musl": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-riscv64-musl/-/rollup-linux-riscv64-musl-4.59.0.tgz",
- "integrity": "sha512-nLckB8WOqHIf1bhymk+oHxvM9D3tyPndZH8i8+35p/1YiVoVswPid2yLzgX7ZJP0KQvnkhM4H6QZ5m0LzbyIAg==",
- "cpu": [
- "riscv64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-s390x-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-s390x-gnu/-/rollup-linux-s390x-gnu-4.59.0.tgz",
- "integrity": "sha512-oF87Ie3uAIvORFBpwnCvUzdeYUqi2wY6jRFWJAy1qus/udHFYIkplYRW+wo+GRUP4sKzYdmE1Y3+rY5Gc4ZO+w==",
- "cpu": [
- "s390x"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-x64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-x64-gnu/-/rollup-linux-x64-gnu-4.59.0.tgz",
- "integrity": "sha512-3AHmtQq/ppNuUspKAlvA8HtLybkDflkMuLK4DPo77DfthRb71V84/c4MlWJXixZz4uruIH4uaa07IqoAkG64fg==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-linux-x64-musl": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-linux-x64-musl/-/rollup-linux-x64-musl-4.59.0.tgz",
- "integrity": "sha512-2UdiwS/9cTAx7qIUZB/fWtToJwvt0Vbo0zmnYt7ED35KPg13Q0ym1g442THLC7VyI6JfYTP4PiSOWyoMdV2/xg==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "linux"
- ]
- },
- "node_modules/@rollup/rollup-openbsd-x64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-openbsd-x64/-/rollup-openbsd-x64-4.59.0.tgz",
- "integrity": "sha512-M3bLRAVk6GOwFlPTIxVBSYKUaqfLrn8l0psKinkCFxl4lQvOSz8ZrKDz2gxcBwHFpci0B6rttydI4IpS4IS/jQ==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "openbsd"
- ]
- },
- "node_modules/@rollup/rollup-openharmony-arm64": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-openharmony-arm64/-/rollup-openharmony-arm64-4.59.0.tgz",
- "integrity": "sha512-tt9KBJqaqp5i5HUZzoafHZX8b5Q2Fe7UjYERADll83O4fGqJ49O1FsL6LpdzVFQcpwvnyd0i+K/VSwu/o/nWlA==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "openharmony"
- ]
- },
- "node_modules/@rollup/rollup-win32-arm64-msvc": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-win32-arm64-msvc/-/rollup-win32-arm64-msvc-4.59.0.tgz",
- "integrity": "sha512-V5B6mG7OrGTwnxaNUzZTDTjDS7F75PO1ae6MJYdiMu60sq0CqN5CVeVsbhPxalupvTX8gXVSU9gq+Rx1/hvu6A==",
- "cpu": [
- "arm64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "win32"
- ]
- },
- "node_modules/@rollup/rollup-win32-ia32-msvc": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-win32-ia32-msvc/-/rollup-win32-ia32-msvc-4.59.0.tgz",
- "integrity": "sha512-UKFMHPuM9R0iBegwzKF4y0C4J9u8C6MEJgFuXTBerMk7EJ92GFVFYBfOZaSGLu6COf7FxpQNqhNS4c4icUPqxA==",
- "cpu": [
- "ia32"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "win32"
- ]
- },
- "node_modules/@rollup/rollup-win32-x64-gnu": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-win32-x64-gnu/-/rollup-win32-x64-gnu-4.59.0.tgz",
- "integrity": "sha512-laBkYlSS1n2L8fSo1thDNGrCTQMmxjYY5G0WFWjFFYZkKPjsMBsgJfGf4TLxXrF6RyhI60L8TMOjBMvXiTcxeA==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "win32"
- ]
- },
- "node_modules/@rollup/rollup-win32-x64-msvc": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/@rollup/rollup-win32-x64-msvc/-/rollup-win32-x64-msvc-4.59.0.tgz",
- "integrity": "sha512-2HRCml6OztYXyJXAvdDXPKcawukWY2GpR5/nxKp4iBgiO3wcoEGkAaqctIbZcNB6KlUQBIqt8VYkNSj2397EfA==",
- "cpu": [
- "x64"
- ],
- "dev": true,
- "license": "MIT",
- "optional": true,
- "os": [
- "win32"
- ]
- },
"node_modules/@simplewebauthn/server": {
- "version": "13.3.1",
- "resolved": "https://registry.npmmirror.com/@simplewebauthn/server/-/server-13.3.1.tgz",
- "integrity": "sha512-GV/oM/qeycWn8p42JZIMJBsXWQcNFg+nJFzeQTnMA4gN8mXg0+HZFWJerHg8ZN/zlveMS3iV1wzuFpOVWS/46w==",
+ "version": "13.3.2",
+ "resolved": "https://registry.npmjs.org/@simplewebauthn/server/-/server-13.3.2.tgz",
+ "integrity": "sha512-KEDhfcGP1PAKRVSDjA3npTQFqS2b/srm+ipoNBNHdkzrHAlaRQUTE+a5f4ywsx6thxAw1NU2rYcLEY1949RGbQ==",
"license": "MIT",
"dependencies": {
"@hexagon/base64": "^1.1.27",
@@ -2341,16 +2536,16 @@
}
},
"node_modules/@speed-highlight/core": {
- "version": "1.2.16",
- "resolved": "https://registry.npmjs.org/@speed-highlight/core/-/core-1.2.16.tgz",
- "integrity": "sha512-yNm/fYEcnpRjYduLMaddTK9XKYil6xB88+qFg79ZdZhHu1PadfoQmFW7pVTx7FZqMBNcUuThiAhxhENgtAO2/w==",
+ "version": "1.2.17",
+ "resolved": "https://registry.npmjs.org/@speed-highlight/core/-/core-1.2.17.tgz",
+ "integrity": "sha512-Z92FwKpCtfaW1V0jTU/fh3QzYEZN8wDwrzRIBoADCJfn4mJCNcJN/XegifX7BDrQ8/h9Xh/JnbyMchL0FqXrkg==",
"dev": true,
"license": "CC0-1.0"
},
"node_modules/@tanstack/query-core": {
- "version": "5.90.20",
- "resolved": "https://registry.npmmirror.com/@tanstack/query-core/-/query-core-5.90.20.tgz",
- "integrity": "sha512-OMD2HLpNouXEfZJWcKeVKUgQ5n+n3A2JFmBaScpNDUqSrQSjiveC7dKMe53uJUg1nDG16ttFPz2xfilz6i2uVg==",
+ "version": "5.101.2",
+ "resolved": "https://registry.npmjs.org/@tanstack/query-core/-/query-core-5.101.2.tgz",
+ "integrity": "sha512-hH5MLoJhF7KaIGd7q3xTXGXvslI+GYlM1Z/35aSHHWaCJWB7XvTSHYuV3eM7tw+aE0mT/xMro4M4Q9rCGHT0lw==",
"license": "MIT",
"funding": {
"type": "github",
@@ -2358,12 +2553,12 @@
}
},
"node_modules/@tanstack/react-query": {
- "version": "5.90.21",
- "resolved": "https://registry.npmmirror.com/@tanstack/react-query/-/react-query-5.90.21.tgz",
- "integrity": "sha512-0Lu6y5t+tvlTJMTO7oh5NSpJfpg/5D41LlThfepTixPYkJ0sE2Jj0m0f6yYqujBwIXlId87e234+MxG3D3g7kg==",
+ "version": "5.101.2",
+ "resolved": "https://registry.npmjs.org/@tanstack/react-query/-/react-query-5.101.2.tgz",
+ "integrity": "sha512-seDkr6kzGzX1okaaTtZPtgA688CDPlXUz1C6xSg0ESqn04Vuc8tlrYms1s3de+znBqhPVxFRfpAfUf+6XvfPWg==",
"license": "MIT",
"dependencies": {
- "@tanstack/query-core": "5.90.20"
+ "@tanstack/query-core": "5.101.2"
},
"funding": {
"type": "github",
@@ -2373,27 +2568,52 @@
"react": "^18 || ^19"
}
},
+ "node_modules/@tybys/wasm-util": {
+ "version": "0.10.3",
+ "resolved": "https://registry.npmjs.org/@tybys/wasm-util/-/wasm-util-0.10.3.tgz",
+ "integrity": "sha512-F3fo1MYrRJYL3zER0OUOmkutjr1Vp23m7OsSgp7nq4SP6OqX6C/56XFIPAl5bt3zaBRjmW7SGz3u/6LwFpYcOg==",
+ "dev": true,
+ "license": "MIT",
+ "optional": true,
+ "dependencies": {
+ "tslib": "^2.4.0"
+ }
+ },
"node_modules/@types/estree": {
"version": "1.0.8",
- "resolved": "https://registry.npmmirror.com/@types/estree/-/estree-1.0.8.tgz",
+ "resolved": "https://registry.npmjs.org/@types/estree/-/estree-1.0.8.tgz",
"integrity": "sha512-dWHzHa2WqEXI/O1E9OjrocMTKJl2mSrEolh1Iomrv6U+JuNwaHXsXx9bLu5gG7BUWFIN0skIQJQ/L1rIex4X6w==",
"dev": true,
"license": "MIT"
},
+ "node_modules/@types/gensync": {
+ "version": "1.0.5",
+ "resolved": "https://registry.npmmirror.com/@types/gensync/-/gensync-1.0.5.tgz",
+ "integrity": "sha512-MbsRCT7mTikHwKZ0X+LVUTLRrZZRLipTuXEO9qOYO+zmjMVk81axyClMROf6uoPD9MRVu46bx8zoR0Ad9q3NAg==",
+ "dev": true,
+ "license": "MIT"
+ },
+ "node_modules/@types/jsesc": {
+ "version": "2.5.1",
+ "resolved": "https://registry.npmmirror.com/@types/jsesc/-/jsesc-2.5.1.tgz",
+ "integrity": "sha512-9VN+6yxLOPLOav+7PwjZbxiID2bVaeq0ED4qSQmdQTdjnXJSaCVKTR58t15oqH1H5t8Ng2ZX1SabJVoN9Q34bw==",
+ "dev": true,
+ "license": "MIT"
+ },
"node_modules/@types/node": {
- "version": "25.2.3",
- "resolved": "https://registry.npmmirror.com/@types/node/-/node-25.2.3.tgz",
- "integrity": "sha512-m0jEgYlYz+mDJZ2+F4v8D1AyQb+QzsNqRuI7xg1VQX/KlKS0qT9r1Mo16yo5F/MtifXFgaofIFsdFMox2SxIbQ==",
+ "version": "26.0.1",
+ "resolved": "https://registry.npmjs.org/@types/node/-/node-26.0.1.tgz",
+ "integrity": "sha512-fc3KiUoBt6kie0N9bIW3E47vZsuaMf0PM2AaUpLCLT0s/LvX1nxAim6Fc049cNxODPpGm6qRAuUOB86SkRuPQw==",
"dev": true,
"license": "MIT",
"dependencies": {
- "undici-types": "~7.16.0"
+ "undici-types": "~8.3.0"
}
},
"node_modules/@zip.js/zip.js": {
- "version": "2.8.22",
- "resolved": "https://registry.npmmirror.com/@zip.js/zip.js/-/zip.js-2.8.22.tgz",
- "integrity": "sha512-0KlzbVR6r8irIX2o3zvUlosBDef62VDl47oUfa1U/qgEs67h4/eGBrX/6HWa1RQbt+J6sAeVmtyFKbTHNdF8qQ==",
+ "version": "2.8.26",
+ "resolved": "https://registry.npmjs.org/@zip.js/zip.js/-/zip.js-2.8.26.tgz",
+ "integrity": "sha512-RQ4h9F6DOiHxpdocUDrOl6xBM+yOtz+LkUol47AVWcfebGBDpZ7w7Xvz9PS24JgXvLGiXXzSAfdCdVy1tPlaFA==",
"license": "BSD-3-Clause",
"engines": {
"bun": ">=0.7.0",
@@ -2403,14 +2623,14 @@
},
"node_modules/any-promise": {
"version": "1.3.0",
- "resolved": "https://registry.npmmirror.com/any-promise/-/any-promise-1.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/any-promise/-/any-promise-1.3.0.tgz",
"integrity": "sha512-7UvmKalWRt1wgjL1RrGxoSJW/0QZFIegpeGvZG9kjp8vrRu55XTHbwnqq2GpXm9uLbcuhxm3IqX9OB4MZR1b2A==",
"dev": true,
"license": "MIT"
},
"node_modules/anymatch": {
"version": "3.1.3",
- "resolved": "https://registry.npmmirror.com/anymatch/-/anymatch-3.1.3.tgz",
+ "resolved": "https://registry.npmjs.org/anymatch/-/anymatch-3.1.3.tgz",
"integrity": "sha512-KMReFUr0B4t+D+OBkjR3KYqvocp2XaSzO55UcB6mgQMd3KbcE+mWTyvVV7D/zsdEbNnV6acZUutkiHQXvTr1Rw==",
"dev": true,
"license": "ISC",
@@ -2424,7 +2644,7 @@
},
"node_modules/anymatch/node_modules/picomatch": {
"version": "2.3.2",
- "resolved": "https://registry.npmmirror.com/picomatch/-/picomatch-2.3.2.tgz",
+ "resolved": "https://registry.npmjs.org/picomatch/-/picomatch-2.3.2.tgz",
"integrity": "sha512-V7+vQEJ06Z+c5tSye8S+nHUfI51xoXIXjHQ99cQtKUkQqqO1kO/KCJUfZXuB47h/YBlDhah2H3hdUGXn8ie0oA==",
"dev": true,
"license": "MIT",
@@ -2437,14 +2657,14 @@
},
"node_modules/arg": {
"version": "5.0.2",
- "resolved": "https://registry.npmmirror.com/arg/-/arg-5.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/arg/-/arg-5.0.2.tgz",
"integrity": "sha512-PYjyFOLKQ9y57JvQ6QLo8dAgNqswh8M1RMJYdQduT6xbWSgK36P/Z/v+p888pM69jMMfS8Xd8F6I1kQ/I9HUGg==",
"dev": true,
"license": "MIT"
},
"node_modules/asn1js": {
"version": "3.0.10",
- "resolved": "https://registry.npmmirror.com/asn1js/-/asn1js-3.0.10.tgz",
+ "resolved": "https://registry.npmjs.org/asn1js/-/asn1js-3.0.10.tgz",
"integrity": "sha512-S2s3aOytiKdFRdulw2qPE51MzjzVOisppcVv7jVFR+Kw0kxwvFrDcYA0h7Ndqbmj0HkMIXYWaoj7fli8kgx1eg==",
"license": "BSD-3-Clause",
"dependencies": {
@@ -2457,9 +2677,9 @@
}
},
"node_modules/autoprefixer": {
- "version": "10.4.21",
- "resolved": "https://registry.npmmirror.com/autoprefixer/-/autoprefixer-10.4.21.tgz",
- "integrity": "sha512-O+A6LWV5LDHSJD3LjHYoNi4VLsj/Whi7k6zG12xTYaU4cQ8oxQGckXNX8cRHK5yOZ/ppVHe0ZBXGzSV9jXdVbQ==",
+ "version": "10.5.2",
+ "resolved": "https://registry.npmjs.org/autoprefixer/-/autoprefixer-10.5.2.tgz",
+ "integrity": "sha512-rD5t5DwOjJdmSORcTq64j8MawTC+tbQ+HHqjR4NDumamy/ambn1UJrlKL+KdwujWxMkFjPM3pPHOEA9tl4767Q==",
"dev": true,
"funding": [
{
@@ -2477,10 +2697,9 @@
],
"license": "MIT",
"dependencies": {
- "browserslist": "^4.24.4",
- "caniuse-lite": "^1.0.30001702",
- "fraction.js": "^4.3.7",
- "normalize-range": "^0.1.2",
+ "browserslist": "^4.28.4",
+ "caniuse-lite": "^1.0.30001799",
+ "fraction.js": "^5.3.4",
"picocolors": "^1.1.1",
"postcss-value-parser": "^4.2.0"
},
@@ -2494,9 +2713,43 @@
"postcss": "^8.1.0"
}
},
+ "node_modules/autoprefixer/node_modules/browserslist": {
+ "version": "4.28.4",
+ "resolved": "https://registry.npmjs.org/browserslist/-/browserslist-4.28.4.tgz",
+ "integrity": "sha512-MTc8i/x9jBQd1iMw2CFGS+rwMa07eYjLR0CCTLDACl9xhxy+nIs3KeML/biicXtk9JrZ6dnnTatmc7ErPXIxqw==",
+ "dev": true,
+ "funding": [
+ {
+ "type": "opencollective",
+ "url": "https://opencollective.com/browserslist"
+ },
+ {
+ "type": "tidelift",
+ "url": "https://tidelift.com/funding/github/npm/browserslist"
+ },
+ {
+ "type": "github",
+ "url": "https://github.com/sponsors/ai"
+ }
+ ],
+ "license": "MIT",
+ "dependencies": {
+ "baseline-browser-mapping": "^2.10.38",
+ "caniuse-lite": "^1.0.30001799",
+ "electron-to-chromium": "^1.5.376",
+ "node-releases": "^2.0.48",
+ "update-browserslist-db": "^1.2.3"
+ },
+ "bin": {
+ "browserslist": "cli.js"
+ },
+ "engines": {
+ "node": "^6 || ^7 || ^8 || ^9 || ^10 || ^11 || ^12 || >=13.7"
+ }
+ },
"node_modules/babel-plugin-transform-hook-names": {
"version": "1.0.2",
- "resolved": "https://registry.npmmirror.com/babel-plugin-transform-hook-names/-/babel-plugin-transform-hook-names-1.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/babel-plugin-transform-hook-names/-/babel-plugin-transform-hook-names-1.0.2.tgz",
"integrity": "sha512-5gafyjyyBTTdX/tQQ0hRgu4AhNHG/hqWi0ZZmg2xvs2FgRkJXzDNKBZCyoYqgFkovfDrgM8OoKg8karoUvWeCw==",
"dev": true,
"license": "MIT",
@@ -2505,9 +2758,9 @@
}
},
"node_modules/baseline-browser-mapping": {
- "version": "2.10.0",
- "resolved": "https://registry.npmmirror.com/baseline-browser-mapping/-/baseline-browser-mapping-2.10.0.tgz",
- "integrity": "sha512-lIyg0szRfYbiy67j9KN8IyeD7q7hcmqnJ1ddWmNt19ItGpNN64mnllmxUNFIOdOm6by97jlL6wfpTTJrmnjWAA==",
+ "version": "2.10.40",
+ "resolved": "https://registry.npmjs.org/baseline-browser-mapping/-/baseline-browser-mapping-2.10.40.tgz",
+ "integrity": "sha512-BSSLZ9/Cjjv7Gtj5B68ZzXcXUg8iOf3fme+FCuh8rC/Go+Kmh8cox7M3A8dolou16s64QjLPOSdngh7GxXvkSw==",
"dev": true,
"license": "Apache-2.0",
"bin": {
@@ -2519,7 +2772,7 @@
},
"node_modules/binary-extensions": {
"version": "2.3.0",
- "resolved": "https://registry.npmmirror.com/binary-extensions/-/binary-extensions-2.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/binary-extensions/-/binary-extensions-2.3.0.tgz",
"integrity": "sha512-Ceh+7ox5qe7LJuLHoY0feh3pHuUDHAcRUeyL2VYghZwfpkNIy/+8Ocg0a3UuSoYzavmylwuLWQOf3hl0jjMMIw==",
"dev": true,
"license": "MIT",
@@ -2532,21 +2785,21 @@
},
"node_modules/blake3-wasm": {
"version": "2.1.5",
- "resolved": "https://registry.npmmirror.com/blake3-wasm/-/blake3-wasm-2.1.5.tgz",
+ "resolved": "https://registry.npmjs.org/blake3-wasm/-/blake3-wasm-2.1.5.tgz",
"integrity": "sha512-F1+K8EbfOZE49dtoPtmxUQrpXaBIl3ICvasLh+nJta0xkz+9kF/7uet9fLnwKqhDrmj6g+6K3Tw9yQPUg2ka5g==",
"dev": true,
"license": "MIT"
},
"node_modules/boolbase": {
"version": "1.0.0",
- "resolved": "https://registry.npmmirror.com/boolbase/-/boolbase-1.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/boolbase/-/boolbase-1.0.0.tgz",
"integrity": "sha512-JZOSA7Mo9sNGB8+UjSgzdLtokWAky1zbztM3WRLCbZ70/3cTANmQmOdR7y2g+J0e2WXywy1yS468tY+IruqEww==",
"dev": true,
"license": "ISC"
},
"node_modules/braces": {
"version": "3.0.3",
- "resolved": "https://registry.npmmirror.com/braces/-/braces-3.0.3.tgz",
+ "resolved": "https://registry.npmjs.org/braces/-/braces-3.0.3.tgz",
"integrity": "sha512-yQbXgO/OSZVD2IsiLlro+7Hf6Q18EJrKSEsdoMzKePKXct3gvD8oLcOQdIzGupr5Fj+EDe8gO/lxc1BzfMpxvA==",
"dev": true,
"license": "MIT",
@@ -2559,7 +2812,7 @@
},
"node_modules/browserslist": {
"version": "4.28.1",
- "resolved": "https://registry.npmmirror.com/browserslist/-/browserslist-4.28.1.tgz",
+ "resolved": "https://registry.npmjs.org/browserslist/-/browserslist-4.28.1.tgz",
"integrity": "sha512-ZC5Bd0LgJXgwGqUknZY/vkUQ04r8NXnJZ3yYi4vDmSiZmC/pdSN0NbNRPxZpbtO4uAfDUAFffO8IZoM3Gj8IkA==",
"dev": true,
"funding": [
@@ -2593,7 +2846,7 @@
},
"node_modules/camelcase-css": {
"version": "2.0.1",
- "resolved": "https://registry.npmmirror.com/camelcase-css/-/camelcase-css-2.0.1.tgz",
+ "resolved": "https://registry.npmjs.org/camelcase-css/-/camelcase-css-2.0.1.tgz",
"integrity": "sha512-QOSvevhslijgYwRx6Rv7zKdMF8lbRmx+uQGx2+vDc+KI/eBnsy9kit5aj23AgGu3pa4t9AgwbnXWqS+iOY+2aA==",
"dev": true,
"license": "MIT",
@@ -2602,9 +2855,9 @@
}
},
"node_modules/caniuse-lite": {
- "version": "1.0.30001774",
- "resolved": "https://registry.npmmirror.com/caniuse-lite/-/caniuse-lite-1.0.30001774.tgz",
- "integrity": "sha512-DDdwPGz99nmIEv216hKSgLD+D4ikHQHjBC/seF98N9CPqRX4M5mSxT9eTV6oyisnJcuzxtZy4n17yKKQYmYQOA==",
+ "version": "1.0.30001799",
+ "resolved": "https://registry.npmjs.org/caniuse-lite/-/caniuse-lite-1.0.30001799.tgz",
+ "integrity": "sha512-hG1bReV+OUU+MOqK4t/ZWI0tZOyz3rqS9XuhOUz1cIcbwBKjOyJEJuw9ER5JuNyqxNk8u/JUVbGibBOL1yrjFw==",
"dev": true,
"funding": [
{
@@ -2624,7 +2877,7 @@
},
"node_modules/chokidar": {
"version": "3.6.0",
- "resolved": "https://registry.npmmirror.com/chokidar/-/chokidar-3.6.0.tgz",
+ "resolved": "https://registry.npmjs.org/chokidar/-/chokidar-3.6.0.tgz",
"integrity": "sha512-7VT13fmjotKpGipCW9JEQAusEPE+Ei8nl6/g4FBAmIm0GOOLMua9NDDo/DWp0ZAxCr3cPq5ZpBqmPAQgDda2Pw==",
"dev": true,
"license": "MIT",
@@ -2649,7 +2902,7 @@
},
"node_modules/chokidar/node_modules/glob-parent": {
"version": "5.1.2",
- "resolved": "https://registry.npmmirror.com/glob-parent/-/glob-parent-5.1.2.tgz",
+ "resolved": "https://registry.npmjs.org/glob-parent/-/glob-parent-5.1.2.tgz",
"integrity": "sha512-AOIgSQCepiJYwP3ARnGx+5VnTu2HBYdzbGP45eLw1vr3zB3vZLeyed1sC9hnbcOc9/SrMyM5RPQrkGz4aS9Zow==",
"dev": true,
"license": "ISC",
@@ -2662,7 +2915,7 @@
},
"node_modules/commander": {
"version": "4.1.1",
- "resolved": "https://registry.npmmirror.com/commander/-/commander-4.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/commander/-/commander-4.1.1.tgz",
"integrity": "sha512-NOKm8xhkzAjzFx8B2v5OAHT+u5pRQc2UCa2Vq9jYL/31o2wi9mxBA7LIFs3sV5VSC49z6pEhfbMULvShKj26WA==",
"dev": true,
"license": "MIT",
@@ -2672,7 +2925,7 @@
},
"node_modules/convert-source-map": {
"version": "2.0.0",
- "resolved": "https://registry.npmmirror.com/convert-source-map/-/convert-source-map-2.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/convert-source-map/-/convert-source-map-2.0.0.tgz",
"integrity": "sha512-Kvp459HrV2FEJ1CAsi1Ku+MY3kasH19TFykTz2xWmMeq6bk2NU3XXvfJ+Q61m0xktWwt+1HSYf3JZsTms3aRJg==",
"dev": true,
"license": "MIT"
@@ -2693,7 +2946,7 @@
},
"node_modules/css-select": {
"version": "5.2.2",
- "resolved": "https://registry.npmmirror.com/css-select/-/css-select-5.2.2.tgz",
+ "resolved": "https://registry.npmjs.org/css-select/-/css-select-5.2.2.tgz",
"integrity": "sha512-TizTzUddG/xYLA3NXodFM0fSbNizXjOKhqiQQwvhlspadZokn1KDy0NZFS0wuEubIYAV5/c1/lAr0TaaFXEXzw==",
"dev": true,
"license": "BSD-2-Clause",
@@ -2710,7 +2963,7 @@
},
"node_modules/css-what": {
"version": "6.2.2",
- "resolved": "https://registry.npmmirror.com/css-what/-/css-what-6.2.2.tgz",
+ "resolved": "https://registry.npmjs.org/css-what/-/css-what-6.2.2.tgz",
"integrity": "sha512-u/O3vwbptzhMs3L1fQE82ZSLHQQfto5gyZzwteVIEyeaY5Fc7R4dapF/BvRoSYFeqfBk4m0V1Vafq5Pjv25wvA==",
"dev": true,
"license": "BSD-2-Clause",
@@ -2723,7 +2976,7 @@
},
"node_modules/cssesc": {
"version": "3.0.0",
- "resolved": "https://registry.npmmirror.com/cssesc/-/cssesc-3.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/cssesc/-/cssesc-3.0.0.tgz",
"integrity": "sha512-/Tb/JcjK111nNScGob5MNtsntNM1aCNUDipB/TkwZFhyDrrE47SOx/18wF2bbjgc3ZzCSKW1T5nt5EbFoAz/Vg==",
"dev": true,
"license": "MIT",
@@ -2736,7 +2989,7 @@
},
"node_modules/debug": {
"version": "4.4.3",
- "resolved": "https://registry.npmmirror.com/debug/-/debug-4.4.3.tgz",
+ "resolved": "https://registry.npmjs.org/debug/-/debug-4.4.3.tgz",
"integrity": "sha512-RGwwWnwQvkVfavKVt22FGLw+xYSdzARwm0ru6DhTVA3umU5hZc28V3kO4stgYryrTlLpuvgI9GiijltAjNbcqA==",
"dev": true,
"license": "MIT",
@@ -2764,21 +3017,21 @@
},
"node_modules/didyoumean": {
"version": "1.2.2",
- "resolved": "https://registry.npmmirror.com/didyoumean/-/didyoumean-1.2.2.tgz",
+ "resolved": "https://registry.npmjs.org/didyoumean/-/didyoumean-1.2.2.tgz",
"integrity": "sha512-gxtyfqMg7GKyhQmb056K7M3xszy/myH8w+B4RT+QXBQsvAOdc3XymqDDPHx1BgPgsdAA5SIifona89YtRATDzw==",
"dev": true,
"license": "Apache-2.0"
},
"node_modules/dlv": {
"version": "1.1.3",
- "resolved": "https://registry.npmmirror.com/dlv/-/dlv-1.1.3.tgz",
+ "resolved": "https://registry.npmjs.org/dlv/-/dlv-1.1.3.tgz",
"integrity": "sha512-+HlytyjlPKnIG8XuRG8WvmBP8xs8P71y+SKKS6ZXWoEgLuePxtDoUEiH7WkdePWrQ5JBpE6aoVqfZfJUQkjXwA==",
"dev": true,
"license": "MIT"
},
"node_modules/dom-serializer": {
"version": "2.0.0",
- "resolved": "https://registry.npmmirror.com/dom-serializer/-/dom-serializer-2.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/dom-serializer/-/dom-serializer-2.0.0.tgz",
"integrity": "sha512-wIkAryiqt/nV5EQKqQpo3SToSOV9J0DnbJqwK7Wv/Trc92zIAYZ4FlMu+JPFW1DfGFt81ZTCGgDEabffXeLyJg==",
"dev": true,
"license": "MIT",
@@ -2793,7 +3046,7 @@
},
"node_modules/domelementtype": {
"version": "2.3.0",
- "resolved": "https://registry.npmmirror.com/domelementtype/-/domelementtype-2.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/domelementtype/-/domelementtype-2.3.0.tgz",
"integrity": "sha512-OLETBj6w0OsagBwdXnPdN0cnMfF9opN69co+7ZrbfPGrdpPVNBUj02spi6B1N7wChLQiPn4CSH/zJvXw56gmHw==",
"dev": true,
"funding": [
@@ -2806,7 +3059,7 @@
},
"node_modules/domhandler": {
"version": "5.0.3",
- "resolved": "https://registry.npmmirror.com/domhandler/-/domhandler-5.0.3.tgz",
+ "resolved": "https://registry.npmjs.org/domhandler/-/domhandler-5.0.3.tgz",
"integrity": "sha512-cgwlv/1iFQiFnU96XXgROh8xTeetsnJiDsTc7TYCLFd9+/WNkIqPTxiM/8pSd8VIrhXGTf1Ny1q1hquVqDJB5w==",
"dev": true,
"license": "BSD-2-Clause",
@@ -2822,7 +3075,7 @@
},
"node_modules/domutils": {
"version": "3.2.2",
- "resolved": "https://registry.npmmirror.com/domutils/-/domutils-3.2.2.tgz",
+ "resolved": "https://registry.npmjs.org/domutils/-/domutils-3.2.2.tgz",
"integrity": "sha512-6kZKyUajlDuqlHKVX1w7gyslj9MPIXzIFiz/rGu35uC1wMi+kMhQwGhl4lt9unC9Vb9INnY9Z3/ZA3+FhASLaw==",
"dev": true,
"license": "BSD-2-Clause",
@@ -2836,15 +3089,25 @@
}
},
"node_modules/electron-to-chromium": {
- "version": "1.5.302",
- "resolved": "https://registry.npmmirror.com/electron-to-chromium/-/electron-to-chromium-1.5.302.tgz",
- "integrity": "sha512-sM6HAN2LyK82IyPBpznDRqlTQAtuSaO+ShzFiWTvoMJLHyZ+Y39r8VMfHzwbU8MVBzQ4Wdn85+wlZl2TLGIlwg==",
+ "version": "1.5.381",
+ "resolved": "https://registry.npmjs.org/electron-to-chromium/-/electron-to-chromium-1.5.381.tgz",
+ "integrity": "sha512-n9Wa6yB+vDsGuA8AKbl/0z7HbvWqt5jxIdvr1IUicd0ryPrk7/xzwqLv8D9AbbvZ6avVNtXYLTfmgFHkwkyelg==",
"dev": true,
"license": "ISC"
},
+ "node_modules/empathic": {
+ "version": "2.0.1",
+ "resolved": "https://registry.npmmirror.com/empathic/-/empathic-2.0.1.tgz",
+ "integrity": "sha512-YGRs8knHhKHVShLkFET/rWAU8kmHbOV5LwN938RHI0pljAJ1Gf6SzXsSmRaEzcXTtOOmVqJ5+WtQPL5uigY50Q==",
+ "dev": true,
+ "license": "MIT",
+ "engines": {
+ "node": ">=14"
+ }
+ },
"node_modules/entities": {
"version": "4.5.0",
- "resolved": "https://registry.npmmirror.com/entities/-/entities-4.5.0.tgz",
+ "resolved": "https://registry.npmjs.org/entities/-/entities-4.5.0.tgz",
"integrity": "sha512-V0hjH4dGPh9Ao5p0MoRY6BVqtwCjhz6vI5LT8AJ55H+4g9/4vbHx1I54fS0XuclLhDHArPQCiMjDxjaL8fPxhw==",
"dev": true,
"license": "BSD-2-Clause",
@@ -2867,7 +3130,7 @@
},
"node_modules/es-errors": {
"version": "1.3.0",
- "resolved": "https://registry.npmmirror.com/es-errors/-/es-errors-1.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/es-errors/-/es-errors-1.3.0.tgz",
"integrity": "sha512-Zf5H2Kxt2xjTvbJvP2ZWLEICxA6j+hAmMzIlypy4xcBg1vKVnx89Wy0GbS+kf5cwCVFFzdCFh2XSCFNULS6csw==",
"dev": true,
"license": "MIT",
@@ -2876,9 +3139,9 @@
}
},
"node_modules/esbuild": {
- "version": "0.27.3",
- "resolved": "https://registry.npmmirror.com/esbuild/-/esbuild-0.27.3.tgz",
- "integrity": "sha512-8VwMnyGCONIs6cWue2IdpHxHnAjzxnw2Zr7MkVxB2vjmQ2ivqGFb4LEG3SMnv0Gb2F/G/2yA8zUaiL1gywDCCg==",
+ "version": "0.28.1",
+ "resolved": "https://registry.npmmirror.com/esbuild/-/esbuild-0.28.1.tgz",
+ "integrity": "sha512-HrJrvZv5ayxBzPfwphOoNzkzOIIlifzk0KJrGK2c8R4+LKpMtpYLQeUdjnwjWv/LZlkH2laZk+4w78pi99D4Vw==",
"dev": true,
"hasInstallScript": true,
"license": "MIT",
@@ -2889,37 +3152,37 @@
"node": ">=18"
},
"optionalDependencies": {
- "@esbuild/aix-ppc64": "0.27.3",
- "@esbuild/android-arm": "0.27.3",
- "@esbuild/android-arm64": "0.27.3",
- "@esbuild/android-x64": "0.27.3",
- "@esbuild/darwin-arm64": "0.27.3",
- "@esbuild/darwin-x64": "0.27.3",
- "@esbuild/freebsd-arm64": "0.27.3",
- "@esbuild/freebsd-x64": "0.27.3",
- "@esbuild/linux-arm": "0.27.3",
- "@esbuild/linux-arm64": "0.27.3",
- "@esbuild/linux-ia32": "0.27.3",
- "@esbuild/linux-loong64": "0.27.3",
- "@esbuild/linux-mips64el": "0.27.3",
- "@esbuild/linux-ppc64": "0.27.3",
- "@esbuild/linux-riscv64": "0.27.3",
- "@esbuild/linux-s390x": "0.27.3",
- "@esbuild/linux-x64": "0.27.3",
- "@esbuild/netbsd-arm64": "0.27.3",
- "@esbuild/netbsd-x64": "0.27.3",
- "@esbuild/openbsd-arm64": "0.27.3",
- "@esbuild/openbsd-x64": "0.27.3",
- "@esbuild/openharmony-arm64": "0.27.3",
- "@esbuild/sunos-x64": "0.27.3",
- "@esbuild/win32-arm64": "0.27.3",
- "@esbuild/win32-ia32": "0.27.3",
- "@esbuild/win32-x64": "0.27.3"
+ "@esbuild/aix-ppc64": "0.28.1",
+ "@esbuild/android-arm": "0.28.1",
+ "@esbuild/android-arm64": "0.28.1",
+ "@esbuild/android-x64": "0.28.1",
+ "@esbuild/darwin-arm64": "0.28.1",
+ "@esbuild/darwin-x64": "0.28.1",
+ "@esbuild/freebsd-arm64": "0.28.1",
+ "@esbuild/freebsd-x64": "0.28.1",
+ "@esbuild/linux-arm": "0.28.1",
+ "@esbuild/linux-arm64": "0.28.1",
+ "@esbuild/linux-ia32": "0.28.1",
+ "@esbuild/linux-loong64": "0.28.1",
+ "@esbuild/linux-mips64el": "0.28.1",
+ "@esbuild/linux-ppc64": "0.28.1",
+ "@esbuild/linux-riscv64": "0.28.1",
+ "@esbuild/linux-s390x": "0.28.1",
+ "@esbuild/linux-x64": "0.28.1",
+ "@esbuild/netbsd-arm64": "0.28.1",
+ "@esbuild/netbsd-x64": "0.28.1",
+ "@esbuild/openbsd-arm64": "0.28.1",
+ "@esbuild/openbsd-x64": "0.28.1",
+ "@esbuild/openharmony-arm64": "0.28.1",
+ "@esbuild/sunos-x64": "0.28.1",
+ "@esbuild/win32-arm64": "0.28.1",
+ "@esbuild/win32-ia32": "0.28.1",
+ "@esbuild/win32-x64": "0.28.1"
}
},
"node_modules/escalade": {
"version": "3.2.0",
- "resolved": "https://registry.npmmirror.com/escalade/-/escalade-3.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/escalade/-/escalade-3.2.0.tgz",
"integrity": "sha512-WUj2qlxaQtO4g6Pq5c29GTcWGDyd8itL8zTlipgECz3JesAiiOKotd8JU6otB3PACgG6xkJUyVhboMS+bje/jA==",
"dev": true,
"license": "MIT",
@@ -2929,14 +3192,14 @@
},
"node_modules/estree-walker": {
"version": "2.0.2",
- "resolved": "https://registry.npmmirror.com/estree-walker/-/estree-walker-2.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/estree-walker/-/estree-walker-2.0.2.tgz",
"integrity": "sha512-Rfkk/Mp/DL7JVje3u18FxFujQlTNR2q6QfMSMB7AvCBx91NGj/ba3kCfza0f6dVDbw7YlRf/nDrn7pQrCCyQ/w==",
"dev": true,
"license": "MIT"
},
"node_modules/fast-glob": {
"version": "3.3.3",
- "resolved": "https://registry.npmmirror.com/fast-glob/-/fast-glob-3.3.3.tgz",
+ "resolved": "https://registry.npmjs.org/fast-glob/-/fast-glob-3.3.3.tgz",
"integrity": "sha512-7MptL8U0cqcFdzIzwOTHoilX9x5BrNqye7Z/LuC7kCMRio1EMSyqRK3BEAUD7sXRq4iT4AzTVuZdhgQ2TCvYLg==",
"dev": true,
"license": "MIT",
@@ -2953,7 +3216,7 @@
},
"node_modules/fast-glob/node_modules/glob-parent": {
"version": "5.1.2",
- "resolved": "https://registry.npmmirror.com/glob-parent/-/glob-parent-5.1.2.tgz",
+ "resolved": "https://registry.npmjs.org/glob-parent/-/glob-parent-5.1.2.tgz",
"integrity": "sha512-AOIgSQCepiJYwP3ARnGx+5VnTu2HBYdzbGP45eLw1vr3zB3vZLeyed1sC9hnbcOc9/SrMyM5RPQrkGz4aS9Zow==",
"dev": true,
"license": "ISC",
@@ -2966,7 +3229,7 @@
},
"node_modules/fastq": {
"version": "1.20.1",
- "resolved": "https://registry.npmmirror.com/fastq/-/fastq-1.20.1.tgz",
+ "resolved": "https://registry.npmjs.org/fastq/-/fastq-1.20.1.tgz",
"integrity": "sha512-GGToxJ/w1x32s/D2EKND7kTil4n8OVk/9mycTc4VDza13lOvpUZTGX3mFSCtV9ksdGBVzvsyAVLM6mHFThxXxw==",
"dev": true,
"license": "ISC",
@@ -2976,7 +3239,7 @@
},
"node_modules/fdir": {
"version": "6.5.0",
- "resolved": "https://registry.npmmirror.com/fdir/-/fdir-6.5.0.tgz",
+ "resolved": "https://registry.npmjs.org/fdir/-/fdir-6.5.0.tgz",
"integrity": "sha512-tIbYtZbucOs0BRGqPJkshJUYdL+SDH7dVM8gjy+ERp3WAUjLEFJE+02kanyHtwjWOnwrKYBiwAmM0p4kLJAnXg==",
"dev": true,
"license": "MIT",
@@ -2993,14 +3256,14 @@
}
},
"node_modules/fflate": {
- "version": "0.8.2",
- "resolved": "https://registry.npmmirror.com/fflate/-/fflate-0.8.2.tgz",
- "integrity": "sha512-cPJU47OaAoCbg0pBvzsgpTPhmhqI5eJjh/JIu8tPj5q+T7iLvW/JAYUqmE7KOB4R1ZyEhzBaIQpQpardBF5z8A==",
+ "version": "0.8.3",
+ "resolved": "https://registry.npmjs.org/fflate/-/fflate-0.8.3.tgz",
+ "integrity": "sha512-tbZNuJrLwGUp3zshBtdy4W+ORxZuIh8a5ilyIEQDC5rY1f3U20JMry0Ll3WBzU58EZKsEuJFXhb5gwv8CsPvgA==",
"license": "MIT"
},
"node_modules/fill-range": {
"version": "7.1.1",
- "resolved": "https://registry.npmmirror.com/fill-range/-/fill-range-7.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/fill-range/-/fill-range-7.1.1.tgz",
"integrity": "sha512-YsGpe3WHLK8ZYi4tWDg2Jy3ebRz2rXowDxnld4bkQB00cc/1Zw9AWnC0i9ztDJitivtQvaI9KaLyKrc+hBW0yg==",
"dev": true,
"license": "MIT",
@@ -3012,22 +3275,22 @@
}
},
"node_modules/fraction.js": {
- "version": "4.3.7",
- "resolved": "https://registry.npmmirror.com/fraction.js/-/fraction.js-4.3.7.tgz",
- "integrity": "sha512-ZsDfxO51wGAXREY55a7la9LScWpwv9RxIrYABrlvOFBlH/ShPnrtsXeuUIfXKKOVicNxQ+o8JTbJvjS4M89yew==",
+ "version": "5.3.4",
+ "resolved": "https://registry.npmjs.org/fraction.js/-/fraction.js-5.3.4.tgz",
+ "integrity": "sha512-1X1NTtiJphryn/uLQz3whtY6jK3fTqoE3ohKs0tT+Ujr1W59oopxmoEh7Lu5p6vBaPbgoM0bzveAW4Qi5RyWDQ==",
"dev": true,
"license": "MIT",
"engines": {
"node": "*"
},
"funding": {
- "type": "patreon",
+ "type": "github",
"url": "https://github.com/sponsors/rawify"
}
},
"node_modules/fsevents": {
"version": "2.3.3",
- "resolved": "https://registry.npmmirror.com/fsevents/-/fsevents-2.3.3.tgz",
+ "resolved": "https://registry.npmjs.org/fsevents/-/fsevents-2.3.3.tgz",
"integrity": "sha512-5xoDfX+fL7faATnagmWPpbFtwh/R77WmMMqqHGS65C3vvB0YHrgF+B1YmZ3441tMj5n63k0212XNoJwzlhffQw==",
"dev": true,
"hasInstallScript": true,
@@ -3042,7 +3305,7 @@
},
"node_modules/function-bind": {
"version": "1.1.2",
- "resolved": "https://registry.npmmirror.com/function-bind/-/function-bind-1.1.2.tgz",
+ "resolved": "https://registry.npmjs.org/function-bind/-/function-bind-1.1.2.tgz",
"integrity": "sha512-7XHNxH7qX9xG5mIwxkhumTox/MIRNcOgDrxWsMt2pAr23WHp6MrRlN7FBSFpCpr+oVO0F744iUgR82nJMfG2SA==",
"dev": true,
"license": "MIT",
@@ -3052,7 +3315,7 @@
},
"node_modules/gensync": {
"version": "1.0.0-beta.2",
- "resolved": "https://registry.npmmirror.com/gensync/-/gensync-1.0.0-beta.2.tgz",
+ "resolved": "https://registry.npmjs.org/gensync/-/gensync-1.0.0-beta.2.tgz",
"integrity": "sha512-3hN7NaskYvMDLQY55gnW3NQ+mesEAepTqlg+VEbj7zzqEMBVNhzcGYYeqFo/TlYz6eQiFcp1HcsCZO+nGgS8zg==",
"dev": true,
"license": "MIT",
@@ -3060,22 +3323,9 @@
"node": ">=6.9.0"
}
},
- "node_modules/get-tsconfig": {
- "version": "4.13.6",
- "resolved": "https://registry.npmmirror.com/get-tsconfig/-/get-tsconfig-4.13.6.tgz",
- "integrity": "sha512-shZT/QMiSHc/YBLxxOkMtgSid5HFoauqCE3/exfsEcwg1WkeqjG+V40yBbBrsD+jW2HDXcs28xOfcbm2jI8Ddw==",
- "dev": true,
- "license": "MIT",
- "dependencies": {
- "resolve-pkg-maps": "^1.0.0"
- },
- "funding": {
- "url": "https://github.com/privatenumber/get-tsconfig?sponsor=1"
- }
- },
"node_modules/glob-parent": {
"version": "6.0.2",
- "resolved": "https://registry.npmmirror.com/glob-parent/-/glob-parent-6.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/glob-parent/-/glob-parent-6.0.2.tgz",
"integrity": "sha512-XxwI8EOhVQgWp6iDL+3b0r86f4d6AX6zSU55HfB4ydCEuXLXc5FcYeOu+nnGftS4TEju/11rt4KJPTMgbfmv4A==",
"dev": true,
"license": "ISC",
@@ -3088,7 +3338,7 @@
},
"node_modules/hasown": {
"version": "2.0.3",
- "resolved": "https://registry.npmmirror.com/hasown/-/hasown-2.0.3.tgz",
+ "resolved": "https://registry.npmjs.org/hasown/-/hasown-2.0.3.tgz",
"integrity": "sha512-ej4AhfhfL2Q2zpMmLo7U1Uv9+PyhIZpgQLGT1F9miIGmiCJIoCgSmczFdrc97mWT4kVY72KA+WnnhJ5pghSvSg==",
"dev": true,
"license": "MIT",
@@ -3101,7 +3351,7 @@
},
"node_modules/he": {
"version": "1.2.0",
- "resolved": "https://registry.npmmirror.com/he/-/he-1.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/he/-/he-1.2.0.tgz",
"integrity": "sha512-F/1DnUGPopORZi0ni+CvrCgHQ5FyEAHRLSApuYWMmrbSwoN2Mn/7k+Gl38gJnR7yyDZk6WLXwiGod1JOWNDKGw==",
"dev": true,
"license": "MIT",
@@ -3109,9 +3359,20 @@
"he": "bin/he"
}
},
+ "node_modules/import-meta-resolve": {
+ "version": "4.2.0",
+ "resolved": "https://registry.npmmirror.com/import-meta-resolve/-/import-meta-resolve-4.2.0.tgz",
+ "integrity": "sha512-Iqv2fzaTQN28s/FwZAoFq0ZSs/7hMAHJVX+w8PZl3cY19Pxk6jFFalxQoIfW2826i/fDLXv8IiEZRIT0lDuWcg==",
+ "dev": true,
+ "license": "MIT",
+ "funding": {
+ "type": "github",
+ "url": "https://github.com/sponsors/wooorm"
+ }
+ },
"node_modules/is-binary-path": {
"version": "2.1.0",
- "resolved": "https://registry.npmmirror.com/is-binary-path/-/is-binary-path-2.1.0.tgz",
+ "resolved": "https://registry.npmjs.org/is-binary-path/-/is-binary-path-2.1.0.tgz",
"integrity": "sha512-ZMERYes6pDydyuGidse7OsHxtbI7WVeUEozgR/g7rd0xUimYNlvZRE/K2MgZTjWy725IfelLeVcEM97mmtRGXw==",
"dev": true,
"license": "MIT",
@@ -3124,7 +3385,7 @@
},
"node_modules/is-core-module": {
"version": "2.16.1",
- "resolved": "https://registry.npmmirror.com/is-core-module/-/is-core-module-2.16.1.tgz",
+ "resolved": "https://registry.npmjs.org/is-core-module/-/is-core-module-2.16.1.tgz",
"integrity": "sha512-UfoeMA6fIJ8wTYFEUjelnaGI67v6+N7qXJEvQuIGa99l4xsCruSYOVSQ0uPANn4dAzm8lkYPaKLrrijLq7x23w==",
"dev": true,
"license": "MIT",
@@ -3140,7 +3401,7 @@
},
"node_modules/is-extglob": {
"version": "2.1.1",
- "resolved": "https://registry.npmmirror.com/is-extglob/-/is-extglob-2.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/is-extglob/-/is-extglob-2.1.1.tgz",
"integrity": "sha512-SbKbANkN603Vi4jEZv49LeVJMn4yGwsbzZworEoyEiutsN3nJYdbO36zfhGJ6QEDpOZIFkDtnq5JRxmvl3jsoQ==",
"dev": true,
"license": "MIT",
@@ -3150,7 +3411,7 @@
},
"node_modules/is-glob": {
"version": "4.0.3",
- "resolved": "https://registry.npmmirror.com/is-glob/-/is-glob-4.0.3.tgz",
+ "resolved": "https://registry.npmjs.org/is-glob/-/is-glob-4.0.3.tgz",
"integrity": "sha512-xelSayHH36ZgE7ZWhli7pW34hNbNl8Ojv5KVmkJD4hBdD3th8Tfk9vYasLM+mXWOZhFkgZfxhLSnrwRr4elSSg==",
"dev": true,
"license": "MIT",
@@ -3163,7 +3424,7 @@
},
"node_modules/is-number": {
"version": "7.0.0",
- "resolved": "https://registry.npmmirror.com/is-number/-/is-number-7.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/is-number/-/is-number-7.0.0.tgz",
"integrity": "sha512-41Cifkg6e8TylSpdtTpeLVMqvSBEVzTttHvERD741+pnZ8ANv0004MRL43QKPDlK9cGvNp6NZWZUBlbGXYxxng==",
"dev": true,
"license": "MIT",
@@ -3173,7 +3434,7 @@
},
"node_modules/jiti": {
"version": "1.21.7",
- "resolved": "https://registry.npmmirror.com/jiti/-/jiti-1.21.7.tgz",
+ "resolved": "https://registry.npmjs.org/jiti/-/jiti-1.21.7.tgz",
"integrity": "sha512-/imKNG4EbWNrVjoNC/1H5/9GFy+tqjGBHCaSsN+P2RnPqjsLmv6UD3Ej+Kj8nBWaRAwyk7kK5ZUc+OEatnTR3A==",
"dev": true,
"license": "MIT",
@@ -3183,14 +3444,14 @@
},
"node_modules/js-tokens": {
"version": "4.0.0",
- "resolved": "https://registry.npmmirror.com/js-tokens/-/js-tokens-4.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/js-tokens/-/js-tokens-4.0.0.tgz",
"integrity": "sha512-RdJUflcE3cUzKiMqQgsCu06FPu9UdIJO0beYbPhHN4k6apgJtifcoCtT9bcxOpYBtpD2kCM6Sbzg4CausW/PKQ==",
"dev": true,
"license": "MIT"
},
"node_modules/jsesc": {
"version": "3.1.0",
- "resolved": "https://registry.npmmirror.com/jsesc/-/jsesc-3.1.0.tgz",
+ "resolved": "https://registry.npmjs.org/jsesc/-/jsesc-3.1.0.tgz",
"integrity": "sha512-/sM3dO2FOzXjKQhJuo0Q173wf2KOo8t4I8vHy6lF9poUp7bKT0/NHE8fPX23PwfhnykfqnC2xRxOnVw5XuGIaA==",
"dev": true,
"license": "MIT",
@@ -3203,7 +3464,7 @@
},
"node_modules/json5": {
"version": "2.2.3",
- "resolved": "https://registry.npmmirror.com/json5/-/json5-2.2.3.tgz",
+ "resolved": "https://registry.npmjs.org/json5/-/json5-2.2.3.tgz",
"integrity": "sha512-XmOWe7eyHYH14cLdVPoyg+GOH3rYX++KpzrylJwSW98t3Nk+U8XOl8FWKOgwtzdb8lXGf6zYwDUzeHMWfxasyg==",
"dev": true,
"license": "MIT",
@@ -3214,6 +3475,12 @@
"node": ">=6"
}
},
+ "node_modules/jsqr": {
+ "version": "1.4.0",
+ "resolved": "https://registry.npmjs.org/jsqr/-/jsqr-1.4.0.tgz",
+ "integrity": "sha512-dxLob7q65Xg2DvstYkRpkYtmKm2sPJ9oFhrhmudT1dZvNFFTlroai3AWSpLey/w5vMcLBXRgOJsbXpdN9HzU/A==",
+ "license": "Apache-2.0"
+ },
"node_modules/kleur": {
"version": "4.1.5",
"resolved": "https://registry.npmjs.org/kleur/-/kleur-4.1.5.tgz",
@@ -3226,14 +3493,287 @@
},
"node_modules/kolorist": {
"version": "1.8.0",
- "resolved": "https://registry.npmmirror.com/kolorist/-/kolorist-1.8.0.tgz",
+ "resolved": "https://registry.npmjs.org/kolorist/-/kolorist-1.8.0.tgz",
"integrity": "sha512-Y+60/zizpJ3HRH8DCss+q95yr6145JXZo46OTpFvDZWLfRCE4qChOyk1b26nMaNpfHHgxagk9dXT5OP0Tfe+dQ==",
"dev": true,
"license": "MIT"
},
+ "node_modules/lightningcss": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss/-/lightningcss-1.32.0.tgz",
+ "integrity": "sha512-NXYBzinNrblfraPGyrbPoD19C1h9lfI/1mzgWYvXUTe414Gz/X1FD2XBZSZM7rRTrMA8JL3OtAaGifrIKhQ5yQ==",
+ "dev": true,
+ "license": "MPL-2.0",
+ "dependencies": {
+ "detect-libc": "^2.0.3"
+ },
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ },
+ "optionalDependencies": {
+ "lightningcss-android-arm64": "1.32.0",
+ "lightningcss-darwin-arm64": "1.32.0",
+ "lightningcss-darwin-x64": "1.32.0",
+ "lightningcss-freebsd-x64": "1.32.0",
+ "lightningcss-linux-arm-gnueabihf": "1.32.0",
+ "lightningcss-linux-arm64-gnu": "1.32.0",
+ "lightningcss-linux-arm64-musl": "1.32.0",
+ "lightningcss-linux-x64-gnu": "1.32.0",
+ "lightningcss-linux-x64-musl": "1.32.0",
+ "lightningcss-win32-arm64-msvc": "1.32.0",
+ "lightningcss-win32-x64-msvc": "1.32.0"
+ }
+ },
+ "node_modules/lightningcss-android-arm64": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-android-arm64/-/lightningcss-android-arm64-1.32.0.tgz",
+ "integrity": "sha512-YK7/ClTt4kAK0vo6w3X+Pnm0D2cf2vPHbhOXdoNti1Ga0al1P4TBZhwjATvjNwLEBCnKvjJc2jQgHXH0NEwlAg==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "android"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-darwin-arm64": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-darwin-arm64/-/lightningcss-darwin-arm64-1.32.0.tgz",
+ "integrity": "sha512-RzeG9Ju5bag2Bv1/lwlVJvBE3q6TtXskdZLLCyfg5pt+HLz9BqlICO7LZM7VHNTTn/5PRhHFBSjk5lc4cmscPQ==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "darwin"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-darwin-x64": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-darwin-x64/-/lightningcss-darwin-x64-1.32.0.tgz",
+ "integrity": "sha512-U+QsBp2m/s2wqpUYT/6wnlagdZbtZdndSmut/NJqlCcMLTWp5muCrID+K5UJ6jqD2BFshejCYXniPDbNh73V8w==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "darwin"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-freebsd-x64": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-freebsd-x64/-/lightningcss-freebsd-x64-1.32.0.tgz",
+ "integrity": "sha512-JCTigedEksZk3tHTTthnMdVfGf61Fky8Ji2E4YjUTEQX14xiy/lTzXnu1vwiZe3bYe0q+SpsSH/CTeDXK6WHig==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "freebsd"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-linux-arm-gnueabihf": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-linux-arm-gnueabihf/-/lightningcss-linux-arm-gnueabihf-1.32.0.tgz",
+ "integrity": "sha512-x6rnnpRa2GL0zQOkt6rts3YDPzduLpWvwAF6EMhXFVZXD4tPrBkEFqzGowzCsIWsPjqSK+tyNEODUBXeeVHSkw==",
+ "cpu": [
+ "arm"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-linux-arm64-gnu": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-linux-arm64-gnu/-/lightningcss-linux-arm64-gnu-1.32.0.tgz",
+ "integrity": "sha512-0nnMyoyOLRJXfbMOilaSRcLH3Jw5z9HDNGfT/gwCPgaDjnx0i8w7vBzFLFR1f6CMLKF8gVbebmkUN3fa/kQJpQ==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-linux-arm64-musl": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-linux-arm64-musl/-/lightningcss-linux-arm64-musl-1.32.0.tgz",
+ "integrity": "sha512-UpQkoenr4UJEzgVIYpI80lDFvRmPVg6oqboNHfoH4CQIfNA+HOrZ7Mo7KZP02dC6LjghPQJeBsvXhJod/wnIBg==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "libc": [
+ "musl"
+ ],
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-linux-x64-gnu": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-linux-x64-gnu/-/lightningcss-linux-x64-gnu-1.32.0.tgz",
+ "integrity": "sha512-V7Qr52IhZmdKPVr+Vtw8o+WLsQJYCTd8loIfpDaMRWGUZfBOYEJeyJIkqGIDMZPwPx24pUMfwSxxI8phr/MbOA==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "libc": [
+ "glibc"
+ ],
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-linux-x64-musl": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-linux-x64-musl/-/lightningcss-linux-x64-musl-1.32.0.tgz",
+ "integrity": "sha512-bYcLp+Vb0awsiXg/80uCRezCYHNg1/l3mt0gzHnWV9XP1W5sKa5/TCdGWaR/zBM2PeF/HbsQv/j2URNOiVuxWg==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "libc": [
+ "musl"
+ ],
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "linux"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-win32-arm64-msvc": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-win32-arm64-msvc/-/lightningcss-win32-arm64-msvc-1.32.0.tgz",
+ "integrity": "sha512-8SbC8BR40pS6baCM8sbtYDSwEVQd4JlFTOlaD3gWGHfThTcABnNDBda6eTZeqbofalIJhFx0qKzgHJmcPTnGdw==",
+ "cpu": [
+ "arm64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "win32"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
+ "node_modules/lightningcss-win32-x64-msvc": {
+ "version": "1.32.0",
+ "resolved": "https://registry.npmjs.org/lightningcss-win32-x64-msvc/-/lightningcss-win32-x64-msvc-1.32.0.tgz",
+ "integrity": "sha512-Amq9B/SoZYdDi1kFrojnoqPLxYhQ4Wo5XiL8EVJrVsB8ARoC1PWW6VGtT0WKCemjy8aC+louJnjS7U18x3b06Q==",
+ "cpu": [
+ "x64"
+ ],
+ "dev": true,
+ "license": "MPL-2.0",
+ "optional": true,
+ "os": [
+ "win32"
+ ],
+ "engines": {
+ "node": ">= 12.0.0"
+ },
+ "funding": {
+ "type": "opencollective",
+ "url": "https://opencollective.com/parcel"
+ }
+ },
"node_modules/lilconfig": {
"version": "3.1.3",
- "resolved": "https://registry.npmmirror.com/lilconfig/-/lilconfig-3.1.3.tgz",
+ "resolved": "https://registry.npmjs.org/lilconfig/-/lilconfig-3.1.3.tgz",
"integrity": "sha512-/vlFKAoH5Cgt3Ie+JLhRbwOsCQePABiU3tJ1egGvyQ+33R/vcwM2Zl2QR/LzjsBeItPt3oSVXapn+m4nQDvpzw==",
"dev": true,
"license": "MIT",
@@ -3246,25 +3786,25 @@
},
"node_modules/lines-and-columns": {
"version": "1.2.4",
- "resolved": "https://registry.npmmirror.com/lines-and-columns/-/lines-and-columns-1.2.4.tgz",
+ "resolved": "https://registry.npmjs.org/lines-and-columns/-/lines-and-columns-1.2.4.tgz",
"integrity": "sha512-7ylylesZQ/PV29jhEDl3Ufjo6ZX7gCqJr5F7PKrqc93v7fzSymt1BpwEU8nAUXs8qzzvqhbjhK5QZg6Mt/HkBg==",
"dev": true,
"license": "MIT"
},
"node_modules/lru-cache": {
- "version": "5.1.1",
- "resolved": "https://registry.npmmirror.com/lru-cache/-/lru-cache-5.1.1.tgz",
- "integrity": "sha512-KpNARQA3Iwv+jTA0utUVVbrh+Jlrr1Fv0e56GGzAFOXN7dk/FviaDW8LHmK52DlcH4WP2n6gI8vN1aesBFgo9w==",
+ "version": "11.5.1",
+ "resolved": "https://registry.npmmirror.com/lru-cache/-/lru-cache-11.5.1.tgz",
+ "integrity": "sha512-RPimw/7aMdv2oqRrxKwvZXcPfwBrn/JZ2xYcY9Hus/6LaS3VOAKVWKWgNLCFSiOm1ESXinjsDlidVU7JlnCN2A==",
"dev": true,
- "license": "ISC",
- "dependencies": {
- "yallist": "^3.0.2"
+ "license": "BlueOak-1.0.0",
+ "engines": {
+ "node": "20 || >=22"
}
},
"node_modules/lucide-preact": {
- "version": "0.575.0",
- "resolved": "https://registry.npmmirror.com/lucide-preact/-/lucide-preact-0.575.0.tgz",
- "integrity": "sha512-W8JZyQEkYv6DlbRrEgmZxVWFKL3zjoyEkFOOSxiX2VEU6Gou8cOqXZ5IAGmqAL4KiPx1tWgGT9awNjAH7MFknw==",
+ "version": "1.22.0",
+ "resolved": "https://registry.npmjs.org/lucide-preact/-/lucide-preact-1.22.0.tgz",
+ "integrity": "sha512-zFaBtoaWQgvapVEI96M3b5iUOlAEvpUfDuW3Gs8K1RHDyoOTrnXm+Cz5tupm8StKbRKn3W/YKIPolllf5voVDw==",
"license": "ISC",
"peerDependencies": {
"preact": "^10.27.2"
@@ -3272,7 +3812,7 @@
},
"node_modules/magic-string": {
"version": "0.30.21",
- "resolved": "https://registry.npmmirror.com/magic-string/-/magic-string-0.30.21.tgz",
+ "resolved": "https://registry.npmjs.org/magic-string/-/magic-string-0.30.21.tgz",
"integrity": "sha512-vd2F4YUyEXKGcLHoq+TEyCjxueSeHnFxyyjNp80yg0XV4vUhnDer/lvvlqM/arB5bXQN5K2/3oinyCRyx8T2CQ==",
"dev": true,
"license": "MIT",
@@ -3282,7 +3822,7 @@
},
"node_modules/merge2": {
"version": "1.4.1",
- "resolved": "https://registry.npmmirror.com/merge2/-/merge2-1.4.1.tgz",
+ "resolved": "https://registry.npmjs.org/merge2/-/merge2-1.4.1.tgz",
"integrity": "sha512-8q7VEgMJW4J8tcfVPy8g09NcQwZdbwFEqhe/WZkoIzjn/3TGDwtOCYtXGxA3O8tPzpczCCDgv+P2P5y00ZJOOg==",
"dev": true,
"license": "MIT",
@@ -3292,7 +3832,7 @@
},
"node_modules/micromatch": {
"version": "4.0.8",
- "resolved": "https://registry.npmmirror.com/micromatch/-/micromatch-4.0.8.tgz",
+ "resolved": "https://registry.npmjs.org/micromatch/-/micromatch-4.0.8.tgz",
"integrity": "sha512-PXwfBhYu0hBCPw8Dn0E+WDYb7af3dSLVWKi3HGv84IdF4TyFoC0ysxFd0Goxw7nSv4T/PzEJQxsYsEiFCKo2BA==",
"dev": true,
"license": "MIT",
@@ -3306,7 +3846,7 @@
},
"node_modules/micromatch/node_modules/picomatch": {
"version": "2.3.2",
- "resolved": "https://registry.npmmirror.com/picomatch/-/picomatch-2.3.2.tgz",
+ "resolved": "https://registry.npmjs.org/picomatch/-/picomatch-2.3.2.tgz",
"integrity": "sha512-V7+vQEJ06Z+c5tSye8S+nHUfI51xoXIXjHQ99cQtKUkQqqO1kO/KCJUfZXuB47h/YBlDhah2H3hdUGXn8ie0oA==",
"dev": true,
"license": "MIT",
@@ -3318,17 +3858,17 @@
}
},
"node_modules/miniflare": {
- "version": "4.20260603.0",
- "resolved": "https://registry.npmjs.org/miniflare/-/miniflare-4.20260603.0.tgz",
- "integrity": "sha512-+kMQYB82gC8MPOuojHur3icQsUeZUEJ+Sphuo5rVC3Ri9txBLAW/mH33b9OVrpmkogQeaaqPS4tPtugJZhk5Kw==",
+ "version": "4.20260625.0",
+ "resolved": "https://registry.npmjs.org/miniflare/-/miniflare-4.20260625.0.tgz",
+ "integrity": "sha512-3kKXwRUObJsnBYPBgR0NiNZYKF/yv8GFyha1cx2EeAEraxNODgRVcyeRo+F1ok1tg5Mg7iUpOWSkknQTHuFhwA==",
"dev": true,
"license": "MIT",
"dependencies": {
"@cspotcode/source-map-support": "0.8.1",
"sharp": "0.34.5",
- "undici": "7.24.8",
- "workerd": "1.20260603.1",
- "ws": "8.20.1",
+ "undici": "7.28.0",
+ "workerd": "1.20260625.1",
+ "ws": "8.21.0",
"youch": "4.1.0-beta.10"
},
"bin": {
@@ -3340,20 +3880,20 @@
},
"node_modules/mitt": {
"version": "3.0.1",
- "resolved": "https://registry.npmmirror.com/mitt/-/mitt-3.0.1.tgz",
+ "resolved": "https://registry.npmjs.org/mitt/-/mitt-3.0.1.tgz",
"integrity": "sha512-vKivATfr97l2/QBCYAkXYDbrIWPM2IIKEl7YPhjCvKlG3kE2gm+uBo6nEXK3M5/Ffh/FLpKExzOQ3JJoJGFKBw==",
"license": "MIT"
},
"node_modules/ms": {
"version": "2.1.3",
- "resolved": "https://registry.npmmirror.com/ms/-/ms-2.1.3.tgz",
+ "resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
"integrity": "sha512-6FlzubTLZG3J2a/NVCAleEhjzq5oxgHyaCU9yYXvcLsvoVaHJq/s5xXI6/XXP6tz7R9xAOtHnSO/tXtF3WRTlA==",
"dev": true,
"license": "MIT"
},
"node_modules/mz": {
"version": "2.7.0",
- "resolved": "https://registry.npmmirror.com/mz/-/mz-2.7.0.tgz",
+ "resolved": "https://registry.npmjs.org/mz/-/mz-2.7.0.tgz",
"integrity": "sha512-z81GNO7nnYMEhrGh9LeymoE4+Yr0Wn5McHIZMK5cfQCl+NDX08sCZgUc9/6MHni9IWuFLm1Z3HTCXu2z9fN62Q==",
"dev": true,
"license": "MIT",
@@ -3364,9 +3904,9 @@
}
},
"node_modules/nanoid": {
- "version": "3.3.12",
- "resolved": "https://registry.npmjs.org/nanoid/-/nanoid-3.3.12.tgz",
- "integrity": "sha512-ZB9RH/39qpq5Vu6Y+NmUaFhQR6pp+M2Xt76XBnEwDaGcVAqhlvxrl3B2bKS5D3NH3QR76v3aSrKaF/Kiy7lEtQ==",
+ "version": "3.3.17",
+ "resolved": "https://registry.npmjs.org/nanoid/-/nanoid-3.3.17.tgz",
+ "integrity": "sha512-xQLf0A3HOMlgHq0n247/LRuAOYmB7dXJ/DvAxGvsSBij45XtBSmQycu+F8ODbHwns/XyFZagyL1+J0Offw1E0g==",
"dev": true,
"funding": [
{
@@ -3384,7 +3924,7 @@
},
"node_modules/node-html-parser": {
"version": "6.1.13",
- "resolved": "https://registry.npmmirror.com/node-html-parser/-/node-html-parser-6.1.13.tgz",
+ "resolved": "https://registry.npmjs.org/node-html-parser/-/node-html-parser-6.1.13.tgz",
"integrity": "sha512-qIsTMOY4C/dAa5Q5vsobRpOOvPfC4pB61UVW2uSwZNUp0QU/jCekTal1vMmbO0DgdHeLUJpv/ARmDqErVxA3Sg==",
"dev": true,
"license": "MIT",
@@ -3394,26 +3934,19 @@
}
},
"node_modules/node-releases": {
- "version": "2.0.27",
- "resolved": "https://registry.npmmirror.com/node-releases/-/node-releases-2.0.27.tgz",
- "integrity": "sha512-nmh3lCkYZ3grZvqcCH+fjmQ7X+H0OeZgP40OierEaAptX4XofMh5kwNbWh7lBduUzCcV/8kZ+NDLCwm2iorIlA==",
- "dev": true,
- "license": "MIT"
- },
- "node_modules/normalize-path": {
- "version": "3.0.0",
- "resolved": "https://registry.npmmirror.com/normalize-path/-/normalize-path-3.0.0.tgz",
- "integrity": "sha512-6eZs5Ls3WtCisHWp9S2GUy8dqkpGi4BVSz3GaqiE6ezub0512ESztXUwUB6C6IKbQkY2Pnb/mD4WYojCRwcwLA==",
+ "version": "2.0.50",
+ "resolved": "https://registry.npmjs.org/node-releases/-/node-releases-2.0.50.tgz",
+ "integrity": "sha512-J6l92tKHX6w8Jy5nO1Vuc01NoIiRGi/d6qBKVxh+IQ8Cr3b6HbVNfKiF8ZpFKufTwpwxMmce2W3iQZ861ZRyTg==",
"dev": true,
"license": "MIT",
"engines": {
- "node": ">=0.10.0"
+ "node": ">=18"
}
},
- "node_modules/normalize-range": {
- "version": "0.1.2",
- "resolved": "https://registry.npmmirror.com/normalize-range/-/normalize-range-0.1.2.tgz",
- "integrity": "sha512-bdok/XvKII3nUpklnV6P2hxtMNrCboOjAcyBuQnWEhO665FwrSNRxU+AqpsyvO6LgGYPspN+lu5CLtw4jPRKNA==",
+ "node_modules/normalize-path": {
+ "version": "3.0.0",
+ "resolved": "https://registry.npmjs.org/normalize-path/-/normalize-path-3.0.0.tgz",
+ "integrity": "sha512-6eZs5Ls3WtCisHWp9S2GUy8dqkpGi4BVSz3GaqiE6ezub0512ESztXUwUB6C6IKbQkY2Pnb/mD4WYojCRwcwLA==",
"dev": true,
"license": "MIT",
"engines": {
@@ -3422,7 +3955,7 @@
},
"node_modules/nth-check": {
"version": "2.1.1",
- "resolved": "https://registry.npmmirror.com/nth-check/-/nth-check-2.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/nth-check/-/nth-check-2.1.1.tgz",
"integrity": "sha512-lqjrjmaOoAnWfMmBPL+XNnynZh2+swxiX3WUE0s4yEHI6m+AwrK2UZOimIRl3X/4QctVqS8AiZjFqyOGrMXb/w==",
"dev": true,
"license": "BSD-2-Clause",
@@ -3435,7 +3968,7 @@
},
"node_modules/object-assign": {
"version": "4.1.1",
- "resolved": "https://registry.npmmirror.com/object-assign/-/object-assign-4.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/object-assign/-/object-assign-4.1.1.tgz",
"integrity": "sha512-rJgTQnkUnH1sFw8yT6VSU3zD3sWmu6sZhIseY8VX+GRu3P6F7Fu+JNDoXfklElbLJSnc3FUQHVe4cU5hj+BcUg==",
"dev": true,
"license": "MIT",
@@ -3445,7 +3978,7 @@
},
"node_modules/object-hash": {
"version": "3.0.0",
- "resolved": "https://registry.npmmirror.com/object-hash/-/object-hash-3.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/object-hash/-/object-hash-3.0.0.tgz",
"integrity": "sha512-RSn9F68PjH9HqtltsSnqYC1XXoWe9Bju5+213R98cNGttag9q9yAOTzdbsqvIa7aNm5WffBZFpWYr2aWrklWAw==",
"dev": true,
"license": "MIT",
@@ -3453,23 +3986,37 @@
"node": ">= 6"
}
},
- "node_modules/opencc-js": {
- "version": "1.0.5",
- "resolved": "https://registry.npmmirror.com/opencc-js/-/opencc-js-1.0.5.tgz",
- "integrity": "sha512-LD+1SoNnZdlRwtYTjnQdFrSVCAaYpuDqL5CkmOaHOkKoKh7mFxUicLTRVNLU5C+Jmi1vXQ3QL4jWdgSaa4sKjg==",
+ "node_modules/obug": {
+ "version": "2.1.3",
+ "resolved": "https://registry.npmmirror.com/obug/-/obug-2.1.3.tgz",
+ "integrity": "sha512-9miFgM2OFba7hB+pRgvtV84pYTBaoTHohvmIgiRt6dRIzbwEOIaNaP+dIlGs2fNFoB0SeISs0Jz5WFVRid6Xyg==",
"dev": true,
- "license": "MIT"
+ "funding": [
+ "https://github.com/sponsors/sxzz",
+ "https://opencollective.com/debug"
+ ],
+ "license": "MIT",
+ "engines": {
+ "node": ">=12.20.0"
+ }
+ },
+ "node_modules/opencc-js": {
+ "version": "1.3.2",
+ "resolved": "https://registry.npmjs.org/opencc-js/-/opencc-js-1.3.2.tgz",
+ "integrity": "sha512-lO4Kq8J4TcPTa8qHcx5qazQCn+NM68kNwLJOQ58DG9MV8v25XJxByMB74zDGmr3LjJMGqDdrvQfoCi3FO0SC2A==",
+ "dev": true,
+ "license": "MIT AND Apache-2.0"
},
"node_modules/path-parse": {
"version": "1.0.7",
- "resolved": "https://registry.npmmirror.com/path-parse/-/path-parse-1.0.7.tgz",
+ "resolved": "https://registry.npmjs.org/path-parse/-/path-parse-1.0.7.tgz",
"integrity": "sha512-LDJzPVEEEPR+y48z93A0Ed0yXb8pAByGWo/k5YYdYgpY2/2EsOsksJrq7lOHxryrVOn1ejG6oAp8ahvOIQD8sw==",
"dev": true,
"license": "MIT"
},
"node_modules/path-to-regexp": {
"version": "6.3.0",
- "resolved": "https://registry.npmmirror.com/path-to-regexp/-/path-to-regexp-6.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/path-to-regexp/-/path-to-regexp-6.3.0.tgz",
"integrity": "sha512-Yhpw4T9C6hPpgPeA28us07OJeqZ5EzQTkbfwuhsUg0c237RomFoETJgmp2sa3F/41gfLE6G5cqcYwznmeEeOlQ==",
"dev": true,
"license": "MIT"
@@ -3483,7 +4030,7 @@
},
"node_modules/picocolors": {
"version": "1.1.1",
- "resolved": "https://registry.npmmirror.com/picocolors/-/picocolors-1.1.1.tgz",
+ "resolved": "https://registry.npmjs.org/picocolors/-/picocolors-1.1.1.tgz",
"integrity": "sha512-xceH2snhtb5M9liqDsmEw56le376mTZkEX/jEb/RxNFyegNul7eNslCXP9FDj/Lcu0X8KEyMceP2ntpaHrDEVA==",
"dev": true,
"license": "ISC"
@@ -3503,7 +4050,7 @@
},
"node_modules/pify": {
"version": "2.3.0",
- "resolved": "https://registry.npmmirror.com/pify/-/pify-2.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/pify/-/pify-2.3.0.tgz",
"integrity": "sha512-udgsAY+fTnvv7kI7aaxbqwWNb0AHiB0qBO89PZKPkoTmGOgdbrHDKD+0B2X4uTfJ/FT1R09r9gTsjUjNJotuog==",
"dev": true,
"license": "MIT",
@@ -3513,7 +4060,7 @@
},
"node_modules/pirates": {
"version": "4.0.7",
- "resolved": "https://registry.npmmirror.com/pirates/-/pirates-4.0.7.tgz",
+ "resolved": "https://registry.npmjs.org/pirates/-/pirates-4.0.7.tgz",
"integrity": "sha512-TfySrs/5nm8fQJDcBDuUng3VOUKsd7S+zqvbOTiGXHfxX4wK31ard+hoNuvkicM/2YFzlpDgABOevKSsB4G/FA==",
"dev": true,
"license": "MIT",
@@ -3522,9 +4069,9 @@
}
},
"node_modules/postcss": {
- "version": "8.5.15",
- "resolved": "https://registry.npmjs.org/postcss/-/postcss-8.5.15.tgz",
- "integrity": "sha512-FfR8sjd4em2T6fb3I2MwAJU7HWVMr9zba+enmQeeWFfCbm+UOC/0X4DS8XtpUTMwWMGbjKYP7xjfNekzyGmB3A==",
+ "version": "8.5.23",
+ "resolved": "https://registry.npmjs.org/postcss/-/postcss-8.5.23.tgz",
+ "integrity": "sha512-g50586zr4bZmwFiTlflMu8E0bDTb5I5gertgwAKmsdUlTQIhZtunzUlD1WSzwcVWPoAVpsrA6vlfCD7oXvRwgg==",
"dev": true,
"funding": [
{
@@ -3542,7 +4089,7 @@
],
"license": "MIT",
"dependencies": {
- "nanoid": "^3.3.12",
+ "nanoid": "^3.3.16",
"picocolors": "^1.1.1",
"source-map-js": "^1.2.1"
},
@@ -3552,7 +4099,7 @@
},
"node_modules/postcss-import": {
"version": "15.1.0",
- "resolved": "https://registry.npmmirror.com/postcss-import/-/postcss-import-15.1.0.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-import/-/postcss-import-15.1.0.tgz",
"integrity": "sha512-hpr+J05B2FVYUAXHeK1YyI267J/dDDhMU6B6civm8hSY1jYJnBXxzKDKDswzJmtLHryrjhnDjqqp/49t8FALew==",
"dev": true,
"license": "MIT",
@@ -3570,7 +4117,7 @@
},
"node_modules/postcss-js": {
"version": "4.1.0",
- "resolved": "https://registry.npmmirror.com/postcss-js/-/postcss-js-4.1.0.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-js/-/postcss-js-4.1.0.tgz",
"integrity": "sha512-oIAOTqgIo7q2EOwbhb8UalYePMvYoIeRY2YKntdpFQXNosSu3vLrniGgmH9OKs/qAkfoj5oB3le/7mINW1LCfw==",
"dev": true,
"funding": [
@@ -3596,7 +4143,7 @@
},
"node_modules/postcss-load-config": {
"version": "4.0.2",
- "resolved": "https://registry.npmmirror.com/postcss-load-config/-/postcss-load-config-4.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-load-config/-/postcss-load-config-4.0.2.tgz",
"integrity": "sha512-bSVhyJGL00wMVoPUzAVAnbEoWyqRxkjv64tUl427SKnPrENtq6hJwUojroMz2VB+Q1edmi4IfrAPpami5VVgMQ==",
"dev": true,
"funding": [
@@ -3632,7 +4179,7 @@
},
"node_modules/postcss-nested": {
"version": "6.2.0",
- "resolved": "https://registry.npmmirror.com/postcss-nested/-/postcss-nested-6.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-nested/-/postcss-nested-6.2.0.tgz",
"integrity": "sha512-HQbt28KulC5AJzG+cZtj9kvKB93CFCdLvog1WFLf1D+xmMvPGlBstkpTEZfK5+AN9hfJocyBFCNiqyS48bpgzQ==",
"dev": true,
"funding": [
@@ -3658,7 +4205,7 @@
},
"node_modules/postcss-selector-parser": {
"version": "6.1.2",
- "resolved": "https://registry.npmmirror.com/postcss-selector-parser/-/postcss-selector-parser-6.1.2.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-selector-parser/-/postcss-selector-parser-6.1.2.tgz",
"integrity": "sha512-Q8qQfPiZ+THO/3ZrOrO0cJJKfpYCagtMUkXbnEfmgUjwXg6z/WBeOyS9APBBPCTSiDV+s4SwQGu8yFsiMRIudg==",
"dev": true,
"license": "MIT",
@@ -3672,15 +4219,15 @@
},
"node_modules/postcss-value-parser": {
"version": "4.2.0",
- "resolved": "https://registry.npmmirror.com/postcss-value-parser/-/postcss-value-parser-4.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/postcss-value-parser/-/postcss-value-parser-4.2.0.tgz",
"integrity": "sha512-1NNCs6uurfkVbeXG4S8JFT9t19m45ICnif8zWLd5oPSZ50QnwMfK+H3jv408d4jw/7Bttv5axS5IiHoLaVNHeQ==",
"dev": true,
"license": "MIT"
},
"node_modules/preact": {
- "version": "10.28.4",
- "resolved": "https://registry.npmmirror.com/preact/-/preact-10.28.4.tgz",
- "integrity": "sha512-uKFfOHWuSNpRFVTnljsCluEFq57OKT+0QdOiQo8XWnQ/pSvg7OpX5eNOejELXJMWy+BwM2nobz0FkvzmnpCNsQ==",
+ "version": "10.29.3",
+ "resolved": "https://registry.npmjs.org/preact/-/preact-10.29.3.tgz",
+ "integrity": "sha512-D9NL1GAnJZhc3RndVs4gDdxEeU9TcHgywMrhhOsnpdlvFjdbx0gAsLUnH6JEhlJH5giL7Tx5biWPUSEXE/HPzw==",
"license": "MIT",
"funding": {
"type": "opencollective",
@@ -3689,7 +4236,7 @@
},
"node_modules/pvtsutils": {
"version": "1.3.6",
- "resolved": "https://registry.npmmirror.com/pvtsutils/-/pvtsutils-1.3.6.tgz",
+ "resolved": "https://registry.npmjs.org/pvtsutils/-/pvtsutils-1.3.6.tgz",
"integrity": "sha512-PLgQXQ6H2FWCaeRak8vvk1GW462lMxB5s3Jm673N82zI4vqtVUPuZdffdZbPDFRoU8kAhItWFtPCWiPpp4/EDg==",
"license": "MIT",
"dependencies": {
@@ -3698,7 +4245,7 @@
},
"node_modules/pvutils": {
"version": "1.1.5",
- "resolved": "https://registry.npmmirror.com/pvutils/-/pvutils-1.1.5.tgz",
+ "resolved": "https://registry.npmjs.org/pvutils/-/pvutils-1.1.5.tgz",
"integrity": "sha512-KTqnxsgGiQ6ZAzZCVlJH5eOjSnvlyEgx1m8bkRJfOhmGRqfo5KLvmAlACQkrjEtOQ4B7wF9TdSLIs9O90MX9xA==",
"license": "MIT",
"engines": {
@@ -3707,13 +4254,13 @@
},
"node_modules/qrcode-generator": {
"version": "2.0.4",
- "resolved": "https://registry.npmmirror.com/qrcode-generator/-/qrcode-generator-2.0.4.tgz",
+ "resolved": "https://registry.npmjs.org/qrcode-generator/-/qrcode-generator-2.0.4.tgz",
"integrity": "sha512-mZSiP6RnbHl4xL2Ap5HfkjLnmxfKcPWpWe/c+5XxCuetEenqmNFf1FH/ftXPCtFG5/TDobjsjz6sSNL0Sr8Z9g==",
"license": "MIT"
},
"node_modules/queue-microtask": {
"version": "1.2.3",
- "resolved": "https://registry.npmmirror.com/queue-microtask/-/queue-microtask-1.2.3.tgz",
+ "resolved": "https://registry.npmjs.org/queue-microtask/-/queue-microtask-1.2.3.tgz",
"integrity": "sha512-NuaNSa6flKT5JaSYQzJok04JzTL1CA6aGhv5rfLW3PgqA+M2ChpZQnAC8h8i4ZFkBS8X5RqkDBHA7r4hej3K9A==",
"dev": true,
"funding": [
@@ -3734,7 +4281,7 @@
},
"node_modules/react": {
"version": "19.2.4",
- "resolved": "https://registry.npmmirror.com/react/-/react-19.2.4.tgz",
+ "resolved": "https://registry.npmjs.org/react/-/react-19.2.4.tgz",
"integrity": "sha512-9nfp2hYpCwOjAN+8TZFGhtWEwgvWHXqESH8qT89AT/lWklpLON22Lc8pEtnpsZz7VmawabSU0gCjnj8aC0euHQ==",
"license": "MIT",
"peer": true,
@@ -3744,7 +4291,7 @@
},
"node_modules/read-cache": {
"version": "1.0.0",
- "resolved": "https://registry.npmmirror.com/read-cache/-/read-cache-1.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/read-cache/-/read-cache-1.0.0.tgz",
"integrity": "sha512-Owdv/Ft7IjOgm/i0xvNDZ1LrRANRfew4b2prF3OWMQLxLfu3bS8FVhCsrSCMK4lR56Y9ya+AThoTpDCTxCmpRA==",
"dev": true,
"license": "MIT",
@@ -3754,7 +4301,7 @@
},
"node_modules/readdirp": {
"version": "3.6.0",
- "resolved": "https://registry.npmmirror.com/readdirp/-/readdirp-3.6.0.tgz",
+ "resolved": "https://registry.npmjs.org/readdirp/-/readdirp-3.6.0.tgz",
"integrity": "sha512-hOS089on8RduqdbhvQ5Z37A0ESjsqz6qnRcffsMU3495FuTdqSm+7bhJ29JvIOsBDEEnan5DPu9t3To9VRlMzA==",
"dev": true,
"license": "MIT",
@@ -3767,7 +4314,7 @@
},
"node_modules/readdirp/node_modules/picomatch": {
"version": "2.3.2",
- "resolved": "https://registry.npmmirror.com/picomatch/-/picomatch-2.3.2.tgz",
+ "resolved": "https://registry.npmjs.org/picomatch/-/picomatch-2.3.2.tgz",
"integrity": "sha512-V7+vQEJ06Z+c5tSye8S+nHUfI51xoXIXjHQ99cQtKUkQqqO1kO/KCJUfZXuB47h/YBlDhah2H3hdUGXn8ie0oA==",
"dev": true,
"license": "MIT",
@@ -3780,13 +4327,13 @@
},
"node_modules/reflect-metadata": {
"version": "0.2.2",
- "resolved": "https://registry.npmmirror.com/reflect-metadata/-/reflect-metadata-0.2.2.tgz",
+ "resolved": "https://registry.npmjs.org/reflect-metadata/-/reflect-metadata-0.2.2.tgz",
"integrity": "sha512-urBwgfrvVP/eAyXx4hluJivBKzuEbSQs9rKWCrCkbSxNv8mxPcUZKeuoF3Uy4mJl3Lwprp6yy5/39VWigZ4K6Q==",
"license": "Apache-2.0"
},
"node_modules/regexparam": {
"version": "3.0.0",
- "resolved": "https://registry.npmmirror.com/regexparam/-/regexparam-3.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/regexparam/-/regexparam-3.0.0.tgz",
"integrity": "sha512-RSYAtP31mvYLkAHrOlh25pCNQ5hWnT106VukGaaFfuJrZFkGRX5GhUAdPqpSDXxOhA2c4akmRuplv1mRqnBn6Q==",
"license": "MIT",
"engines": {
@@ -3795,7 +4342,7 @@
},
"node_modules/resolve": {
"version": "1.22.12",
- "resolved": "https://registry.npmmirror.com/resolve/-/resolve-1.22.12.tgz",
+ "resolved": "https://registry.npmjs.org/resolve/-/resolve-1.22.12.tgz",
"integrity": "sha512-TyeJ1zif53BPfHootBGwPRYT1RUt6oGWsaQr8UyZW/eAm9bKoijtvruSDEmZHm92CwS9nj7/fWttqPCgzep8CA==",
"dev": true,
"license": "MIT",
@@ -3815,19 +4362,9 @@
"url": "https://github.com/sponsors/ljharb"
}
},
- "node_modules/resolve-pkg-maps": {
- "version": "1.0.0",
- "resolved": "https://registry.npmmirror.com/resolve-pkg-maps/-/resolve-pkg-maps-1.0.0.tgz",
- "integrity": "sha512-seS2Tj26TBVOC2NIc2rOe2y2ZO7efxITtLZcGSOnHHNOQ7CkiUBfw0Iw2ck6xkIhPwLhKNLS8BO+hEpngQlqzw==",
- "dev": true,
- "license": "MIT",
- "funding": {
- "url": "https://github.com/privatenumber/resolve-pkg-maps?sponsor=1"
- }
- },
"node_modules/reusify": {
"version": "1.1.0",
- "resolved": "https://registry.npmmirror.com/reusify/-/reusify-1.1.0.tgz",
+ "resolved": "https://registry.npmjs.org/reusify/-/reusify-1.1.0.tgz",
"integrity": "sha512-g6QUff04oZpHs0eG5p83rFLhHeV00ug/Yf9nZM6fLeUrPguBTkTQOdpAWWspMh55TZfVQDPaN3NQJfbVRAxdIw==",
"dev": true,
"license": "MIT",
@@ -3836,54 +4373,43 @@
"node": ">=0.10.0"
}
},
- "node_modules/rollup": {
- "version": "4.59.0",
- "resolved": "https://registry.npmmirror.com/rollup/-/rollup-4.59.0.tgz",
- "integrity": "sha512-2oMpl67a3zCH9H79LeMcbDhXW/UmWG/y2zuqnF2jQq5uq9TbM9TVyXvA4+t+ne2IIkBdrLpAaRQAvo7YI/Yyeg==",
+ "node_modules/rolldown": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/rolldown/-/rolldown-1.1.4.tgz",
+ "integrity": "sha512-IjZYiLxZwpnhwhdBH2ugdTGVSdhCQUmLxLoqyjiL0JxYjyRst+5a0P3xfrTxJ5F638j4Mvvw5FAX5XE6eHpXbA==",
"dev": true,
"license": "MIT",
"dependencies": {
- "@types/estree": "1.0.8"
+ "@oxc-project/types": "=0.138.0",
+ "@rolldown/pluginutils": "^1.0.0"
},
"bin": {
- "rollup": "dist/bin/rollup"
+ "rolldown": "bin/cli.mjs"
},
"engines": {
- "node": ">=18.0.0",
- "npm": ">=8.0.0"
+ "node": "^20.19.0 || >=22.12.0"
},
"optionalDependencies": {
- "@rollup/rollup-android-arm-eabi": "4.59.0",
- "@rollup/rollup-android-arm64": "4.59.0",
- "@rollup/rollup-darwin-arm64": "4.59.0",
- "@rollup/rollup-darwin-x64": "4.59.0",
- "@rollup/rollup-freebsd-arm64": "4.59.0",
- "@rollup/rollup-freebsd-x64": "4.59.0",
- "@rollup/rollup-linux-arm-gnueabihf": "4.59.0",
- "@rollup/rollup-linux-arm-musleabihf": "4.59.0",
- "@rollup/rollup-linux-arm64-gnu": "4.59.0",
- "@rollup/rollup-linux-arm64-musl": "4.59.0",
- "@rollup/rollup-linux-loong64-gnu": "4.59.0",
- "@rollup/rollup-linux-loong64-musl": "4.59.0",
- "@rollup/rollup-linux-ppc64-gnu": "4.59.0",
- "@rollup/rollup-linux-ppc64-musl": "4.59.0",
- "@rollup/rollup-linux-riscv64-gnu": "4.59.0",
- "@rollup/rollup-linux-riscv64-musl": "4.59.0",
- "@rollup/rollup-linux-s390x-gnu": "4.59.0",
- "@rollup/rollup-linux-x64-gnu": "4.59.0",
- "@rollup/rollup-linux-x64-musl": "4.59.0",
- "@rollup/rollup-openbsd-x64": "4.59.0",
- "@rollup/rollup-openharmony-arm64": "4.59.0",
- "@rollup/rollup-win32-arm64-msvc": "4.59.0",
- "@rollup/rollup-win32-ia32-msvc": "4.59.0",
- "@rollup/rollup-win32-x64-gnu": "4.59.0",
- "@rollup/rollup-win32-x64-msvc": "4.59.0",
- "fsevents": "~2.3.2"
+ "@rolldown/binding-android-arm64": "1.1.4",
+ "@rolldown/binding-darwin-arm64": "1.1.4",
+ "@rolldown/binding-darwin-x64": "1.1.4",
+ "@rolldown/binding-freebsd-x64": "1.1.4",
+ "@rolldown/binding-linux-arm-gnueabihf": "1.1.4",
+ "@rolldown/binding-linux-arm64-gnu": "1.1.4",
+ "@rolldown/binding-linux-arm64-musl": "1.1.4",
+ "@rolldown/binding-linux-ppc64-gnu": "1.1.4",
+ "@rolldown/binding-linux-s390x-gnu": "1.1.4",
+ "@rolldown/binding-linux-x64-gnu": "1.1.4",
+ "@rolldown/binding-linux-x64-musl": "1.1.4",
+ "@rolldown/binding-openharmony-arm64": "1.1.4",
+ "@rolldown/binding-wasm32-wasi": "1.1.4",
+ "@rolldown/binding-win32-arm64-msvc": "1.1.4",
+ "@rolldown/binding-win32-x64-msvc": "1.1.4"
}
},
"node_modules/run-parallel": {
"version": "1.2.0",
- "resolved": "https://registry.npmmirror.com/run-parallel/-/run-parallel-1.2.0.tgz",
+ "resolved": "https://registry.npmjs.org/run-parallel/-/run-parallel-1.2.0.tgz",
"integrity": "sha512-5l4VyZR86LZ/lDxZTR6jqL8AFE2S0IFLMP26AbjsLVADxHdhB/c0GUsH+y39UfCi3dzz8OlQuPmnaJOMoDHQBA==",
"dev": true,
"funding": [
@@ -3906,9 +4432,9 @@
}
},
"node_modules/semver": {
- "version": "7.8.3",
- "resolved": "https://registry.npmjs.org/semver/-/semver-7.8.3.tgz",
- "integrity": "sha512-wnilbGyMxzbY7dNOl7jpKbLSjcfeweJWU5j4+u5qW+6/wuGD9KzIGOyZnQVSBM9E7DtWaaH3CyHkppYrKYoxwg==",
+ "version": "7.8.5",
+ "resolved": "https://registry.npmjs.org/semver/-/semver-7.8.5.tgz",
+ "integrity": "sha512-Y7/KDsb8LjooZpwaqGyulO6DQlksgCncchHGk+sZIY4SBvUocMBEFH5Ur1fI4dV+Jvl0w6cjvucaIi40puRioA==",
"dev": true,
"license": "ISC",
"bin": {
@@ -3919,53 +4445,53 @@
}
},
"node_modules/sharp": {
- "version": "0.34.5",
- "resolved": "https://registry.npmjs.org/sharp/-/sharp-0.34.5.tgz",
- "integrity": "sha512-Ou9I5Ft9WNcCbXrU9cMgPBcCK8LiwLqcbywW3t4oDV37n1pzpuNLsYiAV8eODnjbtQlSDwZ2cUEeQz4E54Hltg==",
+ "version": "0.35.0",
+ "resolved": "https://registry.npmjs.org/sharp/-/sharp-0.35.0.tgz",
+ "integrity": "sha512-BqvG5XbwPZ4NV0DK90d86leEECMsoa8bO0nqnKWlBDYxri4GJ7c4EDInaF6q20lTh/mATmnDIKWJFfXnoVfH5g==",
"dev": true,
- "hasInstallScript": true,
"license": "Apache-2.0",
"dependencies": {
- "@img/colour": "^1.0.0",
+ "@img/colour": "^1.1.0",
"detect-libc": "^2.1.2",
- "semver": "^7.7.3"
+ "semver": "^7.8.4"
},
"engines": {
- "node": "^18.17.0 || ^20.3.0 || >=21.0.0"
+ "node": ">=20.9.0"
},
"funding": {
"url": "https://opencollective.com/libvips"
},
"optionalDependencies": {
- "@img/sharp-darwin-arm64": "0.34.5",
- "@img/sharp-darwin-x64": "0.34.5",
- "@img/sharp-libvips-darwin-arm64": "1.2.4",
- "@img/sharp-libvips-darwin-x64": "1.2.4",
- "@img/sharp-libvips-linux-arm": "1.2.4",
- "@img/sharp-libvips-linux-arm64": "1.2.4",
- "@img/sharp-libvips-linux-ppc64": "1.2.4",
- "@img/sharp-libvips-linux-riscv64": "1.2.4",
- "@img/sharp-libvips-linux-s390x": "1.2.4",
- "@img/sharp-libvips-linux-x64": "1.2.4",
- "@img/sharp-libvips-linuxmusl-arm64": "1.2.4",
- "@img/sharp-libvips-linuxmusl-x64": "1.2.4",
- "@img/sharp-linux-arm": "0.34.5",
- "@img/sharp-linux-arm64": "0.34.5",
- "@img/sharp-linux-ppc64": "0.34.5",
- "@img/sharp-linux-riscv64": "0.34.5",
- "@img/sharp-linux-s390x": "0.34.5",
- "@img/sharp-linux-x64": "0.34.5",
- "@img/sharp-linuxmusl-arm64": "0.34.5",
- "@img/sharp-linuxmusl-x64": "0.34.5",
- "@img/sharp-wasm32": "0.34.5",
- "@img/sharp-win32-arm64": "0.34.5",
- "@img/sharp-win32-ia32": "0.34.5",
- "@img/sharp-win32-x64": "0.34.5"
+ "@img/sharp-darwin-arm64": "0.35.0",
+ "@img/sharp-darwin-x64": "0.35.0",
+ "@img/sharp-freebsd-wasm32": "0.35.0",
+ "@img/sharp-libvips-darwin-arm64": "1.3.0",
+ "@img/sharp-libvips-darwin-x64": "1.3.0",
+ "@img/sharp-libvips-linux-arm": "1.3.0",
+ "@img/sharp-libvips-linux-arm64": "1.3.0",
+ "@img/sharp-libvips-linux-ppc64": "1.3.0",
+ "@img/sharp-libvips-linux-riscv64": "1.3.0",
+ "@img/sharp-libvips-linux-s390x": "1.3.0",
+ "@img/sharp-libvips-linux-x64": "1.3.0",
+ "@img/sharp-libvips-linuxmusl-arm64": "1.3.0",
+ "@img/sharp-libvips-linuxmusl-x64": "1.3.0",
+ "@img/sharp-linux-arm": "0.35.0",
+ "@img/sharp-linux-arm64": "0.35.0",
+ "@img/sharp-linux-ppc64": "0.35.0",
+ "@img/sharp-linux-riscv64": "0.35.0",
+ "@img/sharp-linux-s390x": "0.35.0",
+ "@img/sharp-linux-x64": "0.35.0",
+ "@img/sharp-linuxmusl-arm64": "0.35.0",
+ "@img/sharp-linuxmusl-x64": "0.35.0",
+ "@img/sharp-webcontainers-wasm32": "0.35.0",
+ "@img/sharp-win32-arm64": "0.35.0",
+ "@img/sharp-win32-ia32": "0.35.0",
+ "@img/sharp-win32-x64": "0.35.0"
}
},
"node_modules/simple-code-frame": {
"version": "1.3.0",
- "resolved": "https://registry.npmmirror.com/simple-code-frame/-/simple-code-frame-1.3.0.tgz",
+ "resolved": "https://registry.npmjs.org/simple-code-frame/-/simple-code-frame-1.3.0.tgz",
"integrity": "sha512-MB4pQmETUBlNs62BBeRjIFGeuy/x6gGKh7+eRUemn1rCFhqo7K+4slPqsyizCbcbYLnaYqaoZ2FWsZ/jN06D8w==",
"dev": true,
"license": "MIT",
@@ -3975,7 +4501,7 @@
},
"node_modules/source-map": {
"version": "0.7.6",
- "resolved": "https://registry.npmmirror.com/source-map/-/source-map-0.7.6.tgz",
+ "resolved": "https://registry.npmjs.org/source-map/-/source-map-0.7.6.tgz",
"integrity": "sha512-i5uvt8C3ikiWeNZSVZNWcfZPItFQOsYTUAOkcUPGd8DqDy1uOUikjt5dG+uRlwyvR108Fb9DOd4GvXfT0N2/uQ==",
"dev": true,
"license": "BSD-3-Clause",
@@ -3985,7 +4511,7 @@
},
"node_modules/source-map-js": {
"version": "1.2.1",
- "resolved": "https://registry.npmmirror.com/source-map-js/-/source-map-js-1.2.1.tgz",
+ "resolved": "https://registry.npmjs.org/source-map-js/-/source-map-js-1.2.1.tgz",
"integrity": "sha512-UXWMKhLOwVKb728IUtQPXxfYU+usdybtUrK/8uGE8CQMvrhOpwvzDBwj0QhSL7MQc7vIsISBG8VQ8+IDQxpfQA==",
"dev": true,
"license": "BSD-3-Clause",
@@ -3994,18 +4520,18 @@
}
},
"node_modules/stack-trace": {
- "version": "1.0.0-pre2",
- "resolved": "https://registry.npmmirror.com/stack-trace/-/stack-trace-1.0.0-pre2.tgz",
- "integrity": "sha512-2ztBJRek8IVofG9DBJqdy2N5kulaacX30Nz7xmkYF6ale9WBVmIy6mFBchvGX7Vx/MyjBhx+Rcxqrj+dbOnQ6A==",
+ "version": "1.0.0",
+ "resolved": "https://registry.npmjs.org/stack-trace/-/stack-trace-1.0.0.tgz",
+ "integrity": "sha512-H6D7134xi6qONvh7ZHKgviXf+rd3vhGBSvebPZCaUkd8zvQ+7PtDw6CljPTe4cXWNf2IKZGNqw6VJXSb9IgBpA==",
"dev": true,
"license": "MIT",
"engines": {
- "node": ">=16"
+ "node": ">=20.0.0"
}
},
"node_modules/sucrase": {
"version": "3.35.1",
- "resolved": "https://registry.npmmirror.com/sucrase/-/sucrase-3.35.1.tgz",
+ "resolved": "https://registry.npmjs.org/sucrase/-/sucrase-3.35.1.tgz",
"integrity": "sha512-DhuTmvZWux4H1UOnWMB3sk0sbaCVOoQZjv8u1rDoTV0HTdGem9hkAZtl4JZy8P2z4Bg0nT+YMeOFyVr4zcG5Tw==",
"dev": true,
"license": "MIT",
@@ -4041,7 +4567,7 @@
},
"node_modules/supports-preserve-symlinks-flag": {
"version": "1.0.0",
- "resolved": "https://registry.npmmirror.com/supports-preserve-symlinks-flag/-/supports-preserve-symlinks-flag-1.0.0.tgz",
+ "resolved": "https://registry.npmjs.org/supports-preserve-symlinks-flag/-/supports-preserve-symlinks-flag-1.0.0.tgz",
"integrity": "sha512-ot0WnXS9fgdkgIcePe6RHNk1WA8+muPa6cSjeR3V8K27q9BB1rTE3R1p7Hv0z1ZyAc8s6Vvv8DIyWf681MAt0w==",
"dev": true,
"license": "MIT",
@@ -4053,9 +4579,9 @@
}
},
"node_modules/tailwindcss": {
- "version": "3.4.17",
- "resolved": "https://registry.npmmirror.com/tailwindcss/-/tailwindcss-3.4.17.tgz",
- "integrity": "sha512-w33E2aCvSDP0tW9RZuNXadXlkHXqFzSkQew/aIa2i/Sj8fThxwovwlXHSPXTbAHwEIhBFXAedUhP2tueAKP8Og==",
+ "version": "3.4.19",
+ "resolved": "https://registry.npmjs.org/tailwindcss/-/tailwindcss-3.4.19.tgz",
+ "integrity": "sha512-3ofp+LL8E+pK/JuPLPggVAIaEuhvIz4qNcf3nA1Xn2o/7fb7s/TYpHhwGDv1ZU3PkBluUVaF8PyCHcm48cKLWQ==",
"dev": true,
"license": "MIT",
"dependencies": {
@@ -4067,7 +4593,7 @@
"fast-glob": "^3.3.2",
"glob-parent": "^6.0.2",
"is-glob": "^4.0.3",
- "jiti": "^1.21.6",
+ "jiti": "^1.21.7",
"lilconfig": "^3.1.3",
"micromatch": "^4.0.8",
"normalize-path": "^3.0.0",
@@ -4076,7 +4602,7 @@
"postcss": "^8.4.47",
"postcss-import": "^15.1.0",
"postcss-js": "^4.0.1",
- "postcss-load-config": "^4.0.2",
+ "postcss-load-config": "^4.0.2 || ^5.0 || ^6.0",
"postcss-nested": "^6.2.0",
"postcss-selector-parser": "^6.1.2",
"resolve": "^1.22.8",
@@ -4092,7 +4618,7 @@
},
"node_modules/thenify": {
"version": "3.3.1",
- "resolved": "https://registry.npmmirror.com/thenify/-/thenify-3.3.1.tgz",
+ "resolved": "https://registry.npmjs.org/thenify/-/thenify-3.3.1.tgz",
"integrity": "sha512-RVZSIV5IG10Hk3enotrhvz0T9em6cyHBLkH/YAZuKqd8hRkKhSfCGIcP2KUY0EPxndzANBmNllzWPwak+bheSw==",
"dev": true,
"license": "MIT",
@@ -4102,7 +4628,7 @@
},
"node_modules/thenify-all": {
"version": "1.6.0",
- "resolved": "https://registry.npmmirror.com/thenify-all/-/thenify-all-1.6.0.tgz",
+ "resolved": "https://registry.npmjs.org/thenify-all/-/thenify-all-1.6.0.tgz",
"integrity": "sha512-RNxQH/qI8/t3thXJDwcstUO4zeqo64+Uy/+sNVRBx4Xn2OX+OZ9oP+iJnNFqplFra2ZUVeKCSa2oVWi3T4uVmA==",
"dev": true,
"license": "MIT",
@@ -4114,14 +4640,14 @@
}
},
"node_modules/tinyglobby": {
- "version": "0.2.15",
- "resolved": "https://registry.npmmirror.com/tinyglobby/-/tinyglobby-0.2.15.tgz",
- "integrity": "sha512-j2Zq4NyQYG5XMST4cbs02Ak8iJUdxRM0XI5QyxXuZOzKOINmWurp3smXu3y5wDcJrptwpSjgXHzIQxR0omXljQ==",
+ "version": "0.2.17",
+ "resolved": "https://registry.npmjs.org/tinyglobby/-/tinyglobby-0.2.17.tgz",
+ "integrity": "sha512-wXR/dYpcqKmfWpEdZjiKJOwCNFndD0DMnrW/cYjVGttEkBfVgcLFHoNrlj47mjOVic9yyNu65alsgF4NQyTa2g==",
"dev": true,
"license": "MIT",
"dependencies": {
"fdir": "^6.5.0",
- "picomatch": "^4.0.3"
+ "picomatch": "^4.0.4"
},
"engines": {
"node": ">=12.0.0"
@@ -4132,7 +4658,7 @@
},
"node_modules/to-regex-range": {
"version": "5.0.1",
- "resolved": "https://registry.npmmirror.com/to-regex-range/-/to-regex-range-5.0.1.tgz",
+ "resolved": "https://registry.npmjs.org/to-regex-range/-/to-regex-range-5.0.1.tgz",
"integrity": "sha512-65P7iz6X5yEr1cwcgvQxbbIw7Uk3gOy5dIdtZ4rDveLqhrdJP+Li/Hx6tyK0NEb+2GCyneCMJiGqrADCSNk8sQ==",
"dev": true,
"license": "MIT",
@@ -4145,26 +4671,25 @@
},
"node_modules/ts-interface-checker": {
"version": "0.1.13",
- "resolved": "https://registry.npmmirror.com/ts-interface-checker/-/ts-interface-checker-0.1.13.tgz",
+ "resolved": "https://registry.npmjs.org/ts-interface-checker/-/ts-interface-checker-0.1.13.tgz",
"integrity": "sha512-Y/arvbn+rrz3JCKl9C4kVNfTfSm2/mEp5FSz5EsZSANGPSlQrpRI5M4PKF+mJnE52jOO90PnPSc3Ur3bTQw0gA==",
"dev": true,
"license": "Apache-2.0"
},
"node_modules/tslib": {
"version": "2.8.1",
- "resolved": "https://registry.npmmirror.com/tslib/-/tslib-2.8.1.tgz",
+ "resolved": "https://registry.npmjs.org/tslib/-/tslib-2.8.1.tgz",
"integrity": "sha512-oJFu94HQb+KVduSUQL7wnpmqnfmLsOA/nAh6b6EH0wCEoK0/mPeXU6c3wKDV83MkOuHPRHtSXKKU99IBazS/2w==",
"license": "0BSD"
},
"node_modules/tsx": {
- "version": "4.21.0",
- "resolved": "https://registry.npmmirror.com/tsx/-/tsx-4.21.0.tgz",
- "integrity": "sha512-5C1sg4USs1lfG0GFb2RLXsdpXqBSEhAaA/0kPL01wxzpMqLILNxIxIOKiILz+cdg/pLnOUxFYOR5yhHU666wbw==",
+ "version": "4.22.4",
+ "resolved": "https://registry.npmjs.org/tsx/-/tsx-4.22.4.tgz",
+ "integrity": "sha512-X8EX+XV4QR5xCsrgxaED954zTDfY8KqlDtskKEL0cHhyS/P8b4IFOvGDQpsC9Q1XnLq915wEfwwY/zzskCtmhg==",
"dev": true,
"license": "MIT",
"dependencies": {
- "esbuild": "~0.27.0",
- "get-tsconfig": "^4.7.5"
+ "esbuild": "~0.28.0"
},
"bin": {
"tsx": "dist/cli.mjs"
@@ -4178,7 +4703,7 @@
},
"node_modules/tsyringe": {
"version": "4.10.0",
- "resolved": "https://registry.npmmirror.com/tsyringe/-/tsyringe-4.10.0.tgz",
+ "resolved": "https://registry.npmjs.org/tsyringe/-/tsyringe-4.10.0.tgz",
"integrity": "sha512-axr3IdNuVIxnaK5XGEUFTu3YmAQ6lllgrvqfEoR16g/HGnYY/6We4oWENtAnzK6/LpJ2ur9PAb80RBt7/U4ugw==",
"license": "MIT",
"dependencies": {
@@ -4190,14 +4715,14 @@
},
"node_modules/tsyringe/node_modules/tslib": {
"version": "1.14.1",
- "resolved": "https://registry.npmmirror.com/tslib/-/tslib-1.14.1.tgz",
+ "resolved": "https://registry.npmjs.org/tslib/-/tslib-1.14.1.tgz",
"integrity": "sha512-Xni35NKzjgMrwevysHTCArtLDpPvye8zV/0E4EyYn43P7/7qvQwPh9BGkHewbMulVntbigmcT7rdX3BNo9wRJg==",
"license": "0BSD"
},
"node_modules/typescript": {
- "version": "5.9.3",
- "resolved": "https://registry.npmmirror.com/typescript/-/typescript-5.9.3.tgz",
- "integrity": "sha512-jl1vZzPDinLr9eUt3J/t7V6FgNEw9QjvBPdysz9KfQDD41fQrC2Y4vKQdiaUpFT4bXlb1RHhLpp8wtm6M5TgSw==",
+ "version": "6.0.3",
+ "resolved": "https://registry.npmjs.org/typescript/-/typescript-6.0.3.tgz",
+ "integrity": "sha512-y2TvuxSZPDyQakkFRPZHKFm+KKVqIisdg9/CZwm9ftvKXLP8NRWj38/ODjNbr43SsoXqNuAisEf1GdCxqWcdBw==",
"dev": true,
"license": "Apache-2.0",
"bin": {
@@ -4209,19 +4734,19 @@
}
},
"node_modules/undici": {
- "version": "7.24.8",
- "resolved": "https://registry.npmjs.org/undici/-/undici-7.24.8.tgz",
- "integrity": "sha512-6KQ/+QxK49Z/p3HO6E5ZCZWNnCasyZLa5ExaVYyvPxUwKtbCPMKELJOqh7EqOle0t9cH/7d2TaaTRRa6Nhs4YQ==",
+ "version": "8.9.0",
+ "resolved": "https://registry.npmjs.org/undici/-/undici-8.9.0.tgz",
+ "integrity": "sha512-aWZpUj7XoGonMClx4gdDRfgBjqeA+F473aDmROQQbM9n6PRfK/u1q/a0X4wMTgcHfT8H6fpbt98PFuDUwFg2YA==",
"dev": true,
"license": "MIT",
"engines": {
- "node": ">=20.18.1"
+ "node": ">=22.19.0"
}
},
"node_modules/undici-types": {
- "version": "7.16.0",
- "resolved": "https://registry.npmmirror.com/undici-types/-/undici-types-7.16.0.tgz",
- "integrity": "sha512-Zz+aZWSj8LE6zoxD+xrjh4VfkIG8Ya6LvYkZqtUQGJPZjYl53ypCaUwWqo7eI0x66KBGeRo+mlBEkMSeSZ38Nw==",
+ "version": "8.3.0",
+ "resolved": "https://registry.npmjs.org/undici-types/-/undici-types-8.3.0.tgz",
+ "integrity": "sha512-j375ScV60dom+YkPFIfTLcOiPxkN/buHz5GobjLhixFuANaNs3C9l4GmrWqejgXWJ7BbJcFYpTEUkS1Ge8bpZQ==",
"dev": true,
"license": "MIT"
},
@@ -4237,7 +4762,7 @@
},
"node_modules/update-browserslist-db": {
"version": "1.2.3",
- "resolved": "https://registry.npmmirror.com/update-browserslist-db/-/update-browserslist-db-1.2.3.tgz",
+ "resolved": "https://registry.npmjs.org/update-browserslist-db/-/update-browserslist-db-1.2.3.tgz",
"integrity": "sha512-Js0m9cx+qOgDxo0eMiFGEueWztz+d4+M3rGlmKPT+T4IS/jP4ylw3Nwpu6cpTTP8R1MAC1kF4VbdLt3ARf209w==",
"dev": true,
"funding": [
@@ -4268,7 +4793,7 @@
},
"node_modules/use-sync-external-store": {
"version": "1.6.0",
- "resolved": "https://registry.npmmirror.com/use-sync-external-store/-/use-sync-external-store-1.6.0.tgz",
+ "resolved": "https://registry.npmjs.org/use-sync-external-store/-/use-sync-external-store-1.6.0.tgz",
"integrity": "sha512-Pp6GSwGP/NrPIrxVFAIkOQeyw8lFenOHijQWkUTrDvrF4ALqylP2C/KCkeS9dpUM3KvYRQhna5vt7IL95+ZQ9w==",
"license": "MIT",
"peerDependencies": {
@@ -4277,24 +4802,23 @@
},
"node_modules/util-deprecate": {
"version": "1.0.2",
- "resolved": "https://registry.npmmirror.com/util-deprecate/-/util-deprecate-1.0.2.tgz",
+ "resolved": "https://registry.npmjs.org/util-deprecate/-/util-deprecate-1.0.2.tgz",
"integrity": "sha512-EPD5q1uXyFxJpCrLnCc1nHnq3gOa6DZBocAIiI2TaSCA7VCJ1UJDMagCzIkXNsUYfD1daK//LTEQ8xiIbrHtcw==",
"dev": true,
"license": "MIT"
},
"node_modules/vite": {
- "version": "7.3.5",
- "resolved": "https://registry.npmjs.org/vite/-/vite-7.3.5.tgz",
- "integrity": "sha512-KuOaNhcnGFN2zIPGA7wRmzF+lJA1sea7rHq17aiJ++9lzY1WWG6Jpwqwe1KNbRVPIqHmr8GLYx7jbrQcN/7/ww==",
+ "version": "8.1.3",
+ "resolved": "https://registry.npmjs.org/vite/-/vite-8.1.3.tgz",
+ "integrity": "sha512-Ds+gBRbj0lwRO2Y5hwnUBdxSwlAve9LeRyU4sNnAr0ewW0gWF0n5bgXgUzbgZ49MV9BVUAQUFYVcDUcilUExMA==",
"dev": true,
"license": "MIT",
"dependencies": {
- "esbuild": "^0.27.0",
- "fdir": "^6.5.0",
- "picomatch": "^4.0.3",
- "postcss": "^8.5.6",
- "rollup": "^4.43.0",
- "tinyglobby": "^0.2.15"
+ "lightningcss": "^1.32.0",
+ "picomatch": "^4.0.4",
+ "postcss": "^8.5.16",
+ "rolldown": "~1.1.3",
+ "tinyglobby": "^0.2.17"
},
"bin": {
"vite": "bin/vite.js"
@@ -4310,9 +4834,10 @@
},
"peerDependencies": {
"@types/node": "^20.19.0 || >=22.12.0",
+ "@vitejs/devtools": "^0.3.0",
+ "esbuild": "^0.27.0 || ^0.28.0",
"jiti": ">=1.21.0",
"less": "^4.0.0",
- "lightningcss": "^1.21.0",
"sass": "^1.70.0",
"sass-embedded": "^1.70.0",
"stylus": ">=0.54.8",
@@ -4325,15 +4850,18 @@
"@types/node": {
"optional": true
},
+ "@vitejs/devtools": {
+ "optional": true
+ },
+ "esbuild": {
+ "optional": true
+ },
"jiti": {
"optional": true
},
"less": {
"optional": true
},
- "lightningcss": {
- "optional": true
- },
"sass": {
"optional": true
},
@@ -4358,9 +4886,9 @@
}
},
"node_modules/vite-prerender-plugin": {
- "version": "0.5.12",
- "resolved": "https://registry.npmmirror.com/vite-prerender-plugin/-/vite-prerender-plugin-0.5.12.tgz",
- "integrity": "sha512-EiwhbMn+flg14EysbLTmZSzq8NGTxhytgK3bf4aGRF1evWLGwZiHiUJ1KZDvbxgKbMf2pG6fJWGEa3UZXOnR1g==",
+ "version": "0.5.13",
+ "resolved": "https://registry.npmjs.org/vite-prerender-plugin/-/vite-prerender-plugin-0.5.13.tgz",
+ "integrity": "sha512-IKSpYkzDBsKAxa05naRbj7GvNVMSdww/Z/E89oO3xndz+gWnOBOKOAbEXv7qDhktY/j3vHgJmoV1pPzqU2tx9g==",
"dev": true,
"license": "MIT",
"dependencies": {
@@ -4372,13 +4900,13 @@
"stack-trace": "^1.0.0-pre2"
},
"peerDependencies": {
- "vite": "5.x || 6.x || 7.x"
+ "vite": "5.x || 6.x || 7.x || 8.x"
}
},
"node_modules/workerd": {
- "version": "1.20260603.1",
- "resolved": "https://registry.npmjs.org/workerd/-/workerd-1.20260603.1.tgz",
- "integrity": "sha512-NPcbhI1++CS+fnELyXtsIR52en+5kwr/OrKeiQeYXGy10HxmPdsQBv9N+DU7hJIOOmBHhOGAAsoGDjyiQ2YCaA==",
+ "version": "1.20260625.1",
+ "resolved": "https://registry.npmjs.org/workerd/-/workerd-1.20260625.1.tgz",
+ "integrity": "sha512-GApQvFX52SDM6L4u0+RRnUDB1wJOnEwoXjinkmOPtIyofWBxrlZckdegJSYc1leg++lLZ3+DQ4zMVmBqYVtzfA==",
"dev": true,
"hasInstallScript": true,
"license": "Apache-2.0",
@@ -4389,17 +4917,17 @@
"node": ">=16"
},
"optionalDependencies": {
- "@cloudflare/workerd-darwin-64": "1.20260603.1",
- "@cloudflare/workerd-darwin-arm64": "1.20260603.1",
- "@cloudflare/workerd-linux-64": "1.20260603.1",
- "@cloudflare/workerd-linux-arm64": "1.20260603.1",
- "@cloudflare/workerd-windows-64": "1.20260603.1"
+ "@cloudflare/workerd-darwin-64": "1.20260625.1",
+ "@cloudflare/workerd-darwin-arm64": "1.20260625.1",
+ "@cloudflare/workerd-linux-64": "1.20260625.1",
+ "@cloudflare/workerd-linux-arm64": "1.20260625.1",
+ "@cloudflare/workerd-windows-64": "1.20260625.1"
}
},
"node_modules/wouter": {
- "version": "3.9.0",
- "resolved": "https://registry.npmmirror.com/wouter/-/wouter-3.9.0.tgz",
- "integrity": "sha512-sF/od/PIgqEQBQcrN7a2x3MX6MQE6nW0ygCfy9hQuUkuB28wEZuu/6M5GyqkrrEu9M6jxdkgE12yDFsQMKos4Q==",
+ "version": "3.10.0",
+ "resolved": "https://registry.npmjs.org/wouter/-/wouter-3.10.0.tgz",
+ "integrity": "sha512-zTfddD80zc2/J5l8JKcdvzOK6AwP0kpyHEI3DxRN2bn8U1oJPnrSVm8v+X3WwDamvLAOxTO7ZvkxkpRWlyeJ1Q==",
"license": "Unlicense",
"dependencies": {
"mitt": "^3.0.1",
@@ -4411,22 +4939,23 @@
}
},
"node_modules/wrangler": {
- "version": "4.98.0",
- "resolved": "https://registry.npmjs.org/wrangler/-/wrangler-4.98.0.tgz",
- "integrity": "sha512-cXfFUuF4rMIvE0hiMnXjEAB27ERryaCgquBJdUoPIjFzYYE1rbRdMUkEdQ18qDPUtsPvhJdqxLntixT9OfSzQw==",
+ "version": "4.105.0",
+ "resolved": "https://registry.npmjs.org/wrangler/-/wrangler-4.105.0.tgz",
+ "integrity": "sha512-7dXFH6OLj1Fv0y6ZeRPUxFTkp+duWD7/xxVi/1c0vfOeEYwIFKWB7cdqnY05DvY1Ta3BnqAwRkXfLs8PDj538g==",
"dev": true,
"license": "MIT OR Apache-2.0",
"dependencies": {
"@cloudflare/kv-asset-handler": "0.5.0",
"@cloudflare/unenv-preset": "2.16.1",
"blake3-wasm": "2.1.5",
- "esbuild": "0.27.3",
- "miniflare": "4.20260603.0",
+ "esbuild": "0.28.1",
+ "miniflare": "4.20260625.0",
"path-to-regexp": "6.3.0",
"unenv": "2.0.0-rc.24",
- "workerd": "1.20260603.1"
+ "workerd": "1.20260625.1"
},
"bin": {
+ "cf-wrangler": "bin/cf-wrangler.js",
"wrangler": "bin/wrangler.js",
"wrangler2": "bin/wrangler.js"
},
@@ -4437,7 +4966,7 @@
"fsevents": "2.3.3"
},
"peerDependencies": {
- "@cloudflare/workers-types": "^4.20260603.1"
+ "@cloudflare/workers-types": "^4.20260625.1"
},
"peerDependenciesMeta": {
"@cloudflare/workers-types": {
@@ -4446,9 +4975,9 @@
}
},
"node_modules/ws": {
- "version": "8.20.1",
- "resolved": "https://registry.npmjs.org/ws/-/ws-8.20.1.tgz",
- "integrity": "sha512-It4dO0K5v//JtTXuPkfEOaI3uUN87iYPnqo/ZzqCoG3g8uhA66QUMs/SrM0YK7/NAu+r4LMh/9dq2A7k+rHs+w==",
+ "version": "8.21.0",
+ "resolved": "https://registry.npmjs.org/ws/-/ws-8.21.0.tgz",
+ "integrity": "sha512-Vsp28b7DRcimFQvrqu2Wek3z1iYxDCWqHYB8Qsnk/S4RfaCQzPGPyBNuVjJV3cd6UiKtUtp6sNM77gWvzcCH+g==",
"dev": true,
"license": "MIT",
"engines": {
@@ -4467,16 +4996,9 @@
}
}
},
- "node_modules/yallist": {
- "version": "3.1.1",
- "resolved": "https://registry.npmmirror.com/yallist/-/yallist-3.1.1.tgz",
- "integrity": "sha512-a4UGQaWPH59mOXUYnAG2ewncQS4i4F43Tv3JoAM+s2VDAmS9NsK8GpDMLrCHPksFT7h3K6TOoUNn2pb7RoXx4g==",
- "dev": true,
- "license": "ISC"
- },
"node_modules/yaml": {
"version": "2.8.3",
- "resolved": "https://registry.npmmirror.com/yaml/-/yaml-2.8.3.tgz",
+ "resolved": "https://registry.npmjs.org/yaml/-/yaml-2.8.3.tgz",
"integrity": "sha512-AvbaCLOO2Otw/lW5bmh9d/WEdcDFdQp2Z2ZUH3pX9U2ihyUY0nvLv7J6TrWowklRGPYbB/IuIMfYgxaCPg5Bpg==",
"dev": true,
"license": "ISC",
@@ -4514,6 +5036,13 @@
"@poppinss/exception": "^1.2.2",
"error-stack-parser-es": "^1.0.5"
}
+ },
+ "node_modules/zimmerframe": {
+ "version": "1.1.4",
+ "resolved": "https://registry.npmjs.org/zimmerframe/-/zimmerframe-1.1.4.tgz",
+ "integrity": "sha512-B58NGBEoc8Y9MWWCQGl/gq9xBCe4IiKM0a2x7GZdQKOW5Exr8S1W24J6OgM1njK8xCRGvAJIL/MxXHf6SkmQKQ==",
+ "dev": true,
+ "license": "MIT"
}
}
}
diff --git a/package.json b/package.json
index 4016b40..19300f3 100644
--- a/package.json
+++ b/package.json
@@ -1,6 +1,6 @@
{
"name": "nodewarden",
- "version": "1.6.1",
+ "version": "1.8.0",
"description": "Minimal Bitwarden-compatible server running on Cloudflare Workers",
"author": "shuaiplus",
"license": "LGPL-3.0",
@@ -15,6 +15,11 @@
"domains:sync": "node scripts/sync-global-domains.mjs",
"i18n": "node scripts/i18n-validate.cjs",
"i18n:validate": "node scripts/i18n-validate.cjs",
+ "test:config-compatibility": "tsx --test scripts/config-compatibility.test.ts",
+ "test:web-crypto": "tsx --test scripts/web-crypto-availability.test.ts",
+ "test:webauthn-mobile": "node --test scripts/webauthn-mobile-connector.test.mjs",
+ "test:webauthn-connector": "node --test scripts/webauthn-connector.test.mjs && tsx --test scripts/webauthn-connector-headers.test.ts",
+ "test:webauthn-connectors": "node --test scripts/webauthn-mobile-connector.test.mjs scripts/webauthn-connector.test.mjs && tsx --test scripts/webauthn-connector-headers.test.ts",
"deploy": "wrangler deploy",
"deploy:kv": "node scripts/ensure-kv.cjs && wrangler deploy -c wrangler.kv.toml",
"deploy:demo": "npm run build:demo && wrangler pages deploy dist --project-name nw-demo"
@@ -42,28 +47,37 @@
}
}
},
+ "overrides": {
+ "nanoid": "3.3.17",
+ "undici": "8.9.0",
+ "@babel/core": ">=7.29.6",
+ "esbuild": ">=0.28.1",
+ "ws": "8.21.0",
+ "sharp": "0.35.0"
+ },
"devDependencies": {
- "@cloudflare/workers-types": "^4.20260131.0",
- "@preact/preset-vite": "^2.10.3",
- "@types/node": "^25.2.3",
- "autoprefixer": "^10.4.21",
- "opencc-js": "^1.0.5",
- "postcss": "^8.5.6",
- "tailwindcss": "^3.4.17",
- "tsx": "^4.21.0",
- "typescript": "^5.9.3",
- "vite": "^7.3.1",
- "wrangler": "^4.71.0"
+ "@cloudflare/workers-types": "^4.20260630.1",
+ "@preact/preset-vite": "^2.10.5",
+ "@types/node": "^26.0.1",
+ "autoprefixer": "^10.5.2",
+ "opencc-js": "^1.3.2",
+ "postcss": "^8.5.23",
+ "tailwindcss": "^3.4.19",
+ "tsx": "^4.22.4",
+ "typescript": "^6.0.3",
+ "vite": "^8.1.3",
+ "wrangler": "^4.105.0"
},
"dependencies": {
- "@noble/hashes": "^2.0.1",
- "@simplewebauthn/server": "^13.3.1",
- "@tanstack/react-query": "^5.90.21",
- "@zip.js/zip.js": "^2.8.22",
- "fflate": "^0.8.2",
- "lucide-preact": "^0.575.0",
- "preact": "^10.28.4",
+ "@noble/hashes": "^2.2.0",
+ "@simplewebauthn/server": "^13.3.2",
+ "@tanstack/react-query": "^5.101.2",
+ "@zip.js/zip.js": "^2.8.26",
+ "fflate": "^0.8.3",
+ "jsqr": "1.4.0",
+ "lucide-preact": "^1.22.0",
+ "preact": "^10.29.3",
"qrcode-generator": "^2.0.4",
- "wouter": "^3.9.0"
+ "wouter": "^3.10.0"
}
}
diff --git a/scripts/config-compatibility.test.ts b/scripts/config-compatibility.test.ts
new file mode 100644
index 0000000..571192d
--- /dev/null
+++ b/scripts/config-compatibility.test.ts
@@ -0,0 +1,12 @@
+import assert from 'node:assert/strict';
+import test from 'node:test';
+
+import { buildConfigResponse } from '../src/config-response';
+
+test('config enables the official Bitwarden desktop settings dialog', () => {
+ const body = buildConfigResponse('https://vault.example.test');
+
+ assert.equal(body.featureStates['desktop-ui-settings-dialog'], true);
+ assert.equal(body.environment.vault, 'https://vault.example.test');
+ assert.equal(body.object, 'config');
+});
diff --git a/scripts/i18n-utils.cjs b/scripts/i18n-utils.cjs
index 028b377..51a7869 100644
--- a/scripts/i18n-utils.cjs
+++ b/scripts/i18n-utils.cjs
@@ -13,6 +13,11 @@ const localeFiles = [
['zh-TW', 'zh-TW.ts', 'zhTW', 'Traditional Chinese'],
['ru', 'ru.ts', 'ru', 'Russian'],
['es', 'es.ts', 'es', 'Spanish'],
+ ['fi', 'fi.ts', 'fi', 'Finnish'],
+ ['de', 'de.ts', 'de', 'German'],
+ ['fr', 'fr.ts', 'fr', 'French'],
+ ['it', 'it.ts', 'it', 'Italian'],
+ ['sv', 'sv.ts', 'sv', 'Swedish'],
];
function readLocale(fileName, variableName) {
diff --git a/scripts/security-audit-api-key-semantics.mjs b/scripts/security-audit-api-key-semantics.mjs
new file mode 100644
index 0000000..46996e5
--- /dev/null
+++ b/scripts/security-audit-api-key-semantics.mjs
@@ -0,0 +1,128 @@
+import { handleGetApiKey, handleRotateApiKey } from '../src/handlers/accounts.ts';
+import { hashApiKey, verifyApiKey } from '../src/utils/api-key.ts';
+
+function assert(condition, message) {
+ if (!condition) throw new Error(message);
+}
+
+function createUserRow(apiKey) {
+ return {
+ id: 'user-1',
+ email: 'user@example.com',
+ name: 'User',
+ master_password_hint: null,
+ master_password_hash: 'master-proof',
+ key: 'wrapped-user-key',
+ private_key: null,
+ public_key: null,
+ kdf_type: 0,
+ kdf_iterations: 600000,
+ kdf_memory: null,
+ kdf_parallelism: null,
+ security_stamp: 'security-stamp-original',
+ role: 'user',
+ status: 'active',
+ verify_devices: 0,
+ totp_secret: null,
+ totp_recovery_code: null,
+ yubikey_key1: null,
+ yubikey_key2: null,
+ yubikey_key3: null,
+ yubikey_key4: null,
+ yubikey_key5: null,
+ yubikey_nfc: 0,
+ api_key: apiKey,
+ created_at: '2026-01-01T00:00:00.000Z',
+ updated_at: '2026-01-01T00:00:00.000Z',
+ };
+}
+
+function createDb(apiKey) {
+ const state = {
+ user: createUserRow(apiKey),
+ userWrites: 0,
+ refreshDeletes: 0,
+ auditActions: [],
+ };
+ const db = {
+ prepare(sql) {
+ let bindings = [];
+ const statement = {
+ bind(...values) {
+ bindings = values;
+ return statement;
+ },
+ async first() {
+ if (/FROM users WHERE id = \?/i.test(sql)) return { ...state.user };
+ return null;
+ },
+ async all() {
+ return { results: [] };
+ },
+ async run() {
+ if (/INSERT INTO users\(/i.test(sql)) {
+ state.userWrites += 1;
+ state.user.security_stamp = bindings[12];
+ state.user.api_key = bindings[24];
+ state.user.updated_at = bindings[26];
+ }
+ if (/DELETE FROM refresh_tokens/i.test(sql)) state.refreshDeletes += 1;
+ if (/INSERT INTO audit_logs/i.test(sql)) state.auditActions.push(bindings[2]);
+ return { meta: { changes: 1 } };
+ },
+ };
+ return statement;
+ },
+ async batch(statements) {
+ return statements.map(() => ({ success: true, meta: { changes: 1 } }));
+ },
+ };
+ return { db, state };
+}
+
+function request() {
+ return new Request('https://nodewarden.example/api/accounts/api-key', {
+ method: 'POST',
+ headers: { 'Content-Type': 'application/json' },
+ body: JSON.stringify({ masterPasswordHash: 'master-proof' }),
+ });
+}
+
+function env(db) {
+ return { DB: db, JWT_SECRET: 'test-secret-at-least-thirty-two-characters' };
+}
+
+const view = createDb('ExistingReadableApiKey1234567');
+const viewResponse = await handleGetApiKey(request(), env(view.db), 'user-1');
+const viewBody = await viewResponse.json();
+assert(viewResponse.status === 200, 'Viewing an existing readable API key failed');
+assert(viewBody.apiKey === 'ExistingReadableApiKey1234567', 'View did not return the existing API key');
+assert(view.state.userWrites === 0, 'View unexpectedly rewrote the user');
+assert(view.state.refreshDeletes === 0, 'View unexpectedly revoked refresh tokens');
+assert(view.state.auditActions.includes('account.api_key.view'), 'View audit action is missing');
+
+const rotate = createDb('ExistingReadableApiKey1234567');
+const rotateResponse = await handleRotateApiKey(request(), env(rotate.db), 'user-1');
+const rotateBody = await rotateResponse.json();
+assert(rotateResponse.status === 200, 'API key rotation failed');
+assert(rotateBody.apiKey !== 'ExistingReadableApiKey1234567', 'Rotation returned the old API key');
+assert(rotate.state.user.api_key === rotateBody.apiKey, 'Rotation did not persist the returned API key');
+assert(rotate.state.user.security_stamp === 'security-stamp-original', 'Rotation changed securityStamp');
+assert(rotate.state.refreshDeletes === 0, 'Rotation revoked unrelated refresh tokens');
+assert(!(await verifyApiKey('ExistingReadableApiKey1234567', rotate.state.user.api_key)), 'Old API key still authenticates');
+assert(await verifyApiKey(rotateBody.apiKey, rotate.state.user.api_key), 'Rotated API key does not authenticate');
+
+const legacyPlain = 'LegacyHashedApiKey123456789';
+const legacy = createDb(await hashApiKey(legacyPlain));
+const legacyResponse = await handleGetApiKey(request(), env(legacy.db), 'user-1');
+assert(legacyResponse.status === 409, 'Legacy hashed key view should require explicit rotation');
+assert(legacy.state.userWrites === 0, 'Legacy hashed key was silently rotated');
+assert(await verifyApiKey(legacyPlain, legacy.state.user.api_key), 'Legacy hashed API key stopped authenticating');
+
+const missing = createDb(null);
+const missingResponse = await handleGetApiKey(request(), env(missing.db), 'user-1');
+const missingBody = await missingResponse.json();
+assert(missingResponse.status === 200 && !!missingBody.apiKey, 'Missing legacy API key was not initialized');
+assert(missing.state.userWrites === 1, 'Missing legacy API key initialization was not persisted');
+
+console.log('Bitwarden-compatible API key view and rotation semantics: PASS');
diff --git a/scripts/security-audit-backup-auth-state.mjs b/scripts/security-audit-backup-auth-state.mjs
new file mode 100644
index 0000000..d5842ab
--- /dev/null
+++ b/scripts/security-audit-backup-auth-state.mjs
@@ -0,0 +1,138 @@
+import { unzipSync, zipSync } from 'fflate';
+import {
+ buildBackupArchive,
+ parseBackupArchive,
+ validateBackupPayloadContents,
+} from '../src/services/backup-archive.ts';
+import { importBackupArchiveBytes } from '../src/services/backup-import.ts';
+
+const forbiddenRuntimeTables = [
+ 'devices',
+ 'refresh_tokens',
+ 'auth_requests',
+ 'trusted_two_factor_device_tokens',
+ 'account_passkey_challenges',
+ 'used_attachment_download_tokens',
+];
+
+function assert(condition, message) {
+ if (!condition) throw new Error(message);
+}
+
+function sqlTouchesTable(sql, table) {
+ return new RegExp(`\\b(?:from|into|table)\\s+[\"']?${table}\\b`, 'i').test(sql);
+}
+
+function emptyBackupDb(extra = {}) {
+ return {
+ config: [],
+ users: [],
+ domain_settings: [],
+ user_revisions: [],
+ folders: [],
+ ciphers: [],
+ attachments: [],
+ webauthn_credentials: [],
+ ...extra,
+ };
+}
+
+function archiveBytes(db, tableCounts = {}) {
+ const encoder = new TextEncoder();
+ return zipSync({
+ 'manifest.json': encoder.encode(JSON.stringify({
+ formatVersion: 1,
+ exportedAt: new Date(0).toISOString(),
+ appVersion: 'test',
+ storageKind: null,
+ tableCounts,
+ includes: { attachments: false },
+ blobSummary: { attachmentFiles: 0, totalBytes: 0, largestObjectBytes: 0 },
+ attachmentBlobs: [],
+ })),
+ 'db.json': encoder.encode(JSON.stringify(db)),
+ }, { level: 0 });
+}
+
+function createD1Mock({ exportMode = false } = {}) {
+ const preparedSql = [];
+ const db = {
+ prepare(sql) {
+ preparedSql.push(sql);
+ let bindings = [];
+ const statement = {
+ sql,
+ bind(...values) {
+ bindings = values;
+ return statement;
+ },
+ async all() {
+ if (exportMode) return { results: [] };
+ return { results: [] };
+ },
+ async first() {
+ if (/SELECT sql FROM sqlite_master/i.test(sql)) {
+ const table = String(bindings[0] || '').trim();
+ return { sql: `CREATE TABLE ${table} (id TEXT)` };
+ }
+ if (/SELECT COUNT\(\*\).*FROM config__restore/i.test(sql)) return { count: 1 };
+ if (/SELECT COUNT\(\*\)/i.test(sql)) return { count: 0 };
+ return null;
+ },
+ async run() {
+ return { meta: { changes: 0 } };
+ },
+ };
+ return statement;
+ },
+ async batch(statements) {
+ return statements.map(() => ({ success: true, meta: { changes: 0 } }));
+ },
+ };
+ return { db, preparedSql };
+}
+
+const exportMock = createD1Mock({ exportMode: true });
+const exported = await buildBackupArchive({ DB: exportMock.db }, new Date(0), { includeAttachments: false });
+const exportedZip = unzipSync(exported.bytes);
+const exportedManifest = JSON.parse(new TextDecoder().decode(exportedZip['manifest.json']));
+const exportedDb = JSON.parse(new TextDecoder().decode(exportedZip['db.json']));
+
+for (const table of forbiddenRuntimeTables) {
+ assert(!(table in exportedDb), `Export contains forbidden runtime table: ${table}`);
+ assert(!(table in exportedManifest.tableCounts), `Manifest counts forbidden runtime table: ${table}`);
+ assert(!exportMock.preparedSql.some((sql) => sqlTouchesTable(sql, table)), `Export queried forbidden runtime table: ${table}`);
+}
+
+const legacyDb = emptyBackupDb({
+ devices: [{ device_identifier: 'device-secret' }],
+ refresh_tokens: [{ token: 'refresh-secret' }],
+ auth_requests: [{ access_code: 'approval-secret' }],
+ trusted_two_factor_device_tokens: [{ token: 'remember-secret' }],
+ account_passkey_challenges: [{ challenge_hash: 'challenge-secret' }],
+ used_attachment_download_tokens: [{ token_hash: 'download-secret' }],
+});
+const legacyArchive = archiveBytes(legacyDb, {
+ devices: 1,
+ refresh_tokens: 1,
+ auth_requests: 1,
+ trusted_two_factor_device_tokens: 1,
+ account_passkey_challenges: 1,
+ used_attachment_download_tokens: 1,
+});
+const parsedLegacy = parseBackupArchive(legacyArchive);
+validateBackupPayloadContents(parsedLegacy.payload, parsedLegacy.files);
+for (const table of forbiddenRuntimeTables) {
+ assert(!(table in parsedLegacy.payload.db), `Legacy runtime table was not ignored: ${table}`);
+}
+
+const restoreMock = createD1Mock();
+await importBackupArchiveBytes(legacyArchive, { DB: restoreMock.db }, 'actor', false);
+for (const table of forbiddenRuntimeTables) {
+ assert(
+ !restoreMock.preparedSql.some((sql) => sqlTouchesTable(sql, table)),
+ `Restore touched forbidden runtime table: ${table}`
+ );
+}
+
+console.log('backup runtime authentication state exclusion: PASS');
diff --git a/scripts/security-audit-backup-endpoint.mjs b/scripts/security-audit-backup-endpoint.mjs
new file mode 100644
index 0000000..98df727
--- /dev/null
+++ b/scripts/security-audit-backup-endpoint.mjs
@@ -0,0 +1,38 @@
+import { normalizeBackupEndpointUrl } from '../src/services/backup-config.ts';
+import fs from 'node:fs';
+
+const scratch = process.env.SCRATCH || '.';
+const cases = [
+ 'http://127.0.0.1',
+ 'http://169.254.169.254',
+ 'http://[::1]',
+ 'http://[0:0:0:0:0:0:0:1]',
+ 'http://[::2]',
+ 'http://[::]',
+ 'http://[fe80::1]',
+ 'http://[fc00::1]',
+ 'https://example.com',
+];
+
+const out = [];
+for (const url of cases) {
+ try {
+ const normalized = normalizeBackupEndpointUrl(url, 'WebDAV server URL');
+ out.push({ url, allowed: true, normalized });
+ } catch (e) {
+ out.push({ url, allowed: false, error: e instanceof Error ? e.message : String(e) });
+ }
+}
+
+const path = `${scratch}/poc-normalizeBackupEndpointUrl.json`;
+fs.writeFileSync(path, JSON.stringify(out, null, 2));
+console.log(JSON.stringify(out, null, 2));
+
+// Security expectation: IPv6 loopback must NOT be allowed.
+const loopback = out.find((row) => row.url === 'http://[::1]');
+if (loopback?.allowed) {
+ console.error('FINDING_CONFIRMED: normalizeBackupEndpointUrl accepts http://[::1]');
+ process.exitCode = 2;
+} else {
+ console.log('IPv6 loopback rejected as expected');
+}
diff --git a/scripts/web-crypto-availability.test.ts b/scripts/web-crypto-availability.test.ts
new file mode 100644
index 0000000..27311f3
--- /dev/null
+++ b/scripts/web-crypto-availability.test.ts
@@ -0,0 +1,84 @@
+import assert from 'node:assert/strict';
+import test from 'node:test';
+
+import { registerAccount } from '../webapp/src/lib/api/auth';
+import {
+ requireWebCrypto,
+ WebCryptoUnavailableError,
+} from '../webapp/src/lib/crypto';
+
+const supportedCrypto = {
+ subtle: {
+ importKey: () => Promise.reject(new Error('not used by capability checks')),
+ },
+ getRandomValues: (array: T): T => array,
+} as unknown as Crypto;
+
+function restoreGlobalProperty(name: string, descriptor: PropertyDescriptor | undefined): void {
+ if (descriptor) {
+ Object.defineProperty(globalThis, name, descriptor);
+ return;
+ }
+ delete (globalThis as unknown as Record)[name];
+}
+
+test('Web Crypto guard rejects insecure browser contexts', () => {
+ assert.throws(
+ () => requireWebCrypto({ crypto: supportedCrypto, isSecureContext: false }),
+ WebCryptoUnavailableError
+ );
+});
+
+test('Web Crypto guard rejects secure contexts without SubtleCrypto', () => {
+ const cryptoWithoutSubtle = {
+ getRandomValues: (array: T): T => array,
+ } as unknown as Crypto;
+
+ assert.throws(
+ () => requireWebCrypto({ crypto: cryptoWithoutSubtle, isSecureContext: true }),
+ WebCryptoUnavailableError
+ );
+});
+
+test('Web Crypto guard accepts a secure supported browser', () => {
+ assert.equal(
+ requireWebCrypto({ crypto: supportedCrypto, isSecureContext: true }),
+ supportedCrypto
+ );
+});
+
+test('registration returns an actionable error without contacting the backend', async () => {
+ const cryptoDescriptor = Object.getOwnPropertyDescriptor(globalThis, 'crypto');
+ const secureContextDescriptor = Object.getOwnPropertyDescriptor(globalThis, 'isSecureContext');
+ const fetchDescriptor = Object.getOwnPropertyDescriptor(globalThis, 'fetch');
+ let fetchCalled = false;
+
+ Object.defineProperty(globalThis, 'crypto', { value: undefined, configurable: true });
+ Object.defineProperty(globalThis, 'isSecureContext', { value: false, configurable: true });
+ Object.defineProperty(globalThis, 'fetch', {
+ configurable: true,
+ value: async () => {
+ fetchCalled = true;
+ return new Response(null, { status: 500 });
+ },
+ });
+
+ try {
+ const result = await registerAccount({
+ email: 'first@example.test',
+ name: 'First Admin',
+ password: 'correct horse battery staple',
+ fallbackIterations: 600_000,
+ });
+
+ assert.deepEqual(result, {
+ ok: false,
+ message: 'Secure browser cryptography is unavailable. Open NodeWarden over HTTPS in a supported browser.',
+ });
+ assert.equal(fetchCalled, false);
+ } finally {
+ restoreGlobalProperty('crypto', cryptoDescriptor);
+ restoreGlobalProperty('isSecureContext', secureContextDescriptor);
+ restoreGlobalProperty('fetch', fetchDescriptor);
+ }
+});
diff --git a/scripts/webauthn-connector-headers.test.ts b/scripts/webauthn-connector-headers.test.ts
new file mode 100644
index 0000000..d367afb
--- /dev/null
+++ b/scripts/webauthn-connector-headers.test.ts
@@ -0,0 +1,48 @@
+import assert from 'node:assert/strict';
+import { readFile } from 'node:fs/promises';
+import test from 'node:test';
+
+import type { Env } from '../src/types';
+import { getConfiguredWebAuthnAllowedOrigins } from '../src/utils/origins';
+import { applyCors, handleCors } from '../src/utils/response';
+
+const env = {} as Env;
+
+test('only the iframe connector drops anti-framing headers', () => {
+ const connectorRequest = new Request('https://vault.example.test/webauthn-connector.html');
+ const connector = applyCors(connectorRequest, new Response(''), env);
+ assert.equal(connector.headers.get('X-Frame-Options'), null);
+ assert.doesNotMatch(connector.headers.get('Content-Security-Policy') || '', /frame-ancestors/);
+ assert.match(connector.headers.get('Content-Security-Policy') || '', /script-src 'self'/);
+
+ for (const path of ['/', '/webauthn-fallback-connector.html', '/webauthn-mobile-connector.html']) {
+ const request = new Request(`https://vault.example.test${path}`);
+ const response = applyCors(request, new Response(''), env);
+ assert.equal(response.headers.get('X-Frame-Options'), 'DENY');
+ assert.match(response.headers.get('Content-Security-Policy') || '', /frame-ancestors 'none'/);
+ }
+});
+
+test('official Bitwarden desktop origin receives credentialed CORS', () => {
+ assert.ok(getConfiguredWebAuthnAllowedOrigins(env).includes('bw-desktop-file://bundle'));
+ const preflight = handleCors(new Request('https://vault.example.test/api/sync', {
+ method: 'OPTIONS',
+ headers: {
+ Origin: 'bw-desktop-file://bundle',
+ 'Access-Control-Request-Headers': 'authorization, content-type',
+ },
+ }), env);
+ assert.equal(preflight.headers.get('Access-Control-Allow-Origin'), 'bw-desktop-file://bundle');
+ assert.equal(preflight.headers.get('Access-Control-Allow-Credentials'), 'true');
+});
+
+test('Worker assets preserve exact official connector .html paths', async () => {
+ for (const configUrl of [
+ new URL('../wrangler.toml', import.meta.url),
+ new URL('../wrangler.kv.toml', import.meta.url),
+ ]) {
+ const config = await readFile(configUrl, 'utf8');
+ const assetsSection = config.match(/\[assets\]([\s\S]*?)(?=\n\[|$)/)?.[1] || '';
+ assert.match(assetsSection, /^\s*html_handling\s*=\s*"none"\s*$/m);
+ }
+});
diff --git a/scripts/webauthn-connector.test.mjs b/scripts/webauthn-connector.test.mjs
new file mode 100644
index 0000000..f9a2377
--- /dev/null
+++ b/scripts/webauthn-connector.test.mjs
@@ -0,0 +1,126 @@
+import assert from 'node:assert/strict';
+import { readFile } from 'node:fs/promises';
+import test from 'node:test';
+
+import {
+ buildCredentialData,
+ normalizePublicKeyOptions,
+ parseConnectorRequest,
+ resolveParentChannel,
+} from '../webapp/public/webauthn-connector.js';
+
+function encodeBase64Utf8(value) {
+ return Buffer.from(value, 'utf8').toString('base64');
+}
+
+const publicKeyOptions = {
+ challenge: 'AQID',
+ allowCredentials: [{ id: 'BAUG', type: 'public-key', transports: ['usb'] }],
+ timeout: 60000,
+ rpId: 'vault.example.test',
+};
+
+test('parses the official desktop/browser V1 connector request', () => {
+ const params = new URLSearchParams({
+ data: encodeBase64Utf8(JSON.stringify(publicKeyOptions)),
+ parent: encodeURIComponent('file:///C:/Program Files/Bitwarden/resources/app/index.html'),
+ btnText: encodeURIComponent('Read security key'),
+ btnAwaitingInteractionText: encodeURIComponent('Awaiting security key interaction...'),
+ v: '1',
+ });
+ const request = parseConnectorRequest(params);
+ assert.equal(request.parentUrl, 'file:///C:/Program Files/Bitwarden/resources/app/index.html');
+ assert.equal(request.parentProtocol, 'file:');
+ assert.deepEqual(JSON.parse(request.webauthnJson), publicKeyOptions);
+ assert.equal(request.buttonText, 'Read security key');
+ assert.equal(request.awaitingText, 'Awaiting security key interaction...');
+});
+
+test('keeps V2 parsing compatible with the shared official connector protocol', () => {
+ const params = new URLSearchParams({
+ data: encodeBase64Utf8(JSON.stringify({ data: JSON.stringify(publicKeyOptions) })),
+ parent: encodeURIComponent('chrome-extension://nngceckbapebfimnlniiiahkandclblb/popup/index.html'),
+ v: '2',
+ });
+ assert.deepEqual(JSON.parse(parseConnectorRequest(params).webauthnJson), publicKeyOptions);
+});
+
+test('normalizes WebAuthn challenge and allowed credential IDs', () => {
+ const normalized = normalizePublicKeyOptions(JSON.stringify(publicKeyOptions));
+ assert.deepEqual(Array.from(normalized.challenge), [1, 2, 3]);
+ assert.deepEqual(Array.from(normalized.allowCredentials[0].id), [4, 5, 6]);
+});
+
+test('emits the exact assertion shape consumed by official Bitwarden clients', () => {
+ const output = JSON.parse(buildCredentialData({
+ id: 'credential-id',
+ rawId: Uint8Array.from([1, 2, 3]).buffer,
+ type: 'public-key',
+ getClientExtensionResults: () => ({ appid: false }),
+ response: {
+ authenticatorData: Uint8Array.from([4, 5]).buffer,
+ clientDataJSON: Uint8Array.from([6, 7]).buffer,
+ signature: Uint8Array.from([8, 9]).buffer,
+ },
+ }));
+ assert.deepEqual(output, {
+ id: 'credential-id',
+ rawId: 'AQID',
+ type: 'public-key',
+ extensions: { appid: false },
+ response: {
+ authenticatorData: 'BAU',
+ clientDataJson: 'Bgc',
+ signature: 'CAk',
+ },
+ });
+});
+
+test('accepts legacy file and current official desktop parent origins', () => {
+ assert.deepEqual(resolveParentChannel({
+ parentProtocol: 'file:',
+ parentUrl: 'file:///C:/Bitwarden/index.html',
+ }, 'https://vault.example.test'), {
+ eventOrigin: 'null',
+ targetOrigin: 'file:///C:/Bitwarden/index.html',
+ });
+ assert.deepEqual(resolveParentChannel({
+ parentProtocol: 'bw-desktop-file:',
+ parentUrl: 'bw-desktop-file://bundle/index.html',
+ }, 'https://vault.example.test'), {
+ eventOrigin: 'bw-desktop-file://bundle',
+ targetOrigin: 'bw-desktop-file://bundle/index.html',
+ });
+});
+
+test('accepts configured official extension origins and rejects arbitrary parents', () => {
+ const extension = 'chrome-extension://nngceckbapebfimnlniiiahkandclblb';
+ assert.deepEqual(resolveParentChannel({
+ parentProtocol: 'chrome-extension:',
+ parentUrl: `${extension}/popup/index.html`,
+ }, 'https://vault.example.test', [extension]), {
+ eventOrigin: extension,
+ targetOrigin: extension,
+ });
+ assert.throws(() => resolveParentChannel({
+ parentProtocol: 'https:',
+ parentUrl: 'https://attacker.example/frame',
+ }, 'https://vault.example.test', []), /Untrusted parent/);
+});
+
+test('uses the official postMessage message contract and iframe-sized fallback styling', async () => {
+ const [html, source, viteConfig] = await Promise.all([
+ readFile(new URL('../webapp/public/webauthn-connector.html', import.meta.url), 'utf8'),
+ readFile(new URL('../webapp/public/webauthn-connector.js', import.meta.url), 'utf8'),
+ readFile(new URL('../webapp/vite.config.ts', import.meta.url), 'utf8'),
+ ]);
+ assert.match(html, /id="webauthn-button"/);
+ assert.match(html, /min-height:\s*40px/);
+ assert.match(html, /background:\s*#2563eb/);
+ assert.match(source, /post\('info\|ready'\)/);
+ assert.match(source, /post\(`success\|\$\{buildCredentialData\(credential\)\}`\)/);
+ assert.match(source, /post\(`error\|\$\{browserErrorMessage\(error\)\}`\)/);
+ assert.match(source, /event\.data === 'stop'/);
+ assert.match(source, /event\.data === 'start'/);
+ assert.match(viteConfig, /endsWith\('-connector\.html'\)/);
+});
diff --git a/scripts/webauthn-mobile-connector.test.mjs b/scripts/webauthn-mobile-connector.test.mjs
new file mode 100644
index 0000000..4168312
--- /dev/null
+++ b/scripts/webauthn-mobile-connector.test.mjs
@@ -0,0 +1,135 @@
+import assert from 'node:assert/strict';
+import { readFile } from 'node:fs/promises';
+import test from 'node:test';
+import {
+ base64UrlFromBuffer,
+ buildCallbackUrl,
+ buildCredentialData,
+ decodeBase64Utf8,
+ normalizePublicKeyOptions,
+ parseConnectorRequest,
+ resolveMobileCallbackUri,
+} from '../webapp/public/webauthn-mobile-connector.js';
+
+function encodeBase64Utf8(value) {
+ return Buffer.from(value, 'utf8').toString('base64');
+}
+
+function v2Search(payload, extra = '') {
+ return `?data=${encodeURIComponent(encodeBase64Utf8(JSON.stringify(payload)))}&parent=bitwarden%3A__webauthn-callback&v=2${extra}`;
+}
+
+const assertionOptions = {
+ challenge: 'AQID-v8',
+ rpId: 'vault.example.com',
+ timeout: 60000,
+ userVerification: 'preferred',
+ allowCredentials: [{ id: 'BAUGBwg', type: 'public-key', transports: ['internal'] }],
+};
+
+test('parses the current Bitwarden Android V2 connector payload', () => {
+ const request = parseConnectorRequest(v2Search({
+ btnReturnText: 'Return to app', btnText: 'Authenticate', data: JSON.stringify(assertionOptions),
+ headerText: 'Verify your identity', mobile: true,
+ }, '&client=mobile&deeplinkScheme=bitwarden'), 'vault.example.com');
+ assert.equal(request.callbackUri, 'bitwarden://webauthn-callback');
+ assert.equal(request.headerText, 'Verify your identity');
+ assert.equal(request.buttonText, 'Authenticate');
+ assert.equal(request.returnButtonText, 'Return to app');
+ assert.deepEqual(JSON.parse(request.webauthnJson), assertionOptions);
+});
+
+test('uses callbackUri only as a signal and never as the redirect target', () => {
+ const trustedLooking = parseConnectorRequest(v2Search({
+ callbackUri: 'https://bitwarden.eu/webauthn-callback', data: assertionOptions,
+ }).replace('&parent=bitwarden%3A__webauthn-callback', ''));
+ const attacker = parseConnectorRequest(v2Search({
+ callbackUri: 'https://attacker.example/capture', data: assertionOptions,
+ }).replace('&parent=bitwarden%3A__webauthn-callback', ''));
+ assert.equal(trustedLooking.callbackUri, 'bitwarden://webauthn-callback');
+ assert.equal(attacker.callbackUri, 'bitwarden://webauthn-callback');
+});
+
+test('treats any non-HTTPS deeplinkScheme as the fixed Bitwarden custom scheme', () => {
+ const request = parseConnectorRequest(v2Search({ mobile: true, data: assertionOptions }, '&deeplinkScheme=untrusted'));
+ assert.equal(request.callbackUri, 'bitwarden://webauthn-callback');
+});
+
+test('supports Android custom-scheme and official HTTPS App Link callbacks', () => {
+ const payload = { mobile: true, data: assertionOptions };
+ const custom = parseConnectorRequest(v2Search(payload, '&client=mobile&deeplinkScheme=bitwarden'));
+ const eu = parseConnectorRequest(v2Search(payload, '&client=mobile&deeplinkScheme=https'), 'vault.bitwarden.eu');
+ const selfHosted = parseConnectorRequest(v2Search(payload, '&client=mobile&deeplinkScheme=https'), 'vault.example.com');
+ assert.equal(custom.callbackUri, 'bitwarden://webauthn-callback');
+ assert.equal(eu.callbackUri, 'https://bitwarden.eu/webauthn-callback');
+ assert.equal(selfHosted.callbackUri, 'https://bitwarden.com/webauthn-callback');
+});
+
+test('supports V1 mobile requests and requires a recognized mobile signal', () => {
+ const encoded = encodeURIComponent(encodeBase64Utf8(JSON.stringify(assertionOptions)));
+ assert.equal(parseConnectorRequest(`?data=${encoded}&v=1&client=mobile`).callbackUri, 'bitwarden://webauthn-callback');
+ assert.equal(resolveMobileCallbackUri({ payload: {}, hostname: 'vault.example.com' }), null);
+ assert.throws(() => parseConnectorRequest(`?data=${encoded}&v=1`), /return target/i);
+});
+
+test('decodes UTF-8 and normalizes WebAuthn binary fields without mutation', () => {
+ assert.equal(decodeBase64Utf8(encodeBase64Utf8('验证身份')), '验证身份');
+ const original = structuredClone(assertionOptions);
+ const normalized = normalizePublicKeyOptions(original);
+ assert.deepEqual(Array.from(normalized.challenge), [1, 2, 3, 250, 255]);
+ assert.deepEqual(Array.from(normalized.allowCredentials[0].id), [4, 5, 6, 7, 8]);
+ assert.deepEqual(original, assertionOptions);
+});
+
+test('serializes the exact assertion shape emitted by Bitwarden common-webauthn', () => {
+ const serialized = JSON.parse(buildCredentialData({
+ id: 'credential-id', rawId: Uint8Array.from([1, 2, 255]).buffer, type: 'public-key',
+ getClientExtensionResults: () => ({ appid: false }),
+ response: {
+ authenticatorData: Uint8Array.from([3, 4]).buffer,
+ clientDataJSON: Uint8Array.from([5, 6]).buffer,
+ signature: Uint8Array.from([7, 8]).buffer,
+ userHandle: Uint8Array.from([9, 10]).buffer,
+ },
+ }));
+ assert.deepEqual(serialized, {
+ id: 'credential-id',
+ rawId: 'AQL_',
+ type: 'public-key',
+ extensions: { appid: false },
+ response: { authenticatorData: 'AwQ', clientDataJson: 'BQY', signature: 'Bwg' },
+ });
+ assert.equal(base64UrlFromBuffer(Uint8Array.from([251, 255])), '-_8');
+});
+
+test('encodes success and error callbacks safely', () => {
+ assert.equal(buildCallbackUrl('bitwarden://webauthn-callback', 'data', '{"id":"a+b"}'), 'bitwarden://webauthn-callback?data=%7B%22id%22%3A%22a%2Bb%22%7D');
+ assert.equal(buildCallbackUrl('bitwarden://webauthn-callback?source=nodewarden', 'error', 'Not allowed'), 'bitwarden://webauthn-callback?source=nodewarden&error=Not%20allowed');
+});
+
+test('HTML matches the fallback connector visual structure', async () => {
+ const html = await readFile(new URL('../webapp/public/webauthn-mobile-connector.html', import.meta.url), 'utf8');
+ assert.match(html, /id="webauthn-header"/);
+ assert.match(html, /id="webauthn-button"/);
+ assert.match(html, /class="connector-card"/);
+ assert.match(html, /class="brand"/);
+ assert.match(html, /class="form"/);
+ assert.match(html, /class="msg"/);
+ assert.match(html, /src="\/nodewarden-logo\.svg"/);
+ assert.match(html, /src="\/webauthn-mobile-connector\.js"/);
+ assert.match(html, /default-src 'none'/);
+});
+
+test('runtime uses Bitwarden-compatible replacement navigation', async () => {
+ const source = await readFile(new URL('../webapp/public/webauthn-mobile-connector.js', import.meta.url), 'utf8');
+ assert.match(source, /window\.location\.replace\(uri\)/);
+ assert.doesNotMatch(source, /location\.assign/);
+ assert.doesNotMatch(source, /safeCallbackFromPayload/);
+});
+
+test('Service Worker keeps connector navigations out of the SPA shell', async () => {
+ const config = await readFile(new URL('../webapp/vite.config.ts', import.meta.url), 'utf8');
+ assert.match(config, /url\.pathname\.endsWith\('-connector\.html'\)/);
+ assert.match(config, /connectorNavigation\(request\)/);
+ assert.match(config, /WebAuthn connector is unavailable while offline/);
+});
diff --git a/shared/app-version.ts b/shared/app-version.ts
index cb8a81f..afa943c 100644
--- a/shared/app-version.ts
+++ b/shared/app-version.ts
@@ -1 +1 @@
-export const APP_VERSION = '1.6.1';
+export const APP_VERSION = '1.8.0';
diff --git a/shared/backup-schema.ts b/shared/backup-schema.ts
index 2478a6f..f1fb591 100644
--- a/shared/backup-schema.ts
+++ b/shared/backup-schema.ts
@@ -9,7 +9,8 @@
export const BACKUP_DEFAULT_TIMEZONE = 'UTC';
export const BACKUP_DEFAULT_RETENTION_COUNT = 30;
export const BACKUP_DEFAULT_S3_REGION = 'auto';
-export const BACKUP_DEFAULT_REMOTE_PATH = 'nodewarden';
+export const BACKUP_DEFAULT_S3_ROOT_PATH = '';
+export const BACKUP_DEFAULT_WEBDAV_REMOTE_PATH = 'nodewarden';
export const BACKUP_DEFAULT_INTERVAL_HOURS = 24;
export const BACKUP_DEFAULT_START_TIME = '03:00';
@@ -109,14 +110,14 @@ export function createDefaultBackupDestinationConfig(type: BackupDestinationType
region: BACKUP_DEFAULT_S3_REGION,
accessKeyId: '',
secretAccessKey: '',
- rootPath: BACKUP_DEFAULT_REMOTE_PATH,
+ rootPath: BACKUP_DEFAULT_S3_ROOT_PATH,
};
}
return {
baseUrl: '',
username: '',
password: '',
- remotePath: BACKUP_DEFAULT_REMOTE_PATH,
+ remotePath: BACKUP_DEFAULT_WEBDAV_REMOTE_PATH,
};
}
diff --git a/src/config-response.ts b/src/config-response.ts
new file mode 100644
index 0000000..df7631e
--- /dev/null
+++ b/src/config-response.ts
@@ -0,0 +1,53 @@
+import { LIMITS } from './config/limits';
+
+function buildIconServiceTemplate(origin: string): string {
+ return `${origin}/icons/{}/icon.png`;
+}
+
+function buildIconServiceCsp(origin: string): string {
+ return `img-src 'self' data: ${origin}`;
+}
+
+export function buildConfigResponse(origin: string) {
+ const fillAssistBase = `${origin}/fill-assist/`;
+ return {
+ version: LIMITS.compatibility.bitwardenServerVersion,
+ gitHash: 'nodewarden',
+ server: null,
+ environment: {
+ cloudRegion: 'self-hosted',
+ vault: origin,
+ api: origin + '/api',
+ identity: origin + '/identity',
+ notifications: origin + '/notifications',
+ icons: origin,
+ sso: '',
+ fillAssistRules: fillAssistBase,
+ },
+ push: {
+ pushTechnology: 0,
+ vapidPublicKey: null,
+ },
+ communication: null,
+ settings: {
+ disableUserRegistration: false,
+ suppressOnboardingInterstitials: false,
+ },
+ _icon_service_url: buildIconServiceTemplate(origin),
+ _icon_service_csp: buildIconServiceCsp(origin),
+ featureStates: {
+ 'cipher-key-encryption': LIMITS.compatibility.cipherKeyEncryptionFeatureEnabled,
+ 'desktop-ui-settings-dialog': true,
+ 'duo-redirect': true,
+ 'email-verification': true,
+ 'fill-assist-targeting-rules': true,
+ 'pm-19051-send-email-verification': false,
+ 'pm-19148-innovation-archive': true,
+ 'pm-4516-devices-add-last-activity-date': true,
+ 'pm-30529-webauthn-related-origins': true,
+ 'unauth-ui-refresh': true,
+ 'web-push': false,
+ },
+ object: 'config',
+ };
+}
diff --git a/src/config/limits.ts b/src/config/limits.ts
index 2e40bcc..1d855e1 100644
--- a/src/config/limits.ts
+++ b/src/config/limits.ts
@@ -3,12 +3,14 @@
// Access token lifetime in seconds.
// 访问令牌有效期(秒)。
accessTokenTtlSeconds: 7200,
- // Refresh token lifetime in milliseconds.
- // 刷新令牌有效期(毫秒)。
- refreshTokenTtlMs: 365 * 24 * 60 * 60 * 1000,
- // Grace window for previous refresh token after rotation (ms).
- // 刷新令牌轮换后的旧令牌宽限窗口(毫秒)。
- refreshTokenOverlapGraceMs: 30 * 60 * 1000,
+ // Refresh sessions use a reusable opaque token with a sliding idle lifetime.
+ // 刷新会话使用可复用的随机令牌,并按客户端采用滑动空闲期限。
+ refreshTokenWebSlidingTtlMs: 30 * 24 * 60 * 60 * 1000,
+ refreshTokenDefaultSlidingTtlMs: 30 * 24 * 60 * 60 * 1000,
+ refreshTokenMobileSlidingTtlMs: 90 * 24 * 60 * 60 * 1000,
+ // Hard upper bound for one login session, regardless of sliding refreshes.
+ // 单次登录会话的绝对最长寿命,不因滑动续期突破该上限。
+ refreshTokenAbsoluteTtlMs: 365 * 24 * 60 * 60 * 1000,
// Refresh token random byte length.
// 刷新令牌随机字节长度。
refreshTokenRandomBytes: 32,
@@ -62,6 +64,12 @@
// Refresh-token grant budget per IP per minute.
// refresh_token 授权每 IP 每分钟请求配额。
refreshTokenRequestsPerMinute: 30,
+ // Coarser IP budget; the per-session budget above remains the primary guard.
+ // 更宽松的 IP 总预算;主要保护仍由每个 refresh session 的预算承担。
+ refreshTokenRequestsPerIpMinute: 300,
+ // Passwordless/auth-request creation budget per IP/email/device per minute.
+ // 免密/设备审批请求创建接口每 IP/邮箱/设备每分钟配额。
+ authRequestRequestsPerMinute: 5,
// Fixed window size for API rate limiting in seconds.
// API 限流固定窗口大小(秒)。
apiWindowSeconds: 60,
@@ -148,7 +156,9 @@
compatibility: {
// Single source of truth for /config.version and /api/version.
// /config.version 与 /api/version 的统一版本号来源。
- bitwardenServerVersion: '2026.4.1',
+ // Vaultwarden 1.37.0 advertises 2026.6.0 after aligning its API response
+ // with the response contract required by Bitwarden 2026.7.x clients.
+ bitwardenServerVersion: '2026.6.0',
// Official 2026.4.x clients need this flag to receive and use cipher.key.
// Hiding existing item keys makes item-key encrypted vault data unreadable.
// 官方 2026.4.x 客户端需要该开关来接收并使用 cipher.key。
@@ -156,3 +166,10 @@
cipherKeyEncryptionFeatureEnabled: true,
},
} as const;
+
+export function getRefreshTokenSlidingTtlMs(clientType?: string | null): number {
+ const normalized = String(clientType || '').trim().toLowerCase();
+ if (normalized === 'web') return LIMITS.auth.refreshTokenWebSlidingTtlMs;
+ if (normalized === 'mobile') return LIMITS.auth.refreshTokenMobileSlidingTtlMs;
+ return LIMITS.auth.refreshTokenDefaultSlidingTtlMs;
+}
diff --git a/src/durable/backup-transfer-runner.ts b/src/durable/backup-transfer-runner.ts
index 5c1d9ee..35b1d52 100644
--- a/src/durable/backup-transfer-runner.ts
+++ b/src/durable/backup-transfer-runner.ts
@@ -19,7 +19,7 @@ import {
executeConfiguredBackup,
importAndAuditRemoteBackupFile,
} from '../handlers/backup';
-import { verifyBackupArchiveFileNameChecksum } from '../services/backup-archive';
+import { isSafeBackupAttachmentBlobName, verifyBackupArchiveFileNameChecksum } from '../services/backup-archive';
import { zipSync } from 'fflate';
const BACKUP_JOB_STATE_KEY = 'backup.job.state.v1';
@@ -209,6 +209,7 @@ export class BackupTransferRunner {
}
let completed = 0;
+ const failures: Array<{ destinationId: string; error: string }> = [];
try {
await this.touchJob(token);
const storage = new StorageService(this.env.DB);
@@ -230,21 +231,30 @@ export class BackupTransferRunner {
scanStartMs = now.getTime();
for (const destination of dueDestinations) {
await this.touchJob(token);
- await executeConfiguredBackup(
- this.env,
- storage,
- null,
- 'scheduled',
- destination.id,
- () => this.touchJob(token)
- );
- completed += 1;
+ try {
+ await executeConfiguredBackup(
+ this.env,
+ storage,
+ null,
+ 'scheduled',
+ destination.id,
+ () => this.touchJob(token)
+ );
+ completed += 1;
+ } catch (error) {
+ failures.push({
+ destinationId: destination.id,
+ error: error instanceof Error ? error.message : 'Scheduled backup failed',
+ });
+ }
}
}
return new Response(JSON.stringify({
ok: true,
completed,
+ failed: failures.length,
+ failures,
}), {
status: 200,
headers: {
@@ -318,7 +328,8 @@ export class BackupTransferRunner {
replaceExisting,
!checksumOk,
body.auditMetadata || null,
- targetDeviceIdentifier
+ targetDeviceIdentifier,
+ () => this.touchJob(token)
);
return new Response(JSON.stringify(result.result), {
@@ -361,7 +372,7 @@ export class BackupTransferRunner {
return badRequest('Remote attachment download payload is invalid');
}
const blobName = String(body?.blobName || '').trim();
- if (!body?.destination || !blobName) {
+ if (!body?.destination || !isSafeBackupAttachmentBlobName(blobName)) {
return badRequest('Remote attachment download payload is invalid');
}
const file = await downloadRemoteBackupFile(body.destination, `attachments/${blobName}`).catch(() => null);
@@ -387,7 +398,7 @@ export class BackupTransferRunner {
const blobNames = Array.from(new Set(
(Array.isArray(body?.blobNames) ? body.blobNames : [])
.map((blobName) => String(blobName || '').trim())
- .filter(Boolean)
+ .filter(isSafeBackupAttachmentBlobName)
));
if (!body?.destination || !blobNames.length || blobNames.length > 40) {
return badRequest('Remote attachment batch download payload is invalid');
@@ -435,7 +446,7 @@ export class BackupTransferRunner {
for (const attachment of body.attachments) {
const blobName = String(attachment?.blobName || '').trim();
- if (!blobName) {
+ if (!isSafeBackupAttachmentBlobName(blobName)) {
return badRequest('Attachment chunk payload is invalid');
}
diff --git a/src/durable/notifications-hub.ts b/src/durable/notifications-hub.ts
index fa62ca0..f367bb2 100644
--- a/src/durable/notifications-hub.ts
+++ b/src/durable/notifications-hub.ts
@@ -1,13 +1,24 @@
import { DurableObject, waitUntil } from 'cloudflare:workers';
import type { Env } from '../types';
+import { notifyMobilePush } from '../services/push-relay';
const SIGNALR_RECORD_SEPARATOR = 0x1e;
const SIGNALR_HANDSHAKE_ACK = new Uint8Array([0x7b, 0x7d, SIGNALR_RECORD_SEPARATOR]);
+const SIGNALR_UPDATE_TYPE_SYNC_CIPHER_UPDATE = 0;
+const SIGNALR_UPDATE_TYPE_SYNC_CIPHER_CREATE = 1;
+const SIGNALR_UPDATE_TYPE_SYNC_FOLDER_DELETE = 3;
+const SIGNALR_UPDATE_TYPE_SYNC_CIPHERS = 4;
const SIGNALR_UPDATE_TYPE_SYNC_VAULT = 5;
+const SIGNALR_UPDATE_TYPE_SYNC_FOLDER_CREATE = 7;
+const SIGNALR_UPDATE_TYPE_SYNC_FOLDER_UPDATE = 8;
+const SIGNALR_UPDATE_TYPE_SYNC_CIPHER_DELETE = 9;
const SIGNALR_UPDATE_TYPE_LOG_OUT = 11;
-const SIGNALR_UPDATE_TYPE_BACKUP_RESTORE_PROGRESS = 13;
+const SIGNALR_UPDATE_TYPE_SYNC_SEND_CREATE = 12;
+const SIGNALR_UPDATE_TYPE_SYNC_SEND_UPDATE = 13;
+const SIGNALR_UPDATE_TYPE_SYNC_SEND_DELETE = 14;
const SIGNALR_UPDATE_TYPE_AUTH_REQUEST = 15;
const SIGNALR_UPDATE_TYPE_AUTH_REQUEST_RESPONSE = 16;
+const SIGNALR_UPDATE_TYPE_BACKUP_RESTORE_PROGRESS = 102;
type HubProtocol = 'json' | 'messagepack';
type HubKind = 'user' | 'anonymous-auth-request';
@@ -164,7 +175,7 @@ function buildSignalRMessagePackInvocation(
target: string = 'ReceiveMessage'
): Uint8Array {
// SignalR MessagePack hub protocol uses an array-based invocation shape:
- // [type, headers, invocationId, target, arguments]
+ // [type, headers, invocationId, target, arguments, streamIds]
const encodedPayload = encodeMsgPack([
1,
{},
@@ -177,6 +188,7 @@ function buildSignalRMessagePackInvocation(
Payload: messagePayload,
},
],
+ [],
]);
return frameSignalRBinary(encodedPayload);
}
@@ -207,7 +219,9 @@ export class NotificationsHub extends DurableObject {
const revisionDate = String(body?.revisionDate || '').trim() || new Date().toISOString();
const userId = String(request.headers.get('X-NodeWarden-UserId') || body?.userId || '').trim();
const contextId = String(body?.contextId || '').trim() || null;
- const updateType = Number(body?.updateType || SIGNALR_UPDATE_TYPE_SYNC_VAULT) || SIGNALR_UPDATE_TYPE_SYNC_VAULT;
+ const rawUpdateType = body?.updateType;
+ const parsedUpdateType = typeof rawUpdateType === 'number' ? rawUpdateType : Number(rawUpdateType);
+ const updateType = Number.isFinite(parsedUpdateType) ? parsedUpdateType : SIGNALR_UPDATE_TYPE_SYNC_VAULT;
const targetDeviceIdentifier = String(body?.targetDeviceIdentifier || '').trim() || null;
const payload = body?.payload && typeof body.payload === 'object'
? body.payload
@@ -422,6 +436,243 @@ export function notifyUserVaultSync(
waitUntil(notifyUserUpdate(env, userId, SIGNALR_UPDATE_TYPE_SYNC_VAULT, revisionDate, contextId ?? null, null));
}
+export function notifyUserCiphersSync(
+ env: Env,
+ userId: string,
+ revisionDate: string,
+ contextId?: string | null
+): void {
+ waitUntil(notifyUserUpdate(env, userId, SIGNALR_UPDATE_TYPE_SYNC_CIPHERS, revisionDate, contextId ?? null, null));
+}
+
+export function notifyUserCipherCreate(
+ env: Env,
+ payload: {
+ userId: string;
+ cipherId: string;
+ revisionDate: string;
+ organizationId?: string | null;
+ collectionIds?: string[] | null;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_CIPHER_CREATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.cipherId,
+ OrganizationId: payload.organizationId ?? null,
+ CollectionIds: Array.isArray(payload.collectionIds) ? payload.collectionIds : null,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserCipherUpdate(
+ env: Env,
+ payload: {
+ userId: string;
+ cipherId: string;
+ revisionDate: string;
+ organizationId?: string | null;
+ collectionIds?: string[] | null;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_CIPHER_UPDATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.cipherId,
+ OrganizationId: payload.organizationId ?? null,
+ CollectionIds: Array.isArray(payload.collectionIds) ? payload.collectionIds : null,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserCipherDelete(
+ env: Env,
+ payload: {
+ userId: string;
+ cipherId: string;
+ revisionDate: string;
+ organizationId?: string | null;
+ collectionIds?: string[] | null;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_CIPHER_DELETE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.cipherId,
+ OrganizationId: payload.organizationId ?? null,
+ CollectionIds: Array.isArray(payload.collectionIds) ? payload.collectionIds : null,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserFolderCreate(
+ env: Env,
+ payload: {
+ userId: string;
+ folderId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_FOLDER_CREATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.folderId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserFolderUpdate(
+ env: Env,
+ payload: {
+ userId: string;
+ folderId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_FOLDER_UPDATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.folderId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserFolderDelete(
+ env: Env,
+ payload: {
+ userId: string;
+ folderId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_FOLDER_DELETE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.folderId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserSendCreate(
+ env: Env,
+ payload: {
+ userId: string;
+ sendId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_SEND_CREATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.sendId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserSendUpdate(
+ env: Env,
+ payload: {
+ userId: string;
+ sendId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_SEND_UPDATE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.sendId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
+export function notifyUserSendDelete(
+ env: Env,
+ payload: {
+ userId: string;
+ sendId: string;
+ revisionDate: string;
+ contextId?: string | null;
+ }
+): void {
+ waitUntil(notifyUserUpdate(
+ env,
+ payload.userId,
+ SIGNALR_UPDATE_TYPE_SYNC_SEND_DELETE,
+ payload.revisionDate,
+ payload.contextId ?? null,
+ null,
+ {
+ UserId: payload.userId,
+ Id: payload.sendId,
+ RevisionDate: payload.revisionDate,
+ }
+ ));
+}
+
export function notifyUserLogout(
env: Env,
userId: string,
@@ -517,6 +768,16 @@ async function notifyUserUpdate(
},
}),
});
+ await notifyMobilePush(env, {
+ userId,
+ updateType,
+ revisionDate,
+ contextId,
+ payload: payloadOverride || {
+ UserId: userId,
+ Date: revisionDate,
+ },
+ });
} catch (error) {
console.error('Failed to broadcast realtime notification:', error);
}
diff --git a/src/handlers/account-passkeys.ts b/src/handlers/account-passkeys.ts
index 321c7b5..b2ab005 100644
--- a/src/handlers/account-passkeys.ts
+++ b/src/handlers/account-passkeys.ts
@@ -9,7 +9,7 @@ import { StorageService } from '../services/storage';
import { AuthService } from '../services/auth';
import { errorResponse, identityErrorResponse, jsonResponse } from '../utils/response';
import { generateUUID } from '../utils/uuid';
-import { bytesToBase64Url } from '../utils/passkey';
+import { bytesToBase64Url, parseClientDataJSON } from '../utils/passkey';
import {
accountPasskeyCredentialToResponse,
accountPasskeyPrfStatus,
@@ -29,8 +29,10 @@ import {
verifyAccountPasskeyToken,
} from '../utils/account-passkeys';
import { auditRequestMetadata, safeWriteAuditEvent } from '../services/audit-events';
+import { createRecoveryCode } from '../utils/recovery-code';
const MAX_ACCOUNT_PASSKEYS = 5;
+const MAX_TWO_FACTOR_PASSKEYS = 5;
function parseBodyObject(body: unknown): Record {
return body && typeof body === 'object' ? body as Record : {};
@@ -81,6 +83,43 @@ function hasCompletePrfKeySet(body: Record): boolean {
return !!(body.encryptedUserKey && body.encryptedPublicKey && body.encryptedPrivateKey);
}
+function twoFactorWebAuthnResponse(credentials: AccountPasskeyCredential[]): Record {
+ return {
+ Enabled: credentials.length > 0,
+ enabled: credentials.length > 0,
+ Keys: credentials.map((credential, index) => ({
+ Id: index + 1,
+ id: index + 1,
+ Name: credential.name,
+ name: credential.name,
+ Migrated: false,
+ migrated: false,
+ })),
+ keys: credentials.map((credential, index) => ({
+ Id: index + 1,
+ id: index + 1,
+ Name: credential.name,
+ name: credential.name,
+ Migrated: false,
+ migrated: false,
+ })),
+ Object: 'twoFactorWebAuthn',
+ object: 'twoFactorWebAuthn',
+ };
+}
+
+function readRegistrationChallenge(response: ReturnType): string | null {
+ if (!response) return null;
+ const clientData = parseClientDataJSON(response.response.clientDataJSON);
+ return String(clientData?.challenge || '').trim() || null;
+}
+
+function readAuthenticationChallenge(response: ReturnType): string | null {
+ if (!response) return null;
+ const clientData = parseClientDataJSON(response.response.clientDataJSON);
+ return String(clientData?.challenge || '').trim() || null;
+}
+
function readPrfKeySet(body: Record): {
encryptedUserKey: string | null;
encryptedPublicKey: string | null;
@@ -176,6 +215,9 @@ export async function assertAccountPasskeyCredential(
if (payload.userId && credential.userId !== payload.userId) {
throw new Error('Passkey does not belong to this user');
}
+ if (credential.purpose !== 'login') {
+ throw new Error('Passkey is not registered for login');
+ }
const userHandleUserId = userHandleToUserId(response.response.userHandle);
const resolvedUserId = payload.userId || userHandleUserId || credential.userId;
@@ -225,6 +267,268 @@ export async function handleGetAccountPasskeyCredentials(request: Request, env:
});
}
+export async function buildTwoFactorPasskeyAssertionOptions(
+ request: Request,
+ env: Env,
+ storage: StorageService,
+ user: User
+): Promise | null> {
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(user.id, 'twoFactor');
+ if (!credentials.length) return null;
+
+ const { rpId } = getAccountPasskeyRpConfig(request, env);
+ const options = await generateAuthenticationOptions({
+ rpID: rpId,
+ allowCredentials: credentials.map((credential) => ({
+ id: credential.credentialId,
+ transports: (credential.transports || undefined) as any,
+ })),
+ userVerification: 'discouraged',
+ timeout: 60000,
+ });
+ await saveChallenge(storage, 'TwoFactorAuthentication', options.challenge, user.id);
+ return options as unknown as Record;
+}
+
+export async function assertTwoFactorPasskeyCredential(
+ request: Request,
+ env: Env,
+ storage: StorageService,
+ user: User,
+ deviceResponse: unknown
+): Promise {
+ const response = normalizeAuthenticationResponse(deviceResponse);
+ if (!response) {
+ throw new Error('Invalid passkey assertion response');
+ }
+
+ const credential = await storage.getAccountPasskeyCredentialByCredentialId(response.rawId);
+ if (!credential || credential.userId !== user.id || credential.purpose !== 'twoFactor') {
+ throw new Error('Passkey is not registered for two-step login');
+ }
+
+ const challenge = readAuthenticationChallenge(response);
+ if (!challenge) {
+ throw new Error('Passkey assertion challenge is missing');
+ }
+ const consumed = await storage.consumeAccountPasskeyChallenge(
+ await sha256Base64Url(challenge),
+ 'TwoFactorAuthentication',
+ user.id,
+ Date.now()
+ );
+ if (!consumed) {
+ throw new Error('Passkey challenge has expired or was already used');
+ }
+
+ const { origins, rpId } = getAccountPasskeyRpConfig(request, env);
+ const verification = await verifyAuthenticationResponse({
+ response,
+ expectedChallenge: challenge,
+ expectedOrigin: origins,
+ expectedRPID: rpId,
+ credential: toSimpleWebAuthnCredential(credential),
+ requireUserVerification: false,
+ });
+ if (!verification.verified) {
+ throw new Error('Passkey assertion could not be verified');
+ }
+
+ await storage.updateAccountPasskeyCounter(
+ credential.userId,
+ credential.credentialId,
+ verification.authenticationInfo.newCounter,
+ new Date().toISOString()
+ );
+ credential.counter = verification.authenticationInfo.newCounter;
+ return credential;
+}
+
+export async function handleGetTwoFactorWebAuthn(request: Request, env: Env, userId: string, user: User): Promise {
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+ if (!(await verifyUserSecret(env, user, body))) {
+ return errorResponse('User verification failed.', 400);
+ }
+
+ const storage = new StorageService(env.DB);
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(userId, 'twoFactor');
+ return jsonResponse(twoFactorWebAuthnResponse(credentials));
+}
+
+export async function handleGetTwoFactorWebAuthnChallenge(request: Request, env: Env, userId: string, user: User): Promise {
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+ if (!(await verifyUserSecret(env, user, body))) {
+ return errorResponse('User verification failed.', 400);
+ }
+
+ const storage = new StorageService(env.DB);
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(userId, 'twoFactor');
+ if (credentials.length >= MAX_TWO_FACTOR_PASSKEYS) {
+ return errorResponse('Maximum WebAuthn credential count reached.', 400);
+ }
+
+ const { rpId, rpName } = getAccountPasskeyRpConfig(request, env);
+ const options = await generateRegistrationOptions({
+ rpID: rpId,
+ rpName,
+ userID: Uint8Array.from(userIdToWebAuthnUserId(user.id)),
+ userName: user.email,
+ userDisplayName: user.name || user.email,
+ attestationType: 'none',
+ timeout: 60000,
+ excludeCredentials: credentials.map((credential) => ({
+ id: credential.credentialId,
+ transports: (credential.transports || undefined) as any,
+ })),
+ authenticatorSelection: {
+ residentKey: 'discouraged',
+ requireResidentKey: false,
+ userVerification: 'discouraged',
+ },
+ });
+ await saveChallenge(storage, 'TwoFactorCreate', options.challenge, userId);
+ return jsonResponse(options);
+}
+
+export async function handlePutTwoFactorWebAuthn(request: Request, env: Env, userId: string, user: User): Promise {
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+ if (!(await verifyUserSecret(env, user, body))) {
+ return errorResponse('User verification failed.', 400);
+ }
+
+ const storage = new StorageService(env.DB);
+ const currentCount = await storage.countAccountPasskeyCredentialsByUserId(userId, 'twoFactor');
+ if (currentCount >= MAX_TWO_FACTOR_PASSKEYS) {
+ return errorResponse('Maximum WebAuthn credential count reached.', 400);
+ }
+
+ const registrationResponse = normalizeRegistrationResponse(body.deviceResponse);
+ if (!registrationResponse) {
+ return errorResponse('Invalid passkey registration response', 400);
+ }
+ const challenge = readRegistrationChallenge(registrationResponse);
+ if (!challenge) {
+ return errorResponse('Passkey challenge is missing', 400);
+ }
+ const consumed = await storage.consumeAccountPasskeyChallenge(
+ await sha256Base64Url(challenge),
+ 'TwoFactorCreate',
+ userId,
+ Date.now()
+ );
+ if (!consumed) {
+ return errorResponse('Passkey challenge has expired or was already used', 400);
+ }
+
+ const { origins, rpId } = getAccountPasskeyRpConfig(request, env);
+ let verification: Awaited>;
+ try {
+ verification = await verifyRegistrationResponse({
+ response: registrationResponse,
+ expectedChallenge: challenge,
+ expectedOrigin: origins,
+ expectedRPID: rpId,
+ requireUserPresence: true,
+ requireUserVerification: false,
+ });
+ } catch {
+ return errorResponse('Passkey registration could not be verified', 400);
+ }
+ if (!verification.verified) {
+ return errorResponse('Passkey registration could not be verified', 400);
+ }
+
+ const existing = await storage.getAccountPasskeyCredentialByCredentialId(verification.registrationInfo.credential.id);
+ if (existing) {
+ return errorResponse('Passkey is already registered', 409);
+ }
+
+ const now = new Date().toISOString();
+ const transports = normalizeTransports(registrationResponse.response.transports);
+ await storage.saveAccountPasskeyCredential({
+ id: generateUUID(),
+ userId,
+ purpose: 'twoFactor',
+ name: normalizeAccountPasskeyName(body.name || `Passkey ${currentCount + 1}`),
+ publicKey: bytesToBase64Url(verification.registrationInfo.credential.publicKey),
+ credentialId: verification.registrationInfo.credential.id,
+ counter: verification.registrationInfo.credential.counter,
+ type: verification.registrationInfo.credentialType || 'public-key',
+ aaGuid: verification.registrationInfo.aaguid || null,
+ transports,
+ encryptedUserKey: null,
+ encryptedPublicKey: null,
+ encryptedPrivateKey: null,
+ supportsPrf: false,
+ createdAt: now,
+ updatedAt: now,
+ });
+
+ if (!user.totpRecoveryCode) {
+ user.totpRecoveryCode = createRecoveryCode();
+ user.updatedAt = now;
+ await storage.saveUser(user);
+ }
+ await storage.deleteRefreshTokensByUserId(userId);
+ AuthService.invalidateUserCache(userId);
+
+ await safeWriteAuditEvent(env, {
+ actorUserId: userId,
+ action: 'account.webauthn_2fa.enable',
+ category: 'security',
+ level: 'security',
+ targetType: 'accountPasskey',
+ targetId: null,
+ metadata: auditRequestMetadata(request),
+ });
+
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(userId, 'twoFactor');
+ return jsonResponse(twoFactorWebAuthnResponse(credentials));
+}
+
+export async function handleDeleteTwoFactorWebAuthn(request: Request, env: Env, userId: string, user: User): Promise {
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+ if (!(await verifyUserSecret(env, user, body))) {
+ return errorResponse('User verification failed.', 400);
+ }
+
+ const requestedId = Number(body.id ?? body.Id);
+ if (!Number.isInteger(requestedId) || requestedId <= 0) {
+ return errorResponse('Invalid key id', 400);
+ }
+
+ const storage = new StorageService(env.DB);
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(userId, 'twoFactor');
+ if (credentials.length < 2) {
+ return errorResponse('Unable to delete WebAuthn credential.', 400);
+ }
+ const credential = credentials[requestedId - 1];
+ if (!credential) {
+ return errorResponse('Unable to delete WebAuthn credential.', 400);
+ }
+
+ const deleted = await storage.deleteAccountPasskeyCredential(userId, credential.id, 'twoFactor');
+ if (!deleted) return errorResponse('Unable to delete WebAuthn credential.', 400);
+ await storage.deleteRefreshTokensByUserId(userId);
+ AuthService.invalidateUserCache(userId);
+
+ await safeWriteAuditEvent(env, {
+ actorUserId: userId,
+ action: 'account.webauthn_2fa.delete',
+ category: 'security',
+ level: 'security',
+ targetType: 'accountPasskey',
+ targetId: credential.id,
+ metadata: auditRequestMetadata(request),
+ });
+
+ return jsonResponse(twoFactorWebAuthnResponse(await storage.getAccountPasskeyCredentialsByUserId(userId, 'twoFactor')));
+}
+
export async function handleGetAccountPasskeyAttestationOptions(request: Request, env: Env, userId: string, user: User): Promise {
const body = await readJsonBody(request);
if (!body) return errorResponse('Invalid request payload', 400);
@@ -380,6 +684,7 @@ export async function handleCreateAccountPasskeyCredential(request: Request, env
const credential: AccountPasskeyCredential = {
id: generateUUID(),
userId,
+ purpose: 'login',
name: normalizeAccountPasskeyName(body.name),
publicKey: bytesToBase64Url(verification.registrationInfo.credential.publicKey),
credentialId: verification.registrationInfo.credential.id,
diff --git a/src/handlers/accounts.ts b/src/handlers/accounts.ts
index e5a5fdc..89860e4 100644
--- a/src/handlers/accounts.ts
+++ b/src/handlers/accounts.ts
@@ -1,4 +1,4 @@
-import { Env, User, ProfileResponse, DEFAULT_DEV_SECRET } from '../types';
+import { Env, User } from '../types';
import { StorageService } from '../services/storage';
import { AuthService } from '../services/auth';
import { RateLimitService, getClientIdentifier } from '../services/ratelimit';
@@ -6,11 +6,21 @@ import { auditRequestMetadata, writeAuditEvent, safeWriteAuditEvent } from '../s
import { jsonResponse, errorResponse } from '../utils/response';
import { generateUUID } from '../utils/uuid';
import { LIMITS } from '../config/limits';
-import { isTotpEnabled, verifyTotpToken } from '../utils/totp';
+import { isStoredApiKeyHash } from '../utils/api-key';
+import { findMatchingTotpCounter, isTotpEnabled } from '../utils/totp';
import { createRecoveryCode, recoveryCodeEquals } from '../utils/recovery-code';
import { buildAccountKeys } from '../utils/user-decryption';
+import { buildProfileResponse } from '../utils/profile-response';
+import { isYubiKeyEnabled, isYubiKeyPublicId, requestYubicoApiCredentials, verifyYubicoOtp, yubiKeyPublicIdFromOtp } from '../utils/yubico-otp';
+import {
+ getYubicoCredentials,
+ initializeYubicoCredentialsOnce,
+ replaceYubicoCredentials,
+} from '../services/yubico-config';
const TWO_FACTOR_PROVIDER_AUTHENTICATOR = 0;
+const TWO_FACTOR_PROVIDER_YUBIKEY = 3;
+const TWO_FACTOR_PROVIDER_WEBAUTHN = 7;
const TOTP_USER_VERIFICATION_TOKEN_TTL_MS = 10 * 60 * 1000;
const TOTP_BASE32_ALPHABET = 'ABCDEFGHIJKLMNOPQRSTUVWXYZ234567';
@@ -35,6 +45,9 @@ function looksLikeEncString(value: string): boolean {
*/
function validateKdfParams(kdfType: number | undefined, kdfIterations: number | undefined, kdfMemory?: number | undefined, kdfParallelism?: number | undefined): string | null {
const type = kdfType ?? 0;
+ if (type !== 0 && type !== 1) {
+ return 'KDF type must be PBKDF2-SHA256 or Argon2id';
+ }
if (type === 0) {
// PBKDF2-SHA256: minimum 100 000 iterations
if (typeof kdfIterations === 'number' && kdfIterations < 100_000) {
@@ -148,10 +161,9 @@ function normalizeMasterPasswordHint(input: string | null | undefined): string |
return normalized ? normalized : null;
}
-function jwtSecretUnsafeReason(env: Env): 'missing' | 'default' | 'too_short' | null {
+function jwtSecretUnsafeReason(env: Env): 'missing' | 'too_short' | null {
const secret = (env.JWT_SECRET || '').trim();
if (!secret) return 'missing';
- if (secret === DEFAULT_DEV_SECRET) return 'default';
if (secret.length < LIMITS.auth.jwtSecretMinLength) return 'too_short';
return null;
}
@@ -174,6 +186,28 @@ function readBodyString(body: Record, names: string[]): string
return '';
}
+function readNestedString(source: unknown, path: string[]): string {
+ let current = source;
+ for (const key of path) {
+ if (!current || typeof current !== 'object') return '';
+ current = (current as Record)[key];
+ }
+ return typeof current === 'string' ? current : '';
+}
+
+function readNestedNumber(source: unknown, path: string[]): number | undefined {
+ let current = source;
+ for (const key of path) {
+ if (!current || typeof current !== 'object') return undefined;
+ current = (current as Record)[key];
+ }
+ return typeof current === 'number' ? current : undefined;
+}
+
+function isRecord(value: unknown): value is Record {
+ return !!value && typeof value === 'object' && !Array.isArray(value);
+}
+
async function readRequestBody(request: Request): Promise> {
const contentType = request.headers.get('content-type') || '';
if (contentType.includes('application/x-www-form-urlencoded')) {
@@ -183,34 +217,32 @@ async function readRequestBody(request: Request): Promise {
+ return {
+ minComplexity: 0,
+ minLength: 0,
+ requireUpper: false,
+ requireLower: false,
+ requireNumbers: false,
+ requireSpecial: false,
+ enforceOnLogin: false,
+ object: 'masterPasswordPolicy',
+ };
+}
+
+function keysResponse(user: User): Record {
const accountKeys = buildAccountKeys(user);
return {
- id: user.id,
- name: user.name,
- email: user.email,
- emailVerified: true,
- premium: true,
- premiumFromOrganization: false,
- usesKeyConnector: false,
- masterPasswordHint: user.masterPasswordHint,
- culture: 'en-US',
- twoFactorEnabled: !!user.totpSecret,
+ Key: user.key,
+ PublicKey: user.publicKey ?? '',
+ PrivateKey: user.privateKey ?? '',
+ AccountKeys: accountKeys,
+ Object: 'keys',
key: user.key,
- privateKey: user.privateKey,
+ publicKey: user.publicKey ?? '',
+ privateKey: user.privateKey ?? '',
accountKeys,
- securityStamp: user.securityStamp || user.id,
- organizations: [],
- providers: [],
- providerOrganizations: [],
- forcePasswordReset: false,
- avatarColor: null,
- creationDate: user.createdAt,
- verifyDevices: user.verifyDevices,
- role: user.role,
- status: user.status,
- object: 'profile',
+ object: 'keys',
};
}
@@ -224,9 +256,7 @@ export async function handleRegister(request: Request, env: Env): Promise {
const storage = new StorageService(env.DB);
const auth = new AuthService(env);
const user = await storage.getUserById(userId);
if (!user) return errorResponse('User not found', 404);
- let body: {
- secret?: string;
- masterPasswordHash?: string;
- verifyDevices?: boolean;
- };
- try {
- body = await request.json();
- } catch {
- return errorResponse('Invalid JSON', 400);
- }
-
- if (typeof body.verifyDevices !== 'boolean') {
- return errorResponse('verifyDevices must be true or false', 400);
- }
-
- const verified = await verifyUserSecret(auth, user, body.secret || body.masterPasswordHash);
- if (!verified) {
- return errorResponse('User verification failed.', 400);
- }
-
- user.verifyDevices = body.verifyDevices;
- user.updatedAt = new Date().toISOString();
- await storage.saveUser(user);
+ // Log the attempt for audit purposes, but do not change state.
await writeAuditEvent(storage, {
actorUserId: user.id,
- action: 'account.verify_devices.update',
+ action: 'account.verify_devices.update.rejected',
category: 'security',
- level: 'security',
+ level: 'info',
targetType: 'user',
targetId: user.id,
metadata: {
- verifyDevices: user.verifyDevices,
+ reason: 'new-device verification is not supported (no email delivery channel)',
...auditRequestMetadata(request),
},
});
- return new Response(null, { status: 200 });
+ return errorResponse('New device verification is not available on this server. Enable TOTP or WebAuthn two-factor authentication instead.', 400);
+}
+
+// GET /api/accounts/keys
+export async function handleGetKeys(request: Request, env: Env, userId: string): Promise {
+ void request;
+ const storage = new StorageService(env.DB);
+ const user = await storage.getUserById(userId);
+
+ if (!user) {
+ return errorResponse('User not found', 404);
+ }
+
+ return jsonResponse(keysResponse(user));
}
// POST /api/accounts/keys
@@ -593,7 +637,7 @@ export async function handleSetKeys(request: Request, env: Env, userId: string):
},
});
- return handleGetProfile(request, env, userId);
+ return jsonResponse(keysResponse(user));
}
// POST/PUT /api/accounts/password
@@ -607,6 +651,7 @@ export async function handleChangePassword(request: Request, env: Env, userId: s
masterPasswordHash?: string;
currentPasswordHash?: string;
newMasterPasswordHash?: string;
+ masterPasswordHint?: string | null;
key?: string;
newKey?: string;
encryptedPrivateKey?: string;
@@ -617,6 +662,8 @@ export async function handleChangePassword(request: Request, env: Env, userId: s
kdfIterations?: number;
kdfMemory?: number;
kdfParallelism?: number;
+ authenticationData?: Record;
+ unlockData?: Record;
};
try {
body = await request.json();
@@ -629,30 +676,101 @@ export async function handleChangePassword(request: Request, env: Env, userId: s
const valid = await auth.verifyPassword(currentHash, user.masterPasswordHash, user.email);
if (!valid) return errorResponse('Invalid password', 400);
- if (!body.newMasterPasswordHash) {
- return errorResponse('newMasterPasswordHash is required', 400);
+ const hasAuthenticationData = isRecord(body.authenticationData);
+ const hasUnlockData = isRecord(body.unlockData);
+ if (hasAuthenticationData !== hasUnlockData) {
+ return errorResponse('authenticationData and unlockData must be provided together', 400);
}
- const nextKey = body.newKey || body.key;
+
+ const legacyMasterPasswordHash = typeof body.newMasterPasswordHash === 'string'
+ ? body.newMasterPasswordHash.trim()
+ : '';
+ const legacyKey = typeof body.newKey === 'string' && body.newKey.trim()
+ ? body.newKey.trim()
+ : typeof body.key === 'string'
+ ? body.key.trim()
+ : '';
+ let newMasterPasswordHash: string;
+ let nextKey: string;
+
+ if (hasAuthenticationData && hasUnlockData) {
+ newMasterPasswordHash = readNestedString(body, ['authenticationData', 'masterPasswordAuthenticationHash']).trim();
+ nextKey = readNestedString(body, ['unlockData', 'masterKeyWrappedUserKey']).trim();
+ if (!newMasterPasswordHash || !nextKey) {
+ return errorResponse('authenticationData and unlockData are incomplete', 400);
+ }
+
+ const authKdf = readNestedNumber(body, ['authenticationData', 'kdf', 'kdfType']);
+ const authIterations = readNestedNumber(body, ['authenticationData', 'kdf', 'iterations']);
+ const authMemory = readNestedNumber(body, ['authenticationData', 'kdf', 'memory']);
+ const authParallelism = readNestedNumber(body, ['authenticationData', 'kdf', 'parallelism']);
+ const unlockKdf = readNestedNumber(body, ['unlockData', 'kdf', 'kdfType']);
+ const unlockIterations = readNestedNumber(body, ['unlockData', 'kdf', 'iterations']);
+ const unlockMemory = readNestedNumber(body, ['unlockData', 'kdf', 'memory']);
+ const unlockParallelism = readNestedNumber(body, ['unlockData', 'kdf', 'parallelism']);
+ const authSalt = readNestedString(body, ['authenticationData', 'salt']);
+ const unlockSalt = readNestedString(body, ['unlockData', 'salt']);
+ const expectedSalt = user.email.trim().toLowerCase();
+
+ if (authKdf === undefined || authIterations === undefined || unlockKdf === undefined || unlockIterations === undefined) {
+ return errorResponse('authenticationData and unlockData must include KDF settings', 400);
+ }
+ if (
+ authKdf !== unlockKdf ||
+ authIterations !== unlockIterations ||
+ authMemory !== unlockMemory ||
+ authParallelism !== unlockParallelism
+ ) {
+ return errorResponse('authenticationData and unlockData must use the same KDF settings', 400);
+ }
+ if (!authSalt || authSalt !== unlockSalt || authSalt !== expectedSalt) {
+ return errorResponse('Invalid master password salt', 400);
+ }
+ if (
+ authKdf !== user.kdfType ||
+ authIterations !== user.kdfIterations ||
+ (authKdf === 1 && (authMemory !== user.kdfMemory || authParallelism !== user.kdfParallelism))
+ ) {
+ return errorResponse('KDF settings cannot be changed with the password endpoint', 400);
+ }
+ } else {
+ if (!legacyMasterPasswordHash || !legacyKey) {
+ return errorResponse('newMasterPasswordHash and key must be provided together', 400);
+ }
+ newMasterPasswordHash = legacyMasterPasswordHash;
+ nextKey = legacyKey;
+ }
+
const nextPrivateKey = body.newEncryptedPrivateKey || body.encryptedPrivateKey;
const nextPublicKey = body.newPublicKey || body.publicKey;
- if (nextKey && !looksLikeEncString(nextKey)) {
+ if (!looksLikeEncString(nextKey)) {
return errorResponse('new key is not a valid encrypted string', 400);
}
if (nextPrivateKey && !looksLikeEncString(nextPrivateKey)) {
return errorResponse('new encryptedPrivateKey is not a valid encrypted string', 400);
}
- const kdfErr = validateKdfParams(body.kdf ?? user.kdfType, body.kdfIterations, body.kdfMemory, body.kdfParallelism);
- if (kdfErr) return errorResponse(kdfErr, 400);
+ if (
+ (typeof body.kdf === 'number' && body.kdf !== user.kdfType) ||
+ (typeof body.kdfIterations === 'number' && body.kdfIterations !== user.kdfIterations) ||
+ (typeof body.kdfMemory === 'number' && body.kdfMemory !== user.kdfMemory) ||
+ (typeof body.kdfParallelism === 'number' && body.kdfParallelism !== user.kdfParallelism)
+ ) {
+ return errorResponse('KDF settings cannot be changed with the password endpoint', 400);
+ }
+ const shouldUpdateHint = typeof body.masterPasswordHint === 'string' || body.masterPasswordHint === null;
+ const nextMasterPasswordHint = shouldUpdateHint ? normalizeMasterPasswordHint(body.masterPasswordHint) : undefined;
+ if (nextMasterPasswordHint && nextMasterPasswordHint.length > 120) {
+ return errorResponse('masterPasswordHint must be 120 characters or fewer', 400);
+ }
- user.masterPasswordHash = await auth.hashPasswordServer(body.newMasterPasswordHash, user.email);
- if (nextKey) user.key = nextKey;
+ user.masterPasswordHash = await auth.hashPasswordServer(newMasterPasswordHash, user.email);
+ user.key = nextKey;
if (nextPrivateKey) user.privateKey = nextPrivateKey;
if (nextPublicKey) user.publicKey = nextPublicKey;
- if (typeof body.kdf === 'number') user.kdfType = body.kdf;
- if (typeof body.kdfIterations === 'number') user.kdfIterations = body.kdfIterations;
- if (typeof body.kdfMemory === 'number') user.kdfMemory = body.kdfMemory;
- if (typeof body.kdfParallelism === 'number') user.kdfParallelism = body.kdfParallelism;
+ if (shouldUpdateHint) {
+ user.masterPasswordHint = nextMasterPasswordHint ?? null;
+ }
user.securityStamp = generateUUID();
user.updatedAt = new Date().toISOString();
await storage.saveUser(user);
@@ -705,6 +823,51 @@ function twoFactorAuthenticatorResponse(
};
}
+function yubiKeyResponse(user: User): Record {
+ return {
+ Enabled: isYubiKeyEnabled(user),
+ Key1: user.yubikeyKey1,
+ Key2: user.yubikeyKey2,
+ Key3: user.yubikeyKey3,
+ Key4: user.yubikeyKey4,
+ Key5: user.yubikeyKey5,
+ Nfc: !!user.yubikeyNfc,
+ Object: 'twoFactorYubiKey',
+ };
+}
+
+// New-device verification requires an email delivery channel to send OTP
+// challenges to unknown devices. NodeWarden does not integrate with an email
+// provider, so this feature is intentionally unavailable. The settings
+// response always reports disabled regardless of any legacy DB value.
+function deviceVerificationSettingsResponse(_user: User): Record {
+ return {
+ Enabled: false,
+ enabled: false,
+ VerifyDevices: false,
+ verifyDevices: false,
+ Object: 'deviceVerificationSettings',
+ object: 'deviceVerificationSettings',
+ };
+}
+
+async function yubiKeySettingsResponse(storage: StorageService, env: Env, user: User): Promise> {
+ void storage;
+ const credentials = await getYubicoCredentials(env.DB);
+ const canManageCredentials = user.role === 'admin' && user.status === 'active';
+ return {
+ ...yubiKeyResponse(user),
+ YubicoConfigured: !!credentials?.clientId,
+ YubicoCanManage: canManageCredentials,
+ ...(canManageCredentials
+ ? {
+ YubicoClientId: credentials?.clientId ?? '',
+ YubicoSecretKey: credentials?.secretKey ?? '',
+ }
+ : {}),
+ };
+}
+
// GET /api/two-factor
export async function handleGetTwoFactorProviders(request: Request, env: Env, userId: string): Promise {
void request;
@@ -712,9 +875,11 @@ export async function handleGetTwoFactorProviders(request: Request, env: Env, us
const user = await storage.getUserById(userId);
if (!user) return errorResponse('User not found', 404);
- const data = user.totpSecret
- ? [twoFactorProviderResponse(TWO_FACTOR_PROVIDER_AUTHENTICATOR, true)]
- : [];
+ const data = [];
+ if (isTotpEnabled(user.totpSecret)) data.push(twoFactorProviderResponse(TWO_FACTOR_PROVIDER_AUTHENTICATOR, true));
+ if (isYubiKeyEnabled(user)) data.push(twoFactorProviderResponse(TWO_FACTOR_PROVIDER_YUBIKEY, true));
+ const webAuthnCredentials = await storage.getAccountPasskeyCredentialsByUserId(user.id, 'twoFactor');
+ if (webAuthnCredentials.length > 0) data.push(twoFactorProviderResponse(TWO_FACTOR_PROVIDER_WEBAUTHN, true));
return jsonResponse({
Data: data,
@@ -746,6 +911,77 @@ export async function handleGetTwoFactorAuthenticator(request: Request, env: Env
return jsonResponse(twoFactorAuthenticatorResponse(!!user.totpSecret, key, userVerificationToken));
}
+// POST /api/two-factor/get-yubikey
+export async function handleGetTwoFactorYubiKey(request: Request, env: Env, userId: string): Promise {
+ const storage = new StorageService(env.DB);
+ const auth = new AuthService(env);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+
+ let body: Record;
+ try {
+ body = await readRequestBody(request);
+ } catch {
+ return errorResponse('Invalid JSON', 400);
+ }
+
+ const secret = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash', 'otp', 'OTP', 'secret', 'Secret']);
+ const verified = await verifyUserSecret(auth, user, secret);
+ if (!verified) return errorResponse('User verification failed.', 400);
+
+ return jsonResponse(await yubiKeySettingsResponse(storage, env, user));
+}
+
+// POST /api/two-factor/get-device-verification-settings
+export async function handleGetDeviceVerificationSettings(request: Request, env: Env, userId: string): Promise {
+ void request;
+ const storage = new StorageService(env.DB);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+ return jsonResponse(deviceVerificationSettingsResponse(user));
+}
+
+// PUT/POST /api/two-factor/device-verification-settings
+// New-device verification is not supported (no email delivery channel).
+// Reject any attempt to enable it; always return disabled state.
+export async function handlePutDeviceVerificationSettings(request: Request, env: Env, userId: string): Promise {
+ const storage = new StorageService(env.DB);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+
+ let body: Record;
+ try {
+ body = await readRequestBody(request);
+ } catch {
+ return errorResponse('Invalid JSON', 400);
+ }
+
+ const rawEnabled = body.enabled ?? body.Enabled ?? body.verifyDevices ?? body.VerifyDevices;
+
+ // Log the attempt for audit purposes — never change state.
+ await writeAuditEvent(storage, {
+ actorUserId: user.id,
+ action: 'account.verify_devices.update.rejected',
+ category: 'security',
+ level: 'info',
+ targetType: 'user',
+ targetId: user.id,
+ metadata: {
+ requested: rawEnabled,
+ reason: 'new-device verification is not supported (no email delivery channel)',
+ source: 'two-factor.device-verification-settings',
+ ...auditRequestMetadata(request),
+ },
+ });
+
+ if (rawEnabled === true) {
+ return errorResponse('New device verification is not available on this server. Enable TOTP or WebAuthn two-factor authentication instead.', 400);
+ }
+
+ // Setting to false is the only supported state — return it.
+ return jsonResponse(deviceVerificationSettingsResponse(user));
+}
+
// PUT/POST /api/two-factor/authenticator
export async function handlePutTwoFactorAuthenticator(request: Request, env: Env, userId: string): Promise {
const storage = new StorageService(env.DB);
@@ -769,7 +1005,10 @@ export async function handlePutTwoFactorAuthenticator(request: Request, env: Env
return errorResponse('User verification failed.', 400);
}
if (!isTotpEnabled(key)) return errorResponse('Invalid TOTP secret', 400);
- if (!await verifyTotpToken(key, token)) return errorResponse('Invalid token.', 400);
+ const matchedCounter = await findMatchingTotpCounter(key, token);
+ if (matchedCounter == null || !await storage.consumeTotpLoginCounter(user.id, matchedCounter)) {
+ return errorResponse('Invalid token.', 400);
+ }
user.totpSecret = key;
if (!user.totpRecoveryCode) {
@@ -792,6 +1031,182 @@ export async function handlePutTwoFactorAuthenticator(request: Request, env: Env
return jsonResponse(twoFactorAuthenticatorResponse(true, key));
}
+// PUT/POST /api/two-factor/yubikey
+export async function handlePutTwoFactorYubiKey(request: Request, env: Env, userId: string): Promise {
+ const storage = new StorageService(env.DB);
+ const auth = new AuthService(env);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+
+ let body: Record;
+ try {
+ body = await readRequestBody(request);
+ } catch {
+ return errorResponse('Invalid JSON', 400);
+ }
+
+ const secret = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash', 'otp', 'OTP', 'secret', 'Secret']);
+ const verified = await verifyUserSecret(auth, user, secret);
+ if (!verified) return errorResponse('User verification failed.', 400);
+
+ const keys = [
+ readBodyString(body, ['key1', 'Key1']),
+ readBodyString(body, ['key2', 'Key2']),
+ readBodyString(body, ['key3', 'Key3']),
+ readBodyString(body, ['key4', 'Key4']),
+ readBodyString(body, ['key5', 'Key5']),
+ ];
+ const publicIds: Array = [];
+ let credentials = await getYubicoCredentials(env.DB);
+ let apiKeyBootstrapOtpIndex: number | null = null;
+ for (const key of keys) {
+ const trimmed = key.trim();
+ if (!trimmed) {
+ publicIds.push(null);
+ continue;
+ }
+ const publicId = yubiKeyPublicIdFromOtp(trimmed);
+ if (!publicId) return errorResponse('Invalid YubiKey OTP.', 400);
+ if (isYubiKeyPublicId(trimmed)) {
+ publicIds.push(publicId);
+ continue;
+ }
+ if (!credentials) {
+ const initialized = await initializeYubicoCredentialsOnce(env.DB, user.email, trimmed);
+ if (!initialized) return errorResponse('Unable to initialize Yubico validation credentials.', 400);
+ credentials = initialized.credentials;
+ if (initialized.created) apiKeyBootstrapOtpIndex = publicIds.length;
+ }
+ if (apiKeyBootstrapOtpIndex !== publicIds.length && !await verifyYubicoOtp(env, trimmed, credentials)) {
+ return errorResponse('Invalid YubiKey OTP.', 400);
+ }
+ publicIds.push(publicId);
+ }
+ if (!publicIds.some(Boolean)) return errorResponse('At least one YubiKey OTP is required.', 400);
+
+ user.yubikeyKey1 = publicIds[0] ?? null;
+ user.yubikeyKey2 = publicIds[1] ?? null;
+ user.yubikeyKey3 = publicIds[2] ?? null;
+ user.yubikeyKey4 = publicIds[3] ?? null;
+ user.yubikeyKey5 = publicIds[4] ?? null;
+ user.yubikeyNfc = !!(body.nfc ?? body.Nfc);
+ if (!user.totpRecoveryCode) {
+ user.totpRecoveryCode = createRecoveryCode();
+ }
+ user.updatedAt = new Date().toISOString();
+ await storage.saveUser(user);
+ await storage.deleteRefreshTokensByUserId(user.id);
+ AuthService.invalidateUserCache(user.id);
+ await writeAuditEvent(storage, {
+ actorUserId: user.id,
+ action: 'account.yubikey.enable',
+ category: 'security',
+ level: 'security',
+ targetType: 'user',
+ targetId: user.id,
+ metadata: auditRequestMetadata(request),
+ });
+
+ return jsonResponse(await yubiKeySettingsResponse(storage, env, user));
+}
+
+// PUT/POST /api/two-factor/yubikey/config
+export async function handlePutTwoFactorYubiKeyConfig(request: Request, env: Env, userId: string): Promise {
+ const storage = new StorageService(env.DB);
+ const auth = new AuthService(env);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+ if (user.role !== 'admin' || user.status !== 'active') return errorResponse('Forbidden', 403);
+
+ let body: Record;
+ try {
+ body = await readRequestBody(request);
+ } catch {
+ return errorResponse('Invalid JSON', 400);
+ }
+
+ const secret = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash', 'otp', 'OTP', 'secret', 'Secret']);
+ const verified = await verifyUserSecret(auth, user, secret);
+ if (!verified) return errorResponse('User verification failed.', 400);
+
+ const clientId = readBodyString(body, ['yubicoClientId', 'YubicoClientId', 'clientId', 'ClientId']).trim();
+ const secretKey = readBodyString(body, ['yubicoSecretKey', 'YubicoSecretKey', 'secretKey', 'SecretKey']).trim();
+ if (!clientId || !secretKey) return errorResponse('Yubico Client ID and Secret Key are required.', 400);
+
+ await replaceYubicoCredentials(env.DB, { clientId, secretKey });
+ await writeAuditEvent(storage, {
+ actorUserId: user.id,
+ action: 'system.yubico.credentials.update',
+ category: 'security',
+ level: 'security',
+ targetType: 'system',
+ targetId: 'yubico',
+ metadata: auditRequestMetadata(request),
+ });
+
+ return jsonResponse(await yubiKeySettingsResponse(storage, env, user));
+}
+
+// POST /api/two-factor/yubikey/bootstrap
+export async function handleBootstrapTwoFactorYubiKeyConfig(request: Request, env: Env, userId: string): Promise {
+ const storage = new StorageService(env.DB);
+ const auth = new AuthService(env);
+ const user = await storage.getUserById(userId);
+ if (!user) return errorResponse('User not found', 404);
+
+ let body: Record;
+ try {
+ body = await readRequestBody(request);
+ } catch {
+ return errorResponse('Invalid JSON', 400);
+ }
+
+ const secret = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash', 'secret', 'Secret']);
+ const verified = await verifyUserSecret(auth, user, secret);
+ if (!verified) return errorResponse('User verification failed.', 400);
+
+ const otp = readBodyString(body, ['otp', 'OTP', 'token', 'Token']).trim();
+ if (!yubiKeyPublicIdFromOtp(otp)) return errorResponse('Invalid YubiKey OTP.', 400);
+ const existing = await getYubicoCredentials(env.DB);
+ if (user.role !== 'admin' && existing) {
+ return errorResponse('Yubico validation credentials are already configured.', 403);
+ }
+
+ let credentials;
+ if (user.role === 'admin') {
+ credentials = await requestYubicoApiCredentials(user.email, otp);
+ if (!credentials?.clientId || !credentials.secretKey) {
+ return errorResponse('Unable to initialize Yubico validation credentials.', 400);
+ }
+ await replaceYubicoCredentials(env.DB, credentials);
+ } else {
+ const initialized = await initializeYubicoCredentialsOnce(env.DB, user.email, otp);
+ if (!initialized?.created) {
+ return errorResponse(
+ initialized?.credentials
+ ? 'Yubico validation credentials are already configured.'
+ : 'Unable to initialize Yubico validation credentials.',
+ initialized?.credentials ? 403 : 400
+ );
+ }
+ credentials = initialized.credentials;
+ }
+
+ await writeAuditEvent(storage, {
+ actorUserId: user.id,
+ action: user.role === 'admin'
+ ? 'system.yubico.credentials.reconfigure'
+ : 'system.yubico.credentials.initialize',
+ category: 'security',
+ level: 'security',
+ targetType: 'system',
+ targetId: 'yubico',
+ metadata: auditRequestMetadata(request),
+ });
+
+ return jsonResponse(await yubiKeySettingsResponse(storage, env, user));
+}
+
// DELETE /api/two-factor/authenticator and PUT/POST /api/two-factor/disable
export async function handleDisableTwoFactorProvider(request: Request, env: Env, userId: string): Promise {
const storage = new StorageService(env.DB);
@@ -808,30 +1223,40 @@ export async function handleDisableTwoFactorProvider(request: Request, env: Env,
const typeRaw = body.type ?? body.Type ?? TWO_FACTOR_PROVIDER_AUTHENTICATOR;
const type = typeof typeRaw === 'number' ? typeRaw : Number.parseInt(String(typeRaw), 10);
- if (type !== TWO_FACTOR_PROVIDER_AUTHENTICATOR) {
+ if (![TWO_FACTOR_PROVIDER_AUTHENTICATOR, TWO_FACTOR_PROVIDER_YUBIKEY, TWO_FACTOR_PROVIDER_WEBAUTHN].includes(type)) {
return errorResponse('Two-factor provider is not supported by this server.', 400);
}
- const key = normalizeTotpSecret(readBodyString(body, ['key', 'Key']));
- const userVerificationToken = readBodyString(body, ['userVerificationToken', 'UserVerificationToken']);
const secret = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash', 'otp', 'OTP', 'secret', 'Secret']);
- let verified = false;
- if (key && userVerificationToken) {
- verified = await verifyTotpUserVerificationToken(env, user, key, userVerificationToken);
- }
- if (!verified) {
- verified = await verifyUserSecret(auth, user, secret);
- }
+ const verified = await verifyUserSecret(auth, user, secret);
if (!verified) return errorResponse('User verification failed.', 400);
- user.totpSecret = null;
+ if (type === TWO_FACTOR_PROVIDER_AUTHENTICATOR) {
+ user.totpSecret = null;
+ } else if (type === TWO_FACTOR_PROVIDER_YUBIKEY) {
+ user.yubikeyKey1 = null;
+ user.yubikeyKey2 = null;
+ user.yubikeyKey3 = null;
+ user.yubikeyKey4 = null;
+ user.yubikeyKey5 = null;
+ user.yubikeyNfc = false;
+ } else {
+ const credentials = await storage.getAccountPasskeyCredentialsByUserId(user.id, 'twoFactor');
+ for (const credential of credentials) {
+ await storage.deleteAccountPasskeyCredential(user.id, credential.id, 'twoFactor');
+ }
+ }
user.updatedAt = new Date().toISOString();
await storage.saveUser(user);
await storage.deleteRefreshTokensByUserId(user.id);
AuthService.invalidateUserCache(user.id);
await writeAuditEvent(storage, {
actorUserId: user.id,
- action: 'account.totp.disable',
+ action: type === TWO_FACTOR_PROVIDER_AUTHENTICATOR
+ ? 'account.totp.disable'
+ : type === TWO_FACTOR_PROVIDER_YUBIKEY
+ ? 'account.yubikey.disable'
+ : 'account.webauthn_2fa.disable',
category: 'security',
level: 'security',
targetType: 'user',
@@ -839,11 +1264,11 @@ export async function handleDisableTwoFactorProvider(request: Request, env: Env,
metadata: auditRequestMetadata(request),
});
- return jsonResponse(twoFactorProviderResponse(TWO_FACTOR_PROVIDER_AUTHENTICATOR, false));
+ return jsonResponse(twoFactorProviderResponse(type, false));
}
// PUT /api/accounts/totp
-// enable: { enabled: true, secret: "...", token: "123456" }
+// enable: { enabled: true, secret: "...", token: "123456", masterPasswordHash?: "...", userVerificationToken?: "..." }
// disable: { enabled: false, masterPasswordHash: "..." }
export async function handleSetTotpStatus(request: Request, env: Env, userId: string): Promise {
const storage = new StorageService(env.DB);
@@ -851,7 +1276,13 @@ export async function handleSetTotpStatus(request: Request, env: Env, userId: st
const user = await storage.getUserById(userId);
if (!user) return errorResponse('User not found', 404);
- let body: { enabled?: boolean; secret?: string; token?: string; masterPasswordHash?: string };
+ let body: {
+ enabled?: boolean;
+ secret?: string;
+ token?: string;
+ masterPasswordHash?: string;
+ userVerificationToken?: string;
+ };
try {
body = await request.json();
} catch {
@@ -860,14 +1291,26 @@ export async function handleSetTotpStatus(request: Request, env: Env, userId: st
if (body.enabled === true) {
const normalizedSecret = normalizeTotpSecret(body.secret || '');
+ const masterPasswordHash = readBodyString(body, ['masterPasswordHash', 'MasterPasswordHash']);
+ const userVerificationToken = readBodyString(body, ['userVerificationToken', 'UserVerificationToken']);
if (!isTotpEnabled(normalizedSecret)) {
return errorResponse('Invalid TOTP secret', 400);
}
if (!body.token) {
return errorResponse('TOTP token is required', 400);
}
- const verified = await verifyTotpToken(normalizedSecret, body.token);
- if (!verified) {
+ let verifiedUser = false;
+ if (userVerificationToken) {
+ verifiedUser = await verifyTotpUserVerificationToken(env, user, normalizedSecret, userVerificationToken);
+ }
+ if (!verifiedUser && masterPasswordHash) {
+ verifiedUser = await auth.verifyPassword(masterPasswordHash, user.masterPasswordHash, user.email);
+ }
+ if (!verifiedUser) {
+ return errorResponse('User verification failed.', 400);
+ }
+ const matchedCounter = await findMatchingTotpCounter(normalizedSecret, body.token);
+ if (matchedCounter == null || !await storage.consumeTotpLoginCounter(user.id, matchedCounter)) {
return errorResponse('Invalid TOTP token', 400);
}
user.totpSecret = normalizedSecret;
@@ -1015,6 +1458,16 @@ export async function handleRecoverTwoFactor(request: Request, env: Env): Promis
}
user.totpSecret = null;
+ user.yubikeyKey1 = null;
+ user.yubikeyKey2 = null;
+ user.yubikeyKey3 = null;
+ user.yubikeyKey4 = null;
+ user.yubikeyKey5 = null;
+ user.yubikeyNfc = false;
+ const webAuthnCredentials = await storage.getAccountPasskeyCredentialsByUserId(user.id, 'twoFactor');
+ for (const credential of webAuthnCredentials) {
+ await storage.deleteAccountPasskeyCredential(user.id, credential.id, 'twoFactor');
+ }
user.totpRecoveryCode = createRecoveryCode();
user.securityStamp = generateUUID();
user.updatedAt = new Date().toISOString();
@@ -1061,23 +1514,26 @@ export async function handleVerifyPassword(request: Request, env: Env, userId: s
return errorResponse('User not found', 404);
}
- let body: { masterPasswordHash?: string };
+ let body: { masterPasswordHash?: string; authenticationData?: Record };
try {
body = await request.json();
} catch {
return errorResponse('Invalid JSON', 400);
}
- if (!body.masterPasswordHash) {
+ const masterPasswordHash =
+ body.masterPasswordHash ||
+ readNestedString(body, ['authenticationData', 'masterPasswordAuthenticationHash']);
+ if (!masterPasswordHash) {
return errorResponse('masterPasswordHash is required', 400);
}
- const valid = await auth.verifyPassword(body.masterPasswordHash, user.masterPasswordHash, user.email);
+ const valid = await auth.verifyPassword(masterPasswordHash, user.masterPasswordHash, user.email);
if (!valid) {
return errorResponse('Invalid password', 400);
}
- return new Response(null, { status: 200 });
+ return jsonResponse(masterPasswordPolicyResponse());
}
// POST /api/accounts/api-key
@@ -1114,26 +1570,30 @@ async function apiKey(request: Request, env: Env, userId: string, rotate: boolea
const valid = await auth.verifyPassword(currentHash, user.masterPasswordHash, user.email);
if (!valid) return errorResponse('Invalid password', 400);
- if (rotate || user.apiKey === null) {
- // Upstream apikeys are 30-character random alphanumeric strings
+ if (!rotate && isStoredApiKeyHash(user.apiKey)) {
+ return errorResponse(
+ 'This API key was created by an older NodeWarden version and cannot be displayed. Rotate it once to use the Bitwarden-compatible readable format.',
+ 409
+ );
+ }
+
+ let auditAction = 'account.api_key.view';
+ if (rotate || !user.apiKey) {
user.apiKey = randomStringAlphanum(LIMITS.auth.clientSecretLength);
- if (rotate) {
- user.securityStamp = generateUUID();
- await storage.deleteRefreshTokensByUserId(user.id);
- }
user.updatedAt = new Date().toISOString();
await storage.saveUser(user);
AuthService.invalidateUserCache(user.id);
- await writeAuditEvent(storage, {
- actorUserId: user.id,
- action: rotate ? 'account.api_key.rotate' : 'account.api_key.create',
- category: 'security',
- level: rotate ? 'security' : 'info',
- targetType: 'user',
- targetId: user.id,
- metadata: auditRequestMetadata(request),
- });
+ auditAction = rotate ? 'account.api_key.rotate' : 'account.api_key.create';
}
+ await writeAuditEvent(storage, {
+ actorUserId: user.id,
+ action: auditAction,
+ category: 'security',
+ level: rotate ? 'security' : 'info',
+ targetType: 'user',
+ targetId: user.id,
+ metadata: auditRequestMetadata(request),
+ });
return jsonResponse({
apiKey: user.apiKey,
diff --git a/src/handlers/admin.ts b/src/handlers/admin.ts
index cc216c5..8725c61 100644
--- a/src/handlers/admin.ts
+++ b/src/handlers/admin.ts
@@ -9,6 +9,34 @@ function isAdmin(user: User): boolean {
return user.role === 'admin' && user.status === 'active';
}
+async function requireMasterPasswordHash(
+ env: Env,
+ actorUser: User,
+ masterPasswordHash: unknown
+): Promise {
+ const normalized = String(masterPasswordHash || '').trim();
+ if (!normalized) {
+ return errorResponse('masterPasswordHash is required', 400);
+ }
+ const auth = new AuthService(env);
+ const valid = await auth.verifyPassword(normalized, actorUser.masterPasswordHash, actorUser.email);
+ if (!valid) {
+ return errorResponse('Invalid password', 400);
+ }
+ return null;
+}
+
+async function readJsonBody(request: Request): Promise> {
+ try {
+ const body = await request.json();
+ return body && typeof body === 'object' && !Array.isArray(body)
+ ? body as Record
+ : {};
+ } catch {
+ return {};
+ }
+}
+
function randomHex(bytes: number): string {
const data = crypto.getRandomValues(new Uint8Array(bytes));
return Array.from(data).map(v => v.toString(16).padStart(2, '0')).join('');
@@ -69,18 +97,22 @@ export async function handleAdminListUsers(
const storage = new StorageService(env.DB);
const users = await storage.getAllUsers();
- return jsonResponse({
- data: users.map(user => ({
+ const data = await Promise.all(users.map(async user => {
+ const hasTwoFactorPasskey = await storage.countAccountPasskeyCredentialsByUserId(user.id, 'twoFactor') > 0;
+ return {
id: user.id,
email: user.email,
name: user.name,
role: user.role,
status: user.status,
- twoFactorEnabled: !!user.totpSecret,
+ twoFactorEnabled: !!user.totpSecret || Boolean(user.yubikeyKey1 || user.yubikeyKey2 || user.yubikeyKey3 || user.yubikeyKey4 || user.yubikeyKey5) || hasTwoFactorPasskey,
creationDate: user.createdAt,
revisionDate: user.updatedAt,
object: 'user',
- })),
+ };
+ }));
+ return jsonResponse({
+ data,
object: 'list',
continuationToken: null,
});
@@ -183,6 +215,9 @@ export async function handleAdminClearAuditLogs(
}
const storage = new StorageService(env.DB);
const deleted = await storage.clearAuditLogs();
+ await writeAuditLog(storage, actorUser.id, 'admin.audit.clear', 'auditLog', null, {
+ deleted,
+ }, request);
return jsonResponse({ object: 'auditLogClear', deleted });
}
@@ -197,14 +232,11 @@ export async function handleAdminCreateInvite(
}
const storage = new StorageService(env.DB);
- let body: { expiresInHours?: number } = {};
- try {
- body = await request.json();
- } catch {
- body = {};
- }
+ const body = await readJsonBody(request);
+ const passwordError = await requireMasterPasswordHash(env, actorUser, body.masterPasswordHash);
+ if (passwordError) return passwordError;
- const expiresInHours = Number.isFinite(body.expiresInHours)
+ const expiresInHours = Number.isFinite(Number(body.expiresInHours))
? Math.max(1, Math.min(24 * 30, Math.floor(Number(body.expiresInHours))))
: 24 * 7;
const now = new Date();
@@ -249,7 +281,7 @@ export async function handleAdminListInvites(
}
// DELETE /api/admin/invites/:code
-export async function handleAdminRevokeInvite(
+export async function handleAdminDeleteInvite(
request: Request,
env: Env,
actorUser: User,
@@ -259,13 +291,19 @@ export async function handleAdminRevokeInvite(
return errorResponse('Forbidden', 403);
}
+ const body = await readJsonBody(request);
+ const passwordError = await requireMasterPasswordHash(env, actorUser, body.masterPasswordHash);
+ if (passwordError) return passwordError;
+
const storage = new StorageService(env.DB);
- const revoked = await storage.revokeInvite(code);
- if (!revoked) {
- return errorResponse('Invite not found or already inactive', 404);
+ const deleted = await storage.deleteInvite(code);
+ if (!deleted) {
+ return errorResponse('Invite not found', 404);
}
- await writeAuditLog(storage, actorUser.id, 'admin.invite.revoke', 'invite', null, null, request);
+ await writeAuditLog(storage, actorUser.id, 'admin.invite.delete', 'invite', null, {
+ code,
+ }, request);
return new Response(null, { status: 204 });
}
@@ -275,12 +313,25 @@ export async function handleAdminDeleteAllInvites(
env: Env,
actorUser: User
): Promise {
- void request;
if (!isAdmin(actorUser)) {
return errorResponse('Forbidden', 403);
}
+ const body = await readJsonBody(request);
+ const passwordError = await requireMasterPasswordHash(env, actorUser, body.masterPasswordHash);
+ if (passwordError) return passwordError;
+
const storage = new StorageService(env.DB);
+ const url = new URL(request.url);
+ if (url.searchParams.get('scope') === 'invalid') {
+ const deleted = await storage.deleteInvalidInvites();
+ await writeAuditLog(storage, actorUser.id, 'admin.invite.delete_invalid', 'invite', null, {
+ deleted,
+ }, request);
+
+ return jsonResponse({ deleted }, 200);
+ }
+
const deleted = await storage.deleteAllInvites();
await writeAuditLog(storage, actorUser.id, 'admin.invite.delete_all', 'invite', null, {
deleted,
@@ -300,12 +351,9 @@ export async function handleAdminSetUserStatus(
return errorResponse('Forbidden', 403);
}
- let body: { status?: string };
- try {
- body = await request.json();
- } catch {
- return errorResponse('Invalid JSON', 400);
- }
+ const body = await readJsonBody(request);
+ const passwordError = await requireMasterPasswordHash(env, actorUser, body.masterPasswordHash);
+ if (passwordError) return passwordError;
const nextStatus = body.status === 'banned' ? 'banned' : body.status === 'active' ? 'active' : null;
if (!nextStatus) {
@@ -348,7 +396,6 @@ export async function handleAdminDeleteUser(
actorUser: User,
targetUserId: string
): Promise {
- void request;
if (!isAdmin(actorUser)) {
return errorResponse('Forbidden', 403);
}
@@ -356,6 +403,10 @@ export async function handleAdminDeleteUser(
return errorResponse('You cannot delete yourself', 400);
}
+ const body = await readJsonBody(request);
+ const passwordError = await requireMasterPasswordHash(env, actorUser, body.masterPasswordHash);
+ if (passwordError) return passwordError;
+
const storage = new StorageService(env.DB);
const target = await storage.getUserById(targetUserId);
if (!target) {
diff --git a/src/handlers/attachments.ts b/src/handlers/attachments.ts
index c1dea72..9a432f3 100644
--- a/src/handlers/attachments.ts
+++ b/src/handlers/attachments.ts
@@ -1,9 +1,10 @@
-import { Env, Attachment, DEFAULT_DEV_SECRET } from '../types';
-import { notifyUserVaultSync } from '../durable/notifications-hub';
+import { Env, Attachment, Cipher } from '../types';
+import { notifyUserCipherUpdate, notifyUserVaultSync } from '../durable/notifications-hub';
import { StorageService } from '../services/storage';
import { jsonResponse, errorResponse } from '../utils/response';
import { buildDirectUploadUrl, getSafeJwtSecret, parseDirectUploadPayload } from '../utils/direct-upload';
import { generateUUID } from '../utils/uuid';
+import { sanitizeDownloadContentType } from '../utils/content-type';
import {
createAttachmentUploadToken,
createFileDownloadToken,
@@ -31,6 +32,38 @@ function notifyVaultSyncForRequest(
notifyUserVaultSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
+function normalizeOptionalId(value: unknown): string | null {
+ if (value == null) return null;
+ const normalized = String(value).trim();
+ return normalized ? normalized : null;
+}
+
+function notifyCipherUpdateForRequest(
+ request: Request,
+ env: Env,
+ cipher: Cipher,
+ revisionDate: string
+): void {
+ notifyUserCipherUpdate(env, {
+ userId: cipher.userId,
+ cipherId: cipher.id,
+ revisionDate,
+ organizationId: normalizeOptionalId((cipher as any).organizationId ?? null),
+ collectionIds: Array.isArray((cipher as any).collectionIds)
+ ? (cipher as any).collectionIds.map((id: unknown) => String(id || '').trim()).filter(Boolean)
+ : null,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
+function contentDispositionAttachment(fileName: string | null | undefined): string {
+ const fallback = 'attachment';
+ const value = String(fileName || fallback)
+ .replace(/[\r\n"]/g, '_')
+ .trim() || fallback;
+ return `attachment; filename="${value}"`;
+}
+
async function writeAttachmentAudit(
storage: StorageService,
request: Request,
@@ -75,6 +108,7 @@ async function runWithConcurrency(
async function processAttachmentUpload(
request: Request,
env: Env,
+ cipher: Cipher,
attachment: Attachment,
cipherId: string
): Promise {
@@ -90,6 +124,10 @@ async function processAttachmentUpload(
}
const path = getAttachmentObjectKey(cipherId, attachment.id);
+ if (await getBlobObject(env, path)) {
+ return errorResponse('Attachment file has already been uploaded', 409);
+ }
+
try {
await putBlobObject(env, path, upload.body, {
size: upload.size,
@@ -116,6 +154,7 @@ async function processAttachmentUpload(
const revisionInfo = await storage.updateCipherRevisionDate(cipherId);
if (revisionInfo) {
notifyVaultSyncForRequest(request, env, revisionInfo.userId, revisionInfo.revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionInfo.revisionDate);
}
return new Response(null, { status: 201 });
@@ -132,7 +171,7 @@ export async function handleCreateAttachment(
const storage = new StorageService(env.DB);
// Verify cipher exists and belongs to user
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
}
@@ -170,16 +209,17 @@ export async function handleCreateAttachment(
await storage.saveAttachment(attachment);
// Add attachment to cipher
- await storage.addAttachmentToCipher(cipherId, attachmentId);
+ await storage.addAttachmentToCipherForUser(cipherId, attachmentId, userId);
// Update cipher revision date
const revisionInfo = await storage.updateCipherRevisionDate(cipherId);
if (revisionInfo) {
notifyVaultSyncForRequest(request, env, revisionInfo.userId, revisionInfo.revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionInfo.revisionDate);
}
// Get updated cipher for response
- const updatedCipher = await storage.getCipher(cipherId);
+ const updatedCipher = await storage.getCipherForUser(cipherId, userId);
const attachments = await storage.getAttachmentsByCipher(cipherId);
const jwtSecret = getSafeJwtSecret(env);
if (!jwtSecret) {
@@ -208,18 +248,18 @@ export async function handleUploadAttachment(
const storage = new StorageService(env.DB);
// Verify cipher exists and belongs to user
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
}
// Verify attachment exists
- const attachment = await storage.getAttachment(attachmentId);
+ const attachment = await storage.getAttachmentForUser(attachmentId, userId);
if (!attachment || attachment.cipherId !== cipherId) {
return errorResponse('Attachment not found', 404);
}
- return processAttachmentUpload(request, env, attachment, cipherId);
+ return processAttachmentUpload(request, env, cipher, attachment, cipherId);
}
export async function handlePublicUploadAttachment(
@@ -247,17 +287,17 @@ export async function handlePublicUploadAttachment(
}
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, claims.userId);
if (!cipher || cipher.userId !== claims.userId) {
return errorResponse('Cipher not found', 404);
}
- const attachment = await storage.getAttachment(attachmentId);
+ const attachment = await storage.getAttachmentForUser(attachmentId, claims.userId);
if (!attachment || attachment.cipherId !== cipherId) {
return errorResponse('Attachment not found', 404);
}
- return processAttachmentUpload(request, env, attachment, cipherId);
+ return processAttachmentUpload(request, env, cipher, attachment, cipherId);
}
// GET /api/ciphers/{cipherId}/attachment/{attachmentId}
@@ -272,13 +312,13 @@ export async function handleGetAttachment(
const storage = new StorageService(env.DB);
// Verify cipher exists and belongs to user
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
}
// Verify attachment exists
- const attachment = await storage.getAttachment(attachmentId);
+ const attachment = await storage.getAttachmentForUser(attachmentId, userId);
if (!attachment || attachment.cipherId !== cipherId) {
return errorResponse('Attachment not found', 404);
}
@@ -313,12 +353,12 @@ export async function handleUpdateAttachmentMetadata(
): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
}
- const attachment = await storage.getAttachment(attachmentId);
+ const attachment = await storage.getAttachmentForUser(attachmentId, userId);
if (!attachment || attachment.cipherId !== cipherId) {
return errorResponse('Attachment not found', 404);
}
@@ -348,6 +388,7 @@ export async function handleUpdateAttachmentMetadata(
const revisionInfo = await storage.updateCipherRevisionDate(cipherId);
if (revisionInfo) {
notifyVaultSyncForRequest(request, env, revisionInfo.userId, revisionInfo.revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionInfo.revisionDate);
}
return jsonResponse({
@@ -368,10 +409,8 @@ export async function handlePublicDownloadAttachment(
cipherId: string,
attachmentId: string
): Promise {
- const secret = (env.JWT_SECRET || '').trim();
- if (!secret || secret.length < LIMITS.auth.jwtSecretMinLength || secret === DEFAULT_DEV_SECRET) {
- return errorResponse('Server configuration error', 500);
- }
+ const secret = getSafeJwtSecret(env);
+ if (!secret) return errorResponse('Server configuration error', 500);
const url = new URL(request.url);
const token = url.searchParams.get('token');
@@ -381,7 +420,7 @@ export async function handlePublicDownloadAttachment(
}
// Verify token
- const claims = await verifyFileDownloadToken(token, env.JWT_SECRET);
+ const claims = await verifyFileDownloadToken(token, secret);
if (!claims) {
return errorResponse('Invalid or expired token', 401);
}
@@ -400,22 +439,23 @@ export async function handlePublicDownloadAttachment(
}
const path = getAttachmentObjectKey(cipherId, attachmentId);
- const object = await getBlobObject(env, path);
-
- if (!object) {
- return errorResponse('Attachment file not found', 404);
- }
-
const firstUse = await storage.consumeAttachmentDownloadToken(claims.jti, claims.exp);
if (!firstUse) {
return errorResponse('Invalid or expired token', 401);
}
+ const object = await getBlobObject(env, path);
+ if (!object) {
+ return errorResponse('Attachment file not found', 404);
+ }
+
return new Response(object.body, {
headers: {
- 'Content-Type': object.contentType || 'application/octet-stream',
+ 'Content-Type': sanitizeDownloadContentType(object.contentType),
'Content-Length': String(object.size),
+ 'Content-Disposition': contentDispositionAttachment(attachment.fileName),
'Cache-Control': 'private, no-cache',
+ 'X-Content-Type-Options': 'nosniff',
},
});
}
@@ -432,13 +472,13 @@ export async function handleDeleteAttachment(
const storage = new StorageService(env.DB);
// Verify cipher exists and belongs to user
- const cipher = await storage.getCipher(cipherId);
+ const cipher = await storage.getCipherForUser(cipherId, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
}
// Verify attachment exists
- const attachment = await storage.getAttachment(attachmentId);
+ const attachment = await storage.getAttachmentForUser(attachmentId, userId);
if (!attachment || attachment.cipherId !== cipherId) {
return errorResponse('Attachment not found', 404);
}
@@ -447,12 +487,13 @@ export async function handleDeleteAttachment(
await deleteBlobObject(env, path);
// Delete attachment metadata
- await storage.deleteAttachment(attachmentId);
+ await storage.deleteAttachmentForUser(attachmentId, userId);
// Update cipher revision date
const revisionInfo = await storage.updateCipherRevisionDate(cipherId);
if (revisionInfo) {
notifyVaultSyncForRequest(request, env, revisionInfo.userId, revisionInfo.revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionInfo.revisionDate);
await writeAttachmentAudit(storage, request, revisionInfo.userId, 'attachment.delete', {
id: attachmentId,
cipherId,
@@ -461,11 +502,15 @@ export async function handleDeleteAttachment(
}
// Get updated cipher for response
- const updatedCipher = await storage.getCipher(cipherId);
+ const updatedCipher = await storage.getCipherForUser(cipherId, userId);
const attachments = await storage.getAttachmentsByCipher(cipherId);
+ const cipherResponse = cipherToResponse(updatedCipher!, attachments);
return jsonResponse({
- cipher: cipherToResponse(updatedCipher!, attachments),
+ Cipher: cipherResponse,
+ cipher: cipherResponse,
+ Object: 'deleteAttachment',
+ object: 'deleteAttachment',
});
}
diff --git a/src/handlers/auth-requests.ts b/src/handlers/auth-requests.ts
index 04a63e4..c09fd9c 100644
--- a/src/handlers/auth-requests.ts
+++ b/src/handlers/auth-requests.ts
@@ -5,6 +5,8 @@ import { readAuthRequestDeviceInfo, readActingDeviceIdentifier } from '../utils/
import { errorResponse, jsonResponse } from '../utils/response';
import { isAuthRequestExpired } from '../services/storage-auth-request-repo';
import { notifyAuthRequestResponse, notifyUserAuthRequest } from '../durable/notifications-hub';
+import { RateLimitService, getClientIdentifier } from '../services/ratelimit';
+import { LIMITS } from '../config/limits';
const AUTH_REQUEST_TYPE_AUTHENTICATE_AND_UNLOCK = 0;
const AUTH_REQUEST_TYPE_UNLOCK = 1;
@@ -14,6 +16,19 @@ function normalizeText(value: unknown, maxLength: number): string {
return String(value ?? '').trim().slice(0, maxLength);
}
+function isSerializedEncString(value: unknown): value is string {
+ const text = String(value || '').trim();
+ if (!text) return false;
+ const parts = text.split('.');
+ if (parts.length !== 2) return false;
+ const type = Number(parts[0]);
+ const bodyParts = parts[1].split('|');
+ if (type === 2) return bodyParts.length === 3 && bodyParts.every(Boolean);
+ if (type === 3 || type === 4) return bodyParts.length === 1 && !!bodyParts[0];
+ if (type === 5 || type === 6) return bodyParts.length === 2 && bodyParts.every(Boolean);
+ return false;
+}
+
function getClientIp(request: Request): string | null {
return (
request.headers.get('CF-Connecting-IP') ||
@@ -81,8 +96,8 @@ function toAuthRequestResponse(request: Request, authRequest: AuthRequestRecord,
RequestCountryName: authRequest.requestCountryName,
key: authRequest.key,
Key: authRequest.key,
- masterPasswordHash: authRequest.masterPasswordHash,
- MasterPasswordHash: authRequest.masterPasswordHash,
+ masterPasswordHash: null,
+ MasterPasswordHash: null,
creationDate: authRequest.creationDate,
CreationDate: authRequest.creationDate,
responseDate: authRequest.responseDate,
@@ -118,6 +133,30 @@ async function readJsonBody(request: Request): Promise | nul
}
}
+async function enforceAuthRequestCreateRateLimit(
+ request: Request,
+ env: Env,
+ email: string,
+ deviceIdentifier: string
+): Promise {
+ const clientIdentifier = getClientIdentifier(request);
+ if (!clientIdentifier) return errorResponse('Client IP is required', 403);
+
+ const rateLimit = new RateLimitService(env.DB);
+ const limit = LIMITS.rateLimit.authRequestRequestsPerMinute;
+ const encodedEmail = encodeURIComponent(email || 'missing');
+ const encodedDevice = encodeURIComponent(deviceIdentifier || 'missing');
+ const budgets = await Promise.all([
+ rateLimit.consumeStrictBudget(`auth-request:ip:${clientIdentifier}`, limit),
+ rateLimit.consumeStrictBudget(`auth-request:email:${encodedEmail}`, limit),
+ rateLimit.consumeStrictBudget(`auth-request:device:${encodedDevice}`, limit),
+ ]);
+ const blocked = budgets.find((budget) => !budget.allowed);
+ if (!blocked) return null;
+
+ return errorResponse('Too many authentication requests. Try again later.', 429);
+}
+
function readBodyValue(body: Record, names: string[]): unknown {
for (const name of names) {
if (body[name] !== undefined) return body[name];
@@ -151,6 +190,8 @@ export async function handleCreateAuthRequest(request: Request, env: Env): Promi
if (!email || !publicKey || !accessCode || !deviceInfo.deviceIdentifier) {
return errorResponse('Email, public key, device identifier, and access code are required.', 400);
}
+ const rateLimitResponse = await enforceAuthRequestCreateRateLimit(request, env, email, deviceInfo.deviceIdentifier);
+ if (rateLimitResponse) return rateLimitResponse;
if (!isSupportedAuthRequestType(type) || type === AUTH_REQUEST_TYPE_ADMIN_APPROVAL) {
return errorResponse('Invalid auth request type.', 400);
}
@@ -186,9 +227,75 @@ export async function handleCreateAuthRequest(request: Request, env: Env): Promi
return jsonResponse(toAuthRequestResponse(request, authRequest));
}
+export async function handleCreateAdminAuthRequest(
+ request: Request,
+ env: Env,
+ userId: string,
+ userEmail: string
+): Promise {
+ const storage = new StorageService(env.DB);
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+
+ const email = normalizeText(readBodyValue(body, ['email', 'Email']), 320).toLowerCase() || userEmail.toLowerCase();
+ const publicKey = normalizeText(readBodyValue(body, ['publicKey', 'PublicKey']), 8192);
+ const accessCode = normalizeText(readBodyValue(body, ['accessCode', 'AccessCode']), 25);
+ const requestedType = Number(readBodyValue(body, ['type', 'Type']));
+ const deviceInfo = readAuthRequestDeviceInfo(
+ {
+ deviceIdentifier: normalizeText(readBodyValue(body, ['deviceIdentifier', 'DeviceIdentifier']), 128),
+ deviceName: normalizeText(readBodyValue(body, ['deviceName', 'DeviceName']), 128),
+ deviceType: String(readBodyValue(body, ['deviceType', 'DeviceType']) ?? ''),
+ },
+ request
+ );
+
+ if (requestedType !== AUTH_REQUEST_TYPE_ADMIN_APPROVAL) {
+ return errorResponse('Invalid AuthRequestType. Expected AdminApproval.', 400);
+ }
+ if (email !== userEmail.toLowerCase()) {
+ return errorResponse('Email does not match authenticated user.', 400);
+ }
+ if (!publicKey || !accessCode || !deviceInfo.deviceIdentifier) {
+ return errorResponse('Public key, device identifier, and access code are required.', 400);
+ }
+ const rateLimitResponse = await enforceAuthRequestCreateRateLimit(request, env, email, deviceInfo.deviceIdentifier);
+ if (rateLimitResponse) return rateLimitResponse;
+
+ const user = await storage.getUserById(userId);
+ if (!user || user.status !== 'active') {
+ return errorResponse('User not found.', 404);
+ }
+
+ await storage.pruneExpiredAuthRequests();
+ const now = new Date().toISOString();
+ const authRequest: AuthRequestRecord = {
+ id: generateUUID(),
+ userId: user.id,
+ organizationId: null,
+ type: AUTH_REQUEST_TYPE_ADMIN_APPROVAL,
+ requestDeviceIdentifier: deviceInfo.deviceIdentifier,
+ requestDeviceType: deviceInfo.deviceType,
+ requestIpAddress: getClientIp(request),
+ requestCountryName: getCountryName(request),
+ responseDeviceIdentifier: null,
+ accessCode,
+ publicKey,
+ key: null,
+ masterPasswordHash: null,
+ approved: null,
+ creationDate: now,
+ responseDate: null,
+ authenticationDate: null,
+ };
+ await storage.createAuthRequest(authRequest);
+ notifyUserAuthRequest(env, user.id, authRequest.id, deviceInfo.deviceIdentifier);
+ return jsonResponse(toAuthRequestResponse(request, authRequest));
+}
+
export async function handleGetAuthRequest(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const authRequest = await storage.getAuthRequestById(id);
+ const authRequest = await storage.getAuthRequestByIdForUser(id, userId);
if (!authRequest || authRequest.userId !== userId) return errorResponse('Not found', 404);
return jsonResponse(toAuthRequestResponse(request, authRequest));
}
@@ -226,7 +333,7 @@ export async function handleUpdateAuthRequest(request: Request, env: Env, userId
const body = await readJsonBody(request);
if (!body) return errorResponse('Invalid request payload', 400);
- const authRequest = await storage.getAuthRequestById(id);
+ const authRequest = await storage.getAuthRequestByIdForUser(id, userId);
if (!authRequest || authRequest.userId !== userId || isAuthRequestExpired(authRequest)) {
return errorResponse('Not found', 404);
}
@@ -242,7 +349,6 @@ export async function handleUpdateAuthRequest(request: Request, env: Env, userId
const approved = Boolean(readBodyValue(body, ['requestApproved', 'RequestApproved']));
const key = normalizeText(readBodyValue(body, ['key', 'Key']), 20000);
- const masterPasswordHash = normalizeText(readBodyValue(body, ['masterPasswordHash', 'MasterPasswordHash']), 20000) || null;
const responseDeviceIdentifier =
normalizeText(readBodyValue(body, ['deviceIdentifier', 'DeviceIdentifier']), 128) ||
readActingDeviceIdentifier(request) ||
@@ -251,15 +357,18 @@ export async function handleUpdateAuthRequest(request: Request, env: Env, userId
if (approved && !key) {
return errorResponse('Encrypted key is required to approve the request.', 400);
}
+ if (approved && !isSerializedEncString(key)) {
+ return errorResponse('Encrypted key is not a valid encrypted string.', 400);
+ }
const updated = await storage.updateAuthRequestResponse(id, userId, {
approved,
responseDeviceIdentifier,
key,
- masterPasswordHash,
+ masterPasswordHash: null,
});
if (!updated) return errorResponse('Auth request has already been answered.', 409);
- const updatedRequest = await storage.getAuthRequestById(id);
+ const updatedRequest = await storage.getAuthRequestByIdForUser(id, userId);
// Match Bitwarden upstream behavior: only approval wakes the originating anonymous
// client. Denials are not pushed to avoid leaking that a login attempt was rejected.
if (approved) {
diff --git a/src/handlers/backup.ts b/src/handlers/backup.ts
index 288eb65..2b187ae 100644
--- a/src/handlers/backup.ts
+++ b/src/handlers/backup.ts
@@ -2,8 +2,10 @@ import type { Env, User } from '../types';
import { errorResponse, jsonResponse } from '../utils/response';
import {
type BackupArchiveBundle,
+ MAX_BACKUP_ARCHIVE_BYTES,
buildBackupArchive,
inspectBackupArchiveFileNameChecksum,
+ isSafeBackupAttachmentBlobName,
parseBackupArchive,
verifyBackupArchiveFileNameChecksum,
} from '../services/backup-archive';
@@ -18,9 +20,11 @@ import {
loadBackupSettings,
normalizeBackupSettingsInput,
normalizeImportedBackupSettings,
+ redactBackupSettingsSecrets,
repairBackupSettings,
requireBackupDestination,
saveBackupSettings,
+ updateBackupDestinationRuntime,
} from '../services/backup-config';
import {
type BackupImportExecutionResult,
@@ -40,15 +44,60 @@ import {
uploadBackupArchive,
} from '../services/backup-uploader';
import { StorageService } from '../services/storage';
+import { AuthService } from '../services/auth';
import { auditRequestMetadata, writeAuditEvent } from '../services/audit-events';
import { getBlobObject } from '../services/blob-store';
import { notifyUserBackupProgress, notifyUserBackupRestoreProgress } from '../durable/notifications-hub';
+import { getMultipartRequestMaxBytes } from '../utils/direct-upload';
+import { verifyPasskeyUserVerificationToken } from '../utils/user-verification-token';
import { unzipSync } from 'fflate';
function isAdmin(user: User): boolean {
return user.role === 'admin' && user.status === 'active';
}
+function parseRequestContentLength(request: Request): number | null {
+ const raw = request.headers.get('content-length');
+ if (!raw) return null;
+ const value = Number(raw);
+ if (!Number.isFinite(value) || value < 0) return null;
+ return Math.floor(value);
+}
+
+async function requireBackupUserVerification(actorUser: User, masterPasswordHash: string, env: Env): Promise {
+ const normalized = String(masterPasswordHash || '').trim();
+ if (!normalized) {
+ return errorResponse('masterPasswordHash is required', 400);
+ }
+ const auth = new AuthService(env);
+ const valid = await auth.verifyPassword(normalized, actorUser.masterPasswordHash, actorUser.email);
+ if (!valid) {
+ return errorResponse('Invalid password', 400);
+ }
+ return null;
+}
+
+async function requireBackupRepairVerification(
+ actorUser: User,
+ body: { masterPasswordHash?: string; userVerificationToken?: string },
+ env: Env
+): Promise {
+ const masterPasswordHash = String(body.masterPasswordHash || '').trim();
+ if (masterPasswordHash) {
+ return requireBackupUserVerification(actorUser, masterPasswordHash, env);
+ }
+
+ const userVerificationToken = String(body.userVerificationToken || '').trim();
+ if (!userVerificationToken) {
+ return errorResponse('masterPasswordHash or userVerificationToken is required', 400);
+ }
+ const valid = await verifyPasskeyUserVerificationToken(env, userVerificationToken, actorUser.id, 'backup.settings.repair');
+ if (!valid) {
+ return errorResponse('Invalid user verification token', 400);
+ }
+ return null;
+}
+
async function writeAuditLog(
storage: StorageService,
actorUserId: string | null,
@@ -92,11 +141,18 @@ function ensureBackupBlobName(value: string): string {
if (!normalized) {
throw new Error('Backup attachment blob is required');
}
- const parts = normalized.split('/').filter(Boolean);
- if (!parts.length || parts.some((part) => part === '.' || part === '..')) {
+ if (!isSafeBackupAttachmentBlobName(normalized)) {
throw new Error('Backup attachment blob is invalid');
}
- return parts.join('/');
+ return normalized;
+}
+
+function contentDispositionBackup(fileName: string | null | undefined): string {
+ const fallback = 'nodewarden_backup.zip';
+ const value = String(fileName || fallback)
+ .replace(/[\\/\r\n"]/g, '_')
+ .trim() || fallback;
+ return `attachment; filename="${value}"`;
}
const REMOTE_ATTACHMENT_INDEX_PATH = 'attachments/.nodewarden-attachment-index.v1.json';
@@ -224,6 +280,30 @@ async function uploadRemoteAttachmentChunk(
}
}
+async function verifyUploadedBackupArchive(
+ session: RemoteBackupTransferSession,
+ archive: BackupArchiveBundle
+): Promise<'metadata' | 'download'> {
+ try {
+ const stat = await session.stat(archive.fileName);
+ if (stat?.size === archive.bytes.byteLength) {
+ return 'metadata';
+ }
+ } catch {
+ // Fall through to a full read-back verification when lightweight metadata is unavailable.
+ }
+
+ const remoteFile = await session.download(archive.fileName);
+ const checksumOk = await verifyBackupArchiveFileNameChecksum(remoteFile.bytes, archive.fileName);
+ if (!checksumOk) {
+ throw new Error('Remote backup ZIP checksum verification failed');
+ }
+ if (remoteFile.bytes.byteLength !== archive.bytes.byteLength) {
+ throw new Error('Remote backup ZIP size verification failed');
+ }
+ return 'download';
+}
+
export async function executeConfiguredBackup(
env: Env,
storage: StorageService,
@@ -251,12 +331,14 @@ export async function executeConfiguredBackup(
const destination = requireBackupDestination(currentSettings, destinationId);
const now = new Date();
- destination.runtime.lastAttemptAt = now.toISOString();
- destination.runtime.lastAttemptLocalDate = getBackupLocalDateKey(now, destination.schedule.timezone);
- destination.runtime.lastErrorAt = null;
- destination.runtime.lastErrorMessage = null;
await touchLease();
- await saveBackupSettings(storage, env, currentSettings);
+ destination.runtime = await updateBackupDestinationRuntime(storage, destination.id, (runtime) => ({
+ ...runtime,
+ lastAttemptAt: now.toISOString(),
+ lastAttemptLocalDate: getBackupLocalDateKey(now, destination.schedule.timezone),
+ lastErrorAt: null,
+ lastErrorMessage: null,
+ }));
try {
await touchLease();
@@ -318,6 +400,7 @@ export async function executeConfiguredBackup(
}
}
let upload: Awaited> | null = null;
+ let uploadVerificationMethod: 'metadata' | 'download' | null = null;
for (let attempt = 1; attempt <= maxArchiveUploadAttempts; attempt++) {
await touchLease();
await progress?.({
@@ -337,14 +420,7 @@ export async function executeConfiguredBackup(
stageTitle: 'txt_backup_remote_run_progress_verify_title',
stageDetail: 'txt_backup_remote_run_progress_verify_detail',
});
- const remoteFile = await remoteSession.download(archive.fileName);
- const checksumOk = await verifyBackupArchiveFileNameChecksum(remoteFile.bytes, archive.fileName);
- if (!checksumOk) {
- throw new Error('Remote backup ZIP checksum verification failed');
- }
- if (remoteFile.bytes.byteLength !== archive.bytes.byteLength) {
- throw new Error('Remote backup ZIP size verification failed');
- }
+ uploadVerificationMethod = await verifyUploadedBackupArchive(remoteSession, archive);
break;
} catch (error) {
await remoteSession.deleteFile(archive.fileName).catch(() => undefined);
@@ -373,14 +449,16 @@ export async function executeConfiguredBackup(
pruneErrorMessage = error instanceof Error ? error.message : 'Old backup cleanup failed';
}
- destination.runtime.lastSuccessAt = new Date().toISOString();
- destination.runtime.lastErrorAt = null;
- destination.runtime.lastErrorMessage = null;
- destination.runtime.lastUploadedFileName = archive.fileName;
- destination.runtime.lastUploadedSizeBytes = archive.bytes.byteLength;
- destination.runtime.lastUploadedDestination = upload.remotePath;
await touchLease();
- await saveBackupSettings(storage, env, currentSettings);
+ destination.runtime = await updateBackupDestinationRuntime(storage, destination.id, (runtime) => ({
+ ...runtime,
+ lastSuccessAt: new Date().toISOString(),
+ lastErrorAt: null,
+ lastErrorMessage: null,
+ lastUploadedFileName: archive.fileName,
+ lastUploadedSizeBytes: archive.bytes.byteLength,
+ lastUploadedDestination: upload.remotePath,
+ }));
await touchLease();
await writeAuditLog(storage, actorUserId, `admin.backup.remote.${trigger}`, 'backup', null, {
@@ -390,6 +468,7 @@ export async function executeConfiguredBackup(
fileName: archive.fileName,
fileBytes: archive.bytes.byteLength,
uploadVerificationAttempts: maxArchiveUploadAttempts,
+ uploadVerificationMethod,
prunedFileCount,
pruneError: pruneErrorMessage,
...(auditMetadata || {}),
@@ -412,15 +491,18 @@ export async function executeConfiguredBackup(
provider: upload.provider,
};
} catch (error) {
- destination.runtime.lastErrorAt = new Date().toISOString();
- destination.runtime.lastErrorMessage = error instanceof Error ? error.message : 'Backup upload failed';
+ const errorMessage = error instanceof Error ? error.message : 'Backup upload failed';
await touchLease();
- await saveBackupSettings(storage, env, currentSettings);
+ destination.runtime = await updateBackupDestinationRuntime(storage, destination.id, (runtime) => ({
+ ...runtime,
+ lastErrorAt: new Date().toISOString(),
+ lastErrorMessage: errorMessage,
+ }));
await touchLease();
await writeAuditLog(storage, actorUserId, `admin.backup.remote.${trigger}.failed`, 'backup', null, {
...getBackupDestinationSummary(destination),
- error: destination.runtime.lastErrorMessage,
+ error: errorMessage,
...(auditMetadata || {}),
});
await progress?.({
@@ -431,7 +513,7 @@ export async function executeConfiguredBackup(
stageDetail: 'txt_backup_remote_run_progress_failed_detail',
done: true,
ok: false,
- error: destination.runtime.lastErrorMessage,
+ error: errorMessage,
});
throw error;
}
@@ -591,6 +673,7 @@ function collectExternalRemoteAttachmentBlobNames(archiveBytes: Uint8Array): str
if (parsed.files[inlinePath]) continue;
const ref = refs.get(`${cipherId}/${attachmentId}`);
const blobName = String(ref?.blobName || '').trim();
+ if (!isSafeBackupAttachmentBlobName(blobName)) continue;
if (blobName && !seen.has(blobName)) {
seen.add(blobName);
names.push(blobName);
@@ -603,6 +686,7 @@ function collectExternalRemoteAttachmentBlobNames(archiveBytes: Uint8Array): str
function toImportStatusCode(message: string): number {
const lower = message.toLowerCase();
if (lower.includes('checksum')) return 400;
+ if (lower.includes('invalid remote backup path') || lower.includes('please select a backup zip file')) return 409;
if (lower.includes('invalid backup') || lower.includes('invalid json')) return 400;
if (lower.includes('fresh instance')) return 409;
if (lower.includes('not configured') || lower.includes('kv')) return 409;
@@ -619,12 +703,18 @@ export async function importAndAuditRemoteBackupFile(
replaceExisting: boolean,
checksumMismatchAccepted: boolean,
auditMetadata: Record | null = null,
- targetDeviceIdentifier: string | null = null
+ targetDeviceIdentifier: string | null = null,
+ keepAlive?: (() => Promise) | null
): Promise {
+ const touchLease = async () => {
+ await keepAlive?.();
+ };
const restoreFileName = remoteFile.fileName || remotePath.split('/').pop() || remotePath;
+ await touchLease();
const externalAttachmentBlobNames = collectExternalRemoteAttachmentBlobNames(remoteFile.bytes);
const externalAttachmentCache = new Map();
const progress: BackupRestoreProgressReporter = async (event) => {
+ await touchLease();
await notifyUserBackupRestoreProgress(
env,
actorUserId,
@@ -642,6 +732,7 @@ export async function importAndAuditRemoteBackupFile(
replaceExisting,
{
loadAttachment: async (blobName) => {
+ await touchLease();
const normalized = String(blobName || '').trim();
if (!normalized) return null;
if (externalAttachmentCache.has(normalized)) {
@@ -664,6 +755,7 @@ export async function importAndAuditRemoteBackupFile(
} catch {
externalAttachmentCache.set(normalized, await downloadRemoteAttachmentViaDurableObject(env, destination, normalized).catch(() => null));
}
+ await touchLease();
return externalAttachmentCache.get(normalized) || null;
},
},
@@ -778,7 +870,7 @@ export async function handleGetAdminBackupSettings(request: Request, env: Env, a
const storage = new StorageService(env.DB);
try {
const settings = await loadBackupSettings(storage, env, 'UTC');
- return jsonResponse(settings);
+ return jsonResponse(redactBackupSettingsSecrets(settings));
} catch (error) {
return errorResponse(error instanceof Error ? error.message : 'Backup settings could not be loaded', 409);
}
@@ -787,13 +879,16 @@ export async function handleGetAdminBackupSettings(request: Request, env: Env, a
export async function handleUpdateAdminBackupSettings(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
- let body: BackupSettingsInput;
+ let body: BackupSettingsInput & { masterPasswordHash?: string };
try {
- body = await request.json();
+ body = await request.json();
} catch {
return errorResponse('Backup settings payload is invalid', 400);
}
+ const verificationError = await requireBackupUserVerification(actorUser, String(body.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
const storage = new StorageService(env.DB);
let previous;
try {
@@ -814,7 +909,7 @@ export async function handleUpdateAdminBackupSettings(request: Request, env: Env
destinationCount: next.destinations.length,
scheduledDestinationCount: next.destinations.filter((destination) => destination.schedule.enabled).length,
}, request);
- return jsonResponse(next);
+ return jsonResponse(redactBackupSettingsSecrets(next));
}
export async function handleGetAdminBackupSettingsRepairState(request: Request, env: Env, actorUser: User): Promise {
@@ -837,13 +932,16 @@ export async function handleGetAdminBackupSettingsRepairState(request: Request,
export async function handleRepairAdminBackupSettings(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
- let body: BackupSettingsInput;
+ let body: BackupSettingsInput & { masterPasswordHash?: string; userVerificationToken?: string };
try {
- body = await request.json();
+ body = await request.json();
} catch {
return errorResponse('Backup settings repair payload is invalid', 400);
}
+ const verificationError = await requireBackupRepairVerification(actorUser, body, env);
+ if (verificationError) return verificationError;
+
const storage = new StorageService(env.DB);
let previous;
try {
@@ -864,22 +962,25 @@ export async function handleRepairAdminBackupSettings(request: Request, env: Env
destinationCount: next.destinations.length,
scheduledDestinationCount: next.destinations.filter((destination) => destination.schedule.enabled).length,
}, request);
- return jsonResponse(next);
+ return jsonResponse(redactBackupSettingsSecrets(next));
}
export async function handleRunAdminConfiguredBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
try {
- let body: { destinationId?: string } | null = null;
+ let body: { destinationId?: string; masterPasswordHash?: string } | null = null;
try {
if ((request.headers.get('Content-Type') || '').includes('application/json')) {
- body = await request.json<{ destinationId?: string }>();
+ body = await request.json<{ destinationId?: string; masterPasswordHash?: string }>();
}
} catch {
return errorResponse('Backup run payload is invalid', 400);
}
+ const verificationError = await requireBackupUserVerification(actorUser, String(body?.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
const outcome = await runConfiguredBackupInDurableObject(env, {
actorUserId: actorUser.id,
auditMetadata: auditRequestMetadata(request),
@@ -898,7 +999,7 @@ export async function handleRunAdminConfiguredBackup(request: Request, env: Env,
provider: outcome.result.provider,
remotePath: outcome.result.remotePath,
},
- settings: outcome.settings,
+ settings: redactBackupSettingsSecrets(outcome.settings),
});
} catch (error) {
return errorResponse(error instanceof Error ? error.message : 'Backup run failed', 500);
@@ -928,19 +1029,29 @@ export async function handleListAdminRemoteBackups(request: Request, env: Env, a
export async function handleDownloadAdminRemoteBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
+ let body: { destinationId?: string; path?: string; masterPasswordHash?: string };
+ try {
+ body = await request.json<{ destinationId?: string; path?: string; masterPasswordHash?: string }>();
+ } catch {
+ return errorResponse('Remote backup download payload is invalid', 400);
+ }
+
+ const verificationError = await requireBackupUserVerification(actorUser, String(body.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
const storage = new StorageService(env.DB);
try {
const settings = await loadBackupSettings(storage, env, 'UTC');
- const url = new URL(request.url);
- const path = ensureRemoteRestoreCandidate(url.searchParams.get('path') || '');
- const destination = requireBackupDestination(settings, url.searchParams.get('destinationId') || null);
+ const path = ensureRemoteRestoreCandidate(String(body.path || ''));
+ const destination = requireBackupDestination(settings, body.destinationId || null);
const remoteFile = await downloadRemoteBackupFile(destination, path);
return new Response(remoteFile.bytes, {
status: 200,
headers: {
'Content-Type': remoteFile.contentType || 'application/zip',
- 'Content-Disposition': `attachment; filename="${remoteFile.fileName}"`,
+ 'Content-Disposition': contentDispositionBackup(remoteFile.fileName),
'Cache-Control': 'no-store',
+ 'X-Content-Type-Options': 'nosniff',
},
});
} catch (error) {
@@ -951,12 +1062,21 @@ export async function handleDownloadAdminRemoteBackup(request: Request, env: Env
export async function handleInspectAdminRemoteBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
+ let body: { destinationId?: string; path?: string; masterPasswordHash?: string };
+ try {
+ body = await request.json<{ destinationId?: string; path?: string; masterPasswordHash?: string }>();
+ } catch {
+ return errorResponse('Remote backup integrity payload is invalid', 400);
+ }
+
+ const verificationError = await requireBackupUserVerification(actorUser, String(body.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
const storage = new StorageService(env.DB);
try {
const settings = await loadBackupSettings(storage, env, 'UTC');
- const url = new URL(request.url);
- const path = ensureRemoteRestoreCandidate(url.searchParams.get('path') || '');
- const destination = requireBackupDestination(settings, url.searchParams.get('destinationId') || null);
+ const path = ensureRemoteRestoreCandidate(String(body.path || ''));
+ const destination = requireBackupDestination(settings, body.destinationId || null);
const remoteFile = await downloadRemoteBackupFile(destination, path);
const integrity = await inspectBackupArchiveFileNameChecksum(remoteFile.bytes, remoteFile.fileName || path);
return jsonResponse({
@@ -974,12 +1094,21 @@ export async function handleInspectAdminRemoteBackup(request: Request, env: Env,
export async function handleDeleteAdminRemoteBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
+ let body: { destinationId?: string; path?: string; masterPasswordHash?: string };
+ try {
+ body = await request.json<{ destinationId?: string; path?: string; masterPasswordHash?: string }>();
+ } catch {
+ return errorResponse('Remote backup delete payload is invalid', 400);
+ }
+
+ const verificationError = await requireBackupUserVerification(actorUser, String(body.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
const storage = new StorageService(env.DB);
try {
const settings = await loadBackupSettings(storage, env, 'UTC');
- const url = new URL(request.url);
- const path = ensureRemoteRestoreCandidate(url.searchParams.get('path') || '');
- const destination = requireBackupDestination(settings, url.searchParams.get('destinationId') || null);
+ const path = ensureRemoteRestoreCandidate(String(body.path || ''));
+ const destination = requireBackupDestination(settings, body.destinationId || null);
await deleteRemoteBackupFile(destination, path);
await writeAuditLog(storage, actorUser.id, 'admin.backup.remote.delete', 'backup', null, {
...getBackupDestinationSummary(destination),
@@ -994,13 +1123,22 @@ export async function handleDeleteAdminRemoteBackup(request: Request, env: Env,
export async function handleRestoreAdminRemoteBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
- let body: { destinationId?: string; path?: string; replaceExisting?: boolean; allowChecksumMismatch?: boolean };
+ let body: {
+ destinationId?: string;
+ path?: string;
+ replaceExisting?: boolean;
+ allowChecksumMismatch?: boolean;
+ masterPasswordHash?: string;
+ };
try {
body = await request.json<{ destinationId?: string; path?: string; replaceExisting?: boolean }>();
} catch {
return errorResponse('Remote restore payload is invalid', 400);
}
+ const verificationError = await requireBackupUserVerification(actorUser, String(body.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
+
try {
const path = ensureRemoteRestoreCandidate(String(body.path || ''));
const targetDeviceIdentifier = String(request.headers.get('X-NodeWarden-Acting-Device-Id') || '').trim() || null;
@@ -1028,14 +1166,16 @@ export async function handleAdminExportBackup(request: Request, env: Env, actorU
const storage = new StorageService(env.DB);
const targetDeviceIdentifier = String(request.headers.get('X-NodeWarden-Acting-Device-Id') || '').trim() || null;
- let body: { includeAttachments?: boolean } | null = null;
+ let body: { includeAttachments?: boolean; masterPasswordHash?: string } | null = null;
try {
if ((request.headers.get('Content-Type') || '').includes('application/json')) {
- body = await request.json<{ includeAttachments?: boolean }>();
+ body = await request.json<{ includeAttachments?: boolean; masterPasswordHash?: string }>();
}
} catch {
return errorResponse('Backup export payload is invalid', 400);
}
+ const verificationError = await requireBackupUserVerification(actorUser, String(body?.masterPasswordHash || ''), env);
+ if (verificationError) return verificationError;
let archive: BackupArchiveBundle;
try {
const progress = async (event: {
@@ -1096,8 +1236,9 @@ export async function handleAdminExportBackup(request: Request, env: Env, actorU
status: 200,
headers: {
'Content-Type': 'application/zip',
- 'Content-Disposition': `attachment; filename="${archive.fileName}"`,
+ 'Content-Disposition': contentDispositionBackup(archive.fileName),
'Cache-Control': 'no-store',
+ 'X-Content-Type-Options': 'nosniff',
},
});
}
@@ -1106,8 +1247,24 @@ export async function handleDownloadAdminBackupAttachment(request: Request, env:
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
try {
- const url = new URL(request.url);
- const blobName = ensureBackupBlobName(url.searchParams.get('blobName') || '');
+ // Read the request body only. Accepting these fields from the query string
+ // would put the master-password authentication hash in the URL, where it is
+ // captured by request logs, browser history and Referer headers.
+ let input: { blobName?: unknown; masterPasswordHash?: unknown };
+ try {
+ input = await request.json<{ blobName?: unknown; masterPasswordHash?: unknown }>();
+ } catch {
+ return errorResponse('Backup attachment download payload is invalid', 400);
+ }
+
+ const verificationError = await requireBackupUserVerification(
+ actorUser,
+ String(input.masterPasswordHash || ''),
+ env
+ );
+ if (verificationError) return verificationError;
+
+ const blobName = ensureBackupBlobName(String(input.blobName || ''));
const object = await getBlobObject(env, blobName);
if (!object) {
return errorResponse('Backup attachment blob not found', 404);
@@ -1128,6 +1285,15 @@ export async function handleDownloadAdminBackupAttachment(request: Request, env:
export async function handleAdminImportBackup(request: Request, env: Env, actorUser: User): Promise {
if (!isAdmin(actorUser)) return errorResponse('Forbidden', 403);
+ const contentType = request.headers.get('Content-Type') || '';
+ if (!contentType.includes('multipart/form-data')) {
+ return errorResponse('Content-Type must be multipart/form-data', 400);
+ }
+ const declaredSize = parseRequestContentLength(request);
+ if (declaredSize !== null && declaredSize > getMultipartRequestMaxBytes(MAX_BACKUP_ARCHIVE_BYTES)) {
+ return errorResponse(`Backup file too large. Maximum size is ${Math.floor(MAX_BACKUP_ARCHIVE_BYTES / (1024 * 1024))}MB`, 413);
+ }
+
let formData: FormData;
try {
formData = await request.formData();
@@ -1139,6 +1305,12 @@ export async function handleAdminImportBackup(request: Request, env: Env, actorU
if (!file || typeof file !== 'object' || !('arrayBuffer' in file)) {
return errorResponse('Backup file is required', 400);
}
+ if ('size' in file && typeof (file as File).size === 'number' && (file as File).size > MAX_BACKUP_ARCHIVE_BYTES) {
+ return errorResponse(`Backup file too large. Maximum size is ${Math.floor(MAX_BACKUP_ARCHIVE_BYTES / (1024 * 1024))}MB`, 413);
+ }
+
+ const verificationError = await requireBackupUserVerification(actorUser, String(formData.get('masterPasswordHash') || ''), env);
+ if (verificationError) return verificationError;
const replaceExisting = String(formData.get('replaceExisting') || '').trim() === '1';
const allowChecksumMismatch = String(formData.get('allowChecksumMismatch') || '').trim() === '1';
diff --git a/src/handlers/ciphers.ts b/src/handlers/ciphers.ts
index 1563766..4a01420 100644
--- a/src/handlers/ciphers.ts
+++ b/src/handlers/ciphers.ts
@@ -7,11 +7,20 @@ import {
CipherResponse,
CipherSecureNote,
CipherSshKey,
+ CipherBankAccount,
+ CipherDriversLicense,
+ CipherPassport,
Attachment,
PasswordHistory,
} from '../types';
import { StorageService } from '../services/storage';
-import { notifyUserVaultSync } from '../durable/notifications-hub';
+import {
+ notifyUserCipherCreate,
+ notifyUserCipherDelete,
+ notifyUserCipherUpdate,
+ notifyUserCiphersSync,
+ notifyUserVaultSync,
+} from '../durable/notifications-hub';
import { jsonResponse, errorResponse } from '../utils/response';
import { generateUUID } from '../utils/uuid';
import { deleteAllAttachmentsForCipher, deleteAllAttachmentsForCiphers } from './attachments';
@@ -26,6 +35,7 @@ import { auditRequestMetadata, writeAuditEvent } from '../services/audit-events'
// attachments, import/export, and current official clients.
export interface CipherResponseOptions {
preserveRepairableUris?: boolean;
+ validFolderIds?: ReadonlySet;
}
export function shouldPreserveRepairableCipherUris(request: Request): boolean {
@@ -42,6 +52,28 @@ function normalizeOptionalId(value: unknown): string | null {
return normalized ? normalized : null;
}
+function normalizeResponseFolderId(folderId: unknown, validFolderIds?: ReadonlySet): string | null {
+ const normalized = normalizeOptionalId(folderId);
+ if (!normalized) return null;
+ return validFolderIds && !validFolderIds.has(normalized) ? null : normalized;
+}
+
+function readBooleanOrFallback(value: unknown, fallback: boolean): boolean {
+ return typeof value === 'boolean' ? value : fallback;
+}
+
+function buildCipherPermissions(passthrough: Record): { delete: boolean; restore: boolean } {
+ const raw = passthrough.permissions;
+ const source = raw && typeof raw === 'object' && !Array.isArray(raw)
+ ? raw as Record
+ : null;
+
+ return {
+ delete: readBooleanOrFallback(source?.delete, true),
+ restore: readBooleanOrFallback(source?.restore, true),
+ };
+}
+
function notifyVaultSyncForRequest(
request: Request,
env: Env,
@@ -51,6 +83,60 @@ function notifyVaultSyncForRequest(
notifyUserVaultSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
+function notifyCipherCreateForRequest(
+ request: Request,
+ env: Env,
+ cipher: Cipher,
+ revisionDate: string
+): void {
+ notifyUserCipherCreate(env, {
+ userId: cipher.userId,
+ cipherId: cipher.id,
+ revisionDate,
+ organizationId: normalizeOptionalId((cipher as any).organizationId ?? null),
+ collectionIds: Array.isArray((cipher as any).collectionIds)
+ ? (cipher as any).collectionIds.map((id: unknown) => String(id || '').trim()).filter(Boolean)
+ : null,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
+function notifyCipherUpdateForRequest(
+ request: Request,
+ env: Env,
+ cipher: Cipher,
+ revisionDate: string
+): void {
+ notifyUserCipherUpdate(env, {
+ userId: cipher.userId,
+ cipherId: cipher.id,
+ revisionDate,
+ organizationId: normalizeOptionalId((cipher as any).organizationId ?? null),
+ collectionIds: Array.isArray((cipher as any).collectionIds)
+ ? (cipher as any).collectionIds.map((id: unknown) => String(id || '').trim()).filter(Boolean)
+ : null,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
+function notifyCipherDeleteForRequest(
+ request: Request,
+ env: Env,
+ cipher: Cipher,
+ revisionDate: string
+): void {
+ notifyUserCipherDelete(env, {
+ userId: cipher.userId,
+ cipherId: cipher.id,
+ revisionDate,
+ organizationId: normalizeOptionalId((cipher as any).organizationId ?? null),
+ collectionIds: Array.isArray((cipher as any).collectionIds)
+ ? (cipher as any).collectionIds.map((id: unknown) => String(id || '').trim()).filter(Boolean)
+ : null,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
function getAliasedProp(source: any, aliases: string[]): { present: boolean; value: any } {
if (!source || typeof source !== 'object') return { present: false, value: undefined };
for (const key of aliases) {
@@ -171,6 +257,49 @@ function sanitizeEncryptedObject>(
return next as T;
}
+const BANK_ACCOUNT_ENCRYPTED_KEYS = [
+ 'bankName',
+ 'nameOnAccount',
+ 'accountType',
+ 'accountNumber',
+ 'routingNumber',
+ 'branchNumber',
+ 'pin',
+ 'swiftCode',
+ 'iban',
+ 'bankContactPhone',
+] as const;
+
+const DRIVERS_LICENSE_ENCRYPTED_KEYS = [
+ 'firstName',
+ 'middleName',
+ 'lastName',
+ 'dateOfBirth',
+ 'licenseNumber',
+ 'issuingCountry',
+ 'issuingState',
+ 'issueDate',
+ 'expirationDate',
+ 'issuingAuthority',
+ 'licenseClass',
+] as const;
+
+const PASSPORT_ENCRYPTED_KEYS = [
+ 'surname',
+ 'givenName',
+ 'dateOfBirth',
+ 'sex',
+ 'birthPlace',
+ 'nationality',
+ 'issuingCountry',
+ 'passportNumber',
+ 'passportType',
+ 'nationalIdentificationNumber',
+ 'issuingAuthority',
+ 'issueDate',
+ 'expirationDate',
+] as const;
+
function normalizeCipherForStorage(cipher: Cipher): Cipher {
cipher.login = normalizeCipherLoginForStorage(cipher.login);
cipher.sshKey = normalizeCipherSshKeyForCompatibility(cipher.sshKey);
@@ -271,6 +400,48 @@ export function validateCipherEncryptedFieldsForCompatibility(cipher: Cipher): s
if (uri.uriChecksum != null && !optionalEncStringWithin(uri.uriChecksum, 10000)) return 'Login URI checksum must be an encrypted string up to 10000 characters.';
}
}
+
+ // Validate FIDO2 credentials — all encrypted-string fields, both required and optional, must be valid.
+ if (Array.isArray(login.fido2Credentials)) {
+ const fido2EncryptedKeys = ['credentialId', 'keyType', 'keyAlgorithm', 'keyCurve', 'keyValue', 'rpId', 'counter', 'discoverable', 'userHandle', 'userName', 'rpName', 'userDisplayName'];
+ for (const cred of login.fido2Credentials) {
+ if (!cred || typeof cred !== 'object') continue;
+ for (const key of fido2EncryptedKeys) {
+ if (cred[key] != null && !isValidEncString(cred[key])) return `FIDO2 credential ${key} must be an encrypted string.`;
+ }
+ }
+ }
+ }
+
+ // Validate SSH key fields — all three must be encrypted strings.
+ const sshKey = cipher.sshKey as any;
+ if (sshKey && typeof sshKey === 'object') {
+ if (sshKey.privateKey != null && !isValidEncString(sshKey.privateKey)) return 'SSH key private key must be an encrypted string.';
+ if (sshKey.publicKey != null && !isValidEncString(sshKey.publicKey)) return 'SSH key public key must be an encrypted string.';
+ const fingerprint = sshKey.keyFingerprint ?? sshKey.fingerprint;
+ if (fingerprint != null && !isValidEncString(fingerprint)) return 'SSH key fingerprint must be an encrypted string.';
+ }
+
+ const typedEncryptedObjects: Array<[string, any, readonly string[]]> = [
+ ['Bank account', (cipher as any).bankAccount, BANK_ACCOUNT_ENCRYPTED_KEYS],
+ ['Drivers license', (cipher as any).driversLicense, DRIVERS_LICENSE_ENCRYPTED_KEYS],
+ ['Passport', (cipher as any).passport, PASSPORT_ENCRYPTED_KEYS],
+ ];
+ for (const [label, source, keys] of typedEncryptedObjects) {
+ if (!source || typeof source !== 'object') continue;
+ for (const key of keys) {
+ if (source[key] != null && !optionalEncStringWithin(source[key], 10000)) {
+ return `${label} ${key} must be an encrypted string.`;
+ }
+ }
+ }
+
+ // Validate password history — each password must be an encrypted string.
+ if (Array.isArray(cipher.passwordHistory)) {
+ for (const entry of cipher.passwordHistory) {
+ if (!entry || typeof entry !== 'object') continue;
+ if (entry.password != null && !isValidEncString(entry.password)) return 'Password history entry must be an encrypted string.';
+ }
}
return null;
@@ -641,29 +812,40 @@ export function cipherToResponse(
'licenseNumber',
]);
const normalizedSshKey = normalizeCipherSshKeyForCompatibility((passthrough as any).sshKey ?? null);
- const normalizedSecureNote = Number(cipher.type) === 2
+ const normalizedBankAccount = sanitizeEncryptedObject(
+ (passthrough as any).bankAccount ?? null,
+ BANK_ACCOUNT_ENCRYPTED_KEYS
+ );
+ const normalizedDriversLicense = sanitizeEncryptedObject(
+ (passthrough as any).driversLicense ?? null,
+ DRIVERS_LICENSE_ENCRYPTED_KEYS
+ );
+ const normalizedPassport = sanitizeEncryptedObject(
+ (passthrough as any).passport ?? null,
+ PASSPORT_ENCRYPTED_KEYS
+ );
+ const responseType = Number(cipher.type) || 1;
+ const normalizedSecureNote = responseType === 2
? normalizeCipherSecureNoteForCompatibility((passthrough as any).secureNote ?? null) ?? { type: 0 }
: null;
const responseAttachments = applyCipherEmbeddedAttachmentMetadata(cipher, attachments);
+ const responsePermissions = buildCipherPermissions(passthrough);
return {
// Pass through ALL stored cipher fields (known + unknown)
...passthrough,
// Server-computed / enforced fields (always override)
- folderId: normalizeOptionalId(cipher.folderId),
- type: Number(cipher.type) || 1,
+ folderId: normalizeResponseFolderId(cipher.folderId, options.validFolderIds),
+ type: responseType,
organizationId: normalizeOptionalId((passthrough as any).organizationId ?? null),
organizationUseTotp: !!((passthrough as any).organizationUseTotp ?? false),
creationDate: createdAt,
revisionDate: updatedAt,
deletedDate: deletedAt,
archivedDate: archivedAt ?? null,
- edit: true,
- viewPassword: true,
- permissions: {
- delete: true,
- restore: true,
- },
+ edit: readBooleanOrFallback((passthrough as any).edit, true),
+ viewPassword: readBooleanOrFallback((passthrough as any).viewPassword, true),
+ permissions: responsePermissions,
object: 'cipherDetails',
collectionIds: Array.isArray((passthrough as any).collectionIds) ? (passthrough as any).collectionIds : [],
attachments: formatAttachments(responseAttachments),
@@ -676,6 +858,9 @@ export function cipherToResponse(
fields: normalizeCipherFieldsForCompatibility((passthrough as any).fields),
passwordHistory: normalizePasswordHistoryForCompatibility((passthrough as any).passwordHistory),
sshKey: normalizedSshKey,
+ bankAccount: responseType === 6 ? normalizedBankAccount : null,
+ driversLicense: responseType === 7 ? normalizedDriversLicense : null,
+ passport: responseType === 8 ? normalizedPassport : null,
key: responseCipherKey,
data: typeof (passthrough as any).data === 'string' ? (passthrough as any).data : null,
encryptedFor: (passthrough as any).encryptedFor ?? null,
@@ -711,9 +896,10 @@ export async function handleGetCiphers(request: Request, env: Env, userId: strin
const attachmentsByCipher = await storage.getAttachmentsByCipherIds(
filteredCiphers.map((cipher) => cipher.id)
);
+ const validFolderIds = new Set((await storage.getAllFolders(userId)).map((folder) => folder.id));
// Build responses only for the current page to keep pagination cheap.
- const responseOptions = cipherResponseOptionsForRequest(request);
+ const responseOptions = { ...cipherResponseOptionsForRequest(request), validFolderIds };
const cipherResponses: CipherResponse[] = [];
for (const cipher of filteredCiphers) {
const attachments = attachmentsByCipher.get(cipher.id) || [];
@@ -730,7 +916,7 @@ export async function handleGetCiphers(request: Request, env: Env, userId: strin
// GET /api/ciphers/:id
export async function handleGetCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -745,8 +931,8 @@ export async function handleGetCipher(request: Request, env: Env, userId: string
async function verifyFolderOwnership(storage: StorageService, folderId: string | null | undefined, userId: string): Promise {
if (!folderId) return true;
- const folder = await storage.getFolder(folderId);
- return !!(folder && folder.userId === userId);
+ const folder = await storage.getFolderForUser(folderId, userId);
+ return !!folder;
}
// POST /api/ciphers
@@ -770,6 +956,9 @@ export async function handleCreateCipher(request: Request, env: Env, userId: str
const createIdentity = readCipherProp(cipherData, ['identity', 'Identity']);
const createSecureNote = readCipherProp(cipherData, ['secureNote', 'SecureNote']);
const createSshKey = readCipherProp(cipherData, ['sshKey', 'SshKey']);
+ const createBankAccount = readCipherProp(cipherData, ['bankAccount', 'BankAccount']);
+ const createDriversLicense = readCipherProp(cipherData, ['driversLicense', 'DriversLicense']);
+ const createPassport = readCipherProp(cipherData, ['passport', 'Passport']);
const createPasswordHistory = readCipherProp(cipherData, ['passwordHistory', 'PasswordHistory']);
if (createKey.present && !shouldAcceptCipherKey(createKey.value)) {
@@ -799,6 +988,9 @@ export async function handleCreateCipher(request: Request, env: Env, userId: str
cipher.identity = createIdentity.present ? (createIdentity.value ?? null) : (cipher.identity ?? null);
cipher.secureNote = createSecureNote.present ? (createSecureNote.value ?? null) : (cipher.secureNote ?? null);
cipher.sshKey = createSshKey.present ? (createSshKey.value ?? null) : (cipher.sshKey ?? null);
+ cipher.bankAccount = createBankAccount.present ? (createBankAccount.value ?? null) : ((cipher as any).bankAccount ?? null);
+ cipher.driversLicense = createDriversLicense.present ? (createDriversLicense.value ?? null) : ((cipher as any).driversLicense ?? null);
+ cipher.passport = createPassport.present ? (createPassport.value ?? null) : ((cipher as any).passport ?? null);
cipher.passwordHistory = createPasswordHistory.present ? (createPasswordHistory.value ?? null) : (cipher.passwordHistory ?? null);
const createFields = getAliasedProp(cipherData, ['fields', 'Fields']);
cipher.fields = createFields.present ? (createFields.value ?? null) : (cipher.fields ?? null);
@@ -815,6 +1007,7 @@ export async function handleCreateCipher(request: Request, env: Env, userId: str
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherCreateForRequest(request, env, cipher, revisionDate);
const responseOptions = cipherResponseOptionsForRequest(request);
return jsonResponse(
@@ -826,7 +1019,7 @@ export async function handleCreateCipher(request: Request, env: Env, userId: str
// PUT /api/ciphers/:id
export async function handleUpdateCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const existingCipher = await storage.getCipher(id);
+ const existingCipher = await storage.getCipherForUser(id, userId);
if (!existingCipher || existingCipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -849,6 +1042,9 @@ export async function handleUpdateCipher(request: Request, env: Env, userId: str
const incomingIdentity = readCipherProp(cipherData, ['identity', 'Identity']);
const incomingSecureNote = readCipherProp(cipherData, ['secureNote', 'SecureNote']);
const incomingSshKey = readCipherProp(cipherData, ['sshKey', 'SshKey']);
+ const incomingBankAccount = readCipherProp(cipherData, ['bankAccount', 'BankAccount']);
+ const incomingDriversLicense = readCipherProp(cipherData, ['driversLicense', 'DriversLicense']);
+ const incomingPassport = readCipherProp(cipherData, ['passport', 'Passport']);
const incomingPasswordHistory = readCipherProp(cipherData, ['passwordHistory', 'PasswordHistory']);
const incomingRevisionDate = readCipherRevisionDate(cipherData);
const hasAttachmentMigrationMetadata = hasIncomingAttachmentMetadata(cipherData);
@@ -897,6 +1093,9 @@ export async function handleUpdateCipher(request: Request, env: Env, userId: str
cipher.card = nextType === 3 ? (incomingCard.present ? (incomingCard.value ?? null) : (existingCipher.card ?? null)) : null;
cipher.identity = nextType === 4 ? (incomingIdentity.present ? (incomingIdentity.value ?? null) : (existingCipher.identity ?? null)) : null;
cipher.sshKey = nextType === 5 ? (incomingSshKey.present ? (incomingSshKey.value ?? null) : (existingCipher.sshKey ?? null)) : null;
+ cipher.bankAccount = nextType === 6 ? (incomingBankAccount.present ? (incomingBankAccount.value ?? null) : ((existingCipher as any).bankAccount ?? null)) : null;
+ cipher.driversLicense = nextType === 7 ? (incomingDriversLicense.present ? (incomingDriversLicense.value ?? null) : ((existingCipher as any).driversLicense ?? null)) : null;
+ cipher.passport = nextType === 8 ? (incomingPassport.present ? (incomingPassport.value ?? null) : ((existingCipher as any).passport ?? null)) : null;
if (incomingPasswordHistory.present) {
cipher.passwordHistory = incomingPasswordHistory.value ?? null;
}
@@ -925,6 +1124,7 @@ export async function handleUpdateCipher(request: Request, env: Env, userId: str
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionDate);
const attachments = await storage.getAttachmentsByCipher(cipher.id);
const responseOptions = cipherResponseOptionsForRequest(request);
@@ -936,7 +1136,7 @@ export async function handleUpdateCipher(request: Request, env: Env, userId: str
// DELETE /api/ciphers/:id
export async function handleDeleteCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -949,6 +1149,7 @@ export async function handleDeleteCipher(request: Request, env: Env, userId: str
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherDeleteForRequest(request, env, cipher, revisionDate);
await writeCipherAudit(storage, request, userId, 'cipher.delete.soft', {
id: cipher.id,
type: cipher.type,
@@ -967,7 +1168,7 @@ export async function handleDeleteCipher(request: Request, env: Env, userId: str
// - If item is already soft-deleted -> hard delete.
export async function handleDeleteCipherCompat(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -978,6 +1179,7 @@ export async function handleDeleteCipherCompat(request: Request, env: Env, userI
await storage.deleteCipher(id, userId);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherDeleteForRequest(request, env, cipher, revisionDate);
await writeCipherAudit(storage, request, userId, 'cipher.delete.permanent', {
id,
type: cipher.type,
@@ -993,7 +1195,7 @@ export async function handleDeleteCipherCompat(request: Request, env: Env, userI
// DELETE /api/ciphers/:id (permanent)
export async function handlePermanentDeleteCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -1005,6 +1207,7 @@ export async function handlePermanentDeleteCipher(request: Request, env: Env, us
await storage.deleteCipher(id, userId);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherDeleteForRequest(request, env, cipher, revisionDate);
await writeCipherAudit(storage, request, userId, 'cipher.delete.permanent', {
id,
type: cipher.type,
@@ -1017,7 +1220,7 @@ export async function handlePermanentDeleteCipher(request: Request, env: Env, us
// PUT /api/ciphers/:id/restore
export async function handleRestoreCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -1029,6 +1232,7 @@ export async function handleRestoreCipher(request: Request, env: Env, userId: st
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionDate);
return jsonResponse(
cipherToResponse(cipher, [], cipherResponseOptionsForRequest(request))
@@ -1038,7 +1242,7 @@ export async function handleRestoreCipher(request: Request, env: Env, userId: st
// PUT /api/ciphers/:id/partial - Update only favorite/folderId
export async function handlePartialUpdateCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -1068,6 +1272,7 @@ export async function handlePartialUpdateCipher(request: Request, env: Env, user
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionDate);
return jsonResponse(
cipherToResponse(cipher, [], cipherResponseOptionsForRequest(request))
@@ -1129,7 +1334,7 @@ function parseCipherIdList(body: { ids?: unknown }): string[] | null {
// PUT/POST /api/ciphers/:id/archive
export async function handleArchiveCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -1144,6 +1349,7 @@ export async function handleArchiveCipher(request: Request, env: Env, userId: st
await storage.saveCipher(cipher);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyCipherUpdateForRequest(request, env, cipher, revisionDate);
const attachments = await storage.getAttachmentsByCipher(cipher.id);
return jsonResponse(
@@ -1154,7 +1360,7 @@ export async function handleArchiveCipher(request: Request, env: Env, userId: st
// PUT/POST /api/ciphers/:id/unarchive
export async function handleUnarchiveCipher(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const cipher = await storage.getCipher(id);
+ const cipher = await storage.getCipherForUser(id, userId);
if (!cipher || cipher.userId !== userId) {
return errorResponse('Cipher not found', 404);
@@ -1192,6 +1398,7 @@ export async function handleBulkArchiveCiphers(request: Request, env: Env, userI
const revisionDate = await storage.bulkArchiveCiphers(ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserCiphersSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
return buildCipherListResponse(request, storage, userId, ids);
@@ -1216,6 +1423,7 @@ export async function handleBulkUnarchiveCiphers(request: Request, env: Env, use
const revisionDate = await storage.bulkUnarchiveCiphers(ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserCiphersSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
return buildCipherListResponse(request, storage, userId, ids);
@@ -1239,6 +1447,7 @@ export async function handleBulkDeleteCiphers(request: Request, env: Env, userId
const revisionDate = await storage.bulkSoftDeleteCiphers(body.ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserCiphersSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
await writeCipherAudit(storage, request, userId, 'cipher.delete.soft.bulk', {
count: body.ids.length,
});
@@ -1265,6 +1474,7 @@ export async function handleBulkRestoreCiphers(request: Request, env: Env, userI
const revisionDate = await storage.bulkRestoreCiphers(body.ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserCiphersSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
return new Response(null, { status: 204 });
@@ -1301,6 +1511,7 @@ export async function handleBulkPermanentDeleteCiphers(request: Request, env: En
const revisionDate = await storage.bulkDeleteCiphers(ownedIds, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserCiphersSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
await writeCipherAudit(storage, request, userId, 'cipher.delete.permanent.bulk', {
count: ownedIds.length,
requestedCount: ids.length,
diff --git a/src/handlers/devices.ts b/src/handlers/devices.ts
index 280657d..23bb044 100644
--- a/src/handlers/devices.ts
+++ b/src/handlers/devices.ts
@@ -3,9 +3,10 @@ import { Env } from '../types';
import { getOnlineUserDevices, notifyUserLogout } from '../durable/notifications-hub';
import { AuthService } from '../services/auth';
import { auditRequestMetadata, writeAuditEvent } from '../services/audit-events';
+import { registerMobilePushDevice, unregisterMobilePushDevice } from '../services/push-relay';
import { StorageService } from '../services/storage';
import { errorResponse, jsonResponse } from '../utils/response';
-import { readKnownDeviceProbe } from '../utils/device';
+import { readAuthRequestDeviceInfo, readKnownDeviceProbe } from '../utils/device';
import { generateUUID } from '../utils/uuid';
const PERMANENT_TRUST_EXPIRES_AT_MS = Date.UTC(2099, 11, 31, 23, 59, 59);
@@ -47,6 +48,8 @@ function buildDeviceResponse(device: Device): DeviceResponse {
creationDate: device.createdAt,
RevisionDate: device.updatedAt,
revisionDate: device.updatedAt,
+ LastActivityDate: device.lastSeenAt,
+ lastActivityDate: device.lastSeenAt,
LastSeenAt: device.lastSeenAt,
lastSeenAt: device.lastSeenAt,
HasStoredDevice: true,
@@ -122,6 +125,85 @@ function parseDeviceName(value: unknown): string {
return String(value || '').trim().slice(0, 128);
}
+function parseDeviceType(value: unknown): number | null {
+ if (typeof value === 'number' && Number.isFinite(value)) return Math.max(0, Math.floor(value));
+ const parsed = Number.parseInt(String(value ?? ''), 10);
+ return Number.isFinite(parsed) && parsed >= 0 ? parsed : null;
+}
+
+// POST /api/devices
+export async function handleRegisterDevice(request: Request, env: Env, userId: string): Promise {
+ const body = await readJsonBody(request);
+ if (!body) return errorResponse('Invalid request payload', 400);
+
+ const identifier = normalizeIdentifier(body.identifier ?? body.Identifier ?? body.deviceIdentifier ?? body.DeviceIdentifier);
+ const name = parseDeviceName(body.name ?? body.Name ?? body.deviceName ?? body.DeviceName) || 'Unknown device';
+ const type = parseDeviceType(body.type ?? body.Type ?? body.deviceType ?? body.DeviceType);
+ if (!identifier || type == null) return errorResponse('Device identifier and type are required', 400);
+
+ const storage = new StorageService(env.DB);
+ await storage.upsertDevice(userId, identifier, name, type, undefined, parseKeysBody(body));
+
+ const pushToken = String(body.pushToken ?? body.PushToken ?? '').trim();
+ if (pushToken) {
+ const device = await storage.getDevice(userId, identifier);
+ const pushUuid = device?.pushUuid || generateUUID();
+ const updated = await storage.updateDevicePushToken(userId, identifier, pushUuid, pushToken);
+ if (updated) {
+ await registerMobilePushDevice(env, {
+ userId,
+ deviceIdentifier: identifier,
+ type,
+ pushUuid,
+ pushToken,
+ });
+ }
+ }
+
+ const device = await storage.getDevice(userId, identifier);
+ if (!device) return errorResponse('Device registration failed', 500);
+ await writeAuditEvent(storage, {
+ actorUserId: userId,
+ action: 'device.register',
+ category: 'device',
+ level: 'info',
+ targetType: 'device',
+ targetId: identifier,
+ metadata: auditRequestMetadata(request),
+ });
+ return jsonResponse(buildDeviceResponse(device));
+}
+
+// POST /api/devices/lost-trust
+export async function handleReportLostTrust(request: Request, env: Env, userId: string): Promise {
+ const body = await readJsonBody(request) || {};
+ const deviceInfo = readAuthRequestDeviceInfo(
+ {
+ deviceIdentifier: String(body.identifier ?? body.Identifier ?? body.deviceIdentifier ?? body.DeviceIdentifier ?? ''),
+ deviceName: String(body.name ?? body.Name ?? body.deviceName ?? body.DeviceName ?? ''),
+ deviceType: String(body.type ?? body.Type ?? body.deviceType ?? body.DeviceType ?? ''),
+ },
+ request
+ );
+ if (!deviceInfo.deviceIdentifier) return errorResponse('Please provide a device identifier', 400);
+
+ const storage = new StorageService(env.DB);
+ await writeAuditEvent(storage, {
+ actorUserId: userId,
+ action: 'device.lost_trust',
+ category: 'device',
+ level: 'warn',
+ targetType: 'device',
+ targetId: deviceInfo.deviceIdentifier,
+ metadata: {
+ deviceIdentifier: deviceInfo.deviceIdentifier,
+ deviceType: deviceInfo.deviceType,
+ ...auditRequestMetadata(request),
+ },
+ });
+ return new Response(null, { status: 200 });
+}
+
// GET /api/devices/knowndevice
// Compatible with Bitwarden/Vaultwarden behavior:
// - X-Request-Email: base64url(email) without padding
@@ -223,6 +305,8 @@ export async function handleGetAuthorizedDevices(request: Request, env: Env, use
encryptedUserKey: null,
encryptedPublicKey: null,
encryptedPrivateKey: null,
+ pushUuid: null,
+ pushToken: null,
devicePendingAuthRequest: null,
deviceNote: null,
lastSeenAt: null,
@@ -325,10 +409,12 @@ export async function handleDeleteDevice(
if (!normalized) return errorResponse('Invalid device identifier', 400);
const storage = new StorageService(env.DB);
+ const device = await storage.getDevice(userId, normalized);
await storage.deleteTrustedTwoFactorTokensByDevice(userId, normalized);
await storage.deleteRefreshTokensByDevice(userId, normalized);
const deleted = await storage.deleteDevice(userId, normalized);
if (deleted) {
+ await unregisterMobilePushDevice(env, device?.pushUuid);
AuthService.invalidateDeviceCache(userId, normalized);
notifyUserLogout(env, userId, normalized);
}
@@ -378,11 +464,26 @@ export async function handleUpdateDeviceName(
// DELETE /api/devices
export async function handleDeleteAllDevices(request: Request, env: Env, userId: string): Promise {
- void request;
const storage = new StorageService(env.DB);
const user = await storage.getUserById(userId);
if (!user) return errorResponse('User not found', 404);
+ let masterPasswordHash = '';
+ try {
+ const body = await request.json() as { masterPasswordHash?: string };
+ masterPasswordHash = String(body?.masterPasswordHash || '').trim();
+ } catch {
+ masterPasswordHash = '';
+ }
+ if (!masterPasswordHash) {
+ return errorResponse('masterPasswordHash is required', 400);
+ }
+ const auth = new AuthService(env);
+ const passwordValid = await auth.verifyPassword(masterPasswordHash, user.masterPasswordHash, user.email);
+ if (!passwordValid) {
+ return errorResponse('Invalid password', 400);
+ }
+
const [removedTrusted, removedSessions, removedDevices] = await Promise.all([
storage.deleteTrustedTwoFactorTokensByUserId(userId),
storage.deleteRefreshTokensByUserId(userId),
@@ -537,10 +638,12 @@ export async function handleDeactivateDevice(
if (!normalized) return errorResponse('Invalid device identifier', 400);
const storage = new StorageService(env.DB);
+ const device = await storage.getDevice(userId, normalized);
await storage.deleteTrustedTwoFactorTokensByDevice(userId, normalized);
await storage.deleteRefreshTokensByDevice(userId, normalized);
const deleted = await storage.deleteDevice(userId, normalized);
if (deleted) {
+ await unregisterMobilePushDevice(env, device?.pushUuid);
AuthService.invalidateDeviceCache(userId, normalized);
notifyUserLogout(env, userId, normalized);
}
@@ -557,18 +660,36 @@ export async function handleDeactivateDevice(
}
// PUT /api/devices/identifier/{deviceIdentifier}/token
-// Bitwarden mobile reports push token updates to this endpoint.
-// NodeWarden does not implement push notifications, so accept and no-op.
+// Bitwarden mobile reports APNs/FCM push token updates to this endpoint.
export async function handleUpdateDeviceToken(
request: Request,
env: Env,
userId: string,
deviceIdentifier: string
): Promise {
- void request;
- void env;
- void userId;
- void deviceIdentifier;
+ const normalized = normalizeIdentifier(deviceIdentifier);
+ if (!normalized) return errorResponse('Invalid device identifier', 400);
+
+ const body = await readJsonBody(request);
+ const pushToken = String(body?.pushToken ?? body?.PushToken ?? '').trim();
+ if (!pushToken) return errorResponse('Invalid push token', 400);
+
+ const storage = new StorageService(env.DB);
+ const device = await storage.getDevice(userId, normalized);
+ if (!device) return errorResponse('Device not found', 404);
+
+ const pushUuid = device.pushUuid || generateUUID();
+ const updated = await storage.updateDevicePushToken(userId, normalized, pushUuid, pushToken);
+ if (updated) {
+ await registerMobilePushDevice(env, {
+ userId,
+ deviceIdentifier: normalized,
+ type: device.type,
+ pushUuid,
+ pushToken,
+ });
+ }
+
return new Response(null, { status: 200 });
}
@@ -594,9 +715,15 @@ export async function handleClearDeviceToken(
deviceIdentifier: string
): Promise {
void request;
- void env;
- void userId;
- void deviceIdentifier;
+ const normalized = normalizeIdentifier(deviceIdentifier);
+ if (!normalized) return errorResponse('Invalid device identifier', 400);
+
+ const storage = new StorageService(env.DB);
+ const cleared = await storage.clearDevicePushToken(userId, normalized);
+ if (cleared?.pushUuid) {
+ await unregisterMobilePushDevice(env, cleared.pushUuid);
+ }
+
return new Response(null, { status: 200 });
}
diff --git a/src/handlers/fill-assist.ts b/src/handlers/fill-assist.ts
new file mode 100644
index 0000000..a00c988
--- /dev/null
+++ b/src/handlers/fill-assist.ts
@@ -0,0 +1,80 @@
+const EMPTY_FORMS_FILENAME = 'forms.v1.json';
+const EMPTY_FORMS_SCHEMA_FILENAME = 'forms.v1.schema.json';
+const EMPTY_FORMS_CID = 'sha256:189fa7c9bcf8951e65c18b5d9feacf74a5223c75e01667c4235388cbc67091fe';
+
+const EMPTY_FORMS_BODY = JSON.stringify({
+ schemaVersion: '1.0.0',
+ hosts: {},
+});
+
+const EMPTY_FORMS_SCHEMA_BODY = JSON.stringify({
+ $schema: 'https://json-schema.org/draft/2020-12/schema',
+ title: 'Bitwarden Fill Assist Forms v1',
+ type: 'object',
+ required: ['schemaVersion', 'hosts'],
+ properties: {
+ schemaVersion: { type: 'string' },
+ hosts: { type: 'object' },
+ },
+ additionalProperties: true,
+});
+
+const EMPTY_MANIFEST_BODY = JSON.stringify({
+ buildId: 'nodewarden-empty-fill-assist-v1',
+ timestamp: '2026-07-06T00:00:00.000Z',
+ gitSha: 'nodewarden',
+ maps: {
+ forms: {
+ v1: {
+ filename: EMPTY_FORMS_FILENAME,
+ cid: EMPTY_FORMS_CID,
+ schema: EMPTY_FORMS_SCHEMA_FILENAME,
+ deprecated: false,
+ },
+ },
+ },
+});
+
+const DIGITAL_ASSET_LINK_CHECK_BODY = JSON.stringify({
+ linked: false,
+ maxAge: '86400s',
+ debugString: 'No matching digital asset link policy is configured for this server.',
+});
+
+function fillAssistJsonResponse(body: string): Response {
+ return new Response(body, {
+ status: 200,
+ headers: {
+ 'Content-Type': 'application/json; charset=utf-8',
+ 'Cache-Control': 'public, max-age=3600',
+ },
+ });
+}
+
+function normalizeFilename(filename: string): string {
+ const raw = String(filename || '').trim();
+ try {
+ return decodeURIComponent(raw);
+ } catch {
+ return raw;
+ }
+}
+
+export function handleFillAssistManifest(): Response {
+ return fillAssistJsonResponse(EMPTY_MANIFEST_BODY);
+}
+
+export function handleFillAssistForms(filename: string): Response {
+ const normalized = normalizeFilename(filename);
+ if (normalized === EMPTY_FORMS_FILENAME) {
+ return fillAssistJsonResponse(EMPTY_FORMS_BODY);
+ }
+ if (normalized === EMPTY_FORMS_SCHEMA_FILENAME) {
+ return fillAssistJsonResponse(EMPTY_FORMS_SCHEMA_BODY);
+ }
+ return new Response('Not found', { status: 404 });
+}
+
+export function handleDigitalAssetLinkCheck(): Response {
+ return fillAssistJsonResponse(DIGITAL_ASSET_LINK_CHECK_BODY);
+}
diff --git a/src/handlers/folders.ts b/src/handlers/folders.ts
index 08ce5a5..d89dbb9 100644
--- a/src/handlers/folders.ts
+++ b/src/handlers/folders.ts
@@ -1,5 +1,10 @@
import { Env, Folder, FolderResponse } from '../types';
-import { notifyUserVaultSync } from '../durable/notifications-hub';
+import {
+ notifyUserFolderCreate,
+ notifyUserFolderDelete,
+ notifyUserFolderUpdate,
+ notifyUserVaultSync,
+} from '../durable/notifications-hub';
import { StorageService } from '../services/storage';
import { jsonResponse, errorResponse } from '../utils/response';
import { readActingDeviceIdentifier } from '../utils/device';
@@ -75,7 +80,7 @@ export async function handleGetFolders(request: Request, env: Env, userId: strin
// GET /api/folders/:id
export async function handleGetFolder(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const folder = await storage.getFolder(id);
+ const folder = await storage.getFolderForUser(id, userId);
if (!folder || folder.userId !== userId) {
return errorResponse('Folder not found', 404);
@@ -111,6 +116,12 @@ export async function handleCreateFolder(request: Request, env: Env, userId: str
await storage.saveFolder(folder);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserFolderCreate(env, {
+ userId,
+ folderId: folder.id,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
return jsonResponse(folderToResponse(folder), 200);
}
@@ -118,7 +129,7 @@ export async function handleCreateFolder(request: Request, env: Env, userId: str
// PUT /api/folders/:id
export async function handleUpdateFolder(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const folder = await storage.getFolder(id);
+ const folder = await storage.getFolderForUser(id, userId);
if (!folder || folder.userId !== userId) {
return errorResponse('Folder not found', 404);
@@ -139,6 +150,12 @@ export async function handleUpdateFolder(request: Request, env: Env, userId: str
await storage.saveFolder(folder);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserFolderUpdate(env, {
+ userId,
+ folderId: folder.id,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
return jsonResponse(folderToResponse(folder));
}
@@ -146,7 +163,7 @@ export async function handleUpdateFolder(request: Request, env: Env, userId: str
// DELETE /api/folders/:id
export async function handleDeleteFolder(request: Request, env: Env, userId: string, id: string): Promise {
const storage = new StorageService(env.DB);
- const folder = await storage.getFolder(id);
+ const folder = await storage.getFolderForUser(id, userId);
if (!folder || folder.userId !== userId) {
return errorResponse('Folder not found', 404);
@@ -156,6 +173,12 @@ export async function handleDeleteFolder(request: Request, env: Env, userId: str
await storage.deleteFolder(id, userId);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifyUserFolderDelete(env, {
+ userId,
+ folderId: id,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
await writeFolderAudit(storage, request, userId, 'folder.delete', {
id,
});
@@ -179,9 +202,23 @@ export async function handleBulkDeleteFolders(request: Request, env: Env, userId
return errorResponse('Folder ids are required', 400);
}
+ const folders = (
+ await Promise.all(ids.map(async (id) => {
+ const folder = await storage.getFolderForUser(id, userId);
+ return folder;
+ }))
+ ).filter((folder): folder is Folder => !!folder);
const revisionDate = await storage.bulkDeleteFolders(ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ for (const folder of folders) {
+ notifyUserFolderDelete(env, {
+ userId,
+ folderId: folder.id,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
+ }
await writeFolderAudit(storage, request, userId, 'folder.delete.bulk', {
count: ids.length,
});
diff --git a/src/handlers/identity.ts b/src/handlers/identity.ts
index f801883..f97036b 100644
--- a/src/handlers/identity.ts
+++ b/src/handlers/identity.ts
@@ -1,15 +1,16 @@
-import { Env, TokenResponse } from '../types';
+import { Env, TokenResponse, User } from '../types';
import { StorageService } from '../services/storage';
import { AuthService } from '../services/auth';
import { RateLimitService, getClientIdentifier } from '../services/ratelimit';
import { jsonResponse, errorResponse, identityErrorResponse } from '../utils/response';
-import { LIMITS } from '../config/limits';
-import { isTotpEnabled, verifyTotpToken } from '../utils/totp';
+import { getRefreshTokenSlidingTtlMs, LIMITS } from '../config/limits';
+import { findMatchingTotpCounter, isTotpEnabled } from '../utils/totp';
import { createRefreshToken } from '../utils/jwt';
import { readAuthRequestDeviceInfo } from '../utils/device';
import { createRecoveryCode, recoveryCodeEquals } from '../utils/recovery-code';
import { generateUUID } from '../utils/uuid';
import { issueSendAccessToken } from './sends';
+import { registerMobilePushDevice } from '../services/push-relay';
import {
buildAccountKeys,
buildUserDecryptionOptions,
@@ -17,13 +18,21 @@ import {
import { auditRequestMetadata, safeWriteAuditEvent } from '../services/audit-events';
import {
assertAccountPasskeyCredential,
+ assertTwoFactorPasskeyCredential,
buildAccountPasskeyTokenUserDecryptionOption,
+ buildTwoFactorPasskeyAssertionOptions,
} from './account-passkeys';
import { isAuthRequestExpired } from '../services/storage-auth-request-repo';
+import { createPasskeyUserVerificationToken } from '../utils/user-verification-token';
+import { constantTimeEquals, verifyApiKey } from '../utils/api-key';
+import { isYubiKeyEnabled, userYubiKeyPublicIds, verifyYubicoOtp, yubiKeyPublicIdFromOtp } from '../utils/yubico-otp';
+import { getYubicoCredentials, initializeYubicoCredentialsOnce } from '../services/yubico-config';
const TWO_FACTOR_REMEMBER_TTL_MS = 30 * 24 * 60 * 60 * 1000;
const TWO_FACTOR_PROVIDER_AUTHENTICATOR = 0;
+const TWO_FACTOR_PROVIDER_YUBIKEY = 3;
const TWO_FACTOR_PROVIDER_REMEMBER = 5;
+const TWO_FACTOR_PROVIDER_WEBAUTHN = 7;
const TWO_FACTOR_PROVIDER_RECOVERY_CODE = 8;
const WEB_REFRESH_COOKIE = 'nodewarden_web_refresh';
// Some UI surfaces use -1 for the recovery-code settings dialog. Login itself follows
@@ -32,6 +41,10 @@ const WEB_REFRESH_COOKIE = 'nodewarden_web_refresh';
const TWO_FACTOR_PROVIDER_RECOVERY_CODE_RESPONSE = '-1';
const TWO_FACTOR_PROVIDER_RECOVERY_CODE_ANDROID_REQUEST = 100;
+function identityJsonResponse(data: unknown, status: number = 200): Response {
+ return jsonResponse(data, status, { 'Cache-Control': 'no-store', Pragma: 'no-cache' });
+}
+
function resolveTotpSecret(userSecret: string | null): string | null {
if (userSecret && isTotpEnabled(userSecret)) {
return userSecret;
@@ -50,6 +63,71 @@ async function resolveDeviceSession(
return { identifier: deviceInfo.deviceIdentifier, sessionStamp };
}
+function resolveRefreshClientType(request: Request, body: Record): string {
+ if (shouldUseWebSession(request)) return 'web';
+ const clientId = String(body.client_id || '').trim().toLowerCase();
+ if (clientId === 'mobile') return 'mobile';
+ if (clientId === 'browser' || clientId === 'desktop' || clientId === 'cli') return clientId;
+ return clientId || 'other';
+}
+
+async function persistAndResolveDeviceSession(
+ storage: StorageService,
+ userId: string,
+ deviceInfo: ReturnType
+): Promise<{ identifier: string; sessionStamp: string } | null> {
+ const candidate = await resolveDeviceSession(storage, userId, deviceInfo);
+ if (!candidate) return null;
+ await storage.upsertDevice(
+ userId,
+ candidate.identifier,
+ deviceInfo.deviceName,
+ deviceInfo.deviceType,
+ candidate.sessionStamp
+ );
+ const persisted = await storage.getDevice(userId, candidate.identifier);
+ if (!persisted?.sessionStamp) throw new Error('Failed to persist device session');
+ return { identifier: persisted.deviceIdentifier, sessionStamp: persisted.sessionStamp };
+}
+
+function readDevicePushToken(body: Record): string {
+ return String(readBodyValue(body, ['devicePushToken', 'DevicePushToken', 'device_push_token']) || '').trim();
+}
+
+async function persistIdentityDevicePushToken(
+ env: Env,
+ storage: StorageService,
+ userId: string,
+ deviceSession: { identifier: string; sessionStamp: string } | null,
+ deviceType: number,
+ body: Record
+): Promise {
+ if (!deviceSession) return;
+ const pushToken = readDevicePushToken(body);
+ if (!pushToken) return;
+
+ const device = await storage.getDevice(userId, deviceSession.identifier);
+ if (!device) return;
+
+ const pushUuid = device.pushUuid || generateUUID();
+ await storage.updateDevicePushToken(userId, deviceSession.identifier, pushUuid, pushToken);
+ const registered = await registerMobilePushDevice(env, {
+ userId,
+ deviceIdentifier: deviceSession.identifier,
+ type: device.type || deviceType,
+ pushUuid,
+ pushToken,
+ });
+ console.info('Mobile push token updated from identity token request', {
+ userId,
+ deviceIdentifier: deviceSession.identifier,
+ deviceType: device.type || deviceType,
+ pushUuid,
+ pushTokenLength: pushToken.length,
+ relayRegistered: registered,
+ });
+}
+
function shouldUseWebSession(request: Request): boolean {
return String(request.headers.get('X-NodeWarden-Web-Session') || '').trim() === '1';
}
@@ -66,18 +144,6 @@ function parseCookieValue(request: Request, name: string): string | null {
return null;
}
-function constantTimeEquals(a: string, b: string): boolean {
- const encA = new TextEncoder().encode(a);
- const encB = new TextEncoder().encode(b);
- if (encA.length !== encB.length) return false;
-
- let diff = 0;
- for (let i = 0; i < encA.length; i++) {
- diff |= encA[i] ^ encB[i];
- }
- return diff === 0;
-}
-
function readBodyValue(body: Record, names: string[]): string | undefined {
for (const name of names) {
const value = body[name];
@@ -86,6 +152,16 @@ function readBodyValue(body: Record, names: string[]): string |
return undefined;
}
+async function sha256Hex(value: string): Promise {
+ const digest = await crypto.subtle.digest('SHA-256', new TextEncoder().encode(value));
+ return Array.from(new Uint8Array(digest), (byte) => byte.toString(16).padStart(2, '0')).join('');
+}
+
+async function loginRateLimitKey(clientIdentifier: string, grantType: string, subject: string): Promise {
+ const subjectHash = await sha256Hex(`${grantType}:${String(subject || '').trim() || 'unknown'}`);
+ return `${clientIdentifier}:login:${grantType}:${subjectHash}`;
+}
+
function buildRefreshCookie(request: Request, refreshToken: string, maxAgeSeconds: number): string {
const isHttps = new URL(request.url).protocol === 'https:';
const parts = [
@@ -108,7 +184,7 @@ function withWebRefreshCookie(request: Request, response: Response, refreshToken
headers.append(
'Set-Cookie',
refreshToken
- ? buildRefreshCookie(request, refreshToken, Math.floor(LIMITS.auth.refreshTokenTtlMs / 1000))
+ ? buildRefreshCookie(request, refreshToken, Math.floor(getRefreshTokenSlidingTtlMs('web') / 1000))
: buildClearedRefreshCookie(request)
);
return new Response(response.body, {
@@ -130,6 +206,16 @@ function buildPreloginResponse(
kdfIterations,
kdfMemory,
kdfParallelism,
+ // Current official servers expose the consolidated KDF model alongside
+ // the legacy flat fields. Keep both shapes while clients migrate.
+ kdfSettings: {
+ kdfType,
+ iterations: kdfIterations,
+ memory: kdfMemory,
+ parallelism: kdfParallelism,
+ },
+ salt: null,
+ // Preserve the historic NodeWarden aliases for older integrations.
KdfSettings: {
KdfType: kdfType,
Iterations: kdfIterations,
@@ -140,24 +226,55 @@ function buildPreloginResponse(
};
}
-function twoFactorRequiredResponse(message: string = 'Two factor required.'): Response {
+function masterPasswordPolicyResponse(): TokenResponse['MasterPasswordPolicy'] {
+ return {
+ minComplexity: 0,
+ minLength: 0,
+ requireUpper: false,
+ requireLower: false,
+ requireNumbers: false,
+ requireSpecial: false,
+ enforceOnLogin: false,
+ Object: 'masterPasswordPolicy',
+ object: 'masterPasswordPolicy',
+ };
+}
+
+async function twoFactorRequiredResponse(
+ request: Request,
+ env: Env,
+ storage: StorageService,
+ user?: User,
+ message: string = 'Two factor required.'
+): Promise {
// Match Bitwarden Identity: TwoFactorProviders2 lists enabled 2FA providers only.
// Clients expose recovery-code entry points themselves; Android 2026.4 fails to
// parse the challenge if an unknown recovery provider key such as "8" is included.
- const providers = [String(TWO_FACTOR_PROVIDER_AUTHENTICATOR)];
- const providers2: Record = {};
- for (const provider of providers) providers2[provider] = { Email: null };
+ const providers: string[] = [];
+ let webAuthnOptions: Record | null = null;
+ if (!user || resolveTotpSecret(user.totpSecret)) providers.push(String(TWO_FACTOR_PROVIDER_AUTHENTICATOR));
+ if (user && isYubiKeyEnabled(user)) providers.push(String(TWO_FACTOR_PROVIDER_YUBIKEY));
+ if (user) {
+ webAuthnOptions = await buildTwoFactorPasskeyAssertionOptions(request, env, storage, user) as Record | null;
+ if (webAuthnOptions) providers.push(String(TWO_FACTOR_PROVIDER_WEBAUTHN));
+ }
+ const providers2: Record | null> = {};
+ for (const provider of providers) {
+ providers2[provider] = provider === String(TWO_FACTOR_PROVIDER_YUBIKEY)
+ ? { Nfc: user?.yubikeyNfc ?? false }
+ : provider === String(TWO_FACTOR_PROVIDER_WEBAUTHN) && webAuthnOptions
+ ? webAuthnOptions
+ : null;
+ }
const customResponse = {
TwoFactorProviders: providers,
TwoFactorProviders2: providers2,
SsoEmail2faSessionToken: null,
- MasterPasswordPolicy: {
- Object: 'masterPasswordPolicy',
- },
+ MasterPasswordPolicy: masterPasswordPolicyResponse(),
};
// Bitwarden clients rely on these fields to trigger the 2FA UI flow.
- return jsonResponse(
+ return identityJsonResponse(
{
error: 'invalid_grant',
error_description: message,
@@ -231,8 +348,20 @@ export async function handleToken(request: Request, env: Env): Promise
const grantType = body.grant_type;
const clientIdentifier = getClientIdentifier(request);
- if (!clientIdentifier) {
- return identityErrorResponse('Client IP is required', 'invalid_request', 403);
+ if (!clientIdentifier && grantType !== 'refresh_token') {
+ await safeWriteAuditEvent(env, {
+ action: 'auth.client_ip.missing',
+ category: 'auth',
+ level: 'error',
+ targetType: 'tokenEndpoint',
+ metadata: { grantType, reason: 'client_ip_missing', ...auditRequestMetadata(request) },
+ });
+ return identityErrorResponse(
+ 'Authentication is temporarily unavailable',
+ 'temporarily_unavailable',
+ 503,
+ { 'Retry-After': '5' }
+ );
}
if (grantType === 'password') {
@@ -243,13 +372,13 @@ export async function handleToken(request: Request, env: Env): Promise
const twoFactorToken = readBodyValue(body, ['twoFactorToken', 'TwoFactorToken']);
const twoFactorProvider = readBodyValue(body, ['twoFactorProvider', 'TwoFactorProvider']);
const twoFactorRemember = readBodyValue(body, ['twoFactorRemember', 'TwoFactorRemember']);
- const loginIdentifier = clientIdentifier;
const deviceInfo = readAuthRequestDeviceInfo(body, request);
if (!email || !passwordHash) {
// Bitwarden clients expect OAuth-style error fields.
return identityErrorResponse('Email and password are required', 'invalid_request', 400);
}
+ const loginIdentifier = await loginRateLimitKey(clientIdentifier!, grantType, email);
// Check login lockout before user lookup to reduce user-enumeration signal
const loginCheck = await rateLimit.checkLoginAttempt(loginIdentifier);
@@ -285,10 +414,11 @@ export async function handleToken(request: Request, env: Env): Promise
}
let validatedAuthRequestId: string | null = null;
+ let authRequestLoginKey: string | null = null;
let valid = false;
const normalizedAuthRequestId = String(authRequestId || '').trim();
if (normalizedAuthRequestId) {
- const authRequest = await storage.getAuthRequestById(normalizedAuthRequestId);
+ const authRequest = await storage.getAuthRequestByIdForUser(normalizedAuthRequestId, user.id);
valid = !!(
authRequest &&
authRequest.userId === user.id &&
@@ -297,10 +427,12 @@ export async function handleToken(request: Request, env: Env): Promise
authRequest.responseDate &&
!authRequest.authenticationDate &&
!isAuthRequestExpired(authRequest) &&
+ !!authRequest.key &&
constantTimeEquals(authRequest.accessCode, passwordHash)
);
if (valid) {
validatedAuthRequestId = authRequest!.id;
+ authRequestLoginKey = authRequest!.key;
}
} else {
valid = await auth.verifyPassword(passwordHash, user.masterPasswordHash, user.email);
@@ -326,10 +458,12 @@ export async function handleToken(request: Request, env: Env): Promise
);
}
- // Optional 2FA: enabled only by per-user secret.
+ // Optional 2FA: enabled by any supported per-user provider.
let trustedTwoFactorTokenToReturn: string | undefined;
const effectiveTotpSecret = resolveTotpSecret(user.totpSecret);
- if (effectiveTotpSecret) {
+ const effectiveYubiKeyPublicIds = userYubiKeyPublicIds(user);
+ const effectiveWebAuthnCredentials = await storage.getAccountPasskeyCredentialsByUserId(user.id, 'twoFactor');
+ if (effectiveTotpSecret || effectiveYubiKeyPublicIds.length > 0 || effectiveWebAuthnCredentials.length > 0) {
const normalizedTwoFactorProvider = String(twoFactorProvider ?? '').trim();
const normalizedTwoFactorToken = String(twoFactorToken ?? '').trim();
let rememberRequested = ['1', 'true', 'True', 'TRUE', 'on', 'yes', 'Yes', 'YES'].includes(String(twoFactorRemember || '').trim());
@@ -339,7 +473,7 @@ export async function handleToken(request: Request, env: Env): Promise
// Upstream-compatible behavior: if 2FA is required and either provider or token is missing,
// respond with a 2FA challenge payload.
if (!hasProvider || !hasToken) {
- return twoFactorRequiredResponse('Two factor required.');
+ return await twoFactorRequiredResponse(request, env, storage, user, 'Two factor required.');
}
let passedByRememberToken = false;
@@ -354,11 +488,51 @@ export async function handleToken(request: Request, env: Env): Promise
// Remember token missing/invalid/expired should re-enter the 2FA challenge flow.
if (!passedByRememberToken) {
- return twoFactorRequiredResponse('Two factor required.');
+ return await twoFactorRequiredResponse(request, env, storage, user, 'Two factor required.');
}
} else if (normalizedTwoFactorProvider === String(TWO_FACTOR_PROVIDER_AUTHENTICATOR)) {
- const totpOk = await verifyTotpToken(effectiveTotpSecret, normalizedTwoFactorToken);
- if (!totpOk) {
+ if (!effectiveTotpSecret) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ const matchedCounter = await findMatchingTotpCounter(effectiveTotpSecret, normalizedTwoFactorToken);
+ if (matchedCounter == null) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ const consumed = await storage.consumeTotpLoginCounter(user.id, matchedCounter);
+ if (!consumed) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ } else if (normalizedTwoFactorProvider === String(TWO_FACTOR_PROVIDER_YUBIKEY)) {
+ const publicId = yubiKeyPublicIdFromOtp(normalizedTwoFactorToken);
+ if (!publicId || !effectiveYubiKeyPublicIds.includes(publicId)) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ let credentials = await getYubicoCredentials(env.DB);
+ let initializedWithCurrentOtp = false;
+ if (!credentials) {
+ const initialized = await initializeYubicoCredentialsOnce(env.DB, user.email, normalizedTwoFactorToken);
+ if (!initialized) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ credentials = initialized.credentials;
+ initializedWithCurrentOtp = initialized.created;
+ }
+ if (!initializedWithCurrentOtp && !await verifyYubicoOtp(env, normalizedTwoFactorToken, credentials)) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ } else if (normalizedTwoFactorProvider === String(TWO_FACTOR_PROVIDER_WEBAUTHN)) {
+ if (!effectiveWebAuthnCredentials.length) {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ let deviceResponse: unknown;
+ try {
+ deviceResponse = JSON.parse(normalizedTwoFactorToken);
+ } catch {
+ return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
+ }
+ try {
+ await assertTwoFactorPasskeyCredential(request, env, storage, user, deviceResponse);
+ } catch {
return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
}
} else if (
@@ -370,10 +544,21 @@ export async function handleToken(request: Request, env: Env): Promise
return recordFailedTwoFactorAndBuildResponse(rateLimit, loginIdentifier);
}
user.totpSecret = null;
+ user.yubikeyKey1 = null;
+ user.yubikeyKey2 = null;
+ user.yubikeyKey3 = null;
+ user.yubikeyKey4 = null;
+ user.yubikeyKey5 = null;
+ user.yubikeyNfc = false;
+ for (const credential of effectiveWebAuthnCredentials) {
+ await storage.deleteAccountPasskeyCredential(user.id, credential.id, 'twoFactor');
+ }
user.totpRecoveryCode = createRecoveryCode();
+ user.securityStamp = generateUUID();
user.updatedAt = new Date().toISOString();
await storage.saveUser(user);
await storage.deleteRefreshTokensByUserId(user.id);
+ AuthService.invalidateUserCache(user.id);
rememberRequested = false;
} else {
// Unsupported provider for this server profile behaves as an invalid 2FA attempt.
@@ -393,15 +578,9 @@ export async function handleToken(request: Request, env: Env): Promise
}
// Persist device only after successful password + (optional) 2FA verification.
- const deviceSession = await resolveDeviceSession(storage, user.id, deviceInfo);
+ const deviceSession = await persistAndResolveDeviceSession(storage, user.id, deviceInfo);
if (deviceSession) {
- await storage.upsertDevice(
- user.id,
- deviceSession.identifier,
- deviceInfo.deviceName,
- deviceInfo.deviceType,
- deviceSession.sessionStamp
- );
+ await persistIdentityDevicePushToken(env, storage, user.id, deviceSession, deviceInfo.deviceType, body);
}
// Successful login - clear failed attempts
@@ -411,7 +590,7 @@ export async function handleToken(request: Request, env: Env): Promise
}
const accessToken = await auth.generateAccessToken(user, deviceSession);
- const refreshToken = await auth.generateRefreshToken(user.id, deviceSession);
+ const refreshToken = await auth.generateRefreshToken(user, deviceSession, resolveRefreshClientType(request, body));
const accountKeys = buildAccountKeys(user);
const userDecryptionOptions = buildUserDecryptionOptions(user);
await safeWriteAuditEvent(env, {
@@ -436,7 +615,7 @@ export async function handleToken(request: Request, env: Env): Promise
token_type: 'Bearer',
...(shouldUseWebSession(request) ? { web_session: true } : { refresh_token: refreshToken }),
...(trustedTwoFactorTokenToReturn ? { TwoFactorToken: trustedTwoFactorTokenToReturn } : {}),
- Key: user.key,
+ Key: authRequestLoginKey || user.key,
PrivateKey: user.privateKey,
AccountKeys: accountKeys,
accountKeys: accountKeys,
@@ -446,9 +625,7 @@ export async function handleToken(request: Request, env: Env): Promise
KdfParallelism: user.kdfParallelism,
ForcePasswordReset: false,
ResetMasterPassword: false,
- MasterPasswordPolicy: {
- Object: 'masterPasswordPolicy',
- },
+ MasterPasswordPolicy: masterPasswordPolicyResponse(),
ApiUseKeyConnector: false,
scope: 'api offline_access',
unofficialServer: true,
@@ -456,13 +633,14 @@ export async function handleToken(request: Request, env: Env): Promise
userDecryptionOptions: userDecryptionOptions,
};
- const baseResponse = jsonResponse(response);
+ const baseResponse = identityJsonResponse(response);
return shouldUseWebSession(request)
? withWebRefreshCookie(request, baseResponse, refreshToken)
: baseResponse;
} else if (grantType === 'webauthn') {
- const loginIdentifier = clientIdentifier;
+ const token = String(body.token || '').trim();
+ const loginIdentifier = await loginRateLimitKey(clientIdentifier!, grantType, token || 'missing-token');
const loginCheck = await rateLimit.checkLoginAttempt(loginIdentifier);
if (!loginCheck.allowed) {
return identityErrorResponse(
@@ -472,7 +650,6 @@ export async function handleToken(request: Request, env: Env): Promise
);
}
- const token = String(body.token || '').trim();
let deviceResponse: unknown = body.deviceResponse;
if (typeof deviceResponse === 'string') {
try {
@@ -517,21 +694,16 @@ export async function handleToken(request: Request, env: Env): Promise
}
const deviceInfo = readAuthRequestDeviceInfo(body, request);
- const deviceSession = await resolveDeviceSession(storage, user.id, deviceInfo);
+ const deviceSession = await persistAndResolveDeviceSession(storage, user.id, deviceInfo);
if (deviceSession) {
- await storage.upsertDevice(
- user.id,
- deviceSession.identifier,
- deviceInfo.deviceName,
- deviceInfo.deviceType,
- deviceSession.sessionStamp
- );
+ await persistIdentityDevicePushToken(env, storage, user.id, deviceSession, deviceInfo.deviceType, body);
}
await rateLimit.clearLoginAttempts(loginIdentifier);
const accessToken = await auth.generateAccessToken(user, deviceSession);
- const refreshToken = await auth.generateRefreshToken(user.id, deviceSession);
+ const refreshToken = await auth.generateRefreshToken(user, deviceSession, resolveRefreshClientType(request, body));
+ const userVerificationToken = await createPasskeyUserVerificationToken(env, user.id, 'backup.settings.repair');
const accountKeys = buildAccountKeys(user);
const webAuthnPrfOption = buildAccountPasskeyTokenUserDecryptionOption(credential);
const userDecryptionOptions = buildUserDecryptionOptions(user, webAuthnPrfOption);
@@ -566,17 +738,17 @@ export async function handleToken(request: Request, env: Env): Promise
KdfParallelism: user.kdfParallelism,
ForcePasswordReset: false,
ResetMasterPassword: false,
- MasterPasswordPolicy: {
- Object: 'masterPasswordPolicy',
- },
+ MasterPasswordPolicy: masterPasswordPolicyResponse(),
ApiUseKeyConnector: false,
scope: 'api offline_access',
unofficialServer: true,
+ UserVerificationToken: userVerificationToken,
+ userVerificationToken,
UserDecryptionOptions: userDecryptionOptions,
userDecryptionOptions: userDecryptionOptions,
};
- const baseResponse = jsonResponse(response);
+ const baseResponse = identityJsonResponse(response);
return shouldUseWebSession(request)
? withWebRefreshCookie(request, baseResponse, refreshToken)
: baseResponse;
@@ -588,11 +760,12 @@ export async function handleToken(request: Request, env: Env): Promise
const scope = body.scope;
const deviceInfo = readAuthRequestDeviceInfo(body, request);
- const loginIdentifier = clientIdentifier;
const parmValid = checkClientCredentialsParam(clientId, clientSecret, scope);
if (!parmValid) {
return identityErrorResponse('Parameter error', 'invalid_request', 400);
}
+ const uid = clientId.slice(5);
+ const loginIdentifier = await loginRateLimitKey(clientIdentifier!, grantType, uid);
// Check login lockout before user lookup to reduce user-enumeration signal
const loginCheck = await rateLimit.checkLoginAttempt(loginIdentifier);
@@ -604,7 +777,6 @@ export async function handleToken(request: Request, env: Env): Promise
);
}
- const uid = clientId.slice(5);
const user = await storage.getUserById(uid);
if (!user) {
await rateLimit.recordFailedLogin(loginIdentifier);
@@ -628,7 +800,7 @@ export async function handleToken(request: Request, env: Env): Promise
return identityErrorResponse('Account is disabled', 'invalid_grant', 400);
}
- if (!user.apiKey || !constantTimeEquals(clientSecret, user.apiKey)) {
+ if (!user.apiKey || !(await verifyApiKey(clientSecret, user.apiKey))) {
await rateLimit.recordFailedLogin(loginIdentifier);
await safeWriteAuditEvent(env, {
actorUserId: user.id,
@@ -647,22 +819,16 @@ export async function handleToken(request: Request, env: Env): Promise
}
// Persist device only after successful client credential verification.
- const deviceSession = await resolveDeviceSession(storage, user.id, deviceInfo);
+ const deviceSession = await persistAndResolveDeviceSession(storage, user.id, deviceInfo);
if (deviceSession) {
- await storage.upsertDevice(
- user.id,
- deviceSession.identifier,
- deviceInfo.deviceName,
- deviceInfo.deviceType,
- deviceSession.sessionStamp
- );
+ await persistIdentityDevicePushToken(env, storage, user.id, deviceSession, deviceInfo.deviceType, body);
}
// Successful login - clear failed attempts
await rateLimit.clearLoginAttempts(loginIdentifier);
const accessToken = await auth.generateAccessToken(user, deviceSession);
- const refreshToken = await auth.generateRefreshToken(user.id, deviceSession);
+ const refreshToken = await auth.generateRefreshToken(user, deviceSession, resolveRefreshClientType(request, body));
const accountKeys = buildAccountKeys(user);
const userDecryptionOptions = buildUserDecryptionOptions(user);
await safeWriteAuditEvent(env, {
@@ -696,9 +862,7 @@ export async function handleToken(request: Request, env: Env): Promise
KdfParallelism: user.kdfParallelism,
ForcePasswordReset: false,
ResetMasterPassword: false,
- MasterPasswordPolicy: {
- Object: 'masterPasswordPolicy',
- },
+ MasterPasswordPolicy: masterPasswordPolicyResponse(),
ApiUseKeyConnector: false,
scope: 'api offline_access',
unofficialServer: true,
@@ -706,7 +870,7 @@ export async function handleToken(request: Request, env: Env): Promise
userDecryptionOptions: userDecryptionOptions,
};
- const baseResponse = jsonResponse(response);
+ const baseResponse = identityJsonResponse(response);
return shouldUseWebSession(request)
? withWebRefreshCookie(request, baseResponse, refreshToken)
: baseResponse;
@@ -723,7 +887,7 @@ export async function handleToken(request: Request, env: Env): Promise
const sendId = String(body.send_id || body.sendId || '').trim();
if (!sendId) {
- return jsonResponse(
+ return identityJsonResponse(
{
error: 'invalid_request',
error_description: 'send_id is required',
@@ -748,13 +912,13 @@ export async function handleToken(request: Request, env: Env): Promise
passwordHashB64,
password,
rateLimit,
- `${clientIdentifier}:send-password`
+ clientIdentifier || undefined
);
if ('error' in result) {
return result.error;
}
- return jsonResponse({
+ return identityJsonResponse({
access_token: result.token,
expires_in: LIMITS.auth.sendAccessTokenTtlSeconds,
token_type: 'Bearer',
@@ -762,19 +926,6 @@ export async function handleToken(request: Request, env: Env): Promise
unofficialServer: true,
});
} else if (grantType === 'refresh_token') {
- const refreshLimit = await rateLimit.consumeBudget(
- `${clientIdentifier}:identity-refresh`,
- LIMITS.rateLimit.refreshTokenRequestsPerMinute
- );
- if (!refreshLimit.allowed) {
- return identityErrorResponse(
- `Rate limit exceeded. Try again in ${refreshLimit.retryAfterSeconds} seconds.`,
- 'TooManyRequests',
- 429
- );
- }
-
- // Refresh token
const refreshToken = String(body.refresh_token || '').trim() || (
shouldUseWebSession(request)
? parseCookieValue(request, WEB_REFRESH_COOKIE)
@@ -784,7 +935,72 @@ export async function handleToken(request: Request, env: Env): Promise
return identityErrorResponse('Refresh token is required', 'invalid_request', 400);
}
- const result = await auth.refreshAccessTokenDetailed(refreshToken);
+ const refreshTokenHash = await sha256Hex(refreshToken);
+ try {
+ const sessionLimit = await rateLimit.consumeBudget(
+ `refresh-session:${refreshTokenHash}`,
+ LIMITS.rateLimit.refreshTokenRequestsPerMinute
+ );
+ const ipLimit = clientIdentifier
+ ? await rateLimit.consumeBudget(
+ `refresh-ip:${clientIdentifier}`,
+ LIMITS.rateLimit.refreshTokenRequestsPerIpMinute
+ )
+ : null;
+ const rejected = !sessionLimit.allowed ? sessionLimit : (ipLimit && !ipLimit.allowed ? ipLimit : null);
+ if (rejected) {
+ const retryAfter = Math.max(1, rejected.retryAfterSeconds || 1);
+ return identityErrorResponse(
+ `Rate limit exceeded. Try again in ${retryAfter} seconds.`,
+ 'temporarily_unavailable',
+ 429,
+ { 'Retry-After': String(retryAfter) }
+ );
+ }
+ } catch (error) {
+ await safeWriteAuditEvent(env, {
+ action: 'auth.refresh.failed.rate_limit_unavailable',
+ category: 'auth',
+ level: 'error',
+ targetType: 'refreshToken',
+ metadata: { grantType, reason: 'rate_limit_unavailable', error: error instanceof Error ? error.message : String(error), ...auditRequestMetadata(request) },
+ });
+ return identityErrorResponse(
+ 'Session refresh is temporarily unavailable',
+ 'temporarily_unavailable',
+ 503,
+ { 'Retry-After': '5' }
+ );
+ }
+
+ if (!clientIdentifier) {
+ await safeWriteAuditEvent(env, {
+ action: 'auth.client_ip.missing',
+ category: 'auth',
+ level: 'warn',
+ targetType: 'refreshToken',
+ metadata: { grantType, reason: 'client_ip_missing', webSession: shouldUseWebSession(request), ...auditRequestMetadata(request) },
+ });
+ }
+
+ let result: Awaited>;
+ try {
+ result = await auth.refreshAccessTokenDetailed(refreshToken);
+ } catch (error) {
+ await safeWriteAuditEvent(env, {
+ action: 'auth.refresh.failed.temporarily_unavailable',
+ category: 'auth',
+ level: 'error',
+ targetType: 'refreshToken',
+ metadata: { grantType, reason: 'storage_or_worker_error', error: error instanceof Error ? error.message : String(error), webSession: shouldUseWebSession(request), ...auditRequestMetadata(request) },
+ });
+ return identityErrorResponse(
+ 'Session refresh is temporarily unavailable',
+ 'temporarily_unavailable',
+ 503,
+ { 'Retry-After': '5' }
+ );
+ }
if (!result.ok) {
await safeWriteAuditEvent(env, {
actorUserId: result.userId ?? null,
@@ -806,18 +1022,10 @@ export async function handleToken(request: Request, env: Env): Promise
: invalidResponse;
}
- // Keep a short overlap window for old refresh token to absorb
- // concurrent refresh requests from multiple client contexts.
- await storage.constrainRefreshTokenExpiry(
- refreshToken,
- Date.now() + LIMITS.auth.refreshTokenOverlapGraceMs
- );
-
const { accessToken, user, device } = result;
if (device?.identifier) {
await storage.touchDeviceLastSeen(user.id, device.identifier);
}
- const newRefreshToken = await auth.generateRefreshToken(user.id, device);
const accountKeys = buildAccountKeys(user);
const userDecryptionOptions = buildUserDecryptionOptions(user);
@@ -825,7 +1033,7 @@ export async function handleToken(request: Request, env: Env): Promise
access_token: accessToken,
expires_in: LIMITS.auth.accessTokenTtlSeconds,
token_type: 'Bearer',
- ...(shouldUseWebSession(request) ? { web_session: true } : { refresh_token: newRefreshToken }),
+ ...(shouldUseWebSession(request) ? { web_session: true } : { refresh_token: refreshToken }),
Key: user.key,
PrivateKey: user.privateKey,
AccountKeys: accountKeys,
@@ -836,9 +1044,7 @@ export async function handleToken(request: Request, env: Env): Promise
KdfParallelism: user.kdfParallelism,
ForcePasswordReset: false,
ResetMasterPassword: false,
- MasterPasswordPolicy: {
- Object: 'masterPasswordPolicy',
- },
+ MasterPasswordPolicy: masterPasswordPolicyResponse(),
ApiUseKeyConnector: false,
scope: 'api offline_access',
unofficialServer: true,
@@ -846,9 +1052,9 @@ export async function handleToken(request: Request, env: Env): Promise
userDecryptionOptions: userDecryptionOptions,
};
- const baseResponse = jsonResponse(response);
+ const baseResponse = identityJsonResponse(response);
return shouldUseWebSession(request)
- ? withWebRefreshCookie(request, baseResponse, newRefreshToken)
+ ? withWebRefreshCookie(request, baseResponse, refreshToken)
: baseResponse;
}
@@ -881,7 +1087,7 @@ export async function handlePrelogin(request: Request, env: Env): Promise {
const storage = new StorageService(env.DB);
-
let body: Record;
const contentType = request.headers.get('content-type') || '';
try {
@@ -900,7 +1105,7 @@ export async function handleRevocation(request: Request, env: Env): Promise | null;
@@ -92,6 +95,12 @@ function readAliasedImportProp(source: any, aliases: string[]): T |
return undefined;
}
+function normalizeOptionalId(value: unknown): string | null {
+ if (value == null) return null;
+ const normalized = String(value).trim();
+ return normalized ? normalized : null;
+}
+
async function runBatchInChunks(db: D1Database, statements: D1PreparedStatement[], chunkSize: number): Promise {
for (let i = 0; i < statements.length; i += chunkSize) {
const chunk = statements.slice(i, i + chunkSize);
@@ -112,9 +121,9 @@ export async function handleCiphersImport(request: Request, env: Env, userId: st
return errorResponse('Invalid JSON', 400);
}
- const folders = importData.folders || [];
- const ciphers = importData.ciphers || [];
- const folderRelationships = importData.folderRelationships || [];
+ const folders = Array.isArray(importData.folders) ? importData.folders : [];
+ const ciphers = Array.isArray(importData.ciphers) ? importData.ciphers : [];
+ const folderRelationships = Array.isArray(importData.folderRelationships) ? importData.folderRelationships : [];
if (folders.length + ciphers.length > LIMITS.performance.importItemLimit) {
return errorResponse(`Import exceeds maximum of ${LIMITS.performance.importItemLimit} items`, 400);
@@ -128,13 +137,14 @@ export async function handleCiphersImport(request: Request, env: Env, userId: st
const folderRows: Folder[] = [];
for (let i = 0; i < folders.length; i++) {
+ const importedFolder = folders[i] && typeof folders[i] === 'object' ? folders[i] : null;
const folderId = generateUUID();
folderIdMap.set(i, folderId);
const folder: Folder = {
id: folderId,
userId: userId,
- name: folders[i].name,
+ name: typeof importedFolder?.name === 'string' && importedFolder.name ? importedFolder.name : 'Folder',
createdAt: now,
updatedAt: now,
};
@@ -157,24 +167,31 @@ export async function handleCiphersImport(request: Request, env: Env, userId: st
// Build cipher index -> folder id mapping from relationships
const cipherFolderMap = new Map();
for (const rel of folderRelationships) {
+ if (!rel || typeof rel !== 'object') continue;
const folderId = folderIdMap.get(rel.value);
if (folderId) {
cipherFolderMap.set(rel.key, folderId);
}
}
+ const existingFolderIds = new Set((await storage.getAllFolders(userId)).map((folder) => folder.id));
// Create ciphers
const cipherRows: Cipher[] = [];
const cipherMapRows: Array<{ index: number; sourceId: string | null; id: string }> = [];
for (let i = 0; i < ciphers.length; i++) {
- const c = ciphers[i];
- const folderId = cipherFolderMap.get(i) || readAliasedImportProp(c, ['folderId', 'FolderId']) || null;
+ const c = ciphers[i] && typeof ciphers[i] === 'object' ? ciphers[i] : {} as CiphersImportRequest['ciphers'][number];
+ const importedFolderId = normalizeOptionalId(readAliasedImportProp(c, ['folderId', 'FolderId']));
+ const folderId = cipherFolderMap.get(i) || (importedFolderId && existingFolderIds.has(importedFolderId) ? importedFolderId : null);
const sourceIdRaw = String(c?.id ?? '').trim();
const sourceId = sourceIdRaw || null;
const login = readAliasedImportProp(c, ['login', 'Login']);
const card = readAliasedImportProp(c, ['card', 'Card']);
const identity = readAliasedImportProp(c, ['identity', 'Identity']);
const secureNote = readAliasedImportProp(c, ['secureNote', 'SecureNote']);
+ const sshKey = readAliasedImportProp(c, ['sshKey', 'SshKey']);
+ const bankAccount = readAliasedImportProp(c, ['bankAccount', 'BankAccount']);
+ const driversLicense = readAliasedImportProp(c, ['driversLicense', 'DriversLicense']);
+ const passport = readAliasedImportProp(c, ['passport', 'Passport']);
const fields = readAliasedImportProp(c, ['fields', 'Fields']);
const passwordHistory = readAliasedImportProp(c, ['passwordHistory', 'PasswordHistory']);
const key = readAliasedImportProp(c, ['key', 'Key']);
@@ -244,7 +261,10 @@ export async function handleCiphersImport(request: Request, env: Env, userId: st
})) || null,
passwordHistory: passwordHistory ?? null,
reprompt: c.reprompt ?? 0,
- sshKey: normalizeCipherSshKeyForCompatibility((c as any).sshKey ?? null),
+ sshKey: normalizeCipherSshKeyForCompatibility(sshKey ?? null),
+ bankAccount: bankAccount ?? null,
+ driversLicense: driversLicense ?? null,
+ passport: passport ?? null,
key: key ?? null,
createdAt: now,
updatedAt: now,
diff --git a/src/handlers/notifications.ts b/src/handlers/notifications.ts
index f978119..fecb822 100644
--- a/src/handlers/notifications.ts
+++ b/src/handlers/notifications.ts
@@ -1,4 +1,6 @@
import { AuthService } from '../services/auth';
+import { StorageService } from '../services/storage';
+import { isAuthRequestExpired } from '../services/storage-auth-request-repo';
import type { Env, JWTPayload } from '../types';
import { errorResponse, jsonResponse } from '../utils/response';
import { generateUUID } from '../utils/uuid';
@@ -65,6 +67,12 @@ export async function handleAnonymousNotificationsHub(request: Request, env: Env
return errorResponse('Expected websocket', 426);
}
+ const storage = new StorageService(env.DB);
+ const authRequest = await storage.getAuthRequestById(authRequestId);
+ if (!authRequest || isAuthRequestExpired(authRequest)) {
+ return errorResponse('Not found', 404);
+ }
+
const id = env.NOTIFICATIONS_HUB.idFromName(authRequestId);
const stub = env.NOTIFICATIONS_HUB.get(id);
const forwardedUrl = new URL(request.url);
diff --git a/src/handlers/sends-private.ts b/src/handlers/sends-private.ts
index 67daaf2..390c2f0 100644
--- a/src/handlers/sends-private.ts
+++ b/src/handlers/sends-private.ts
@@ -8,6 +8,7 @@ import { LIMITS } from '../config/limits';
import {
getBlobStorageMaxBytes,
getSendFileObjectKey,
+ getBlobObject,
putBlobObject,
deleteBlobObject,
} from '../services/blob-store';
@@ -16,6 +17,9 @@ import {
formatSize,
getAliasedProp,
normalizeEmails,
+ notifySendCreateForRequest,
+ notifySendDeleteForRequest,
+ notifySendUpdateForRequest,
notifyVaultSyncForRequest,
parseDate,
parseFileLength,
@@ -31,6 +35,8 @@ import {
} from './sends-shared';
import { auditRequestMetadata, writeAuditEvent } from '../services/audit-events';
+const SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE = 'Send email verification is not supported by this server.';
+
async function writeSendAudit(
storage: StorageService,
request: Request,
@@ -79,8 +85,13 @@ async function processSendFileUpload(
return upload;
}
+ const path = getSendFileObjectKey(send.id, fileId);
+ if (await getBlobObject(env, path)) {
+ return errorResponse('Send file has already been uploaded', 409);
+ }
+
try {
- await putBlobObject(env, getSendFileObjectKey(send.id, fileId), upload.body, {
+ await putBlobObject(env, path, upload.body, {
size: upload.size,
contentType: upload.contentType,
customMetadata: {
@@ -99,6 +110,7 @@ async function processSendFileUpload(
const storage = new StorageService(env.DB);
const revisionDate = await storage.updateRevisionDate(send.userId);
notifyVaultSyncForRequest(request, env, send.userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, send.userId, revisionDate);
return new Response(null, { status: 201 });
}
@@ -130,7 +142,7 @@ export async function handleGetSends(request: Request, env: Env, userId: string)
export async function handleGetSend(request: Request, env: Env, userId: string, sendId: string): Promise {
void request;
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
@@ -206,11 +218,17 @@ export async function handleCreateSend(request: Request, env: Env, userId: strin
if (authTypeRaw.present && requestedAuthType === null) {
return errorResponse('Invalid authType', 400);
}
+ if (requestedAuthType === SendAuthType.Email) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
+ }
const normalizedEmails = normalizeEmails(emailsRaw.value);
if (emailsRaw.present && emailsRaw.value !== null && normalizedEmails === null) {
return errorResponse('Invalid emails', 400);
}
+ if (normalizedEmails) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
+ }
const now = new Date().toISOString();
const send: Send = {
@@ -249,6 +267,7 @@ export async function handleCreateSend(request: Request, env: Env, userId: strin
await storage.saveSend(send);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendCreateForRequest(request, env, send.id, userId, revisionDate);
return jsonResponse(sendToResponse(send));
}
@@ -329,11 +348,17 @@ export async function handleCreateFileSendV2(request: Request, env: Env, userId:
if (authTypeRaw.present && requestedAuthType === null) {
return errorResponse('Invalid authType', 400);
}
+ if (requestedAuthType === SendAuthType.Email) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
+ }
const normalizedEmails = normalizeEmails(emailsRaw.value);
if (emailsRaw.present && emailsRaw.value !== null && normalizedEmails === null) {
return errorResponse('Invalid emails', 400);
}
+ if (normalizedEmails) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
+ }
const now = new Date().toISOString();
const send: Send = {
@@ -372,6 +397,7 @@ export async function handleCreateFileSendV2(request: Request, env: Env, userId:
await storage.saveSend(send);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendCreateForRequest(request, env, send.id, userId, revisionDate);
const jwtSecret = getSafeJwtSecret(env);
if (!jwtSecret) {
return errorResponse('Server configuration error', 500);
@@ -395,7 +421,7 @@ export async function handleGetSendFileUpload(
): Promise {
void request;
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
}
@@ -430,7 +456,7 @@ export async function handleUploadSendFile(
fileId: string
): Promise {
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found. Unable to save the file.', 404);
}
@@ -466,7 +492,7 @@ export async function handlePublicUploadSendFile(
}
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, claims.userId);
if (!send || send.userId !== claims.userId) {
return errorResponse('Send not found. Unable to save the file.', 404);
}
@@ -479,7 +505,7 @@ export async function handlePublicUploadSendFile(
export async function handleUpdateSend(request: Request, env: Env, userId: string, sendId: string): Promise {
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
}
@@ -586,10 +612,11 @@ export async function handleUpdateSend(request: Request, env: Env, userId: strin
if (parsedAuthType === null) {
return errorResponse('Invalid authType', 400);
}
- send.authType = parsedAuthType;
- if (parsedAuthType !== SendAuthType.Email) {
- send.emails = null;
+ if (parsedAuthType === SendAuthType.Email) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
}
+ send.authType = parsedAuthType;
+ send.emails = null;
}
const emailsRaw = getAliasedProp(body, ['emails', 'Emails']);
@@ -598,10 +625,13 @@ export async function handleUpdateSend(request: Request, env: Env, userId: strin
if (emailsRaw.value !== null && normalizedEmails === null) {
return errorResponse('Invalid emails', 400);
}
+ if (normalizedEmails) {
+ return errorResponse(SEND_EMAIL_AUTH_UNSUPPORTED_MESSAGE, 501);
+ }
send.emails = normalizedEmails;
if (send.emails) {
send.authType = SendAuthType.Email;
- } else if (send.authType === SendAuthType.Email) {
+ } else if (Number(send.authType) === SendAuthType.Email) {
send.authType = SendAuthType.None;
}
}
@@ -619,13 +649,14 @@ export async function handleUpdateSend(request: Request, env: Env, userId: strin
await storage.saveSend(send);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, userId, revisionDate);
return jsonResponse(sendToResponse(send));
}
export async function handleDeleteSend(request: Request, env: Env, userId: string, sendId: string): Promise {
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
}
@@ -641,6 +672,7 @@ export async function handleDeleteSend(request: Request, env: Env, userId: strin
await storage.deleteSend(sendId, userId);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendDeleteForRequest(request, env, sendId, userId, revisionDate);
await writeSendAudit(storage, request, userId, 'send.delete', {
id: sendId,
type: send.type,
@@ -676,6 +708,9 @@ export async function handleBulkDeleteSends(request: Request, env: Env, userId:
const revisionDate = await storage.bulkDeleteSends(body.ids, userId);
if (revisionDate) {
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ for (const send of sends) {
+ notifySendDeleteForRequest(request, env, send.id, userId, revisionDate);
+ }
await writeSendAudit(storage, request, userId, 'send.delete.bulk', {
count: sends.length,
requestedCount: body.ids.length,
@@ -687,7 +722,7 @@ export async function handleBulkDeleteSends(request: Request, env: Env, userId:
export async function handleRemoveSendPassword(request: Request, env: Env, userId: string, sendId: string): Promise {
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
}
@@ -697,6 +732,7 @@ export async function handleRemoveSendPassword(request: Request, env: Env, userI
await storage.saveSend(send);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, userId, revisionDate);
await writeSendAudit(storage, request, userId, 'send.password.remove', {
id: send.id,
type: send.type,
@@ -707,7 +743,7 @@ export async function handleRemoveSendPassword(request: Request, env: Env, userI
export async function handleRemoveSendAuth(request: Request, env: Env, userId: string, sendId: string): Promise {
const storage = new StorageService(env.DB);
- const send = await storage.getSend(sendId);
+ const send = await storage.getSendForUser(sendId, userId);
if (!send || send.userId !== userId) {
return errorResponse('Send not found', 404);
}
@@ -718,6 +754,7 @@ export async function handleRemoveSendAuth(request: Request, env: Env, userId: s
await storage.saveSend(send);
const revisionDate = await storage.updateRevisionDate(userId);
notifyVaultSyncForRequest(request, env, userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, userId, revisionDate);
await writeSendAudit(storage, request, userId, 'send.auth.remove', {
id: send.id,
type: send.type,
diff --git a/src/handlers/sends-public.ts b/src/handlers/sends-public.ts
index 064fbce..bdeadef 100644
--- a/src/handlers/sends-public.ts
+++ b/src/handlers/sends-public.ts
@@ -2,7 +2,7 @@ import { Env, SendType } from '../types';
import { StorageService } from '../services/storage';
import { RateLimitService, getClientIdentifier } from '../services/ratelimit';
import { jsonResponse, errorResponse } from '../utils/response';
-import { LIMITS } from '../config/limits';
+import { sanitizeDownloadContentType } from '../utils/content-type';
import {
createSendAccessToken,
createSendFileDownloadToken,
@@ -21,6 +21,7 @@ import {
getSafeJwtSecret,
hasEmailAuth,
isSendAvailable,
+ notifySendUpdateForRequest,
notifyVaultSyncForRequest,
parseStoredSendData,
resolveSendFromIdOrAccessId,
@@ -33,6 +34,14 @@ import {
verifySendPasswordHashB64,
} from './sends-shared';
+function contentDispositionAttachment(fileName: string | null | undefined): string {
+ const fallback = 'send-file';
+ const value = String(fileName || fallback)
+ .replace(/[\r\n"]/g, '_')
+ .trim() || fallback;
+ return `attachment; filename="${value}"`;
+}
+
export async function handleAccessSend(request: Request, env: Env, accessId: string): Promise {
const storage = new StorageService(env.DB);
const sendId = fromAccessId(accessId);
@@ -59,7 +68,7 @@ export async function handleAccessSend(request: Request, env: Env, accessId: str
if (!clientIdentifier) {
return errorResponse('Client IP is required', 403);
}
- sendPasswordLimitIpKey = sendPasswordLimitKey(clientIdentifier);
+ sendPasswordLimitIpKey = sendPasswordLimitKey(clientIdentifier, send.id);
sendPasswordRateLimit = new RateLimitService(env.DB);
const sendPasswordCheck = await sendPasswordRateLimit.checkLoginAttempt(sendPasswordLimitIpKey);
if (!sendPasswordCheck.allowed) {
@@ -90,6 +99,7 @@ export async function handleAccessSend(request: Request, env: Env, accessId: str
send.accessCount += 1;
const revisionDate = await storage.updateRevisionDate(send.userId);
notifyVaultSyncForRequest(request, env, send.userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, send.userId, revisionDate);
}
const creatorIdentifier = await getCreatorIdentifier(storage, send);
@@ -102,10 +112,9 @@ export async function handleAccessSendFile(
idOrAccessId: string,
fileId: string
): Promise {
- const secret = (env.JWT_SECRET || '').trim();
- if (!secret || secret.length < LIMITS.auth.jwtSecretMinLength) {
- return errorResponse('Server configuration error', 500);
- }
+ const safeSecret = getSafeJwtSecret(env);
+ if (!safeSecret.ok) return safeSecret.response;
+ const { secret } = safeSecret;
const storage = new StorageService(env.DB);
const send = await resolveSendFromIdOrAccessId(storage, idOrAccessId);
@@ -133,7 +142,7 @@ export async function handleAccessSendFile(
if (!clientIdentifier) {
return errorResponse('Client IP is required', 403);
}
- sendPasswordLimitIpKey = sendPasswordLimitKey(clientIdentifier);
+ sendPasswordLimitIpKey = sendPasswordLimitKey(clientIdentifier, send.id);
sendPasswordRateLimit = new RateLimitService(env.DB);
const sendPasswordCheck = await sendPasswordRateLimit.checkLoginAttempt(sendPasswordLimitIpKey);
if (!sendPasswordCheck.allowed) {
@@ -163,6 +172,7 @@ export async function handleAccessSendFile(
send.accessCount += 1;
const revisionDate = await storage.updateRevisionDate(send.userId);
notifyVaultSyncForRequest(request, env, send.userId, revisionDate);
+ notifySendUpdateForRequest(request, env, send.id, send.userId, revisionDate);
const token = await createSendFileDownloadToken(send.id, fileId, secret);
const url = new URL(request.url);
@@ -203,6 +213,7 @@ export async function handleAccessSendV2(request: Request, env: Env): Promise {
const jwt = getSafeJwtSecret(env);
if (!jwt.ok) {
@@ -343,11 +368,14 @@ export async function issueSendAccessToken(
Object: 'error',
},
},
- 400
+ 501
),
};
}
+ const sendPasswordLimitIpKey =
+ rateLimit && clientIdentifier ? sendPasswordLimitKey(clientIdentifier, send.id) : null;
+
if (send.passwordHash) {
if (rateLimit && sendPasswordLimitIpKey) {
const sendPasswordCheck = await rateLimit.checkLoginAttempt(sendPasswordLimitIpKey);
diff --git a/src/handlers/sends-shared.ts b/src/handlers/sends-shared.ts
index d5d97ff..c29859b 100644
--- a/src/handlers/sends-shared.ts
+++ b/src/handlers/sends-shared.ts
@@ -1,5 +1,10 @@
-import { Env, Send, SendAuthType, SendResponse, SendType, DEFAULT_DEV_SECRET } from '../types';
-import { notifyUserVaultSync } from '../durable/notifications-hub';
+import { Env, Send, SendAuthType, SendResponse, SendType } from '../types';
+import {
+ notifyUserSendCreate,
+ notifyUserSendDelete,
+ notifyUserSendUpdate,
+ notifyUserVaultSync,
+} from '../durable/notifications-hub';
import { StorageService } from '../services/storage';
import { jsonResponse, errorResponse } from '../utils/response';
import { readActingDeviceIdentifier } from '../utils/device';
@@ -18,6 +23,51 @@ export function notifyVaultSyncForRequest(
notifyUserVaultSync(env, userId, revisionDate, readActingDeviceIdentifier(request));
}
+export function notifySendCreateForRequest(
+ request: Request,
+ env: Env,
+ sendId: string,
+ userId: string,
+ revisionDate: string
+): void {
+ notifyUserSendCreate(env, {
+ userId,
+ sendId,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
+export function notifySendUpdateForRequest(
+ request: Request,
+ env: Env,
+ sendId: string,
+ userId: string,
+ revisionDate: string
+): void {
+ notifyUserSendUpdate(env, {
+ userId,
+ sendId,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
+export function notifySendDeleteForRequest(
+ request: Request,
+ env: Env,
+ sendId: string,
+ userId: string,
+ revisionDate: string
+): void {
+ notifyUserSendDelete(env, {
+ userId,
+ sendId,
+ revisionDate,
+ contextId: readActingDeviceIdentifier(request),
+ });
+}
+
export function getAliasedProp(source: unknown, aliases: string[]): { present: boolean; value: unknown } {
if (!source || typeof source !== 'object') return { present: false, value: undefined };
for (const key of aliases) {
@@ -105,7 +155,15 @@ export function formatSize(bytes: number): string {
export function parseDate(raw: unknown): Date | null {
if (typeof raw !== 'string' || !raw.trim()) return null;
- const date = new Date(raw);
+ let value = raw.trim();
+ if (!/[zZ]$/.test(value) && !/[+\-]\d{2}:?\d{2}$/.test(value)) {
+ if (/^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}/.test(value)) {
+ value += 'Z';
+ } else if (/^\d{4}-\d{2}-\d{2} \d{2}:\d{2}/.test(value)) {
+ value = value.replace(' ', 'T') + 'Z';
+ }
+ }
+ const date = new Date(value);
if (Number.isNaN(date.getTime())) return null;
return date;
}
@@ -321,7 +379,7 @@ export function hasEmailAuth(send: Send): boolean {
export function getSafeJwtSecret(env: Env): { ok: true; secret: string } | { ok: false; response: Response } {
const secret = (env.JWT_SECRET || '').trim();
- if (!secret || secret.length < LIMITS.auth.jwtSecretMinLength || secret === DEFAULT_DEV_SECRET) {
+ if (!secret || secret.length < LIMITS.auth.jwtSecretMinLength) {
return { ok: false, response: errorResponse('Server configuration error', 500) };
}
return { ok: true, secret };
@@ -384,8 +442,8 @@ export type PublicSendAccessValidationResult =
| { ok: true }
| { ok: false; response: Response; reason: 'email_auth_unsupported' | 'password_missing' | 'invalid_password' };
-export function sendPasswordLimitKey(clientIdentifier: string): string {
- return `${clientIdentifier}:${SEND_PASSWORD_LIMIT_SCOPE}`;
+export function sendPasswordLimitKey(clientIdentifier: string, sendId: string): string {
+ return `${clientIdentifier}:${SEND_PASSWORD_LIMIT_SCOPE}:${String(sendId || '').trim() || 'unknown-send'}`;
}
function sendPasswordLockMessage(retryAfterSeconds: number): string {
@@ -414,7 +472,11 @@ export function sendPasswordLockedOAuthResponse(retryAfterSeconds: number): Resp
export async function validatePublicSendAccess(send: Send, body: unknown): Promise {
if (hasEmailAuth(send)) {
- return { ok: false, response: errorResponse(SEND_INACCESSIBLE_MSG, 404), reason: 'email_auth_unsupported' };
+ return {
+ ok: false,
+ response: errorResponse('Send email verification is not supported by this server.', 501),
+ reason: 'email_auth_unsupported',
+ };
}
if (!send.passwordHash) return { ok: true };
diff --git a/src/handlers/sync.ts b/src/handlers/sync.ts
index 86cd097..dbbca5b 100644
--- a/src/handlers/sync.ts
+++ b/src/handlers/sync.ts
@@ -5,12 +5,12 @@ import { cipherToResponse, isCipherResponseSyncCompatible, shouldPreserveRepaira
import { sendToResponse } from './sends';
import { LIMITS } from '../config/limits';
import {
- buildAccountKeys,
buildUserDecryptionCompat,
buildUserDecryptionOptions,
} from '../utils/user-decryption';
import { buildDomainsResponse } from '../services/domain-rules';
import { buildWebAuthnPrfOption } from '../utils/account-passkeys';
+import { buildProfileResponse } from '../utils/profile-response';
// CONTRACT:
// /api/sync reuses cipherToResponse() as the single cipher response shaper.
@@ -84,40 +84,17 @@ export async function handleSync(request: Request, env: Env, userId: string): Pr
storage.getAttachmentsByUserId(userId),
excludeDomains ? Promise.resolve(null) : storage.getUserDomainSettings(userId),
]);
- const accountKeys = buildAccountKeys(user);
const webAuthnPrfOptions = accountPasskeys
.map(buildWebAuthnPrfOption)
.filter((option): option is NonNullable => !!option);
const userDecryptionOptions = buildUserDecryptionOptions(user, webAuthnPrfOptions[0] || null);
+ const validFolderIds = new Set(folders.map((folder) => folder.id));
- const profile: ProfileResponse = {
- id: user.id,
- name: user.name,
- email: user.email,
- emailVerified: true,
- premium: true,
- premiumFromOrganization: false,
- usesKeyConnector: false,
- masterPasswordHint: user.masterPasswordHint,
- culture: 'en-US',
- twoFactorEnabled: !!user.totpSecret,
- key: user.key,
- privateKey: user.privateKey,
- accountKeys,
- securityStamp: user.securityStamp || user.id,
- organizations: [],
- providers: [],
- providerOrganizations: [],
- forcePasswordReset: false,
- avatarColor: null,
- creationDate: user.createdAt,
- verifyDevices: user.verifyDevices,
- object: 'profile',
- };
+ const profile: ProfileResponse = buildProfileResponse(user, env);
const cipherResponses: CipherResponse[] = [];
for (const cipher of ciphers) {
- const response = cipherToResponse(cipher, attachmentsByCipher.get(cipher.id) || [], { preserveRepairableUris });
+ const response = cipherToResponse(cipher, attachmentsByCipher.get(cipher.id) || [], { preserveRepairableUris, validFolderIds });
if (isCipherResponseSyncCompatible(response)) {
cipherResponses.push(response);
}
@@ -149,6 +126,7 @@ export async function handleSync(request: Request, env: Env, userId: string): Pr
{ omitExcludedGlobals: true }
),
policies: [],
+ policiesNew: [],
sends: sendResponses,
UserDecryption: {
MasterPasswordUnlock: userDecryptionOptions.MasterPasswordUnlock,
@@ -156,6 +134,7 @@ export async function handleSync(request: Request, env: Env, userId: string): Pr
KeyConnectorOption: null,
WebAuthnPrfOption: webAuthnPrfOptions[0] || null,
WebAuthnPrfOptions: webAuthnPrfOptions,
+ V2UpgradeToken: null,
Object: 'userDecryption',
},
UserDecryptionOptions: userDecryptionOptions,
diff --git a/src/index.ts b/src/index.ts
index 58bbd5c..e34d0b4 100644
--- a/src/index.ts
+++ b/src/index.ts
@@ -5,6 +5,11 @@ import { handleRequest } from './router';
import { StorageService } from './services/storage';
import { applyCors, jsonResponse } from './utils/response';
import { runScheduledBackupIfDue } from './handlers/backup';
+import {
+ isBackendRequestPath,
+ isWebVaultHidden,
+ webVaultNotFoundResponse,
+} from './web-vault-visibility';
let dbInitialized = false;
let dbInitError: string | null = null;
@@ -19,19 +24,6 @@ function normalizeRequestUrl(request: Request): Request {
return new Request(url.toString(), request);
}
-function isWorkerHandledPath(path: string): boolean {
- return (
- path.startsWith('/api/') ||
- path.startsWith('/identity/') ||
- path.startsWith('/icons/') ||
- path.startsWith('/notifications/') ||
- path.startsWith('/.well-known/') ||
- path === '/config' ||
- path === '/api/config' ||
- path === '/api/version'
- );
-}
-
function addSearchIndexHeaders(request: Request, response: Response): Response {
const url = new URL(request.url);
const contentType = String(response.headers.get('Content-Type') || '').toLowerCase();
@@ -55,7 +47,7 @@ async function maybeServeAsset(request: Request, env: Env): Promise {
void ctx;
const normalizedRequest = normalizeRequestUrl(request);
+ const requestPath = new URL(normalizedRequest.url).pathname;
+
+ if (isWebVaultHidden(env) && !isBackendRequestPath(requestPath)) {
+ return webVaultNotFoundResponse(normalizedRequest);
+ }
+
const assetResponse = await maybeServeAsset(normalizedRequest, env);
if (assetResponse) {
- return applyCors(normalizedRequest, assetResponse);
+ return applyCors(normalizedRequest, assetResponse, env);
}
await ensureDatabaseInitialized(env);
@@ -107,11 +105,11 @@ export default {
},
500
);
- return applyCors(normalizedRequest, resp);
+ return applyCors(normalizedRequest, resp, env);
}
const resp = await handleRequest(normalizedRequest, env);
- return applyCors(normalizedRequest, resp);
+ return applyCors(normalizedRequest, resp, env);
},
async scheduled(controller: ScheduledController, env: Env, ctx: ExecutionContext): Promise {
diff --git a/src/router-admin-backup.ts b/src/router-admin-backup.ts
index 548b073..54d4af4 100644
--- a/src/router-admin-backup.ts
+++ b/src/router-admin-backup.ts
@@ -14,6 +14,7 @@ import {
handleRunAdminConfiguredBackup,
handleUpdateAdminBackupSettings,
} from './handlers/backup';
+import { errorResponse } from './utils/response';
export async function handleAdminBackupRoute(
request: Request,
@@ -26,8 +27,22 @@ export async function handleAdminBackupRoute(
return handleAdminExportBackup(request, env, actorUser);
}
- if (path === '/api/admin/backup/blob' && method === 'GET') {
- return handleDownloadAdminBackupAttachment(request, env, actorUser);
+ if (path === '/api/admin/backup/blob') {
+ // POST only: this endpoint requires master-password verification, and a GET
+ // could only carry that credential in the query string, where it would leak
+ // into request logs, proxy logs, browser history and Referer headers.
+ // The credential is the same value clients send to /identity/connect/token,
+ // so a leaked copy is enough to sign in as this admin.
+ if (method === 'POST') {
+ return handleDownloadAdminBackupAttachment(request, env, actorUser);
+ }
+ if (method === 'GET') {
+ return errorResponse(
+ 'Use POST with a JSON body for this endpoint. Credentials must not be sent in the URL.',
+ 405
+ );
+ }
+ return null;
}
if (path === '/api/admin/backup/settings') {
@@ -50,11 +65,11 @@ export async function handleAdminBackupRoute(
return handleListAdminRemoteBackups(request, env, actorUser);
}
- if (path === '/api/admin/backup/remote/download' && method === 'GET') {
+ if (path === '/api/admin/backup/remote/download' && method === 'POST') {
return handleDownloadAdminRemoteBackup(request, env, actorUser);
}
- if (path === '/api/admin/backup/remote/integrity' && method === 'GET') {
+ if (path === '/api/admin/backup/remote/integrity' && method === 'POST') {
return handleInspectAdminRemoteBackup(request, env, actorUser);
}
diff --git a/src/router-admin.ts b/src/router-admin.ts
index 71e9d8b..6d36266 100644
--- a/src/router-admin.ts
+++ b/src/router-admin.ts
@@ -4,7 +4,7 @@ import {
handleAdminCreateInvite,
handleAdminListInvites,
handleAdminDeleteAllInvites,
- handleAdminRevokeInvite,
+ handleAdminDeleteInvite,
handleAdminSetUserStatus,
handleAdminDeleteUser,
handleAdminListAuditLogs,
@@ -13,6 +13,23 @@ import {
handleAdminClearAuditLogs,
} from './handlers/admin';
import { handleAdminBackupRoute } from './router-admin-backup';
+import { errorResponse } from './utils/response';
+
+function isKnownAdminPath(path: string): boolean {
+ return (
+ path === '/api/admin/users' ||
+ path === '/api/admin/logs' ||
+ path === '/api/admin/logs/settings' ||
+ path === '/api/admin/invites' ||
+ path.startsWith('/api/admin/backup') ||
+ /^\/api\/admin\/invites\/[^/]+$/i.test(path) ||
+ /^\/api\/admin\/users\/[a-f0-9-]+(?:\/status)?$/i.test(path)
+ );
+}
+
+function isActiveAdmin(user: User): boolean {
+ return user.role === 'admin' && user.status === 'active';
+}
export async function handleAdminRoute(
request: Request,
@@ -21,6 +38,13 @@ export async function handleAdminRoute(
path: string,
method: string
): Promise {
+ if (!isKnownAdminPath(path)) {
+ return null;
+ }
+ if (!isActiveAdmin(actorUser)) {
+ return errorResponse('Forbidden', 403);
+ }
+
if (path === '/api/admin/users' && method === 'GET') {
return handleAdminListUsers(request, env, actorUser);
}
@@ -52,7 +76,7 @@ export async function handleAdminRoute(
const adminInviteMatch = path.match(/^\/api\/admin\/invites\/([^/]+)$/i);
if (adminInviteMatch && method === 'DELETE') {
const inviteCode = decodeURIComponent(adminInviteMatch[1]);
- return handleAdminRevokeInvite(request, env, actorUser, inviteCode);
+ return handleAdminDeleteInvite(request, env, actorUser, inviteCode);
}
const adminUserStatusMatch = path.match(/^\/api\/admin\/users\/([a-f0-9-]+)\/status$/i);
diff --git a/src/router-authenticated.ts b/src/router-authenticated.ts
index 46d091d..ff99b0c 100644
--- a/src/router-authenticated.ts
+++ b/src/router-authenticated.ts
@@ -1,8 +1,9 @@
import type { Env, User } from './types';
-import { errorResponse, jsonResponse } from './utils/response';
+import { errorResponse, jsonResponse, unsupportedResponse } from './utils/response';
import {
handleGetProfile,
handleUpdateProfile,
+ handleGetKeys,
handleSetKeys,
handleGetRevisionDate,
handleVerifyPassword,
@@ -14,6 +15,12 @@ import {
handleGetTwoFactorProviders,
handleGetTwoFactorAuthenticator,
handlePutTwoFactorAuthenticator,
+ handleGetTwoFactorYubiKey,
+ handlePutTwoFactorYubiKey,
+ handlePutTwoFactorYubiKeyConfig,
+ handleBootstrapTwoFactorYubiKeyConfig,
+ handleGetDeviceVerificationSettings,
+ handlePutDeviceVerificationSettings,
handleDisableTwoFactorProvider,
handleGetApiKey,
handleRotateApiKey,
@@ -73,12 +80,17 @@ import { handleGetDomains, handleUpdateDomains } from './handlers/domains';
import {
handleCreateAccountPasskeyCredential,
handleDeleteAccountPasskeyCredential,
+ handleDeleteTwoFactorWebAuthn,
handleGetAccountPasskeyAttestationOptions,
handleGetAccountPasskeyCredentials,
handleGetAccountPasskeyUpdateAssertionOptions,
+ handleGetTwoFactorWebAuthn,
+ handleGetTwoFactorWebAuthnChallenge,
+ handlePutTwoFactorWebAuthn,
handleUpdateAccountPasskeyEncryption,
} from './handlers/account-passkeys';
import {
+ handleCreateAdminAuthRequest,
handleGetAuthRequest,
handleListAuthRequests,
handleListPendingAuthRequests,
@@ -105,6 +117,40 @@ export async function handleAuthenticatedRoute(
}
}
+ if ((path === '/api/accounts/kdf' || path === '/accounts/kdf') && (method === 'POST' || method === 'PUT')) {
+ return unsupportedResponse('KDF changes are not supported by this server.');
+ }
+
+ const mailBackedAccountPaths = new Set([
+ '/api/accounts/email-token',
+ '/accounts/email-token',
+ '/api/accounts/verify-email',
+ '/accounts/verify-email',
+ '/api/accounts/verify-email-token',
+ '/accounts/verify-email-token',
+ '/api/accounts/request-otp',
+ '/accounts/request-otp',
+ '/api/accounts/verify-otp',
+ '/accounts/verify-otp',
+ ]);
+ if (mailBackedAccountPaths.has(path) && (method === 'POST' || method === 'PUT')) {
+ return unsupportedResponse('Email delivery is not supported by this server.');
+ }
+
+ const emailTwoFactorPaths = new Set([
+ '/api/two-factor/get-email',
+ '/two-factor/get-email',
+ '/api/two-factor/send-email',
+ '/two-factor/send-email',
+ '/api/two-factor/send-email-login',
+ '/two-factor/send-email-login',
+ '/api/two-factor/email',
+ '/two-factor/email',
+ ]);
+ if (emailTwoFactorPaths.has(path) && (method === 'POST' || method === 'PUT' || method === 'DELETE')) {
+ return unsupportedResponse('Email two-step login is not supported by this server.');
+ }
+
if (path === '/api/accounts/profile') {
if (method === 'GET') return handleGetProfile(request, env, userId);
if (method === 'PUT') return handleUpdateProfile(request, env, userId);
@@ -115,8 +161,10 @@ export async function handleAuthenticatedRoute(
return handleChangePassword(request, env, userId);
}
- if (path === '/api/accounts/keys' && method === 'POST') {
- return handleSetKeys(request, env, userId);
+ if (path === '/api/accounts/keys') {
+ if (method === 'GET') return handleGetKeys(request, env, userId);
+ if (method === 'POST') return handleSetKeys(request, env, userId);
+ return errorResponse('Method not allowed', 405);
}
if (path === '/api/accounts/totp') {
@@ -138,12 +186,53 @@ export async function handleAuthenticatedRoute(
return handleGetTwoFactorAuthenticator(request, env, userId);
}
+ if ((path === '/api/two-factor/get-yubikey' || path === '/api/two-factor/get-yubi-key') && method === 'POST') {
+ return handleGetTwoFactorYubiKey(request, env, userId);
+ }
+
+ if (path === '/api/two-factor/get-device-verification-settings' && method === 'POST') {
+ return handleGetDeviceVerificationSettings(request, env, userId);
+ }
+
+ if (path === '/api/two-factor/device-verification-settings') {
+ if (method === 'PUT' || method === 'POST') return handlePutDeviceVerificationSettings(request, env, userId);
+ return errorResponse('Method not allowed', 405);
+ }
+
+ if (path === '/api/two-factor/get-webauthn' && method === 'POST') {
+ return handleGetTwoFactorWebAuthn(request, env, userId, currentUser);
+ }
+
+ if (path === '/api/two-factor/get-webauthn-challenge' && method === 'POST') {
+ return handleGetTwoFactorWebAuthnChallenge(request, env, userId, currentUser);
+ }
+
if (path === '/api/two-factor/authenticator') {
if (method === 'PUT' || method === 'POST') return handlePutTwoFactorAuthenticator(request, env, userId);
if (method === 'DELETE') return handleDisableTwoFactorProvider(request, env, userId);
return errorResponse('Method not allowed', 405);
}
+ if ((path === '/api/two-factor/yubikey' || path === '/api/two-factor/yubi-key')) {
+ if (method === 'PUT' || method === 'POST') return handlePutTwoFactorYubiKey(request, env, userId);
+ if (method === 'DELETE') return handleDisableTwoFactorProvider(request, env, userId);
+ return errorResponse('Method not allowed', 405);
+ }
+
+ if (path === '/api/two-factor/webauthn') {
+ if (method === 'PUT' || method === 'POST') return handlePutTwoFactorWebAuthn(request, env, userId, currentUser);
+ if (method === 'DELETE') return handleDeleteTwoFactorWebAuthn(request, env, userId, currentUser);
+ return errorResponse('Method not allowed', 405);
+ }
+
+ if ((path === '/api/two-factor/yubikey/config' || path === '/api/two-factor/yubi-key/config') && (method === 'PUT' || method === 'POST')) {
+ return handlePutTwoFactorYubiKeyConfig(request, env, userId);
+ }
+
+ if ((path === '/api/two-factor/yubikey/bootstrap' || path === '/api/two-factor/yubi-key/bootstrap') && method === 'POST') {
+ return handleBootstrapTwoFactorYubiKeyConfig(request, env, userId);
+ }
+
if (path === '/api/two-factor/disable' && (method === 'PUT' || method === 'POST')) {
return handleDisableTwoFactorProvider(request, env, userId);
}
@@ -291,17 +380,22 @@ export async function handleAuthenticatedRoute(
if (method === 'DELETE') return handleDeleteFolder(request, env, userId, folderId);
}
- if (path === '/api/auth-requests' || path === '/api/auth-requests/') {
+ if (path === '/api/auth-requests' || path === '/api/auth-requests/' || path === '/auth-requests' || path === '/auth-requests/') {
if (method === 'GET') return handleListAuthRequests(request, env, userId);
return errorResponse('Method not allowed', 405);
}
- if (path === '/api/auth-requests/pending') {
+ if (path === '/api/auth-requests/pending' || path === '/auth-requests/pending') {
if (method === 'GET') return handleListPendingAuthRequests(request, env, userId);
return errorResponse('Method not allowed', 405);
}
- const authRequestMatch = path.match(/^\/api\/auth-requests\/([a-f0-9-]+)$/i);
+ if (path === '/api/auth-requests/admin-request' || path === '/auth-requests/admin-request') {
+ if (method === 'POST') return handleCreateAdminAuthRequest(request, env, userId, currentUser.email);
+ return errorResponse('Method not allowed', 405);
+ }
+
+ const authRequestMatch = path.match(/^\/(?:api\/)?auth-requests\/([a-f0-9-]+)$/i);
if (authRequestMatch) {
if (method === 'GET') return handleGetAuthRequest(request, env, userId, authRequestMatch[1]);
if (method === 'PUT') return handleUpdateAuthRequest(request, env, userId, authRequestMatch[1]);
diff --git a/src/router-devices.ts b/src/router-devices.ts
index c6730c1..b5e7ebd 100644
--- a/src/router-devices.ts
+++ b/src/router-devices.ts
@@ -18,8 +18,14 @@ import {
handleUpdateDeviceToken,
handleUpdateDeviceWebPushAuth,
handleClearDeviceToken,
+ handleRegisterDevice,
+ handleReportLostTrust,
} from './handlers/devices';
+function devicesPath(pattern: string): RegExp {
+ return new RegExp(`^/(?:api/)?devices${pattern}$`, 'i');
+}
+
export async function handleAuthenticatedDeviceRoute(
request: Request,
env: Env,
@@ -27,31 +33,36 @@ export async function handleAuthenticatedDeviceRoute(
path: string,
method: string
): Promise {
- if (path === '/api/devices') {
+ if (path === '/api/devices' || path === '/devices') {
if (method === 'GET') return handleGetDevices(request, env, userId);
+ if (method === 'POST') return handleRegisterDevice(request, env, userId);
if (method === 'DELETE') return handleDeleteAllDevices(request, env, userId);
return null;
}
- if (path === '/api/devices/authorized') {
+ if ((path === '/api/devices/lost-trust' || path === '/devices/lost-trust') && method === 'POST') {
+ return handleReportLostTrust(request, env, userId);
+ }
+
+ if (path === '/api/devices/authorized' || path === '/devices/authorized') {
if (method === 'GET') return handleGetAuthorizedDevices(request, env, userId);
if (method === 'DELETE') return handleRevokeAllTrustedDevices(request, env, userId);
return null;
}
- const authorizedDeviceMatch = path.match(/^\/api\/devices\/authorized\/([^/]+)$/i);
+ const authorizedDeviceMatch = path.match(devicesPath('/authorized/([^/]+)'));
if (authorizedDeviceMatch && method === 'DELETE') {
const deviceIdentifier = decodeURIComponent(authorizedDeviceMatch[1]);
return handleRevokeTrustedDevice(request, env, userId, deviceIdentifier);
}
- const permanentAuthorizedDeviceMatch = path.match(/^\/api\/devices\/authorized\/([^/]+)\/permanent$/i);
+ const permanentAuthorizedDeviceMatch = path.match(devicesPath('/authorized/([^/]+)/permanent'));
if (permanentAuthorizedDeviceMatch && method === 'POST') {
const deviceIdentifier = decodeURIComponent(permanentAuthorizedDeviceMatch[1]);
return handleTrustDevicePermanently(request, env, userId, deviceIdentifier);
}
- const deleteDeviceMatch = path.match(/^\/api\/devices\/([^/]+)$/i);
+ const deleteDeviceMatch = path.match(devicesPath('/([^/]+)'));
if (deleteDeviceMatch && method === 'GET') {
const deviceIdentifier = decodeURIComponent(deleteDeviceMatch[1]);
return handleGetDevice(request, env, userId, deviceIdentifier);
@@ -61,59 +72,59 @@ export async function handleAuthenticatedDeviceRoute(
return handleDeleteDevice(request, env, userId, deviceIdentifier);
}
- const updateDeviceNameMatch = path.match(/^\/api\/devices\/([^/]+)\/name$/i);
+ const updateDeviceNameMatch = path.match(devicesPath('/([^/]+)/name'));
if (updateDeviceNameMatch && method === 'PUT') {
const deviceIdentifier = decodeURIComponent(updateDeviceNameMatch[1]);
return handleUpdateDeviceName(request, env, userId, deviceIdentifier);
}
- const identifierMatch = path.match(/^\/api\/devices\/identifier\/([^/]+)$/i);
+ const identifierMatch = path.match(devicesPath('/identifier/([^/]+)'));
if (identifierMatch && method === 'GET') {
const deviceIdentifier = decodeURIComponent(identifierMatch[1]);
return handleGetDeviceByIdentifier(request, env, userId, deviceIdentifier);
}
- const deviceKeysMatch = path.match(/^\/api\/devices\/([^/]+)\/keys$/i) || path.match(/^\/api\/devices\/identifier\/([^/]+)\/keys$/i);
+ const deviceKeysMatch = path.match(devicesPath('/([^/]+)/keys')) || path.match(devicesPath('/identifier/([^/]+)/keys'));
if (deviceKeysMatch && (method === 'PUT' || method === 'POST')) {
const deviceIdentifier = decodeURIComponent(deviceKeysMatch[1]);
return handleUpdateDeviceKeys(request, env, userId, deviceIdentifier);
}
- const identifierTokenMatch = path.match(/^\/api\/devices\/identifier\/([^/]+)\/token$/i);
+ const identifierTokenMatch = path.match(devicesPath('/identifier/([^/]+)/token'));
if (identifierTokenMatch && (method === 'PUT' || method === 'POST')) {
const deviceIdentifier = decodeURIComponent(identifierTokenMatch[1]);
return handleUpdateDeviceToken(request, env, userId, deviceIdentifier);
}
- const identifierWebPushMatch = path.match(/^\/api\/devices\/identifier\/([^/]+)\/web-push-auth$/i);
+ const identifierWebPushMatch = path.match(devicesPath('/identifier/([^/]+)/web-push-auth'));
if (identifierWebPushMatch && (method === 'PUT' || method === 'POST')) {
const deviceIdentifier = decodeURIComponent(identifierWebPushMatch[1]);
return handleUpdateDeviceWebPushAuth(request, env, userId, deviceIdentifier);
}
- const identifierClearTokenMatch = path.match(/^\/api\/devices\/identifier\/([^/]+)\/clear-token$/i);
+ const identifierClearTokenMatch = path.match(devicesPath('/identifier/([^/]+)/clear-token'));
if (identifierClearTokenMatch && (method === 'PUT' || method === 'POST')) {
const deviceIdentifier = decodeURIComponent(identifierClearTokenMatch[1]);
return handleClearDeviceToken(request, env, userId, deviceIdentifier);
}
- const identifierRetrieveKeysMatch = path.match(/^\/api\/devices\/([^/]+)\/retrieve-keys$/i);
+ const identifierRetrieveKeysMatch = path.match(devicesPath('/([^/]+)/retrieve-keys'));
if (identifierRetrieveKeysMatch && method === 'POST') {
const deviceIdentifier = decodeURIComponent(identifierRetrieveKeysMatch[1]);
return handleRetrieveDeviceKeys(request, env, userId, deviceIdentifier);
}
- const identifierDeactivateMatch = path.match(/^\/api\/devices\/([^/]+)\/deactivate$/i);
+ const identifierDeactivateMatch = path.match(devicesPath('/([^/]+)/deactivate'));
if (identifierDeactivateMatch && (method === 'POST' || method === 'DELETE')) {
const deviceIdentifier = decodeURIComponent(identifierDeactivateMatch[1]);
return handleDeactivateDevice(request, env, userId, deviceIdentifier);
}
- if (path === '/api/devices/update-trust' && method === 'POST') {
+ if ((path === '/api/devices/update-trust' || path === '/devices/update-trust') && method === 'POST') {
return handleUpdateDeviceTrust(request, env, userId);
}
- if (path === '/api/devices/untrust' && method === 'POST') {
+ if ((path === '/api/devices/untrust' || path === '/devices/untrust') && method === 'POST') {
return handleUntrustDevices(request, env, userId);
}
diff --git a/src/router-public.ts b/src/router-public.ts
index d3f0674..30f8f3f 100644
--- a/src/router-public.ts
+++ b/src/router-public.ts
@@ -1,5 +1,4 @@
import { LIMITS } from './config/limits';
-import { DEFAULT_DEV_SECRET } from './types';
import {
handleAccessSend,
handleAccessSendFile,
@@ -8,6 +7,11 @@ import {
handleDownloadSendFile,
} from './handlers/sends';
import { handleKnownDevice } from './handlers/devices';
+import {
+ handleDigitalAssetLinkCheck,
+ handleFillAssistForms,
+ handleFillAssistManifest,
+} from './handlers/fill-assist';
import { handleToken, handlePrelogin, handleRevocation } from './handlers/identity';
import { handleGetAccountPasskeyAssertionOptions } from './handlers/account-passkeys';
import {
@@ -27,18 +31,27 @@ import {
handleNotificationsNegotiate,
} from './handlers/notifications';
import { handlePublicUploadSendFile } from './handlers/sends';
-import { jsonResponse } from './utils/response';
+import { isSafeWebsiteIconContentType } from './utils/content-type';
+import { jsonResponse, unsupportedResponse } from './utils/response';
import { StorageService } from './services/storage';
import type { Env } from './types';
+import { getConfiguredWebAuthnAllowedOrigins } from './utils/origins';
+import { buildConfigResponse } from './config-response';
type PublicRateLimiter = (category?: string, maxRequests?: number) => Promise;
-type JwtUnsafeReason = 'missing' | 'default' | 'too_short' | null;
+type JwtUnsafeReason = 'missing' | 'too_short' | null;
export interface WebBootstrapResponse {
defaultKdfIterations: number;
jwtUnsafeReason: JwtUnsafeReason;
jwtSecretMinLength: number;
registrationInviteRequired: boolean;
+ webAuthnAllowedOrigins: string[];
+ websiteIconsEnabled: boolean;
+}
+
+function isWebsiteIconProxyEnabled(env: Env): boolean {
+ return true;
}
function isSameOriginWriteRequest(request: Request): boolean {
@@ -83,56 +96,6 @@ function handleMissingWebsiteIcon(): Response {
});
}
-function buildIconServiceBase(origin: string): string {
- return `${origin}/icons`;
-}
-
-function buildIconServiceTemplate(origin: string): string {
- return `${buildIconServiceBase(origin)}/{}/icon.png`;
-}
-
-function buildIconServiceCsp(origin: string): string {
- return `img-src 'self' data: ${origin}`;
-}
-
-function buildConfigResponse(origin: string) {
- return {
- version: LIMITS.compatibility.bitwardenServerVersion,
- gitHash: 'nodewarden',
- server: null,
- environment: {
- cloudRegion: 'self-hosted',
- vault: origin,
- api: origin + '/api',
- identity: origin + '/identity',
- notifications: origin + '/notifications',
- icons: origin,
- sso: '',
- fillAssistRules: null,
- },
- push: {
- pushTechnology: 0,
- vapidPublicKey: null,
- },
- communication: null,
- settings: {
- disableUserRegistration: false,
- },
- _icon_service_url: buildIconServiceTemplate(origin),
- _icon_service_csp: buildIconServiceCsp(origin),
- featureStates: {
- 'cipher-key-encryption': LIMITS.compatibility.cipherKeyEncryptionFeatureEnabled,
- 'duo-redirect': true,
- 'email-verification': true,
- 'pm-19051-send-email-verification': false,
- 'pm-19148-innovation-archive': true,
- 'unauth-ui-refresh': true,
- 'web-push': false,
- },
- object: 'config',
- };
-}
-
function normalizeIconHost(rawHost: string): string | null {
let decoded: string;
try {
@@ -241,11 +204,16 @@ function iconResponse(body: BodyInit | null, contentType: string | null): Respon
headers: {
'Content-Type': contentType || 'image/png',
'Cache-Control': `public, max-age=${LIMITS.cache.iconTtlSeconds}, immutable`,
+ 'Content-Security-Policy': "default-src 'none'; img-src 'self' data:; sandbox",
},
});
}
-async function handleWebsiteIcon(host: string, fallbackMode: 'default' | 'not-found' = 'default'): Promise {
+async function handleWebsiteIcon(env: Env, host: string, fallbackMode: 'default' | 'not-found' = 'default'): Promise {
+ if (!isWebsiteIconProxyEnabled(env)) {
+ return fallbackMode === 'not-found' ? handleMissingWebsiteIcon() : handleNwFavicon();
+ }
+
const normalizedHost = normalizeIconHost(host);
if (!normalizedHost) return fallbackMode === 'not-found' ? handleMissingWebsiteIcon() : handleNwFavicon();
@@ -272,7 +240,7 @@ async function handleWebsiteIcon(host: string, fallbackMode: 'default' | 'not-fo
if (!resp.ok) continue;
const contentType = String(resp.headers.get('Content-Type') || '').toLowerCase();
- if (!contentType.startsWith('image/')) continue;
+ if (!isSafeWebsiteIconContentType(contentType)) continue;
const contentLength = getPositiveContentLength(resp.headers);
if (contentLength !== null && contentLength > ICON_MAX_BUFFER_BYTES) continue;
@@ -301,9 +269,7 @@ export async function buildWebBootstrapResponse(env: Env): Promise 0,
+ webAuthnAllowedOrigins: getConfiguredWebAuthnAllowedOrigins(env),
+ websiteIconsEnabled: isWebsiteIconProxyEnabled(env),
};
}
@@ -340,12 +308,31 @@ export async function handlePublicRoute(
return jsonResponse(await buildWebBootstrapResponse(env));
}
+ if (path === '/fill-assist/manifest.json' && method === 'GET') {
+ const blocked = await enforcePublicRateLimit('public-read', LIMITS.rateLimit.publicReadRequestsPerMinute);
+ if (blocked) return blocked;
+ return handleFillAssistManifest();
+ }
+
+ if ((path === '/v1/assetlinks:check' || path === '/api/v1/assetlinks:check') && method === 'GET') {
+ const blocked = await enforcePublicRateLimit('public-read', LIMITS.rateLimit.publicReadRequestsPerMinute);
+ if (blocked) return blocked;
+ return handleDigitalAssetLinkCheck();
+ }
+
+ const fillAssistFormsMatch = path.match(/^\/fill-assist\/([^/]+)$/i);
+ if (fillAssistFormsMatch && method === 'GET') {
+ const blocked = await enforcePublicRateLimit('public-read', LIMITS.rateLimit.publicReadRequestsPerMinute);
+ if (blocked) return blocked;
+ return handleFillAssistForms(fillAssistFormsMatch[1]);
+ }
+
const iconMatch = path.match(/^\/icons\/([^/]+)\/icon\.png$/i);
if (iconMatch && method === 'GET') {
const blocked = await enforcePublicRateLimit('public-icon', LIMITS.rateLimit.publicIconRequestsPerMinute);
if (blocked) return blocked;
const fallbackMode = new URL(request.url).searchParams.get('fallback') === '404' ? 'not-found' : 'default';
- return handleWebsiteIcon(iconMatch[1], fallbackMode);
+ return handleWebsiteIcon(env, iconMatch[1], fallbackMode);
}
const publicAttachmentMatch = path.match(/^\/api\/attachments\/([a-f0-9-]+)\/([a-f0-9-]+)$/i);
@@ -395,13 +382,13 @@ export async function handlePublicRoute(
return handleDownloadSendFile(request, env, sendDownloadMatch[1], sendDownloadMatch[2]);
}
- if ((path === '/api/auth-requests' || path === '/api/auth-requests/') && method === 'POST') {
+ if ((path === '/api/auth-requests' || path === '/api/auth-requests/' || path === '/auth-requests' || path === '/auth-requests/') && method === 'POST') {
const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
if (blocked) return blocked;
return handleCreateAuthRequest(request, env);
}
- const authRequestResponseMatch = path.match(/^\/api\/auth-requests\/([a-f0-9-]+)\/response$/i);
+ const authRequestResponseMatch = path.match(/^\/(?:api\/)?auth-requests\/([a-f0-9-]+)\/response$/i);
if (authRequestResponseMatch && method === 'GET') {
const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
if (blocked) return blocked;
@@ -448,9 +435,34 @@ export async function handlePublicRoute(
}
if ((path === '/identity/accounts/recover-2fa' || path === '/api/accounts/recover-2fa') && method === 'POST') {
+ const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
+ if (blocked) return blocked;
return handleRecoverTwoFactor(request, env);
}
+ const publicMailBackedPaths = new Set([
+ '/api/accounts/resend-new-device-otp',
+ '/accounts/resend-new-device-otp',
+ '/api/accounts/register/send-verification-email',
+ '/accounts/register/send-verification-email',
+ '/identity/accounts/register/send-verification-email',
+ '/api/accounts/register/verification-email-clicked',
+ '/accounts/register/verification-email-clicked',
+ '/identity/accounts/register/verification-email-clicked',
+ '/api/accounts/register/finish',
+ '/accounts/register/finish',
+ '/identity/accounts/register/finish',
+ '/api/accounts/verify-email-token',
+ '/accounts/verify-email-token',
+ '/api/two-factor/send-email-login',
+ '/two-factor/send-email-login',
+ ]);
+ if (publicMailBackedPaths.has(path) && method === 'POST') {
+ const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
+ if (blocked) return blocked;
+ return unsupportedResponse('Email delivery is not supported by this server.');
+ }
+
if (path === '/api/accounts/password-hint' && method === 'POST') {
const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
if (blocked) return blocked;
@@ -467,7 +479,7 @@ export async function handlePublicRoute(
const blocked = await enforcePublicRateLimit('public-read', LIMITS.rateLimit.publicReadRequestsPerMinute);
if (blocked) return blocked;
const origin = new URL(request.url).origin;
- return jsonResponse(buildConfigResponse(origin));
+ return jsonResponse(buildConfigResponse(origin), 200, { 'Cache-Control': 'no-store' });
}
if (path === '/api/version' && method === 'GET') {
@@ -497,6 +509,8 @@ export async function handlePublicRoute(
}
if (path === '/notifications/anonymous-hub' && method === 'GET') {
+ const blocked = await enforcePublicRateLimit('public-sensitive', LIMITS.rateLimit.sensitivePublicRequestsPerMinute);
+ if (blocked) return blocked;
return handleAnonymousNotificationsHub(request, env);
}
return null;
diff --git a/src/router.ts b/src/router.ts
index 93c6298..a171427 100644
--- a/src/router.ts
+++ b/src/router.ts
@@ -1,4 +1,4 @@
-import { DEFAULT_DEV_SECRET, Env } from './types';
+import { Env } from './types';
import { AuthService } from './services/auth';
import { RateLimitService, getClientIdentifier } from './services/ratelimit';
import { handleCors, errorResponse } from './utils/response';
@@ -6,14 +6,25 @@ import { LIMITS } from './config/limits';
import { handleAuthenticatedRoute } from './router-authenticated';
import { handlePublicRoute } from './router-public';
-function jwtSecretUnsafeReason(env: Env): 'missing' | 'default' | 'too_short' | null {
+function jwtSecretUnsafeReason(env: Env): 'missing' | 'too_short' | null {
const secret = (env.JWT_SECRET || '').trim();
if (!secret) return 'missing';
- if (secret === DEFAULT_DEV_SECRET) return 'default';
if (secret.length < LIMITS.auth.jwtSecretMinLength) return 'too_short';
return null;
}
+function canServeWithUnsafeJwtSecret(path: string, method: string): boolean {
+ if (method === 'OPTIONS') return true;
+ if (method === 'GET' && (path === '/api/web-bootstrap' || path === '/web-bootstrap')) return true;
+ if (method === 'GET' && (path === '/config' || path === '/api/config' || path === '/api/version')) return true;
+ if (method === 'GET' && path === '/.well-known/appspecific/com.chrome.devtools.json') return true;
+ if (method === 'GET' && path === '/fill-assist/manifest.json') return true;
+ if (method === 'GET' && /^\/fill-assist\/[^/]+$/i.test(path)) return true;
+ if (method === 'GET' && (path === '/v1/assetlinks:check' || path === '/api/v1/assetlinks:check')) return true;
+ if (method === 'GET' && /^\/icons\/[^/]+\/icon\.png$/i.test(path)) return true;
+ return false;
+}
+
function isImportBypassRequest(request: Request, path: string, method: string): boolean {
if (request.headers.get('X-NodeWarden-Import') !== '1') return false;
@@ -26,6 +37,70 @@ function isImportBypassRequest(request: Request, path: string, method: string):
return false;
}
+const BODY_LIMIT_METHODS = new Set(['POST', 'PUT', 'PATCH', 'DELETE']);
+
+function isLargeUploadPath(path: string): boolean {
+ return (
+ /^\/api\/ciphers\/[a-f0-9-]+\/attachment\/[a-f0-9-]+$/i.test(path) ||
+ /^\/api\/sends\/[a-f0-9-]+\/file\/[a-f0-9-]+$/i.test(path) ||
+ path === '/api/admin/backup/import'
+ );
+}
+
+async function enforceRequestBodyLimit(
+ request: Request,
+ path: string,
+ method: string
+): Promise {
+ if (!BODY_LIMIT_METHODS.has(method) || isLargeUploadPath(path) || !request.body) {
+ return request;
+ }
+
+ const contentLengthRaw = request.headers.get('Content-Length');
+ if (contentLengthRaw) {
+ const contentLength = Number(contentLengthRaw);
+ if (Number.isFinite(contentLength) && contentLength > LIMITS.request.maxBodyBytes) {
+ return errorResponse('Request body too large', 413);
+ }
+ if (Number.isFinite(contentLength) && contentLength >= 0) {
+ return request;
+ }
+ }
+
+ const reader = request.body.getReader();
+ const chunks: Uint8Array[] = [];
+ let total = 0;
+ while (true) {
+ const { done, value } = await reader.read();
+ if (done) break;
+ if (!value) continue;
+ total += value.byteLength;
+ if (total > LIMITS.request.maxBodyBytes) {
+ try {
+ await reader.cancel();
+ } catch {
+ // Ignore cancellation races after the oversized body is rejected.
+ }
+ return errorResponse('Request body too large', 413);
+ }
+ chunks.push(value);
+ }
+
+ const body = new Uint8Array(total);
+ let offset = 0;
+ for (const chunk of chunks) {
+ body.set(chunk, offset);
+ offset += chunk.byteLength;
+ }
+
+ return new Request(request.url, {
+ method: request.method,
+ headers: request.headers,
+ body,
+ redirect: request.redirect,
+ });
+}
+
export async function handleRequest(request: Request, env: Env): Promise {
const url = new URL(request.url);
const path = url.pathname;
@@ -50,7 +125,10 @@ export async function handleRequest(request: Request, env: Env): Promise LIMITS.request.maxBodyBytes) {
- return errorResponse('Request body too large', 413);
- }
+ const bodyLimitResult = await enforceRequestBodyLimit(request, path, method);
+ if (bodyLimitResult instanceof Response) {
+ return bodyLimitResult;
+ }
+ request = bodyLimitResult;
+
+ const secretIssue = jwtSecretUnsafeReason(env);
+ if (secretIssue && !canServeWithUnsafeJwtSecret(path, method)) {
+ return errorResponse('Server configuration error: JWT_SECRET is not set or too weak', 500);
}
const publicResponse = await handlePublicRoute(request, env, path, method, enforcePublicRateLimit);
if (publicResponse) return publicResponse;
- const secretIssue = jwtSecretUnsafeReason(env);
- if (secretIssue) {
- return errorResponse('Server configuration error: JWT_SECRET is not set or too weak', 500);
- }
-
const auth = new AuthService(env);
const authHeader = request.headers.get('Authorization');
const verified = await auth.verifyAccessTokenWithUser(authHeader);
diff --git a/src/services/auth.ts b/src/services/auth.ts
index c7d5d0c..28a12e9 100644
--- a/src/services/auth.ts
+++ b/src/services/auth.ts
@@ -1,5 +1,6 @@
import { Env, JWTPayload, User } from '../types';
import { verifyJWT, createJWT, createRefreshToken } from '../utils/jwt';
+import { getRefreshTokenSlidingTtlMs, LIMITS } from '../config/limits';
import { StorageService } from './storage';
// Server-side iterations for second-layer hashing.
@@ -28,11 +29,12 @@ export type RefreshAccessTokenFailureReason =
| 'token_not_found_or_expired'
| 'user_missing'
| 'user_inactive'
+ | 'security_stamp_mismatch'
| 'device_missing'
| 'device_session_mismatch';
export type RefreshAccessTokenResult =
- | { ok: true; accessToken: string; user: User; device: { identifier: string; sessionStamp: string } | null }
+ | { ok: true; accessToken: string; user: User; device: { identifier: string; sessionStamp: string } | null; expiresAt: number }
| {
ok: false;
reason: RefreshAccessTokenFailureReason;
@@ -190,9 +192,23 @@ export class AuthService {
}
// Generate refresh token
- async generateRefreshToken(userId: string, device?: { identifier: string; sessionStamp: string } | null): Promise {
+ async generateRefreshToken(
+ user: User,
+ device?: { identifier: string; sessionStamp: string } | null,
+ clientType: string = 'other'
+ ): Promise {
const token = createRefreshToken();
- await this.storage.saveRefreshToken(token, userId, undefined, device?.identifier ?? null, device?.sessionStamp ?? null);
+ const now = Date.now();
+ await this.storage.saveRefreshToken(
+ token,
+ user.id,
+ now + getRefreshTokenSlidingTtlMs(clientType),
+ device?.identifier ?? null,
+ device?.sessionStamp ?? null,
+ user.securityStamp,
+ clientType,
+ now + LIMITS.auth.refreshTokenAbsoluteTtlMs
+ );
return token;
}
@@ -251,25 +267,42 @@ export class AuthService {
return { ok: false, reason: 'user_inactive', userId: user.id, deviceIdentifier: record.deviceIdentifier };
}
+ if (record.securityStamp && record.securityStamp !== user.securityStamp) {
+ await this.storage.deleteRefreshToken(refreshToken);
+ return { ok: false, reason: 'security_stamp_mismatch', userId: user.id, deviceIdentifier: record.deviceIdentifier };
+ }
+ if (!record.securityStamp) {
+ await this.storage.bindRefreshTokenSecurityStamp(refreshToken, user.securityStamp);
+ }
+
let device: { identifier: string; sessionStamp: string } | null = null;
- if (!record.deviceIdentifier || !record.deviceSessionStamp) {
- await this.storage.deleteRefreshToken(refreshToken);
- return { ok: false, reason: 'device_missing', userId: user.id, deviceIdentifier: record.deviceIdentifier };
+ if (record.deviceIdentifier) {
+ const boundDevice = await this.storage.getDevice(user.id, record.deviceIdentifier);
+ if (!boundDevice) {
+ await this.storage.deleteRefreshToken(refreshToken);
+ return { ok: false, reason: 'device_missing', userId: user.id, deviceIdentifier: record.deviceIdentifier };
+ }
+ if (record.deviceSessionStamp && boundDevice.sessionStamp !== record.deviceSessionStamp) {
+ await this.storage.deleteRefreshToken(refreshToken);
+ return { ok: false, reason: 'device_session_mismatch', userId: user.id, deviceIdentifier: record.deviceIdentifier };
+ }
+ if (!record.deviceSessionStamp) {
+ await this.storage.bindRefreshTokenDeviceStamp(refreshToken, boundDevice.sessionStamp);
+ }
+ device = { identifier: boundDevice.deviceIdentifier, sessionStamp: boundDevice.sessionStamp };
}
- const boundDevice = await this.storage.getDevice(user.id, record.deviceIdentifier);
- if (!boundDevice) {
- await this.storage.deleteRefreshToken(refreshToken);
- return { ok: false, reason: 'device_missing', userId: user.id, deviceIdentifier: record.deviceIdentifier };
+ const now = Date.now();
+ const expiresAt = Math.min(
+ now + getRefreshTokenSlidingTtlMs(record.clientType),
+ record.absoluteExpiresAt || (now + LIMITS.auth.refreshTokenAbsoluteTtlMs)
+ );
+ const extended = await this.storage.extendRefreshTokenExpiry(refreshToken, expiresAt, now);
+ if (!extended) {
+ return { ok: false, reason: 'token_not_found_or_expired', userId: user.id, deviceIdentifier: record.deviceIdentifier };
}
- if (boundDevice.sessionStamp !== record.deviceSessionStamp) {
- await this.storage.deleteRefreshToken(refreshToken);
- return { ok: false, reason: 'device_session_mismatch', userId: user.id, deviceIdentifier: record.deviceIdentifier };
- }
- device = { identifier: boundDevice.deviceIdentifier, sessionStamp: boundDevice.sessionStamp };
-
const accessToken = await this.generateAccessToken(user, device);
- return { ok: true, accessToken, user, device };
+ return { ok: true, accessToken, user, device, expiresAt };
}
async refreshAccessToken(
diff --git a/src/services/backup-archive.ts b/src/services/backup-archive.ts
index 0ae3cf2..c353548 100644
--- a/src/services/backup-archive.ts
+++ b/src/services/backup-archive.ts
@@ -1,7 +1,8 @@
-import { zipSync, unzipSync } from 'fflate';
+import { zipSync, unzipSync, type UnzipFileInfo } from 'fflate';
import type { Env } from '../types';
import { APP_VERSION } from '../../shared/app-version';
import { BACKUP_SETTINGS_CONFIG_KEY } from './backup-config';
+import { YUBICO_BOOTSTRAP_CLAIM_CONFIG_KEY } from './yubico-config';
import { exportPortableBackupSettingsEnvelope } from './backup-settings-crypto';
import {
getAttachmentObjectKey,
@@ -16,6 +17,8 @@ import {
// - Add persistent tables to BackupPayload, export SQL, manifest tableCounts,
// and validateBackupPayloadContents().
// - Keep secrets and transient runtime rows sanitized before writing db.json.
+// - Runtime authentication state (devices, sessions, auth requests, remembered
+// 2FA devices, and one-time tokens) must never enter an instance backup.
// - users.api_key is intentionally not exported.
// - backup.settings.v1 is exported as portable-only; the current server runtime
// envelope must not leave the instance.
@@ -28,10 +31,11 @@ const BACKUP_FILE_HASH_PREFIX_LENGTH = 5;
// Prefer store-only ZIP entries over heavier compression to keep exports reliable.
const BACKUP_TEXT_COMPRESSION_LEVEL = 0;
const BACKUP_JSON_INDENT = 2;
-const MAX_BACKUP_ARCHIVE_BYTES = 64 * 1024 * 1024;
+export const MAX_BACKUP_ARCHIVE_BYTES = 64 * 1024 * 1024;
const MAX_BACKUP_ARCHIVE_ENTRY_COUNT = 10_000;
const MAX_BACKUP_EXTRACTED_BYTES = 64 * 1024 * 1024;
const MAX_BACKUP_DB_JSON_BYTES = 32 * 1024 * 1024;
+const MAX_BACKUP_PATH_SEGMENT_LENGTH = 128;
export interface BackupManifest {
formatVersion: 1;
@@ -68,7 +72,6 @@ export interface BackupPayload {
ciphers: SqlRow[];
attachments: SqlRow[];
webauthn_credentials?: SqlRow[];
- trusted_two_factor_device_tokens?: SqlRow[];
};
}
@@ -110,7 +113,7 @@ function sanitizeConfigRowsForExport(rows: SqlRow[]): SqlRow[] {
const sanitized: SqlRow[] = [];
for (const row of rows) {
const key = String(row.key || '').trim();
- if (!key || key === BACKUP_RUNNER_LOCK_CONFIG_KEY) continue;
+ if (!key || key === BACKUP_RUNNER_LOCK_CONFIG_KEY || key === YUBICO_BOOTSTRAP_CLAIM_CONFIG_KEY) continue;
if (key === BACKUP_SETTINGS_CONFIG_KEY) {
const portableOnly = exportPortableBackupSettingsEnvelope(typeof row.value === 'string' ? row.value : null);
@@ -186,6 +189,61 @@ function validateArchiveSize(bytes: Uint8Array): void {
}
}
+function isSafeBackupPathSegment(value: string): boolean {
+ if (!value || value.length > MAX_BACKUP_PATH_SEGMENT_LENGTH) return false;
+ if (value === '.' || value === '..') return false;
+ return /^[A-Za-z0-9._-]+$/.test(value);
+}
+
+export function isSafeBackupAttachmentBlobName(value: unknown): boolean {
+ const normalized = String(value ?? '').trim();
+ const parts = normalized.split('/');
+ return parts.length === 2 && parts.every(isSafeBackupPathSegment);
+}
+
+function isSafeBackupAttachmentEntryName(value: string): boolean {
+ if (!value.startsWith('attachments/') || !value.endsWith('.bin')) return false;
+ const relative = value.slice('attachments/'.length, -'.bin'.length);
+ return isSafeBackupAttachmentBlobName(relative);
+}
+
+function validateBackupEntryName(name: string): void {
+ const normalized = String(name || '').trim();
+ if (normalized !== name || !normalized) {
+ throw new Error('Backup archive contains an invalid file name');
+ }
+ if (normalized.includes('\\') || normalized.includes('\0') || normalized.startsWith('/') || normalized.includes('//')) {
+ throw new Error(`Backup archive contains an unsafe file name: ${normalized}`);
+ }
+ if (normalized !== 'manifest.json' && normalized !== 'db.json' && !isSafeBackupAttachmentEntryName(normalized)) {
+ throw new Error(`Backup archive contains an unsupported file: ${normalized}`);
+ }
+}
+
+function createBackupUnzipFilter(): (file: UnzipFileInfo) => boolean {
+ let entryCount = 0;
+ let totalOriginalBytes = 0;
+ return (file: UnzipFileInfo): boolean => {
+ entryCount += 1;
+ if (entryCount > MAX_BACKUP_ARCHIVE_ENTRY_COUNT) {
+ throw new Error('Backup archive contains too many files');
+ }
+ validateBackupEntryName(file.name);
+ const originalSize = Number(file.originalSize);
+ if (!Number.isFinite(originalSize) || originalSize < 0) {
+ throw new Error(`Backup archive contains an invalid file size: ${file.name}`);
+ }
+ if (file.name === 'db.json' && originalSize > MAX_BACKUP_DB_JSON_BYTES) {
+ throw new Error('Backup archive database payload is too large');
+ }
+ totalOriginalBytes += originalSize;
+ if (totalOriginalBytes > MAX_BACKUP_EXTRACTED_BYTES) {
+ throw new Error('Backup archive expands beyond the current restore limit');
+ }
+ return true;
+ };
+}
+
function getRequiredZipEntries(db: BackupPayload['db']): string[] {
const entries: string[] = [];
for (const row of db.attachments) {
@@ -204,6 +262,25 @@ function ensureRowArray(value: unknown, table: string): SqlRow[] {
return value as SqlRow[];
}
+function normalizeParsedBackupDb(value: unknown): BackupPayload['db'] {
+ if (!value || typeof value !== 'object' || Array.isArray(value)) {
+ throw new Error('Backup archive database payload is invalid');
+ }
+ const source = value as Record;
+ // Restore uses an explicit allowlist. Extra tables from old or modified
+ // archives, especially runtime authentication state, are intentionally ignored.
+ return {
+ config: source.config as SqlRow[],
+ users: source.users as SqlRow[],
+ domain_settings: source.domain_settings as SqlRow[],
+ user_revisions: source.user_revisions as SqlRow[],
+ folders: source.folders as SqlRow[],
+ ciphers: source.ciphers as SqlRow[],
+ attachments: source.attachments as SqlRow[],
+ webauthn_credentials: source.webauthn_credentials as SqlRow[] | undefined,
+ };
+}
+
function createZipEntries(files: Record): Record {
const entries: Record = {};
for (const [path, bytes] of Object.entries(files)) {
@@ -223,8 +300,11 @@ export function parseBackupArchive(
validateArchiveSize(bytes);
let zipped: Record;
try {
- zipped = unzipSync(bytes);
- } catch {
+ zipped = unzipSync(bytes, { filter: createBackupUnzipFilter() });
+ } catch (error) {
+ if (error instanceof Error && error.message.startsWith('Backup archive ')) {
+ throw error;
+ }
throw new Error('Invalid backup archive');
}
@@ -235,6 +315,7 @@ export function parseBackupArchive(
let totalExtractedBytes = 0;
for (const entry of entryNames) {
+ validateBackupEntryName(entry);
const entryBytes = zipped[entry];
totalExtractedBytes += entryBytes.byteLength;
if (entry === 'db.json' && entryBytes.byteLength > MAX_BACKUP_DB_JSON_BYTES) {
@@ -253,10 +334,10 @@ export function parseBackupArchive(
const decoder = new TextDecoder();
let manifest: BackupManifest;
- let db: BackupPayload['db'];
+ let rawDb: unknown;
try {
manifest = JSON.parse(decoder.decode(manifestBytes)) as BackupManifest;
- db = JSON.parse(decoder.decode(dbBytes)) as BackupPayload['db'];
+ rawDb = JSON.parse(decoder.decode(dbBytes));
} catch {
throw new Error('Backup archive contains invalid JSON metadata');
}
@@ -264,9 +345,7 @@ export function parseBackupArchive(
if (manifest?.formatVersion !== BACKUP_FORMAT_VERSION) {
throw new Error('Unsupported backup format version');
}
- if (!db || typeof db !== 'object') {
- throw new Error('Backup archive database payload is invalid');
- }
+ const db = normalizeParsedBackupDb(rawDb);
const externalAttachmentKeys = new Set(
options.allowExternalAttachmentBlobs
@@ -303,7 +382,6 @@ export function validateBackupPayloadContents(
const cipherRows = ensureRowArray(payload.db.ciphers, 'ciphers');
const attachmentRows = ensureRowArray(payload.db.attachments, 'attachments');
const accountPasskeyRows = ensureRowArray(payload.db.webauthn_credentials || [], 'webauthn_credentials');
- const trustedTwoFactorTokenRows = ensureRowArray(payload.db.trusted_two_factor_device_tokens || [], 'trusted_two_factor_device_tokens');
const externalAttachmentKeys = new Set(
options.allowExternalAttachmentBlobs
? (payload.manifest.attachmentBlobs || []).map((item) => `attachments/${String(item.cipherId || '').trim()}/${String(item.attachmentId || '').trim()}.bin`)
@@ -368,7 +446,7 @@ export function validateBackupPayloadContents(
for (const row of attachmentRows) {
const id = String(row.id || '').trim();
const cipherId = String(row.cipher_id || '').trim();
- if (!id || !cipherId || !cipherIds.has(cipherId)) {
+ if (!id || !cipherId || !isSafeBackupPathSegment(id) || !isSafeBackupPathSegment(cipherId) || !cipherIds.has(cipherId)) {
throw new Error('Backup archive contains an invalid attachment row');
}
const attachmentPath = `attachments/${cipherId}/${id}.bin`;
@@ -382,9 +460,10 @@ export function validateBackupPayloadContents(
for (const row of accountPasskeyRows) {
const id = String(row.id || '').trim();
const userId = String(row.user_id || '').trim();
+ const purpose = row.purpose == null ? 'login' : String(row.purpose || '').trim();
const credentialId = String(row.credential_id || '').trim();
const publicKey = String(row.public_key || '').trim();
- if (!id || !userIds.has(userId) || !credentialId || !publicKey) {
+ if (!id || !userIds.has(userId) || !credentialId || !publicKey || (purpose !== 'login' && purpose !== 'twoFactor')) {
throw new Error('Backup archive contains an invalid account passkey row');
}
if (accountPasskeyIds.has(id)) throw new Error(`Backup archive contains duplicate account passkey id: ${id}`);
@@ -393,20 +472,6 @@ export function validateBackupPayloadContents(
accountPasskeyCredentialIds.add(credentialId);
}
- const trustedTwoFactorTokens = new Set();
- for (const row of trustedTwoFactorTokenRows) {
- const token = String(row.token || '').trim();
- const userId = String(row.user_id || '').trim();
- const deviceIdentifier = String(row.device_identifier || '').trim();
- const expiresAt = Number(row.expires_at || 0);
- if (!token || !userIds.has(userId) || !deviceIdentifier || !Number.isFinite(expiresAt) || expiresAt <= 0) {
- throw new Error('Backup archive contains an invalid trusted two-factor device token row');
- }
- if (trustedTwoFactorTokens.has(token)) {
- throw new Error(`Backup archive contains duplicate trusted two-factor device token: ${token}`);
- }
- trustedTwoFactorTokens.add(token);
- }
}
export async function buildBackupArchive(
@@ -425,16 +490,15 @@ export async function buildBackupArchive(
includeAttachments,
});
const encoder = new TextEncoder();
- const [configRows, userRows, domainSettingsRows, revisionRows, folderRows, cipherRows, attachmentRows, accountPasskeyRows, trustedTwoFactorTokenRows] = await Promise.all([
+ const [configRows, userRows, domainSettingsRows, revisionRows, folderRows, cipherRows, attachmentRows, accountPasskeyRows] = await Promise.all([
queryRows(env.DB, 'SELECT key, value FROM config ORDER BY key ASC'),
- queryRows(env.DB, 'SELECT id, email, name, master_password_hint, master_password_hash, key, private_key, public_key, kdf_type, kdf_iterations, kdf_memory, kdf_parallelism, security_stamp, role, status, verify_devices, totp_secret, totp_recovery_code, created_at, updated_at FROM users ORDER BY created_at ASC'),
+ queryRows(env.DB, 'SELECT id, email, name, master_password_hint, master_password_hash, key, private_key, public_key, kdf_type, kdf_iterations, kdf_memory, kdf_parallelism, security_stamp, role, status, verify_devices, totp_secret, totp_recovery_code, yubikey_key1, yubikey_key2, yubikey_key3, yubikey_key4, yubikey_key5, yubikey_nfc, created_at, updated_at FROM users ORDER BY created_at ASC'),
queryRows(env.DB, 'SELECT user_id, equivalent_domains, custom_equivalent_domains, excluded_global_equivalent_domains, updated_at FROM domain_settings ORDER BY user_id ASC'),
queryRows(env.DB, 'SELECT user_id, revision_date FROM user_revisions ORDER BY user_id ASC'),
queryRows(env.DB, 'SELECT id, user_id, name, created_at, updated_at FROM folders ORDER BY created_at ASC'),
queryRows(env.DB, 'SELECT id, user_id, type, folder_id, name, notes, favorite, data, reprompt, key, created_at, updated_at, archived_at, deleted_at FROM ciphers ORDER BY created_at ASC'),
queryRows(env.DB, 'SELECT id, cipher_id, file_name, size, size_name, key FROM attachments ORDER BY cipher_id ASC, id ASC'),
- queryRows(env.DB, 'SELECT id, user_id, name, public_key, credential_id, counter, type, aa_guid, transports, encrypted_user_key, encrypted_public_key, encrypted_private_key, supports_prf, created_at, updated_at FROM webauthn_credentials ORDER BY created_at ASC'),
- queryRows(env.DB, 'SELECT token, user_id, device_identifier, expires_at FROM trusted_two_factor_device_tokens WHERE expires_at >= ? ORDER BY user_id ASC, device_identifier ASC, expires_at DESC', date.getTime()),
+ queryRows(env.DB, 'SELECT id, user_id, purpose, name, public_key, credential_id, counter, type, aa_guid, transports, encrypted_user_key, encrypted_public_key, encrypted_private_key, supports_prf, created_at, updated_at FROM webauthn_credentials ORDER BY created_at ASC'),
]);
const exportedConfigRows = sanitizeConfigRowsForExport(configRows);
const exportedAttachmentRows = includeAttachments ? attachmentRows : [];
@@ -463,7 +527,6 @@ export async function buildBackupArchive(
ciphers: cipherRows.length,
attachments: exportedAttachmentRows.length,
webauthn_credentials: accountPasskeyRows.length,
- trusted_two_factor_device_tokens: trustedTwoFactorTokenRows.length,
},
includes: {
attachments: includeAttachments,
@@ -487,7 +550,6 @@ export async function buildBackupArchive(
ciphers: cipherRows,
attachments: exportedAttachmentRows,
webauthn_credentials: accountPasskeyRows,
- trusted_two_factor_device_tokens: trustedTwoFactorTokenRows,
}, null, BACKUP_JSON_INDENT)),
};
diff --git a/src/services/backup-config.ts b/src/services/backup-config.ts
index 9ecfc66..902db37 100644
--- a/src/services/backup-config.ts
+++ b/src/services/backup-config.ts
@@ -26,7 +26,9 @@ import {
} from '../../shared/backup-schema';
export const BACKUP_SETTINGS_CONFIG_KEY = 'backup.settings.v1';
+const BACKUP_RUNTIME_CONFIG_KEY = 'backup.runtime.v1';
export const BACKUP_SCHEDULER_WINDOW_MINUTES = 5;
+export const REDACTED_BACKUP_SECRET = '********';
const MAX_BACKUP_DESTINATIONS = 24;
export type {
@@ -66,6 +68,163 @@ function normalizePath(value: unknown): string {
return asTrimmedString(value).replace(/\\/g, '/').replace(/^\/+|\/+$/g, '');
}
+function normalizeHostnameForPolicy(hostname: string): string {
+ return hostname.trim().toLowerCase().replace(/^\[|\]$/g, '').replace(/\.$/, '');
+}
+
+function parseIpv4Address(hostname: string): number[] | null {
+ const parts = hostname.split('.');
+ if (parts.length !== 4) return null;
+ const octets = parts.map((part) => {
+ if (!/^\d{1,3}$/.test(part)) return -1;
+ const value = Number(part);
+ return Number.isInteger(value) && value >= 0 && value <= 255 ? value : -1;
+ });
+ return octets.every((value) => value >= 0) ? octets : null;
+}
+
+function isBlockedIpv4Address(octets: number[]): boolean {
+ const [a, b, c] = octets;
+ return (
+ a === 0 ||
+ a === 10 ||
+ a === 127 ||
+ (a === 100 && b >= 64 && b <= 127) ||
+ (a === 169 && b === 254) ||
+ (a === 172 && b >= 16 && b <= 31) ||
+ (a === 192 && (b === 0 || b === 168)) ||
+ (a === 198 && (b === 18 || b === 19 || (b === 51 && c === 100))) ||
+ (a === 203 && b === 0 && c === 113) ||
+ a >= 224
+ );
+}
+
+/**
+ * Expand a hostname-form IPv6 literal to eight 4-digit hextets.
+ * Needed so compressed forms like "::1" are not misclassified by a naive
+ * "first non-empty hextet" check (which would read "1" and miss loopback).
+ */
+function expandIpv6Address(hostname: string): string[] | null {
+ const normalized = hostname.trim().toLowerCase().replace(/^\[|\]$/g, '');
+ if (!normalized.includes(':')) return null;
+ if (normalized.includes('.')) {
+ // IPv4-embedded forms are handled separately by the caller.
+ return null;
+ }
+ if ((normalized.match(/::/g) || []).length > 1) return null;
+
+ const sides = normalized.split('::');
+ const left = sides[0] ? sides[0].split(':').filter((part) => part.length > 0) : [];
+ const right = sides.length > 1 && sides[1] ? sides[1].split(':').filter((part) => part.length > 0) : [];
+ if (left.length + right.length > 8) return null;
+ if (sides.length === 1 && left.length !== 8) return null;
+
+ const missing = 8 - left.length - right.length;
+ if (sides.length > 1 && missing < 0) return null;
+ const middle = sides.length > 1 ? Array.from({ length: missing }, () => '0') : [];
+ const parts = [...left, ...middle, ...right];
+ if (parts.length !== 8) return null;
+
+ const hextets: string[] = [];
+ for (const part of parts) {
+ if (!/^[0-9a-f]{1,4}$/i.test(part)) return null;
+ hextets.push(part.padStart(4, '0'));
+ }
+ return hextets;
+}
+
+function isBlockedIpv6Address(hostname: string): boolean {
+ if (!hostname.includes(':')) return false;
+ const normalized = hostname.toLowerCase().replace(/^\[|\]$/g, '');
+
+ // IPv4-mapped dotted form: ::ffff:127.0.0.1
+ const mappedIpv4 = normalized.match(/::ffff:(\d{1,3}(?:\.\d{1,3}){3})$/i);
+ if (mappedIpv4) {
+ const octets = parseIpv4Address(mappedIpv4[1]);
+ return !octets || isBlockedIpv4Address(octets);
+ }
+
+ // IPv4-mapped hex form produced by some URL parsers: ::ffff:7f00:1
+ const mappedHex = normalized.match(/::ffff:([0-9a-f]{1,4}):([0-9a-f]{1,4})$/i);
+ if (mappedHex) {
+ const hi = Number.parseInt(mappedHex[1], 16);
+ const lo = Number.parseInt(mappedHex[2], 16);
+ if (!Number.isFinite(hi) || !Number.isFinite(lo)) return true;
+ const octets = [(hi >> 8) & 0xff, hi & 0xff, (lo >> 8) & 0xff, lo & 0xff];
+ return isBlockedIpv4Address(octets);
+ }
+
+ const hextets = expandIpv6Address(normalized);
+ if (!hextets) return true;
+ const firstHextet = Number.parseInt(hextets[0], 16);
+ if (!Number.isFinite(firstHextet)) return true;
+ // After expansion, loopback (::1) and unspecified (::) have first hextet 0.
+ return (
+ firstHextet === 0 ||
+ (firstHextet & 0xfe00) === 0xfc00 ||
+ (firstHextet & 0xffc0) === 0xfe80 ||
+ (firstHextet & 0xff00) === 0xff00 ||
+ hextets.join(':').startsWith('2001:0db8:')
+ );
+}
+
+function assertBackupEndpointHostAllowed(hostname: string, label: string): void {
+ const normalized = normalizeHostnameForPolicy(hostname);
+ if (!normalized) throw new Error(`${label} host is required`);
+ if (
+ normalized === 'localhost' ||
+ normalized === 'localhost.localdomain' ||
+ normalized.endsWith('.localhost.localdomain') ||
+ normalized.endsWith('.localhost') ||
+ normalized.endsWith('.local') ||
+ normalized.endsWith('.home.arpa') ||
+ normalized.endsWith('.internal') ||
+ normalized.endsWith('.lan') ||
+ normalized === 'metadata.google.internal' ||
+ normalized === 'localtest.me' ||
+ normalized.endsWith('.localtest.me') ||
+ normalized === 'lvh.me' ||
+ normalized.endsWith('.lvh.me') ||
+ normalized === 'vcap.me' ||
+ normalized.endsWith('.vcap.me') ||
+ normalized === 'nip.io' ||
+ normalized.endsWith('.nip.io') ||
+ normalized === 'sslip.io' ||
+ normalized.endsWith('.sslip.io') ||
+ normalized === 'xip.io' ||
+ normalized.endsWith('.xip.io')
+ ) {
+ throw new Error(`${label} host is not allowed`);
+ }
+ const ipv4 = parseIpv4Address(normalized);
+ if (ipv4 && isBlockedIpv4Address(ipv4)) {
+ throw new Error(`${label} host is not allowed`);
+ }
+ if (isBlockedIpv6Address(normalized)) {
+ throw new Error(`${label} host is not allowed`);
+ }
+}
+
+export function normalizeBackupEndpointUrl(value: string, label: string): string {
+ let parsed: URL;
+ try {
+ parsed = new URL(value);
+ } catch {
+ throw new Error(`${label} must be a valid URL`);
+ }
+ if (parsed.protocol !== 'http:' && parsed.protocol !== 'https:') {
+ throw new Error(`${label} must start with http:// or https://`);
+ }
+ if (parsed.username || parsed.password) {
+ throw new Error(`${label} must not include credentials`);
+ }
+ if (parsed.search || parsed.hash) {
+ throw new Error(`${label} must not include query or fragment`);
+ }
+ assertBackupEndpointHostAllowed(parsed.hostname, label);
+ return parsed.toString().replace(/\/+$/, '');
+}
+
function assertValidTimeZone(timezone: string): string {
try {
new Intl.DateTimeFormat('en-US', { timeZone: timezone }).format(new Date());
@@ -121,7 +280,7 @@ function normalizeS3Destination(value: unknown, allowIncomplete = false): S3Back
if (!allowIncomplete || endpoint) {
if (!endpoint) throw new Error('S3 endpoint is required');
- if (!/^https?:\/\//i.test(endpoint)) throw new Error('S3 endpoint must start with http:// or https://');
+ normalizeBackupEndpointUrl(endpoint, 'S3 endpoint');
}
if (!allowIncomplete || bucket) {
if (!bucket) throw new Error('S3 bucket is required');
@@ -134,7 +293,7 @@ function normalizeS3Destination(value: unknown, allowIncomplete = false): S3Back
}
return {
- endpoint: endpoint ? endpoint.replace(/\/+$/, '') : '',
+ endpoint: endpoint ? normalizeBackupEndpointUrl(endpoint, 'S3 endpoint') : '',
bucket,
addressingStyle,
region,
@@ -153,7 +312,7 @@ function normalizeWebDavDestination(value: unknown, allowIncomplete = false): We
if (!allowIncomplete || baseUrl) {
if (!baseUrl) throw new Error('WebDAV server URL is required');
- if (!/^https?:\/\//i.test(baseUrl)) throw new Error('WebDAV server URL must start with http:// or https://');
+ normalizeBackupEndpointUrl(baseUrl, 'WebDAV server URL');
}
if (!allowIncomplete || username) {
if (!username) throw new Error('WebDAV username is required');
@@ -163,7 +322,7 @@ function normalizeWebDavDestination(value: unknown, allowIncomplete = false): We
}
return {
- baseUrl: baseUrl ? baseUrl.replace(/\/+$/, '') : '',
+ baseUrl: baseUrl ? normalizeBackupEndpointUrl(baseUrl, 'WebDAV server URL') : '',
username,
password,
remotePath,
@@ -179,6 +338,32 @@ function normalizeDestination(
return normalizeWebDavDestination(destination, allowIncomplete);
}
+function shouldPreserveBackupSecret(value: unknown): boolean {
+ if (value === undefined || value === null) return true;
+ const raw = String(value);
+ return raw === '' || raw === REDACTED_BACKUP_SECRET;
+}
+
+function withPreservedDestinationSecret(
+ destinationType: BackupDestinationType,
+ inputDestination: unknown,
+ previous: BackupDestinationRecord | undefined
+): unknown {
+ const source = isPlainObject(inputDestination) ? { ...inputDestination } : {};
+ if (destinationType === 's3') {
+ const previousDestination = previous?.type === 's3' ? previous.destination as S3BackupDestination : null;
+ if (shouldPreserveBackupSecret(source.secretAccessKey)) {
+ source.secretAccessKey = previousDestination?.secretAccessKey || '';
+ }
+ } else {
+ const previousDestination = previous?.type === 'webdav' ? previous.destination as WebDavBackupDestination : null;
+ if (shouldPreserveBackupSecret(source.password)) {
+ source.password = previousDestination?.password || '';
+ }
+ }
+ return source;
+}
+
function normalizeRuntime(value: unknown): BackupRuntimeState {
const source = isPlainObject(value) ? value : {};
const asIso = (input: unknown): string | null => {
@@ -249,7 +434,11 @@ function normalizeDestinationRecord(
retentionCount: normalizeRetentionCount(retentionSource, previousSchedule.retentionCount),
};
- const destination = normalizeDestination(type, input.destination, !schedule.enabled);
+ const destination = normalizeDestination(
+ type,
+ withPreservedDestinationSecret(type, input.destination, previous),
+ !schedule.enabled
+ );
return {
id,
@@ -324,6 +513,47 @@ function mapDestinationsById(destinations: BackupDestinationRecord[]): Map [destination.id, destination]));
}
+function stripRuntimeFromSettings(settings: BackupSettings): BackupSettings {
+ return {
+ destinations: settings.destinations.map((destination) => ({
+ ...destination,
+ runtime: normalizeRuntime(null),
+ })),
+ };
+}
+
+function serializeRuntimeState(settings: BackupSettings): string {
+ return JSON.stringify({
+ version: 1,
+ destinations: Object.fromEntries(
+ settings.destinations.map((destination) => [destination.id, normalizeRuntime(destination.runtime)])
+ ),
+ });
+}
+
+async function loadBackupRuntimeStates(storage: StorageService): Promise> {
+ const raw = await storage.getConfigValue(BACKUP_RUNTIME_CONFIG_KEY);
+ if (!raw) return new Map();
+ try {
+ const parsed = JSON.parse(raw) as { destinations?: Record };
+ const entries = Object.entries(parsed.destinations || {})
+ .filter(([id]) => !!asTrimmedString(id))
+ .map(([id, runtime]) => [id, normalizeRuntime(runtime)] as const);
+ return new Map(entries);
+ } catch {
+ return new Map();
+ }
+}
+
+function mergeRuntimeStates(settings: BackupSettings, runtimes: Map): BackupSettings {
+ return {
+ destinations: settings.destinations.map((destination) => ({
+ ...destination,
+ runtime: runtimes.get(destination.id) || normalizeRuntime(destination.runtime),
+ })),
+ };
+}
+
export function getDefaultBackupSettings(timezone: string = 'UTC'): BackupSettings {
return createSharedDefaultBackupSettings(assertValidTimeZone(timezone));
}
@@ -387,27 +617,55 @@ export function normalizeBackupSettingsInput(
}
export function serializeBackupSettings(settings: BackupSettings): string {
- return JSON.stringify(settings);
+ return JSON.stringify(stripRuntimeFromSettings(settings));
+}
+
+export function redactBackupSettingsSecrets(settings: BackupSettings): BackupSettings {
+ return {
+ destinations: settings.destinations.map((destination) => {
+ if (destination.type === 's3') {
+ const config = destination.destination as S3BackupDestination;
+ return {
+ ...destination,
+ destination: {
+ ...config,
+ secretAccessKey: config.secretAccessKey ? REDACTED_BACKUP_SECRET : '',
+ },
+ };
+ }
+ const config = destination.destination as WebDavBackupDestination;
+ return {
+ ...destination,
+ destination: {
+ ...config,
+ password: config.password ? REDACTED_BACKUP_SECRET : '',
+ },
+ };
+ }),
+ };
}
export async function loadBackupSettings(storage: StorageService, env: Env, fallbackTimezone: string = 'UTC'): Promise {
const raw = await storage.getConfigValue(BACKUP_SETTINGS_CONFIG_KEY);
+ const mergeRuntime = async (settings: BackupSettings): Promise => (
+ mergeRuntimeStates(settings, await loadBackupRuntimeStates(storage))
+ );
if (!raw) {
const settings = getDefaultBackupSettings(fallbackTimezone);
await saveBackupSettings(storage, env, settings);
- return settings;
+ return mergeRuntime(settings);
}
const envelope = parseBackupSettingsEnvelope(raw);
if (!envelope) {
const settings = parseBackupSettings(raw, fallbackTimezone);
await saveBackupSettings(storage, env, settings);
- return settings;
+ return mergeRuntime(settings);
}
try {
const decrypted = await decryptBackupSettingsRuntime(raw, env);
- return parseBackupSettings(decrypted, fallbackTimezone);
+ return mergeRuntime(parseBackupSettings(decrypted, fallbackTimezone));
} catch {
throw new Error('Backup settings need administrator reactivation after restore');
}
@@ -417,6 +675,27 @@ export async function saveBackupSettings(storage: StorageService, env: Env, sett
const users = await storage.getAllUsers();
const encrypted = await encryptBackupSettingsEnvelope(serializeBackupSettings(settings), env, users);
await storage.setConfigValue(BACKUP_SETTINGS_CONFIG_KEY, encrypted);
+ await saveBackupRuntimeStates(storage, settings);
+}
+
+export async function saveBackupRuntimeStates(storage: StorageService, settings: BackupSettings): Promise {
+ await storage.setConfigValue(BACKUP_RUNTIME_CONFIG_KEY, serializeRuntimeState(settings));
+}
+
+export async function updateBackupDestinationRuntime(
+ storage: StorageService,
+ destinationId: string,
+ mutator: (runtime: BackupRuntimeState) => BackupRuntimeState
+): Promise {
+ const runtimes = await loadBackupRuntimeStates(storage);
+ const current = runtimes.get(destinationId) || normalizeRuntime(null);
+ const next = normalizeRuntime(mutator(current));
+ runtimes.set(destinationId, next);
+ await storage.setConfigValue(BACKUP_RUNTIME_CONFIG_KEY, JSON.stringify({
+ version: 1,
+ destinations: Object.fromEntries(runtimes.entries()),
+ }));
+ return next;
}
export async function normalizeImportedBackupSettings(storage: StorageService, env: Env, fallbackTimezone: string = 'UTC'): Promise {
@@ -596,9 +875,9 @@ export function hasBackupSlotBetween(
const endMs = endExclusive.getTime();
if (!Number.isFinite(startMs) || !Number.isFinite(endMs) || endMs <= startMs) return false;
- const lastAttemptAt = destination.runtime.lastAttemptAt ? new Date(destination.runtime.lastAttemptAt) : null;
- const lastAttemptMs = lastAttemptAt && Number.isFinite(lastAttemptAt.getTime())
- ? lastAttemptAt.getTime()
+ const lastSuccessAt = destination.runtime.lastSuccessAt ? new Date(destination.runtime.lastSuccessAt) : null;
+ const lastSuccessMs = lastSuccessAt && Number.isFinite(lastSuccessAt.getTime())
+ ? lastSuccessAt.getTime()
: Number.NEGATIVE_INFINITY;
const dayCursor = new Date(startMs);
@@ -620,7 +899,7 @@ export function hasBackupSlotBetween(
for (const slotStart of slotStarts) {
const slotStartMs = slotStart.getTime();
if (slotStartMs < startMs || slotStartMs >= endMs) continue;
- if (lastAttemptMs >= slotStartMs) continue;
+ if (lastSuccessMs >= slotStartMs) continue;
return true;
}
}
@@ -637,9 +916,9 @@ export function isBackupDueNow(
): boolean {
if (!destination.schedule.enabled) return false;
const toleranceMs = Math.max(1, windowMinutes) * 60 * 1000;
- const lastAttemptAt = destination.runtime.lastAttemptAt ? new Date(destination.runtime.lastAttemptAt) : null;
- const lastAttemptMs = lastAttemptAt && Number.isFinite(lastAttemptAt.getTime())
- ? lastAttemptAt.getTime()
+ const lastSuccessAt = destination.runtime.lastSuccessAt ? new Date(destination.runtime.lastSuccessAt) : null;
+ const lastSuccessMs = lastSuccessAt && Number.isFinite(lastSuccessAt.getTime())
+ ? lastSuccessAt.getTime()
: Number.NEGATIVE_INFINITY;
const localDateKey = getBackupLocalDateKey(now, destination.schedule.timezone);
const slotStarts = getBackupSlotStartsForLocalDay(
@@ -652,7 +931,7 @@ export function isBackupDueNow(
for (const slotStart of slotStarts) {
const slotStartMs = slotStart.getTime();
if (now.getTime() < slotStartMs || now.getTime() >= slotStartMs + toleranceMs) continue;
- if (lastAttemptMs >= slotStartMs) return false;
+ if (lastSuccessMs >= slotStartMs) return false;
return true;
}
return false;
diff --git a/src/services/backup-import.ts b/src/services/backup-import.ts
index e95c249..79f3b57 100644
--- a/src/services/backup-import.ts
+++ b/src/services/backup-import.ts
@@ -1,9 +1,11 @@
import type { Env, User } from '../types';
import { KV_MAX_OBJECT_BYTES, deleteBlobObject, getAttachmentObjectKey, getBlobStorageKind, putBlobObject } from './blob-store';
import { BACKUP_SETTINGS_CONFIG_KEY, normalizeImportedBackupSettingsValue } from './backup-config';
+import { YUBICO_BOOTSTRAP_CLAIM_CONFIG_KEY } from './yubico-config';
import {
type BackupManifestAttachmentBlob,
type BackupPayload,
+ isSafeBackupAttachmentBlobName,
parseBackupArchive,
validateBackupPayloadContents,
} from './backup-archive';
@@ -18,13 +20,14 @@ import {
// shadow-table count validation, insert column lists, and frontend import
// count types together.
// - Do not import users.api_key, even if an older backup contains it.
+// - Do not import, clear, or replace runtime authentication state such as
+// devices, sessions, auth requests, or remembered 2FA device tokens.
type SqlRow = Record;
type BackupTableName =
| 'config'
| 'users'
| 'domain_settings'
| 'user_revisions'
- | 'trusted_two_factor_device_tokens'
| 'webauthn_credentials'
| 'folders'
| 'ciphers'
@@ -35,7 +38,6 @@ const BACKUP_TABLES: BackupTableName[] = [
'users',
'domain_settings',
'user_revisions',
- 'trusted_two_factor_device_tokens',
'webauthn_credentials',
'folders',
'ciphers',
@@ -53,7 +55,6 @@ export interface BackupImportResultBody {
users: number;
domainSettings: number;
userRevisions: number;
- trustedTwoFactorDeviceTokens: number;
webauthnCredentials: number;
folders: number;
ciphers: number;
@@ -175,7 +176,6 @@ function buildResetImportTargetStatements(db: D1Database): D1PreparedStatement[]
'DELETE FROM ciphers',
'DELETE FROM folders',
'DELETE FROM webauthn_credentials',
- 'DELETE FROM trusted_two_factor_device_tokens',
'DELETE FROM domain_settings',
'DELETE FROM user_revisions',
'DELETE FROM users',
@@ -253,6 +253,10 @@ function cloneRows(rows: SqlRow[]): SqlRow[] {
return rows.map((row) => ({ ...row }));
}
+function normalizeAccountPasskeyPurpose(value: unknown): 'login' | 'twoFactor' {
+ return value == null ? 'login' : String(value).trim() === 'twoFactor' ? 'twoFactor' : 'login';
+}
+
function upsertConfigRow(rows: SqlRow[], key: string, value: string): SqlRow[] {
let replaced = false;
const nextRows = rows.map((row) => {
@@ -271,7 +275,9 @@ async function prepareImportedConfigRows(
configRows: SqlRow[],
userRows: SqlRow[]
): Promise {
- let nextConfigRows = cloneRows(configRows || []);
+ let nextConfigRows = cloneRows(configRows || []).filter(
+ (row) => String(row.key || '').trim() !== YUBICO_BOOTSTRAP_CLAIM_CONFIG_KEY
+ );
const rawBackupSettings = nextConfigRows.find((row) => String(row.key || '').trim() === BACKUP_SETTINGS_CONFIG_KEY);
const normalizedBackupSettings = await normalizeImportedBackupSettingsValue(
typeof rawBackupSettings?.value === 'string' ? rawBackupSettings.value : null,
@@ -296,12 +302,15 @@ async function importPreparedBackupRows(db: D1Database, payload: BackupPayload['
config: await prepareImportedConfigRows(env, payload.config || [], payload.users || []),
users: cloneRows(payload.users || []).map((row) => ({
...row,
- verify_devices: row.verify_devices ?? 1,
+ verify_devices: row.verify_devices ?? 0,
+ yubikey_nfc: row.yubikey_nfc ?? 0,
})),
domain_settings: cloneRows(payload.domain_settings || []),
user_revisions: cloneRows(payload.user_revisions || []),
- trusted_two_factor_device_tokens: cloneRows(payload.trusted_two_factor_device_tokens || []),
- webauthn_credentials: cloneRows(payload.webauthn_credentials || []),
+ webauthn_credentials: cloneRows(payload.webauthn_credentials || []).map((row) => ({
+ ...row,
+ purpose: normalizeAccountPasskeyPurpose(row.purpose),
+ })),
folders: cloneRows(payload.folders || []),
ciphers: cloneRows(payload.ciphers || []).map((row) => ({
...row,
@@ -461,9 +470,20 @@ async function restoreBlobFiles(env: Env, db: BackupPayload['db'], files: Record
}
function buildAttachmentBlobLookup(manifest: BackupPayload['manifest']): Map {
- return new Map(
- (manifest.attachmentBlobs || []).map((item) => [`${item.cipherId}/${item.attachmentId}`, item])
- );
+ const lookup = new Map();
+ for (const item of manifest.attachmentBlobs || []) {
+ const cipherId = String(item.cipherId || '').trim();
+ const attachmentId = String(item.attachmentId || '').trim();
+ const blobName = String(item.blobName || '').trim();
+ if (!cipherId || !attachmentId || !isSafeBackupAttachmentBlobName(blobName)) continue;
+ lookup.set(`${cipherId}/${attachmentId}`, {
+ ...item,
+ cipherId,
+ attachmentId,
+ blobName,
+ });
+ }
+ return lookup;
}
async function prepareRemoteAttachmentPayload(
@@ -619,7 +639,7 @@ async function importBackupRows(db: D1Database, payload: BackupPayload['db'], us
buildInsertStatements(
db,
tableName('users'),
- ['id', 'email', 'name', 'master_password_hint', 'master_password_hash', 'key', 'private_key', 'public_key', 'kdf_type', 'kdf_iterations', 'kdf_memory', 'kdf_parallelism', 'security_stamp', 'role', 'status', 'verify_devices', 'totp_secret', 'totp_recovery_code', 'created_at', 'updated_at'],
+ ['id', 'email', 'name', 'master_password_hint', 'master_password_hash', 'key', 'private_key', 'public_key', 'kdf_type', 'kdf_iterations', 'kdf_memory', 'kdf_parallelism', 'security_stamp', 'role', 'status', 'verify_devices', 'totp_secret', 'totp_recovery_code', 'yubikey_key1', 'yubikey_key2', 'yubikey_key3', 'yubikey_key4', 'yubikey_key5', 'yubikey_nfc', 'created_at', 'updated_at'],
payload.users || []
)
);
@@ -639,23 +659,13 @@ async function importBackupRows(db: D1Database, payload: BackupPayload['db'], us
true
)
);
- await runInsertBatch(
- db,
- tableName('trusted_two_factor_device_tokens'),
- buildInsertStatements(
- db,
- tableName('trusted_two_factor_device_tokens'),
- ['token', 'user_id', 'device_identifier', 'expires_at'],
- payload.trusted_two_factor_device_tokens || []
- )
- );
await runInsertBatch(
db,
tableName('webauthn_credentials'),
buildInsertStatements(
db,
tableName('webauthn_credentials'),
- ['id', 'user_id', 'name', 'public_key', 'credential_id', 'counter', 'type', 'aa_guid', 'transports', 'encrypted_user_key', 'encrypted_public_key', 'encrypted_private_key', 'supports_prf', 'created_at', 'updated_at'],
+ ['id', 'user_id', 'purpose', 'name', 'public_key', 'credential_id', 'counter', 'type', 'aa_guid', 'transports', 'encrypted_user_key', 'encrypted_public_key', 'encrypted_private_key', 'supports_prf', 'created_at', 'updated_at'],
payload.webauthn_credentials || []
)
);
@@ -727,7 +737,6 @@ export async function importBackupArchiveBytes(
users: (db.users || []).length,
domain_settings: (db.domain_settings || []).length,
user_revisions: (db.user_revisions || []).length,
- trusted_two_factor_device_tokens: (db.trusted_two_factor_device_tokens || []).length,
webauthn_credentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
@@ -751,7 +760,6 @@ export async function importBackupArchiveBytes(
users: (db.users || []).length,
domain_settings: (db.domain_settings || []).length,
user_revisions: (db.user_revisions || []).length,
- trusted_two_factor_device_tokens: (db.trusted_two_factor_device_tokens || []).length,
webauthn_credentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
@@ -793,7 +801,6 @@ export async function importBackupArchiveBytes(
users: (db.users || []).length,
domainSettings: (db.domain_settings || []).length,
userRevisions: (db.user_revisions || []).length,
- trustedTwoFactorDeviceTokens: (db.trusted_two_factor_device_tokens || []).length,
webauthnCredentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
@@ -871,7 +878,6 @@ export async function importRemoteBackupArchiveBytes(
users: (db.users || []).length,
domain_settings: (db.domain_settings || []).length,
user_revisions: (db.user_revisions || []).length,
- trusted_two_factor_device_tokens: (db.trusted_two_factor_device_tokens || []).length,
webauthn_credentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
@@ -895,7 +901,6 @@ export async function importRemoteBackupArchiveBytes(
users: (db.users || []).length,
domain_settings: (db.domain_settings || []).length,
user_revisions: (db.user_revisions || []).length,
- trusted_two_factor_device_tokens: (db.trusted_two_factor_device_tokens || []).length,
webauthn_credentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
@@ -943,7 +948,6 @@ export async function importRemoteBackupArchiveBytes(
users: (db.users || []).length,
domainSettings: (db.domain_settings || []).length,
userRevisions: (db.user_revisions || []).length,
- trustedTwoFactorDeviceTokens: (db.trusted_two_factor_device_tokens || []).length,
webauthnCredentials: (db.webauthn_credentials || []).length,
folders: (db.folders || []).length,
ciphers: (db.ciphers || []).length,
diff --git a/src/services/backup-uploader.ts b/src/services/backup-uploader.ts
index 53b2520..c9c666a 100644
--- a/src/services/backup-uploader.ts
+++ b/src/services/backup-uploader.ts
@@ -3,6 +3,7 @@ import {
BackupDestinationType,
S3BackupDestination,
WebDavBackupDestination,
+ normalizeBackupEndpointUrl,
} from './backup-config';
export interface BackupUploadResult {
@@ -33,6 +34,13 @@ export interface RemoteBackupFile {
bytes: Uint8Array;
}
+export interface RemoteBackupFileStat {
+ provider: BackupDestinationType;
+ remotePath: string;
+ size: number | null;
+ modifiedAt: string | null;
+}
+
export interface RemoteBackupFilePutOptions {
contentType?: string;
}
@@ -208,7 +216,7 @@ function ensureDestinationConfigReady(destination: BackupDestinationRecord): voi
if (destination.type === 'webdav') {
const config = destination.destination as WebDavBackupDestination;
if (!String(config.baseUrl || '').trim()) throw new Error('WebDAV server URL is required');
- if (!/^https?:\/\//i.test(String(config.baseUrl || '').trim())) throw new Error('WebDAV server URL must start with http:// or https://');
+ normalizeBackupEndpointUrl(String(config.baseUrl || '').trim(), 'WebDAV server URL');
if (!String(config.username || '').trim()) throw new Error('WebDAV username is required');
if (!String(config.password || '')) throw new Error('WebDAV password is required');
return;
@@ -216,7 +224,7 @@ function ensureDestinationConfigReady(destination: BackupDestinationRecord): voi
if (destination.type === 's3') {
const config = destination.destination as S3BackupDestination;
if (!String(config.endpoint || '').trim()) throw new Error('S3 endpoint is required');
- if (!/^https?:\/\//i.test(String(config.endpoint || '').trim())) throw new Error('S3 endpoint must start with http:// or https://');
+ normalizeBackupEndpointUrl(String(config.endpoint || '').trim(), 'S3 endpoint');
if (!String(config.bucket || '').trim()) throw new Error('S3 bucket is required');
if (!String(config.accessKeyId || '').trim()) throw new Error('S3 access key is required');
if (!String(config.secretAccessKey || '')) throw new Error('S3 secret key is required');
@@ -245,7 +253,7 @@ async function ensureWebDavDirectory(baseUrl: string, directoryPath: string, aut
Authorization: authHeader,
},
});
- if ([200, 201, 204, 301, 302, 405].includes(response.status)) continue;
+ if ([200, 201, 204, 405].includes(response.status)) continue;
throw new Error(`WebDAV directory creation failed: ${response.status}`);
}
}
@@ -268,7 +276,7 @@ async function ensureWebDavDirectoryCached(
Authorization: authHeader,
},
});
- if ([200, 201, 204, 301, 302, 405].includes(response.status)) {
+ if ([200, 201, 204, 405].includes(response.status)) {
ensuredDirectories.add(current);
continue;
}
@@ -433,6 +441,10 @@ async function deleteFromWebDav(config: WebDavBackupDestination, relativePath: s
}
async function existsInWebDav(config: WebDavBackupDestination, relativePath: string): Promise {
+ return (await statWebDavFile(config, relativePath)) !== null;
+}
+
+async function statWebDavFile(config: WebDavBackupDestination, relativePath: string): Promise {
const authHeader = toBasicAuthHeader(config.username, config.password);
const remotePath = webDavFullPath(config, relativePath);
const response = await fetch(buildWebDavUrl(config.baseUrl, remotePath), {
@@ -441,11 +453,17 @@ async function existsInWebDav(config: WebDavBackupDestination, relativePath: str
Authorization: authHeader,
},
});
- if (response.status === 404) return false;
+ if (response.status === 404) return null;
if (!response.ok) {
throw new Error(`WebDAV existence check failed: ${response.status}`);
}
- return true;
+ const size = Number(response.headers.get('Content-Length') || '');
+ return {
+ provider: 'webdav',
+ remotePath: normalizeRelativePath(relativePath),
+ size: Number.isFinite(size) ? size : null,
+ modifiedAt: parseHttpDate(response.headers.get('Last-Modified') || ''),
+ };
}
function isBucketHostedS3Endpoint(endpoint: URL, bucket: string): boolean {
@@ -501,7 +519,7 @@ async function signedS3Request(
config.region || 'auto'
);
- return fetch(url.toString(), {
+ return fetch(url, {
method,
headers: {
Authorization: authorization,
@@ -540,61 +558,68 @@ async function listS3Entries(config: S3BackupDestination, relativePath: string):
const currentPath = normalizeRelativePath(relativePath);
const targetPrefixBase = normalizeS3ObjectKey(config, currentPath);
const targetPrefix = trimSlashes(targetPrefixBase) ? `${trimSlashes(targetPrefixBase)}/` : '';
- const url = s3BucketBaseUrl(config);
- url.searchParams.set('list-type', '2');
- url.searchParams.set('delimiter', '/');
- if (targetPrefix) url.searchParams.set('prefix', targetPrefix);
-
- const response = await signedS3Request(config, 'GET', url);
- if (!response.ok) {
- throw new Error(`S3 listing failed: ${response.status}`);
- }
-
- const xml = await response.text();
const rootPrefix = trimSlashes(config.rootPath);
const items: RemoteBackupItem[] = [];
+ let continuationToken = '';
- for (const prefix of extractXmlBlocks(xml, 'CommonPrefixes')) {
- const fullPrefix = trimSlashes(extractXmlFirst(prefix, 'Prefix') || '');
- if (!fullPrefix) continue;
- const relative = rootPrefix
- ? fullPrefix === rootPrefix
- ? ''
- : fullPrefix.startsWith(`${rootPrefix}/`)
- ? fullPrefix.slice(rootPrefix.length + 1)
+ do {
+ const url = s3BucketBaseUrl(config);
+ url.searchParams.set('list-type', '2');
+ url.searchParams.set('delimiter', '/');
+ if (targetPrefix) url.searchParams.set('prefix', targetPrefix);
+ if (continuationToken) url.searchParams.set('continuation-token', continuationToken);
+
+ const response = await signedS3Request(config, 'GET', url);
+ if (!response.ok) {
+ throw new Error(`S3 listing failed: ${response.status}`);
+ }
+
+ const xml = await response.text();
+
+ for (const prefix of extractXmlBlocks(xml, 'CommonPrefixes')) {
+ const fullPrefix = trimSlashes(extractXmlFirst(prefix, 'Prefix') || '');
+ if (!fullPrefix) continue;
+ const relative = rootPrefix
+ ? fullPrefix === rootPrefix
+ ? ''
+ : fullPrefix.startsWith(`${rootPrefix}/`)
+ ? fullPrefix.slice(rootPrefix.length + 1)
+ : ''
+ : fullPrefix;
+ const normalizedRelative = trimSlashes(relative);
+ if (!normalizedRelative) continue;
+ const itemPath = normalizedRelative.replace(/\/+$/, '');
+ if ((parentPath(itemPath) || '') !== currentPath) continue;
+ items.push({
+ path: itemPath,
+ name: basename(itemPath) || itemPath,
+ isDirectory: true,
+ size: null,
+ modifiedAt: null,
+ });
+ }
+
+ for (const content of extractXmlBlocks(xml, 'Contents')) {
+ const fullKey = trimSlashes(extractXmlFirst(content, 'Key') || '');
+ if (!fullKey || (targetPrefix && fullKey === trimSlashes(targetPrefix))) continue;
+ const relative = rootPrefix
+ ? fullKey.startsWith(`${rootPrefix}/`)
+ ? fullKey.slice(rootPrefix.length + 1)
: ''
- : fullPrefix;
- const normalizedRelative = trimSlashes(relative);
- if (!normalizedRelative) continue;
- const itemPath = normalizedRelative.replace(/\/+$/, '');
- if ((parentPath(itemPath) || '') !== currentPath) continue;
- items.push({
- path: itemPath,
- name: basename(itemPath) || itemPath,
- isDirectory: true,
- size: null,
- modifiedAt: null,
- });
- }
+ : fullKey;
+ const normalizedRelative = trimSlashes(relative);
+ if (!normalizedRelative || (parentPath(normalizedRelative) || '') !== currentPath) continue;
+ items.push({
+ path: normalizedRelative,
+ name: basename(normalizedRelative) || normalizedRelative,
+ isDirectory: false,
+ size: Number(extractXmlFirst(content, 'Size') || 0) || null,
+ modifiedAt: parseHttpDate(extractXmlFirst(content, 'LastModified') || '') || null,
+ });
+ }
- for (const content of extractXmlBlocks(xml, 'Contents')) {
- const fullKey = trimSlashes(extractXmlFirst(content, 'Key') || '');
- if (!fullKey || (targetPrefix && fullKey === trimSlashes(targetPrefix))) continue;
- const relative = rootPrefix
- ? fullKey.startsWith(`${rootPrefix}/`)
- ? fullKey.slice(rootPrefix.length + 1)
- : ''
- : fullKey;
- const normalizedRelative = trimSlashes(relative);
- if (!normalizedRelative || (parentPath(normalizedRelative) || '') !== currentPath) continue;
- items.push({
- path: normalizedRelative,
- name: basename(normalizedRelative) || normalizedRelative,
- isDirectory: false,
- size: Number(extractXmlFirst(content, 'Size') || 0) || null,
- modifiedAt: parseHttpDate(extractXmlFirst(content, 'LastModified') || '') || null,
- });
- }
+ continuationToken = extractXmlFirst(xml, 'NextContinuationToken') || '';
+ } while (continuationToken);
const deduped = new Map();
for (const item of items) deduped.set(`${item.isDirectory ? 'd' : 'f'}:${item.path}`, item);
@@ -637,14 +662,24 @@ async function deleteFromS3(config: S3BackupDestination, relativePath: string):
}
async function existsInS3(config: S3BackupDestination, relativePath: string): Promise {
+ return (await statS3File(config, relativePath)) !== null;
+}
+
+async function statS3File(config: S3BackupDestination, relativePath: string): Promise {
const objectKey = normalizeS3ObjectKey(config, relativePath);
const url = s3ObjectUrl(config, objectKey);
const response = await signedS3Request(config, 'HEAD', url);
- if (response.status === 404) return false;
+ if (response.status === 404) return null;
if (!response.ok) {
throw new Error(`S3 existence check failed: ${response.status}`);
}
- return true;
+ const size = Number(response.headers.get('Content-Length') || '');
+ return {
+ provider: 's3',
+ remotePath: normalizeRelativePath(relativePath),
+ size: Number.isFinite(size) ? size : null,
+ modifiedAt: parseHttpDate(response.headers.get('Last-Modified') || ''),
+ };
}
interface ConfiguredDestinationAdapter {
@@ -656,6 +691,7 @@ interface ConfiguredDestinationAdapter {
download: (config: WebDavBackupDestination | S3BackupDestination, relativePath: string) => Promise;
deleteFile: (config: WebDavBackupDestination | S3BackupDestination, relativePath: string) => Promise;
exists: (config: WebDavBackupDestination | S3BackupDestination, relativePath: string) => Promise;
+ stat: (config: WebDavBackupDestination | S3BackupDestination, relativePath: string) => Promise;
}
export interface RemoteBackupTransferSession {
@@ -666,6 +702,7 @@ export interface RemoteBackupTransferSession {
download(relativePath: string): Promise;
deleteFile(relativePath: string): Promise;
exists(relativePath: string): Promise;
+ stat(relativePath: string): Promise;
}
function resolveConfiguredDestinationAdapter(
@@ -683,6 +720,7 @@ function resolveConfiguredDestinationAdapter(
download: (config, relativePath) => downloadFromWebDav(config as WebDavBackupDestination, relativePath),
deleteFile: (config, relativePath) => deleteFromWebDav(config as WebDavBackupDestination, relativePath),
exists: (config, relativePath) => existsInWebDav(config as WebDavBackupDestination, relativePath),
+ stat: (config, relativePath) => statWebDavFile(config as WebDavBackupDestination, relativePath),
};
}
if (destination.type === 's3') {
@@ -695,6 +733,7 @@ function resolveConfiguredDestinationAdapter(
download: (config, relativePath) => downloadFromS3(config as S3BackupDestination, relativePath),
deleteFile: (config, relativePath) => deleteFromS3(config as S3BackupDestination, relativePath),
exists: (config, relativePath) => existsInS3(config as S3BackupDestination, relativePath),
+ stat: (config, relativePath) => statS3File(config as S3BackupDestination, relativePath),
};
}
@@ -730,6 +769,7 @@ export function createRemoteBackupTransferSession(destination: BackupDestination
download: async (relativePath: string) => adapter.download(adapter.config, relativePath),
deleteFile: async (relativePath: string) => adapter.deleteFile(adapter.config, normalizeRelativePath(relativePath)),
exists: async (relativePath: string) => adapter.exists(adapter.config, normalizeRelativePath(relativePath)),
+ stat: async (relativePath: string) => adapter.stat(adapter.config, normalizeRelativePath(relativePath)),
};
}
diff --git a/src/services/push-relay.ts b/src/services/push-relay.ts
new file mode 100644
index 0000000..765cca1
--- /dev/null
+++ b/src/services/push-relay.ts
@@ -0,0 +1,258 @@
+import type { Env } from '../types';
+import {
+ setConfigValue as saveConfigValue,
+} from './storage-config-repo';
+
+const PUSH_RELAY_URI = 'https://push.bitwarden.com';
+const PUSH_IDENTITY_URI = 'https://identity.bitwarden.com';
+const INSTALLATIONS_URI = 'https://api.bitwarden.com/installations';
+const PUSH_INSTALLATION_ID_KEY = 'push.installation.id';
+const PUSH_INSTALLATION_KEY_KEY = 'push.installation.key';
+const PUSH_REQUEST_TIMEOUT_MS = 5000;
+
+interface CachedPushAccessToken {
+ token: string;
+ expiresAt: number;
+}
+
+let cachedPushAccessToken: CachedPushAccessToken | null = null;
+
+async function fetchPushEndpoint(url: string, init: RequestInit, errorMessage: string): Promise {
+ const controller = new AbortController();
+ const timeout = setTimeout(() => controller.abort(), PUSH_REQUEST_TIMEOUT_MS);
+ try {
+ return await fetch(url, { ...init, signal: controller.signal });
+ } catch (error) {
+ console.error(errorMessage, error);
+ return null;
+ } finally {
+ clearTimeout(timeout);
+ }
+}
+
+function randomInstallationEmail(): string {
+ const bytes = new Uint8Array(10);
+ crypto.getRandomValues(bytes);
+ const localPart = Array.from(bytes, (byte) => (byte % 36).toString(36)).join('');
+ return `${localPart}@nodewarden.app`;
+}
+
+async function getConfigKeyPresence(db: D1Database, key: string): Promise {
+ const row = await db.prepare('SELECT value FROM config WHERE key = ? LIMIT 1').bind(key).first<{ value: string }>();
+ return typeof row?.value === 'string' ? row.value : null;
+}
+
+async function getPushInstallationCredentials(db: D1Database): Promise<{ id: string; key: string } | null> {
+ const [id, key] = await Promise.all([
+ getConfigKeyPresence(db, PUSH_INSTALLATION_ID_KEY),
+ getConfigKeyPresence(db, PUSH_INSTALLATION_KEY_KEY),
+ ]);
+ const normalizedId = String(id || '').trim();
+ const normalizedKey = String(key || '').trim();
+ return normalizedId && normalizedKey ? { id: normalizedId, key: normalizedKey } : null;
+}
+
+export async function ensurePushInstallationCredentials(db: D1Database): Promise<{ id: string; key: string } | null> {
+ const existing = await getPushInstallationCredentials(db);
+ if (existing) return existing;
+
+ const response = await fetchPushEndpoint(
+ INSTALLATIONS_URI,
+ {
+ method: 'POST',
+ headers: {
+ accept: 'application/json',
+ 'content-type': 'application/json',
+ },
+ body: JSON.stringify({
+ email: randomInstallationEmail(),
+ }),
+ },
+ 'Failed to request Bitwarden push installation:'
+ );
+ if (!response) return null;
+
+ if (!response.ok) {
+ console.error('Failed to request Bitwarden push installation:', response.status, await response.text().catch(() => ''));
+ return null;
+ }
+
+ const body = (await response.json().catch(() => null)) as { id?: string; Id?: string; key?: string; Key?: string; enabled?: boolean; Enabled?: boolean } | null;
+ const id = String(body?.id || body?.Id || '').trim();
+ const key = String(body?.key || body?.Key || '').trim();
+ if (!id || !key) {
+ console.error('Bitwarden push installation response did not include id/key');
+ return null;
+ }
+
+ await Promise.all([
+ saveConfigValue(db, PUSH_INSTALLATION_ID_KEY, id),
+ saveConfigValue(db, PUSH_INSTALLATION_KEY_KEY, key),
+ ]);
+ return { id, key };
+}
+
+async function getPushAccessToken(env: Env): Promise {
+ const credentials = await ensurePushInstallationCredentials(env.DB);
+ if (!credentials) return null;
+
+ const now = Date.now();
+ if (cachedPushAccessToken && cachedPushAccessToken.expiresAt > now + 30_000) {
+ return cachedPushAccessToken.token;
+ }
+
+ const params = new URLSearchParams({
+ grant_type: 'client_credentials',
+ scope: 'api.push',
+ client_id: `installation.${credentials.id}`,
+ client_secret: credentials.key,
+ });
+
+ const response = await fetchPushEndpoint(
+ `${PUSH_IDENTITY_URI}/connect/token`,
+ {
+ method: 'POST',
+ headers: {
+ accept: 'application/json',
+ 'content-type': 'application/x-www-form-urlencoded',
+ },
+ body: params.toString(),
+ },
+ 'Failed to get Bitwarden push relay token:'
+ );
+ if (!response) return null;
+
+ if (!response.ok) {
+ console.error('Failed to get Bitwarden push relay token:', response.status, await response.text().catch(() => ''));
+ return null;
+ }
+
+ const body = (await response.json().catch(() => null)) as { access_token?: string; expires_in?: number } | null;
+ const token = String(body?.access_token || '').trim();
+ if (!token) {
+ console.error('Bitwarden push relay token response did not include an access_token');
+ return null;
+ }
+
+ const expiresInSeconds = Math.max(60, Number(body?.expires_in || 3600));
+ cachedPushAccessToken = {
+ token,
+ expiresAt: now + Math.floor(expiresInSeconds * 500),
+ };
+ return token;
+}
+
+async function postToPushRelay(env: Env, path: string, body?: unknown): Promise {
+ const token = await getPushAccessToken(env);
+ if (!token) return false;
+
+ const response = await fetchPushEndpoint(
+ `${PUSH_RELAY_URI}${path}`,
+ {
+ method: 'POST',
+ headers: {
+ accept: 'application/json',
+ authorization: `Bearer ${token}`,
+ ...(body === undefined ? {} : { 'content-type': 'application/json' }),
+ },
+ body: body === undefined ? undefined : JSON.stringify(body),
+ },
+ `Bitwarden push relay request failed: ${path}`
+ );
+ if (!response) return false;
+
+ if (!response.ok) {
+ console.error('Bitwarden push relay request failed:', path, response.status, await response.text().catch(() => ''));
+ return false;
+ }
+
+ return true;
+}
+
+function mobilePayloadFromSignalR(updateType: number, userId: string, revisionDate: string, payload: Record | null | undefined): Record {
+ const source = payload || {};
+ const id = source.Id ?? source.id;
+ const organizationId = source.OrganizationId ?? source.organizationId ?? null;
+ const collectionIds = source.CollectionIds ?? source.collectionIds ?? null;
+
+ if (id != null) {
+ return {
+ id,
+ userId: source.UserId ?? source.userId ?? userId,
+ organizationId,
+ collectionIds,
+ revisionDate: source.RevisionDate ?? source.revisionDate ?? revisionDate,
+ };
+ }
+
+ return {
+ userId: source.UserId ?? source.userId ?? userId,
+ date: source.Date ?? source.date ?? revisionDate,
+ };
+}
+
+export async function registerMobilePushDevice(
+ env: Env,
+ input: {
+ userId: string;
+ deviceIdentifier: string;
+ type: number;
+ pushUuid: string;
+ pushToken: string;
+ }
+): Promise {
+ const credentials = await ensurePushInstallationCredentials(env.DB);
+ if (!credentials) return false;
+
+ return postToPushRelay(env, '/push/register', {
+ deviceId: input.pushUuid,
+ pushToken: input.pushToken,
+ userId: input.userId,
+ type: input.type,
+ identifier: input.deviceIdentifier,
+ installationId: credentials.id,
+ });
+}
+
+export async function unregisterMobilePushDevice(env: Env, pushUuid: string | null | undefined): Promise